
CVE-2026-35584
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
exploitationinformation-gatheringpenetration-testing+3
spoo1k/cve-2026-35584Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
 elcuervo/tangalanga
Tangalanga: the Zoom conference scanner hacking tool
 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
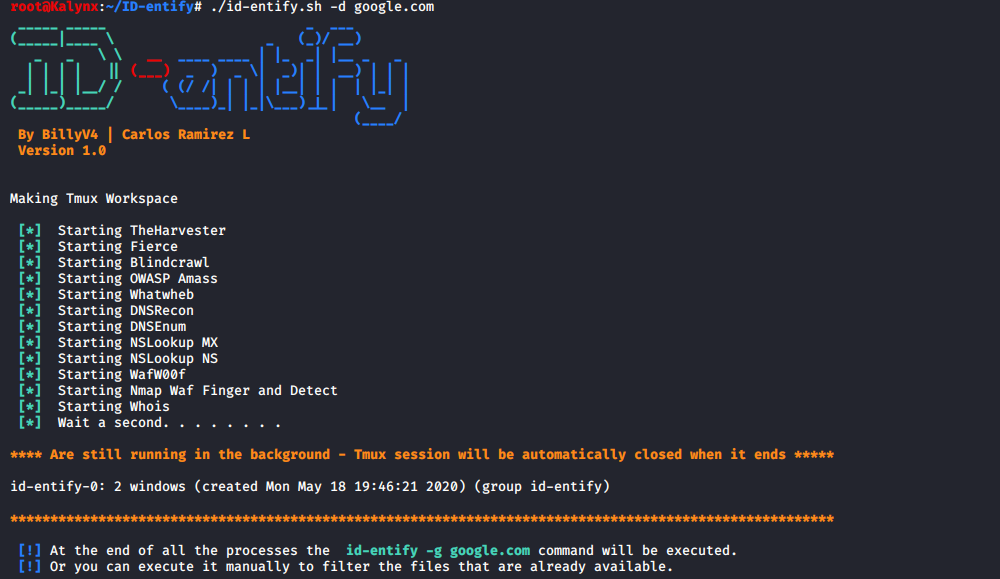 billyv4/id-entify
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.
 aj2108/cve-2026-9833
Technical analysis of a reflected XSS vulnerability in the Tag Groups WordPress plugin before 2.2.0, covering root cause, attack flow, impact,…
 cappricio-securities/cve-2023-29489
An issue was discovered in cPanel before 11.109.9999.116. Cross-Site Scripting can occur on the cpsrvd error page via an invalid webcall ID.
 0xn4d/poc-cve-xss-inventory-press-plugin
PoC for CVE-2023-2579
 0xn4d/poc-cve-xss-encoded-wp-inventory-manager-plugin
PoC for CVE-2023-2123
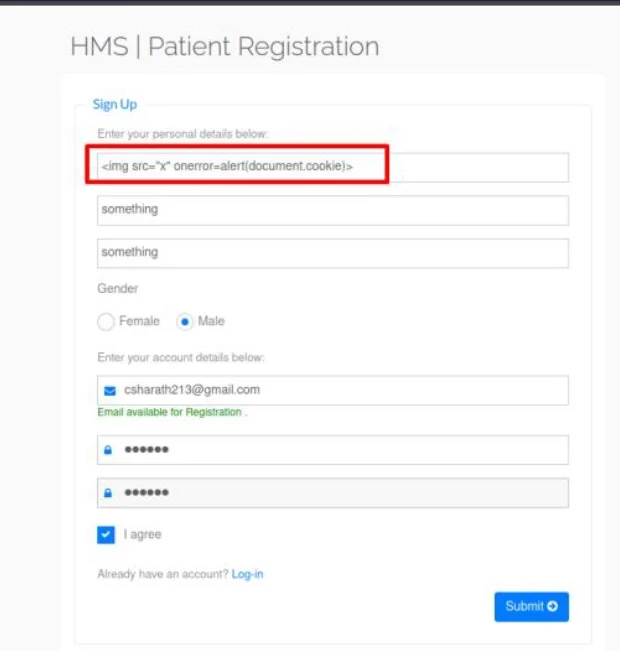 sharathc213/cve-2023-7173
Proof-of-concept for CVE-2023-7173, a stored XSS in Hospital Management System 1.0, with Docker setup and reproduction steps.
 kirubel-cve/cve-2026-36957
Proof-of-concept for CVE-2026-36957, a denial-of-service vulnerability in Dbit Router firmware via HTTP flood on the Boa web server, causing resource…
 open-flaw/cve-2025-12758
Detailed CVE-2025-12758 disclosure with PoC demonstrating Unicode variation selector bypass in validator.js isLength(), including root cause…
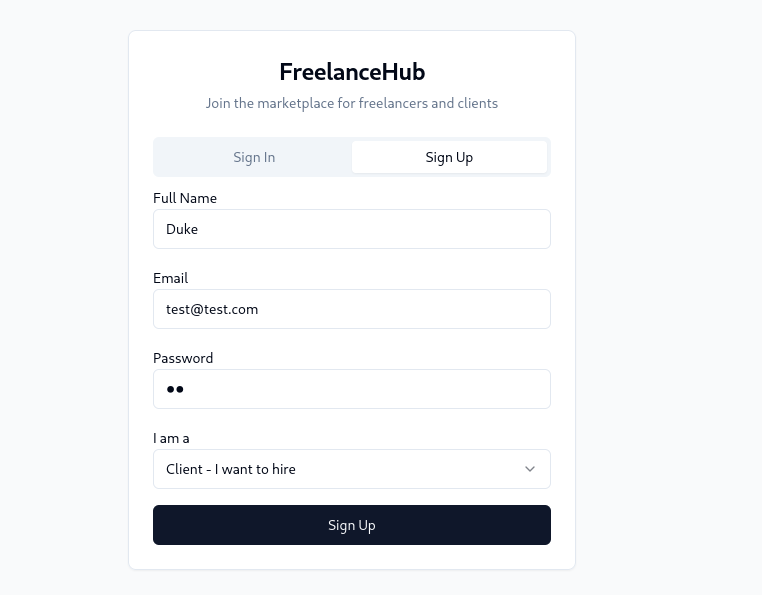 pushkarayengar/cve-2025-55854-poc
Proof-of-concept demonstrating a stored XSS vulnerability in FreelanceHub's profile bio field, with step-by-step reproduction and impact analysis.
 shemkumar/cve-2025-46181-xss
Reflected XSS vulnerability disclosure with PoC script and remediation guidance for an online appointment booking system. Includes vulnerable…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 mehran-seifalinia/cve-2023-37979
Python exploit script and Nuclei template for CVE-2023-37979, a reflected XSS vulnerability in the Ninja-forms WordPress plugin, enabling automated…
 my0723/cnvd-2022-27366__cve-2023-37621
Exploit for CVE-2023-37621 targeting unauthorized access in Fronius Datalogger Web 2.0.5-4, allowing attackers to retrieve sensitive device…