
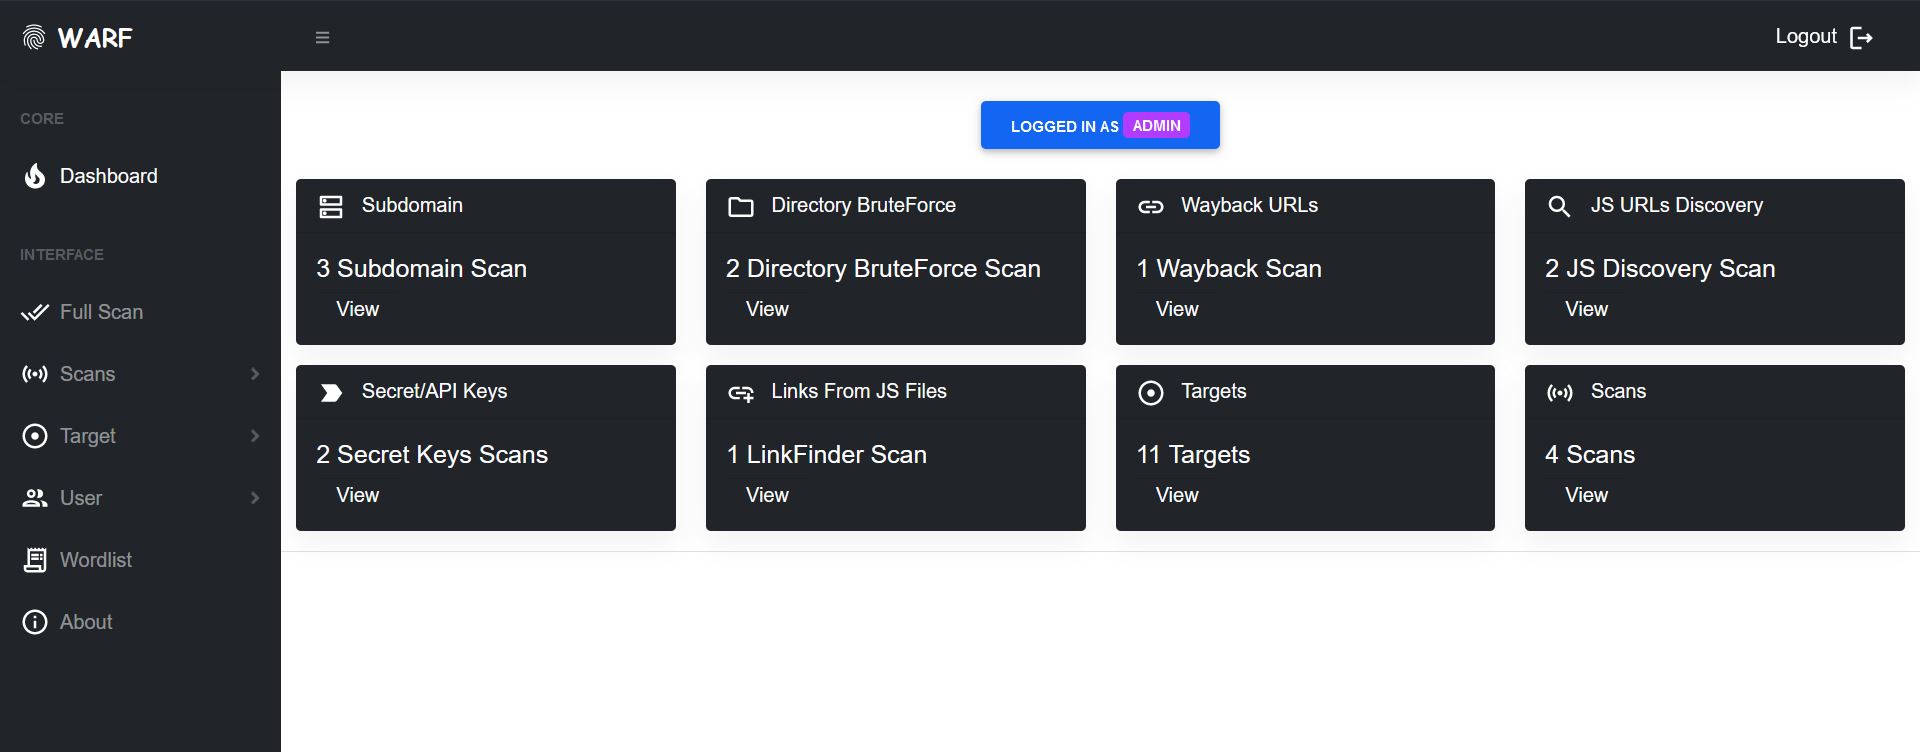
warf
 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
information-gatheringosintpenetration-testing+3
194
iamnihal/warfModular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 shellkraft/cve-2024-27914
Reflected XSS exploit PoC for GLPI (CVE-2024-27914) targeting unauthenticated debug mode. Provides a malicious link to trigger XSS in administrator's…
 zunak/cve-2023-49471
Proof-of-concept exploit for a Blind Server-Side Request Forgery (SSRF) vulnerability in Bar Assistant < 3.2.0, enabling authenticated attackers to…
 nles-crt/cve-2023-6895
Python script to scan websites for CVE-2023-6895 vulnerability. Sends crafted requests, checks responses, and logs exploitable URLs with progress bar…
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)