SharePointSecurityMonitor

A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…

A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…

Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…

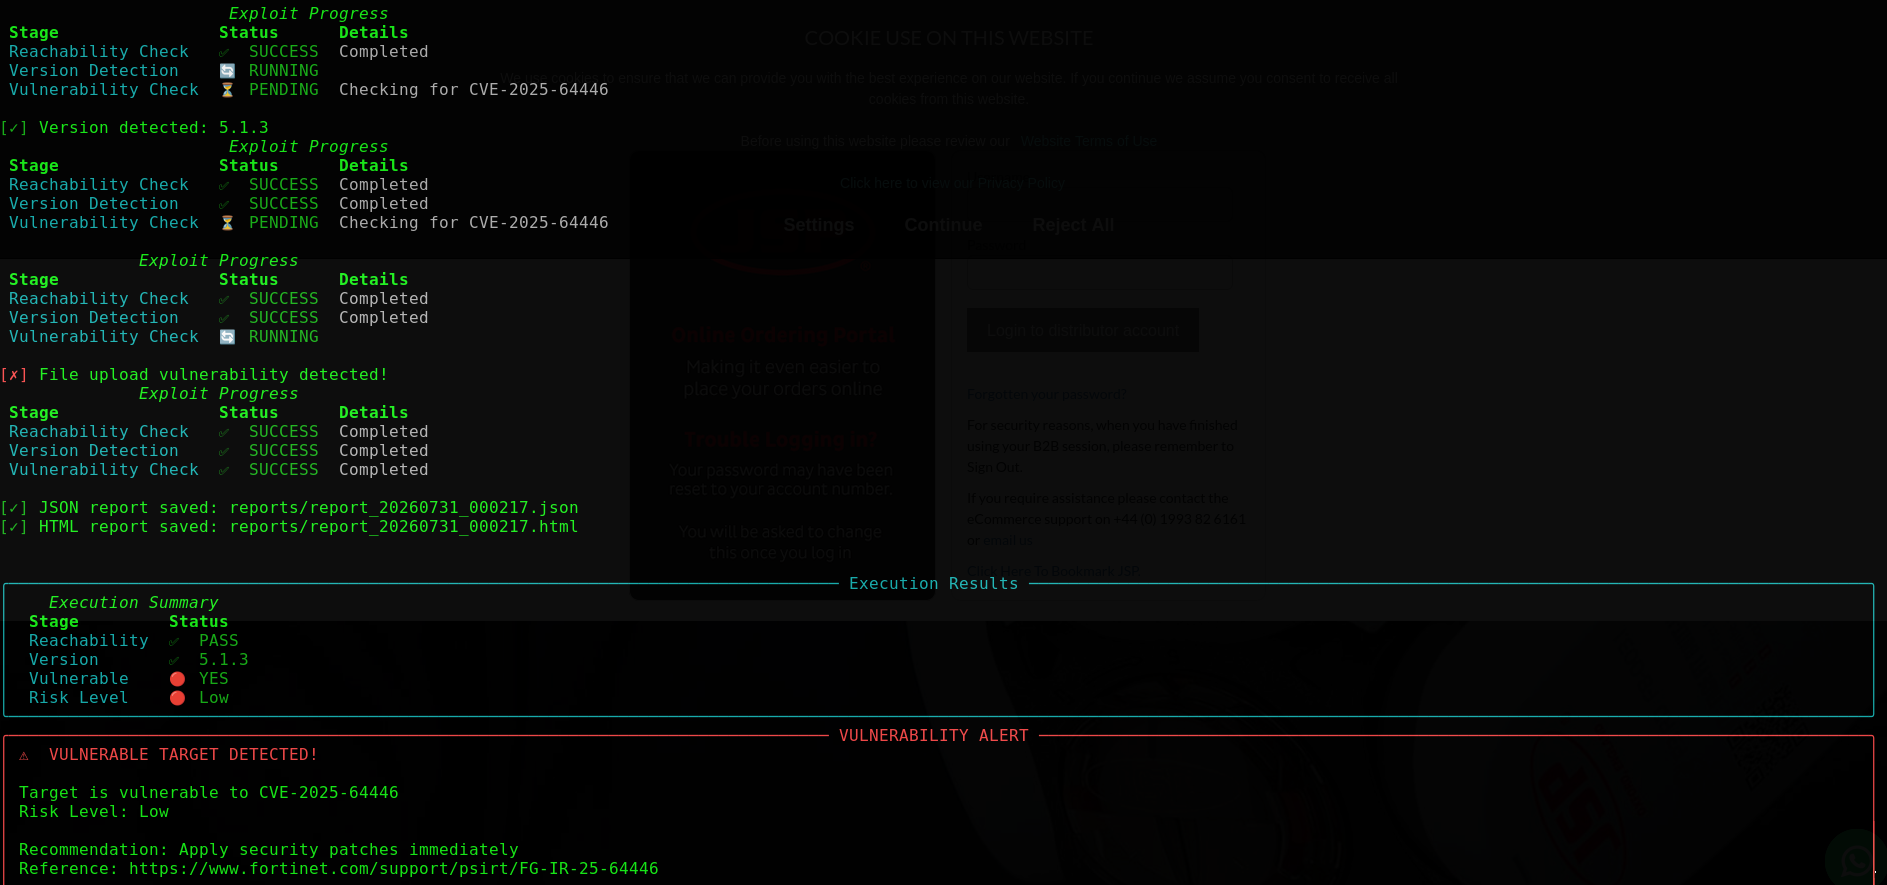
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…

Demonstration of CVE-2024-32002 exploitation with a Python-based proof-of-concept for vulnerability analysis and security testing.

🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…

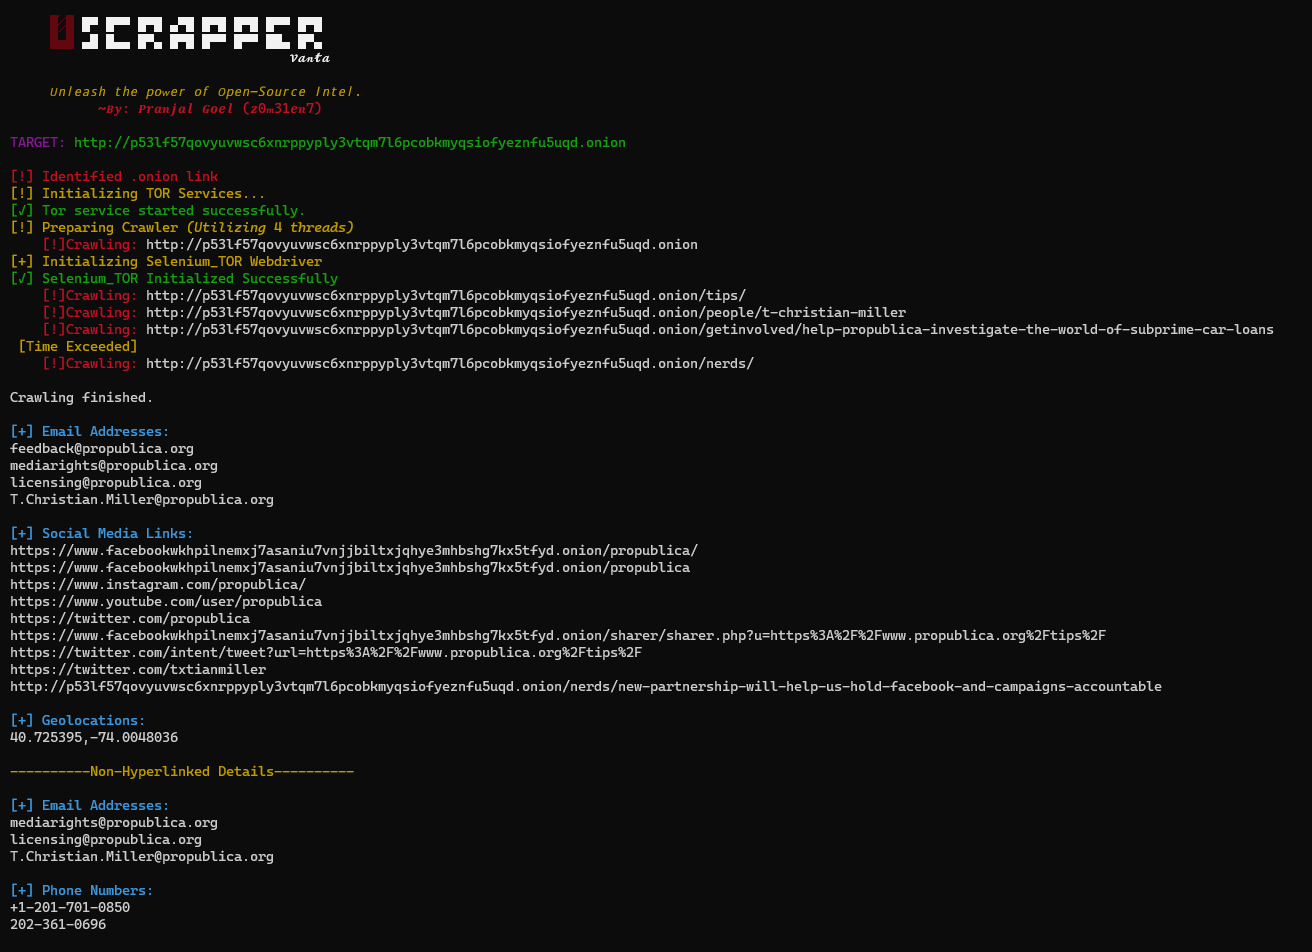
Uscrapper Vanta: Dive deeper into the web with this powerful open-source tool. Extract valuable insights with ease and efficiency, from both surface…

HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.

Perform advanced MiTM attacks on websites with ease 💉

Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC

Advanced Client-Side Prototype Pollution Scanner

High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…

High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…

Curated collection of V8 sandbox escape, bypass, and violation reports with issue tracker links, articles, papers, slides, and design documents for…

Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…

Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…

Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…


Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…