
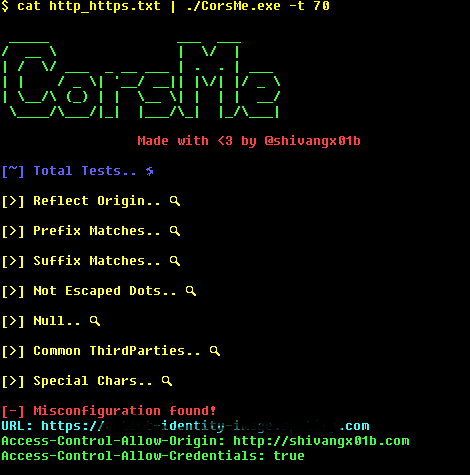
CorsMe
 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
misconfigurationpenetration-testingvulnerability-scanners+1
172
shivangx01b/corsmeCross Origin Resource Sharing MisConfiguration Scanner
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 rub-nds/corstest
A simple CORS misconfiguration scanner
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 timvisee/send
📬 Simple, private file sharing. Mirror of https://gitlab.com/timvisee/send
 pushsecurity/browser-identity-attacks-matrix
Offensive security drives defensive security. We're sharing a collection of SaaS attack techniques to help defenders understand the threats they…
 chithi-dev/chithi
The next generation encrypted file sharing project
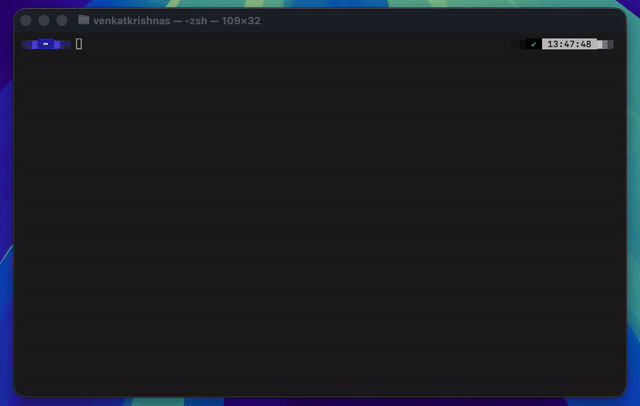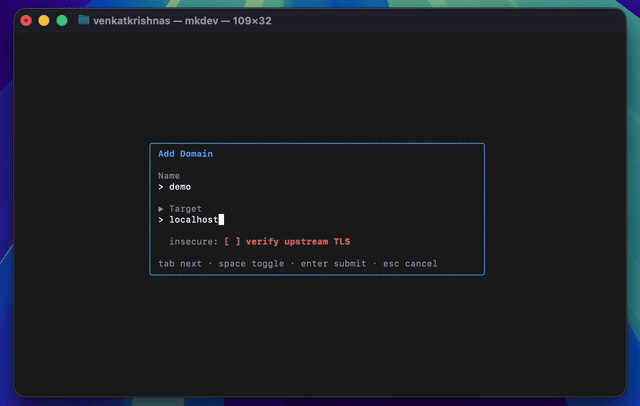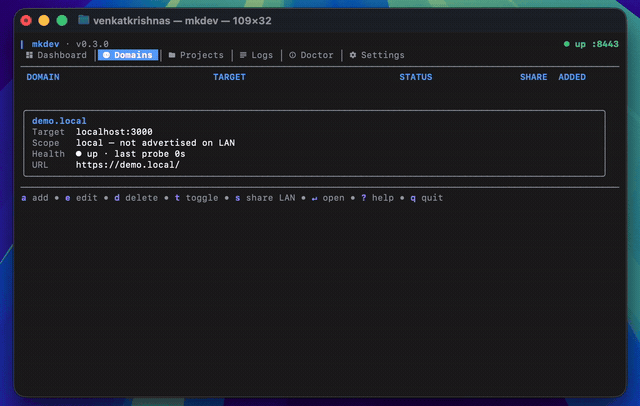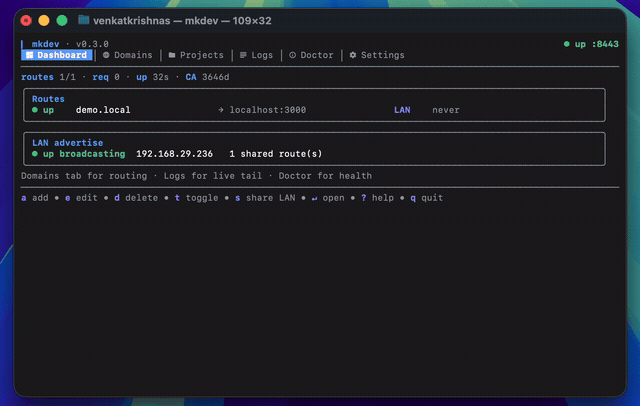 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 elandio-com/sharemylogin
Zero-Knowledge Credential Sharing
 katsana/remote-control
Grant remote access to user account without sharing credentials
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…