
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
49 results
Addon preview

Addon

GitHubclearurls/addon

ClearURLs is an add-on based on the new WebExtensions technology and will automatically remove tracking elements from URLs to help protect your…
privacyweb-security
5.0k1 year ago
wp-allowed-hosts preview

wp-allowed-hosts

GitHubalash3al/wp-allowed-hosts

a plugin that protects your wp site from the CVE-2017-8295 vulnerability
authentication-authorizationdefensive-toolsmisconfiguration+2
29 years ago
keycloak__keycloak_CVE-2014-3656_1-0-5-Final preview

keycloak__keycloak_CVE-2014-3656_1-0-5-Final

GitHubshoucheng3/keycloak__keycloak_cve-2014-3656_1-0-5-final

Open-source identity and access management solution providing authentication, user federation, single sign-on, and fine-grained authorization for…
api-securityauthentication-authorizationcloud-security+3
1 year ago
ReconAIzer preview

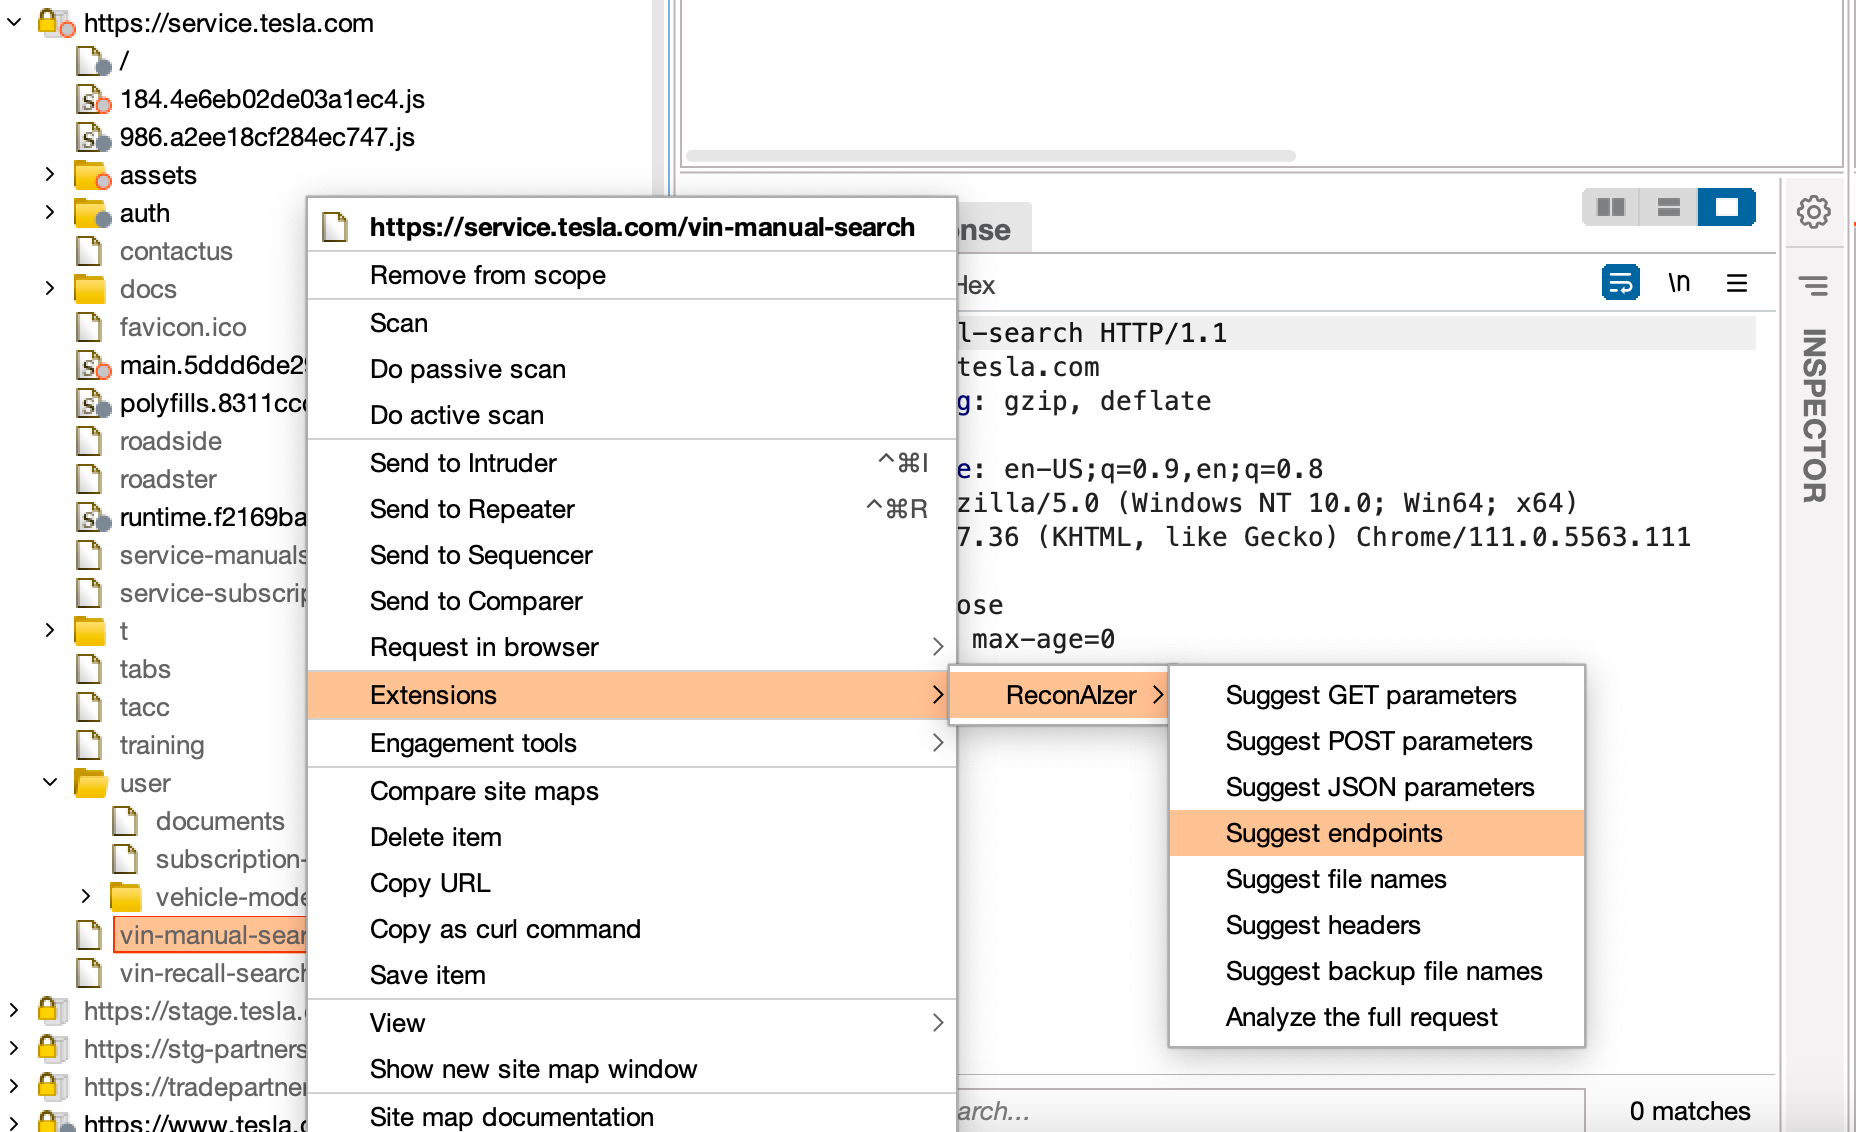
ReconAIzer

GitHubhisxo/reconaizer

A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
ai-securityinformation-gatheringreconnaissance+1
9073 years ago
Http11Probe preview

Http11Probe

GitHubmda2av/http11probe

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
api-security-testingfuzzingmisconfiguration+2
302 days ago
log-add-http-post-bodies preview

log-add-http-post-bodies

GitHubcorelight/log-add-http-post-bodies

Add POST body excerpt to Bro's HTTP log

digital-forensicslog-analysisnetwork-security+1
149 months ago
test_cve-2023-46747 preview

test_cve-2023-46747

GitHubnvansluis/test_cve-2023-46747

Python script to test F5 BIG-IP for CVE-2023-46747 and add an administrator account if vulnerable.
cloud-securityconfiguration-auditingexploitation+3
72 years ago
CVE-2025-29927-check preview

CVE-2025-29927-check

GitHubc0dejump/cve-2025-29927-check

script to check cve "CVE-2025-29927" while waiting to add it to HExHTTP

exploitationinformation-gatheringpenetration-testing+2
31 year ago
CVE-2022-32114 preview

CVE-2022-32114

GitHubbypazs/cve-2022-32114

An unrestricted file upload vulnerability in the Add New Assets function of Strapi v4.1.12 allows attackers to execute arbitrary code via a crafted…
exploitationpenetration-testingvulnerability-analysis+2
14 years ago
CVE-2020-23586 preview

CVE-2020-23586

GitHubhuzaifahussain98/cve-2020-23586

CSRF allows to Add Network Traffic Control Type Rule
exploitationmisconfigurationpenetration-testing+3
13 years ago
CVE-2017-12542 preview

CVE-2017-12542

GitHubvijayshankar22/cve-2017-12542

This script checks if an HP iLO server is vulnerable and can add an admin user
authenticationexploitationpenetration-testing+2
11 months ago
CVE-2025-56219 preview

CVE-2025-56219

GitHubsaykino/cve-2025-56219

Detailed advisory for CVE-2025-56219, a rate-limiting flaw in Ascertia SigningHub's Add User API, enabling automated user creation and denial of…
api-securitycurated-resourceseducation+2
11 months ago
CVE-2023-26982 preview

CVE-2023-26982

GitHubbypazs/cve-2023-26982

Trudesk v1.2.6 was discovered to contain a stored cross-site scripting (XSS) vulnerability via the Add Tags parameter under the Create Ticket…
exploitationpenetration-testingvulnerability-analysis+2
3 years ago
CVE-2023-43355-CMSmadesimple-Reflected-XSS---Add-user preview

CVE-2023-43355-CMSmadesimple-Reflected-XSS---Add-user

GitHubsromanhu/cve-2023-43355-cmsmadesimple-reflected-xss---add-user

Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the password…

exploitationpenetration-testingvulnerability-analysis+2
3 years ago
CVE-2024-33209 preview

CVE-2024-33209

GitHubparagbagul111/cve-2024-33209

FlatPress 1.3. is vulnerable to Cross Site Scripting (XSS). An attacker can inject malicious JavaScript code into the "Add New Entry" section, which…

exploitationpenetration-testingvulnerability-analysis+2
1 year ago
AWSGoat preview

AWSGoat

GitHubine-labs/awsgoat

AWSGoat : A Damn Vulnerable AWS Infrastructure
cloud-infrastructure-securitycloud-securitycontainer-security+6
2.0k1 year ago
destroylist preview

destroylist

GitHubphishdestroy/destroylist

Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats

curated-resourcesdefensive-toolsdns-analysis+8
1.9k5h 26m ago
HackBar preview

HackBar

GitHubd3vilbug/hackbar

HackBar plugin for Burpsuite

penetration-testingwaf-bypassweb-application-exploitation+1
1.6k5 years ago
Previous123Next