
CVE-2026-38360
 a1ohadance/cve-2026-38360
Advisory: CVE-2026-38360 path traversal (CWE-22) in dash-uploader (Python/PyPI)
code-analysiseducationexploitation+3
25 months ago
a1ohadance/cve-2026-38360Advisory: CVE-2026-38360 path traversal (CWE-22) in dash-uploader (Python/PyPI)
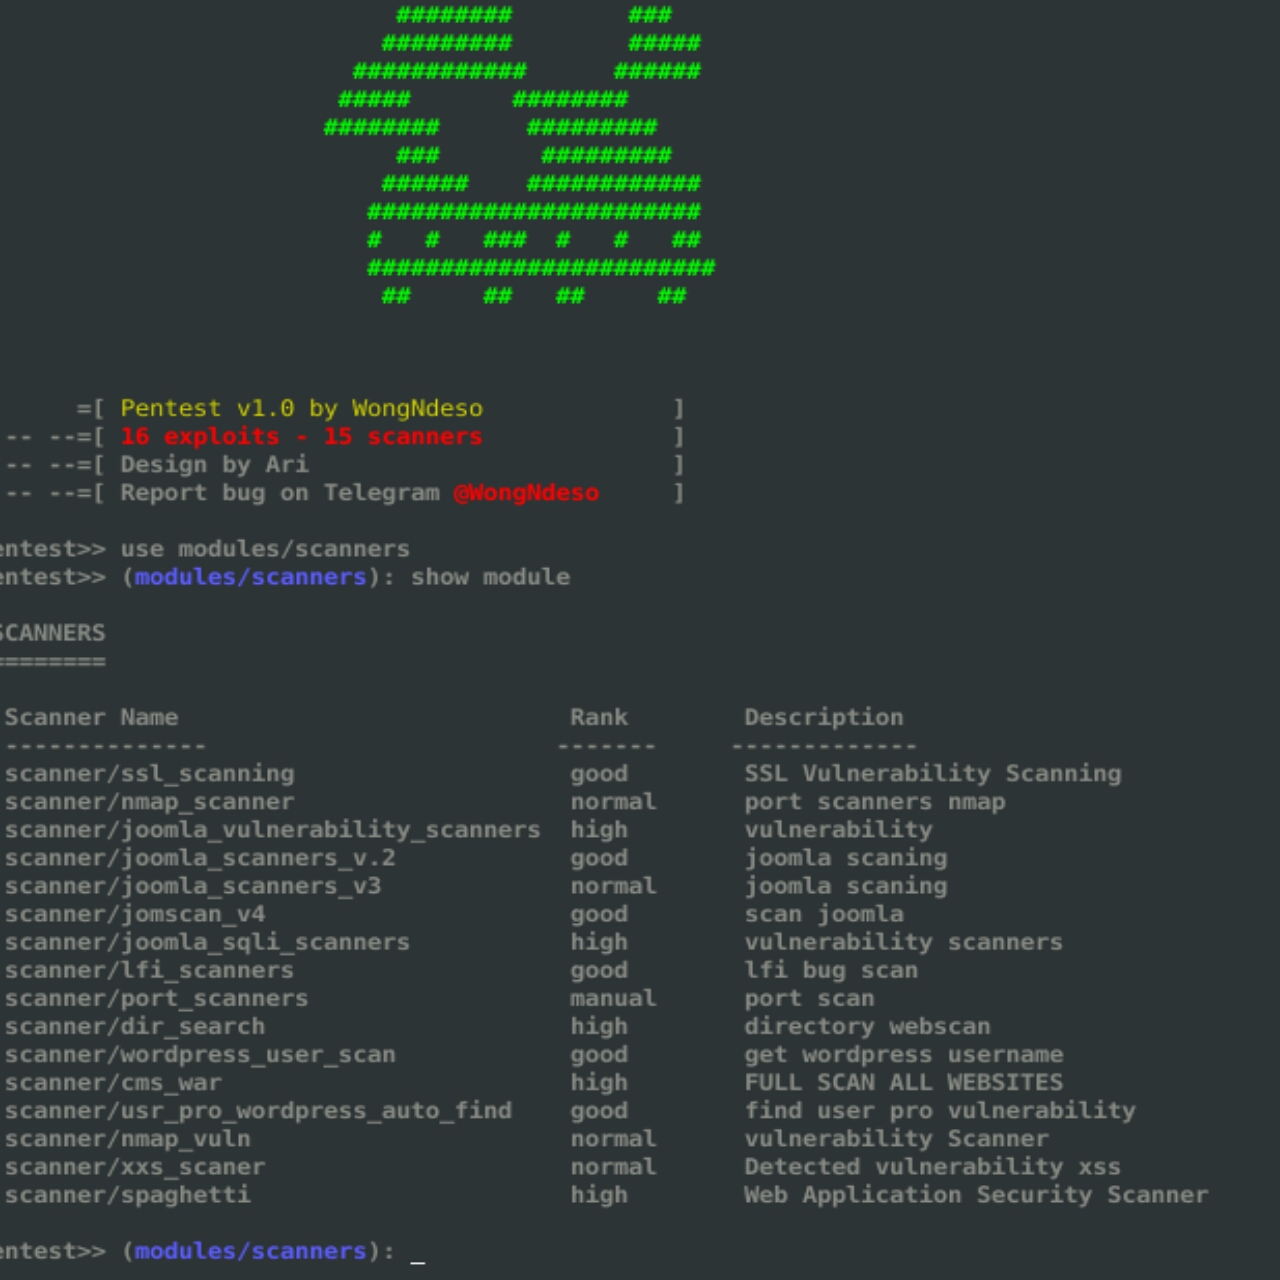 pikpikcu/pentest-tools-framework
Pentest Tools Framework is a database of exploits, Scanners and tools for penetration testing. Pentest is a powerful framework includes a lot of…
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 shadowforge-cyber/cve-2026-104286-poc
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 anestisb/webacoo
Web Backdoor Cookie Script-Kit

 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 nxploited/cve-2026-0920-
LA-Studio Element Kit for Elementor <= 1.5.6.3 - Unauthenticated Privilege Escalation via Backdoor to Administrative User Creation via lakit_bkrole…
 mrsqar-ye/door404
Web application backdoor builder
 edgarloyola/cve-2021-40906
Proof-of-concept for a reflected XSS vulnerability in CheckMK Management Web Console (versions 1.5.0 to 1.6.0), enabling session theft or backdoor…
 chybeta/web-security-learning
Web-Security-Learning
 puvipavan/cve-2024-2667
This is POC for CVE-2024-2667 (InstaWP Connect – 1-click WP Staging & Migration <= 0.1.0.22 - Unauthenticated Arbitrary File Upload)