
CVE-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…

This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…

Proof-of-concept exploit for CVE-2024-33911, a post-authenticated SQL injection vulnerability in The School Management WordPress plugin v10.3.4,…

Proof-of-concept exploit for CVE-2024-27316, an HTTP/2 CONTINUATION flood vulnerability in Apache httpd, demonstrating resource exhaustion via…

Proof-of-concept exploit for CVE-2024-2876, a critical SQL injection in Email Subscribers by Icegram Express WordPress plugin, allowing…

Exploit for CVE-2024-4879 affecting Vancouver, Washington DC Now and Utah Platform releases

Exploit For: CVE-2024-40111: Stored Cross-Site Scripting (XSS) in Automad 2.0.0-alpha.4

Exploit For: CVE-2024-39123: Stored XSS in Calibre-web 0.6.21

WordPress的News and Blog Designer Bundle插件在1.1及之前所有版本中,存在通过template参数导致的本地文件包含漏洞。该漏洞使得未经身份验证的攻击者能够包含并执行服务器上的任意.php文件,从而运行这些文件中的任何PHP代码。在允许上传和包含.php文件类型…

poc for the rst dos attack discovered in 2023

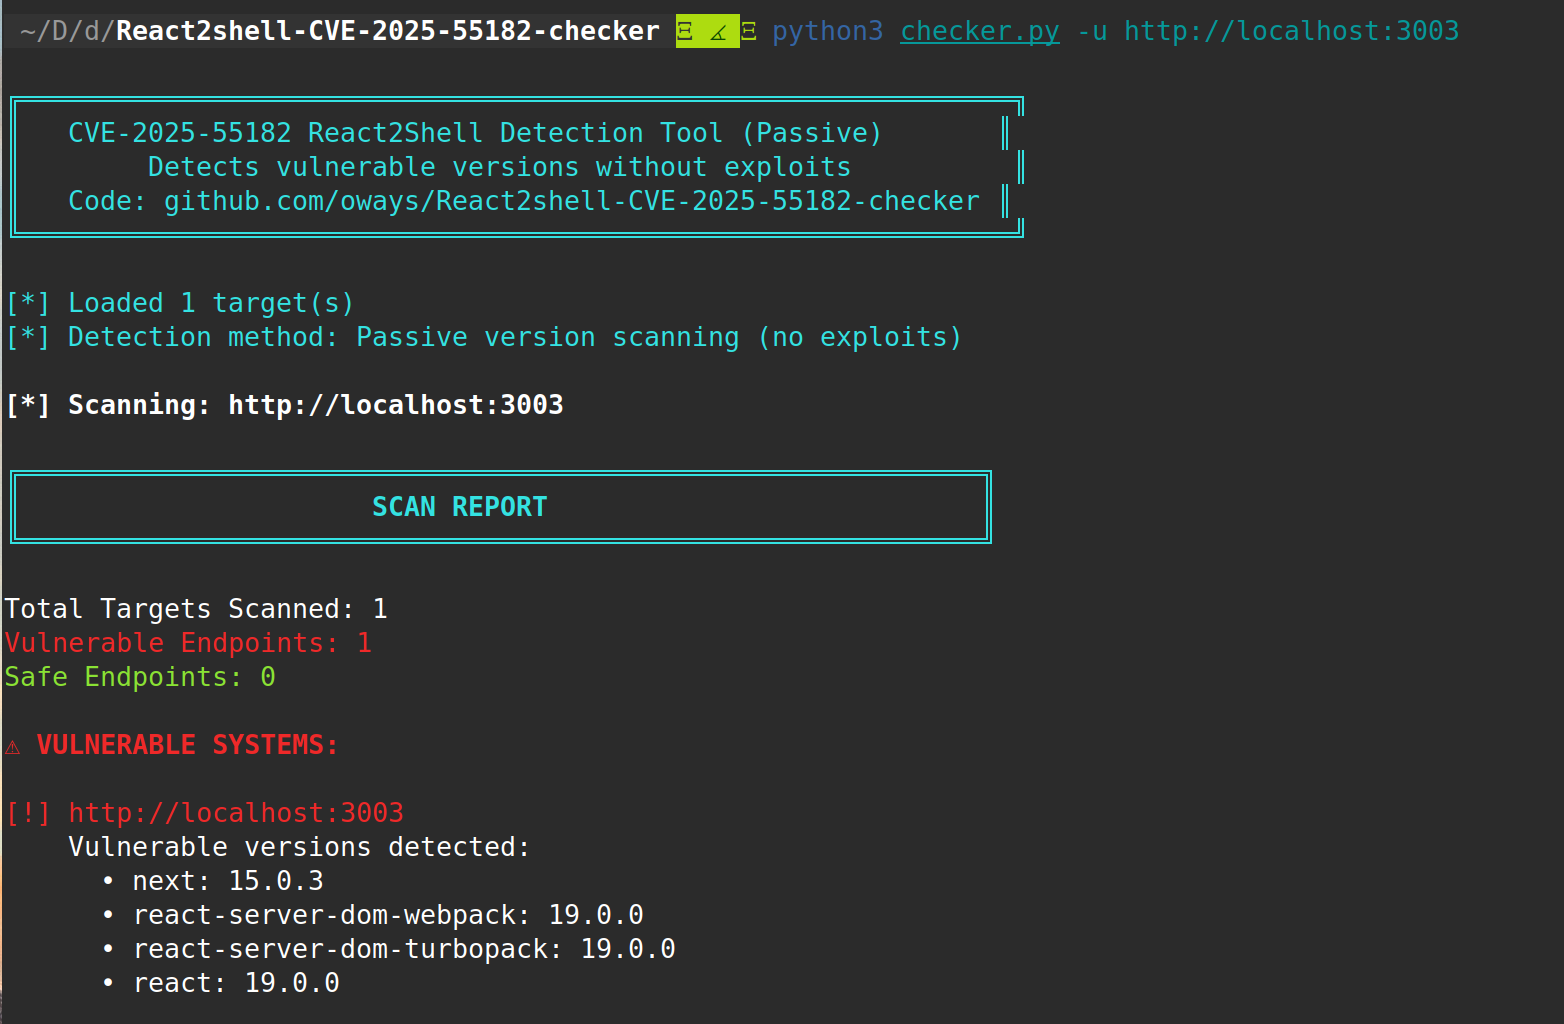
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

Docker container implementing tests for CVE-2016-2107 - LuckyNegative20

Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…

Detection for CVE-2025-7775

Proof-of-concept for reflected cross-site scripting in Academy LMS versions before 5.9.1, triggered via the search?query parameter to execute…

Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…

eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Deletion

Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…

Mitigated version for CVE-2016-1000027 spring web.