
CVE-2025-63498
 xryptoh/cve-2025-63498
Stored XSS proof-of-concept for SOGo groupware, exploiting the 'Remember Username' cookie to inject JavaScript payloads via the login endpoint.
exploitationpenetration-testingvulnerability-analysis+2
2
xryptoh/cve-2025-63498Stored XSS proof-of-concept for SOGo groupware, exploiting the 'Remember Username' cookie to inject JavaScript payloads via the login endpoint.
 delbertgiovanni/test-xss-swagger-cve-2019-1749
PoC for testing reflected XSS in Swagger UI via CVE-2019-1749; sends crafted payloads and verifies vulnerable endpoints with minimal setup.
 1337skid/cve-2026-51565
Security Advisory for CVE-2026-51565
 scrt/cve-2024-53703-poc
POC for exploiting CVE-2024-53703, a stack-based buffer overflow in SonicWall SMA mod_httprp.so
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
 forceea001/cve-2024-40898-ssl-bypass-detection
This Python script is a Proof-of-Concept (PoC) scanner for detecting the vulnerability CVE-2024-40898, which affects Apache HTTP Server’s SSL…
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
 nk7667/-linx-server-vulnerability-report
Public disclosure for CVE-2026-52100 (CSRF) & CVE-2026-52101 (SSRF) in linx-server. MITRE assigned the CVEs; this repo provides a public reference…
 w5m1n9/nginx-ngx_http_rewrite_module-heap-buffer-overflow-cve-2026-9256
Proof-of-concept for CVE-2026-9256, a heap buffer overflow in NGINX's ngx_http_rewrite_module. Demonstrates worker crash and denial of service via…
 madhusudhan-in/cve_2023_44487-rapid_reset
A comprehensive Python testing tool for CVE-2023-44487, the HTTP/2 Rapid Reset vulnerability. This enhanced version provides granular control over…
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 rxerium/cve-2025-37164
Detection for CVE-2025-37164
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
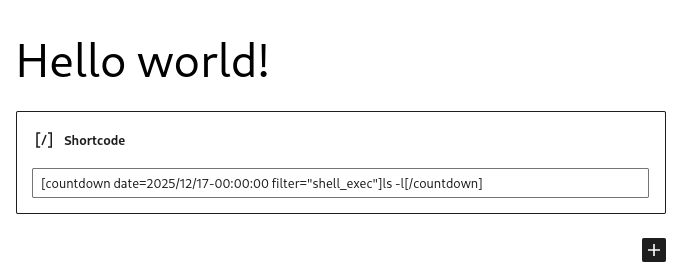 nimisha17/poc-cve-2025-9519
Proof-of-concept exploit for CVE-2025-9519, demonstrating remote code execution in WordPress Easy Timer plugin via a crafted shortcode filter, with…
 rat-c/cve-2024-1512
PoC for CVE-2024-1512 in MasterStudy LMS WordPress Plugin.
 hackpatato/cve-2026-33057---mesop-unauthenticated-rce-poc-and-yara-rules
Proof-of-concept exploit for CVE-2026-33057, an unauthenticated RCE in Mesop, with accompanying YARA rules for detection.
 typedefabcd1234ntd/cve-2026-19500-poc
Proof-of-concept for CVE-2026-19500, a DoS vulnerability in the SureForms WordPress plugin that exhausts server resources via oversized key-value…
 swornim619/cve-2026-65650
PoC for CVE-2026-65650 - Elgg avatar upload DoS