
CVE-2026-30252
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
educationexploitationpapers-research+2
venablee/cve-2026-30252The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 bishopfox/vulnerablegwtapp
An intentionally-vulnerable GWT-based web application to test tooling and techniques
 brianwrf/nagascan
NagaScan is a distributed passive vulnerability scanner for Web application.
 smarttfoxx/cve-2025-45778
A stored cross-site scripting (XSS) vulnerability in The Language Sloth Web Application v1.0 allows attackers to execute arbitrary javascript or HTML…
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 owasp/wafec
Structured evaluation criteria framework for assessing Web Application Firewalls (WAFs), enabling users, vendors, and third parties to compare…
 usernameisunavailable-cell/bili-cracker
Exploit tool leveraging CVE-2026-350234 to obtain bilibili membership privileges, demonstrating web application vulnerability exploitation.
 4chech/cve-2026-41242
Proof-of-concept exploit for CVE-2026-41242 in a Node.js web application, demonstrating the vulnerability and potential impact.
 mrsqar-ye/door404
Web application backdoor builder
 shoucheng3/dspace__dspace_cve-2016-10726_4-4
Repository containing the DSpace 4.4 source code with a focus on CVE-2016-10726, providing a reference for vulnerability analysis and educational…
 chandraprarikraj/cve-2023-51214
Proof-of-concept for CVE-2023-51214: a stored XSS vulnerability in a PHP-based activity log web application allowing remote code execution via…
 joojiii/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 in Next.js 15.2.0, demonstrating a specific web application vulnerability for testing and educational…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 adindrabkin/llama_facts
Web application vulnerable to Python3 Flask SSTI (CVE-2019-8341)
 zecure/shadowd
The Shadow Daemon web application firewall server
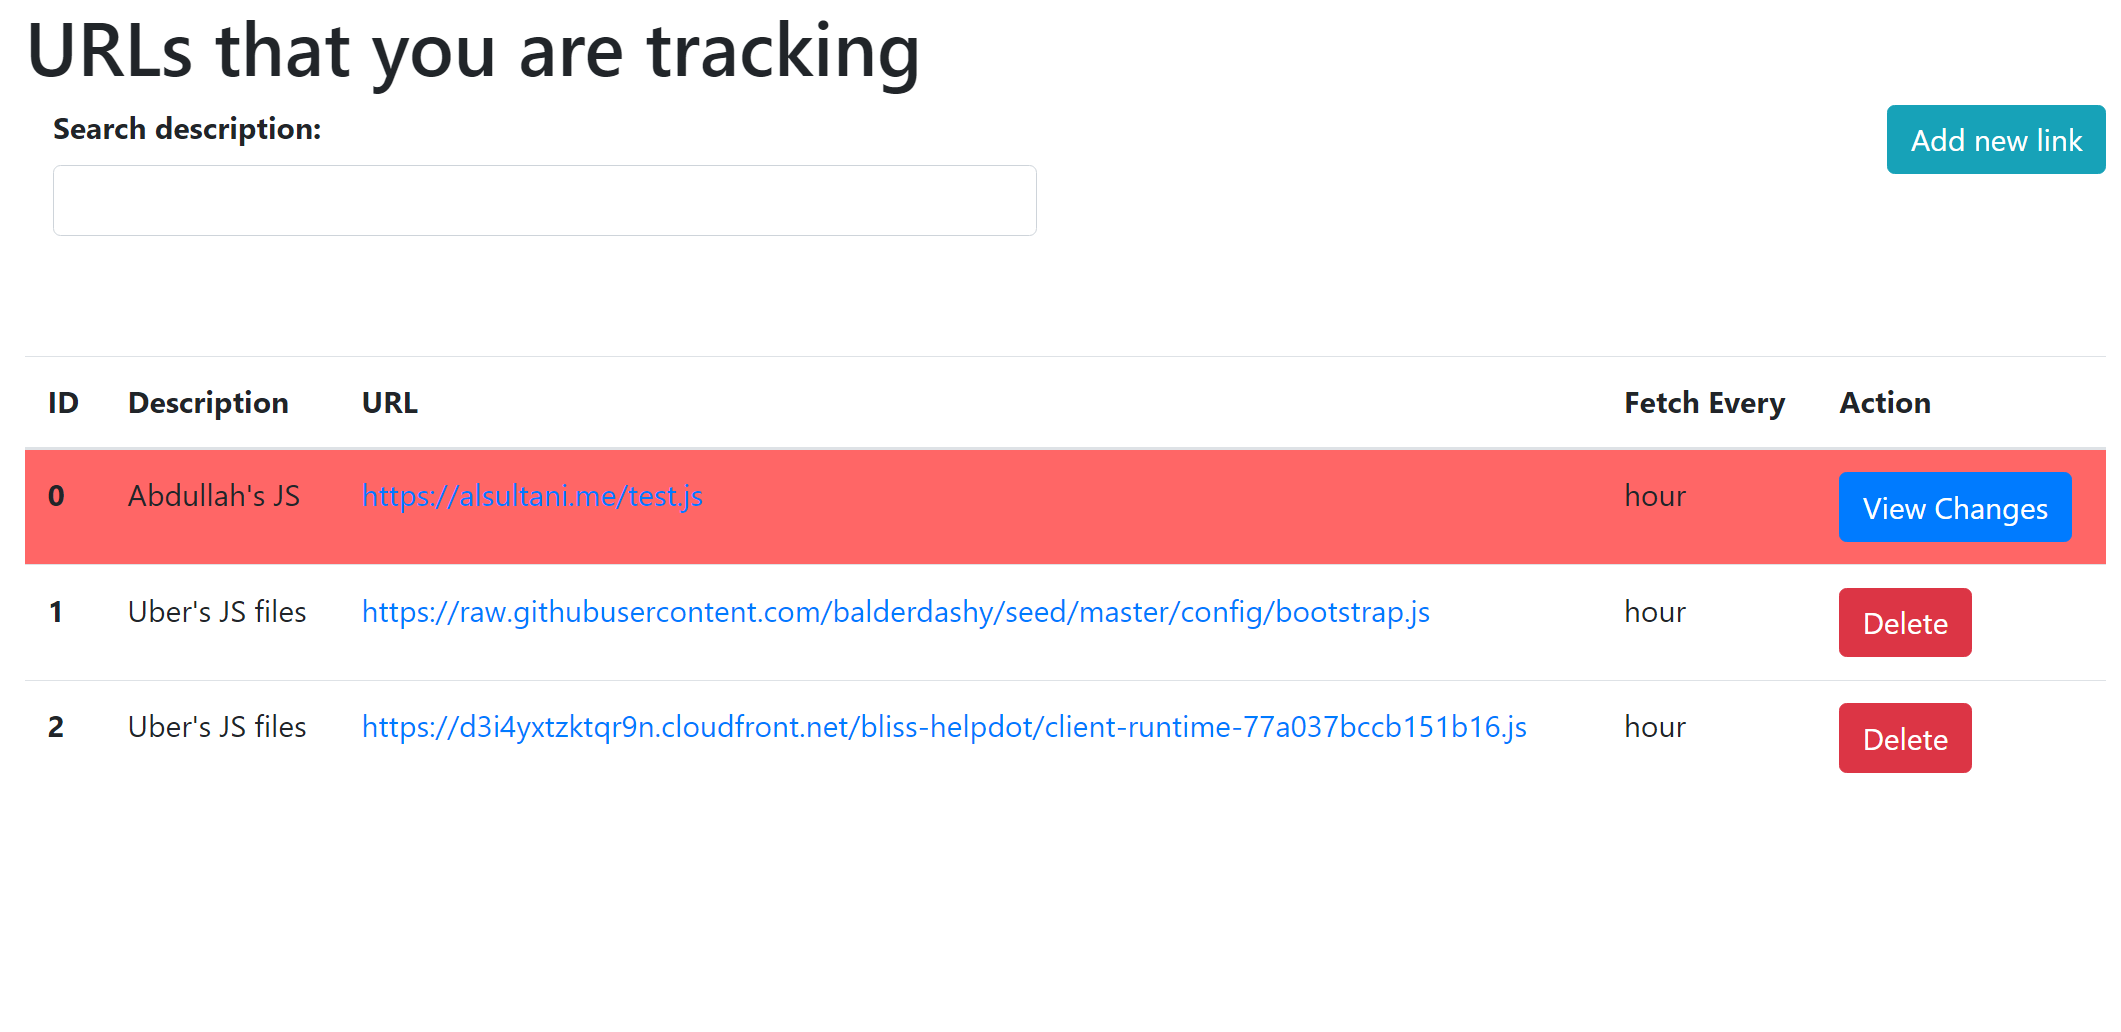 al-sultani/url-tracker
Change monitoring app that checks the content of web pages in different periods.
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10