

zap-api-rust
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
api-securitypenetration-testingvulnerability-scanners+3
15
zaproxy/zap-api-rustRust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 azurit/crsprober
Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…
 mehedi-hasan-sami98/dvwa-zap-pentest
Web application security assessment of DVWA using OWASP ZAP — vulnerability scanning, RCE (CVE-2012-1823) analysis, and remediation report.
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 klairmanraj/multi-vlan-enterprise-network-security-infrastructure
Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
 axselll/cve-2025-20384
Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.
 waburig/open-worldwide-application-security-project-owasp-
Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 khaliquesx/cve-2024-48415
Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
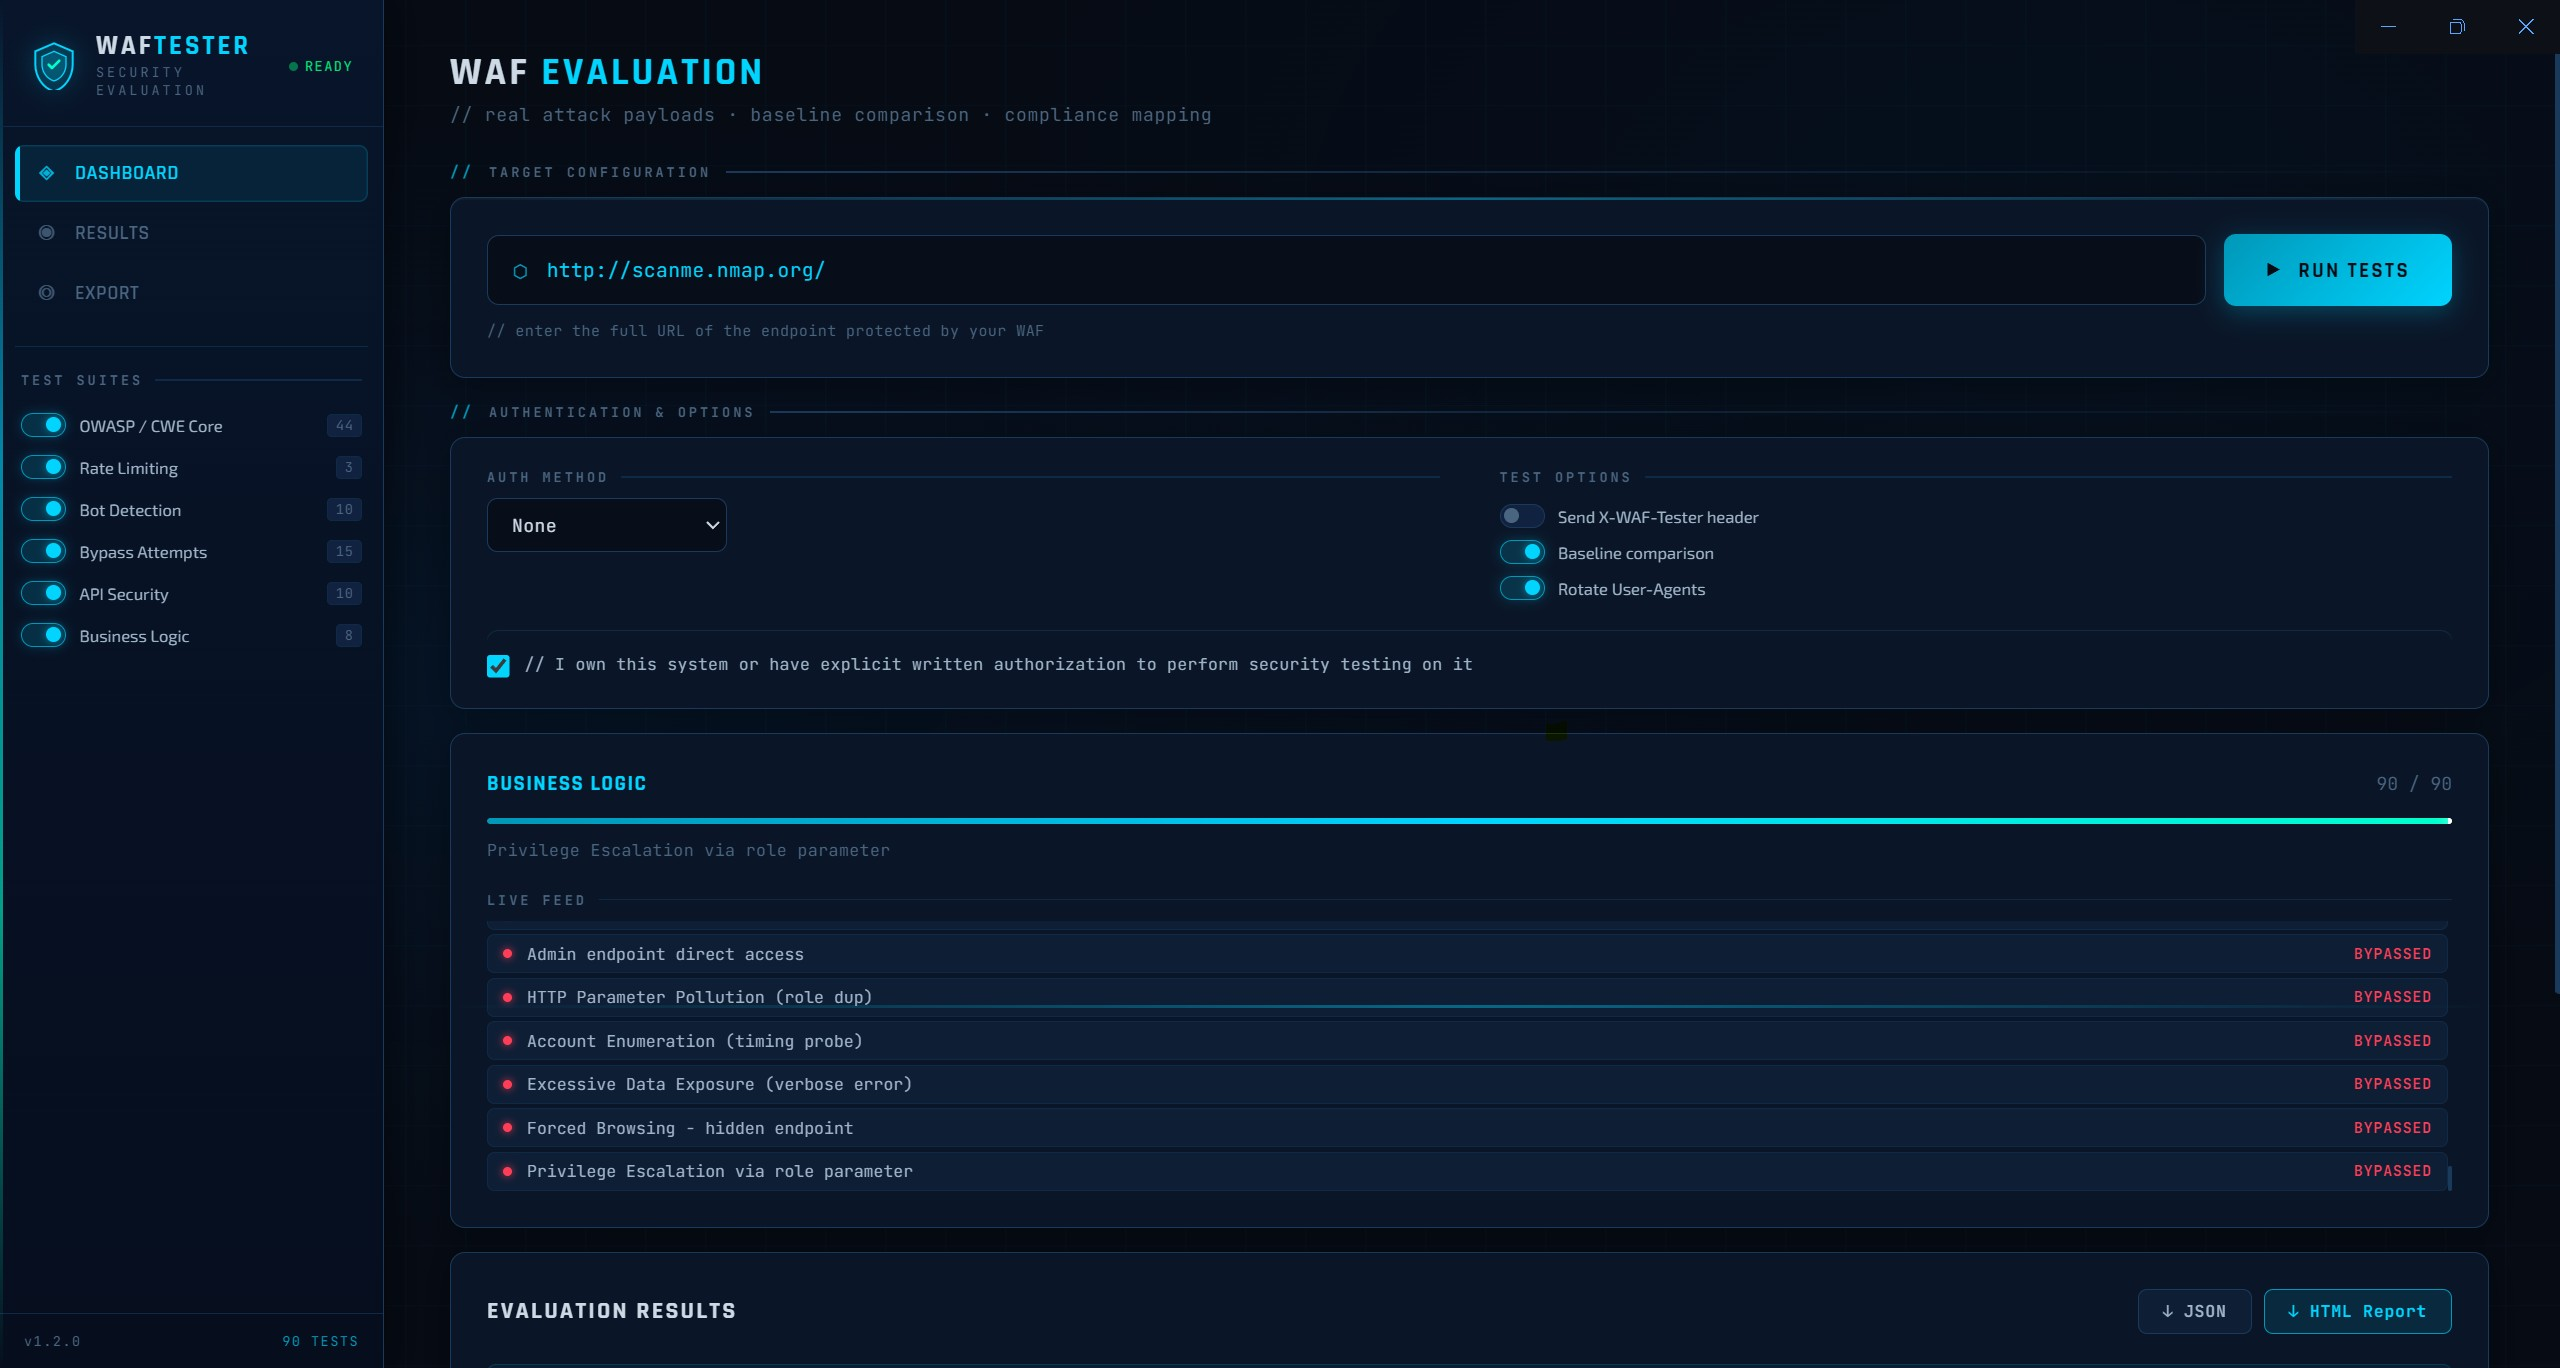 kpomin57/waf-tester
A program for testing WAF functionality