

web-hacking-playground
 takito1812/web-hacking-playground
Web application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.
ctfeducationlabs-practice+4
172
takito1812/web-hacking-playgroundWeb application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
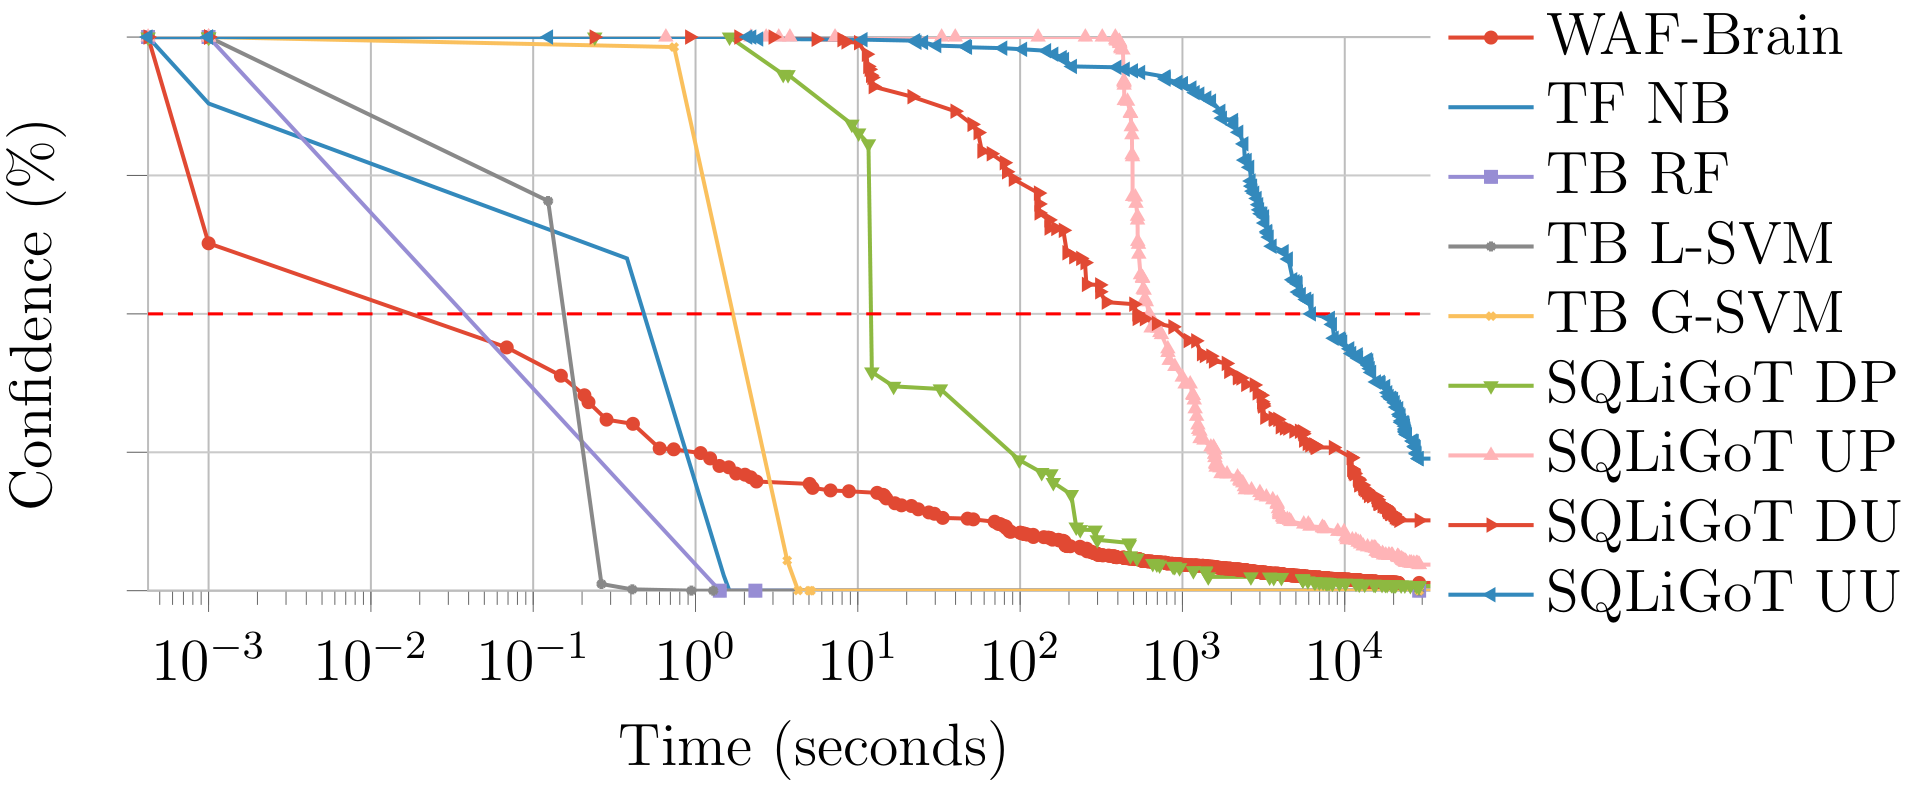 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/asvs
Application Security Verification Standard
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 hakluke/hakrawler
Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 nccgroup/abptts
TCP tunneling over HTTP/HTTPS for web application servers
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
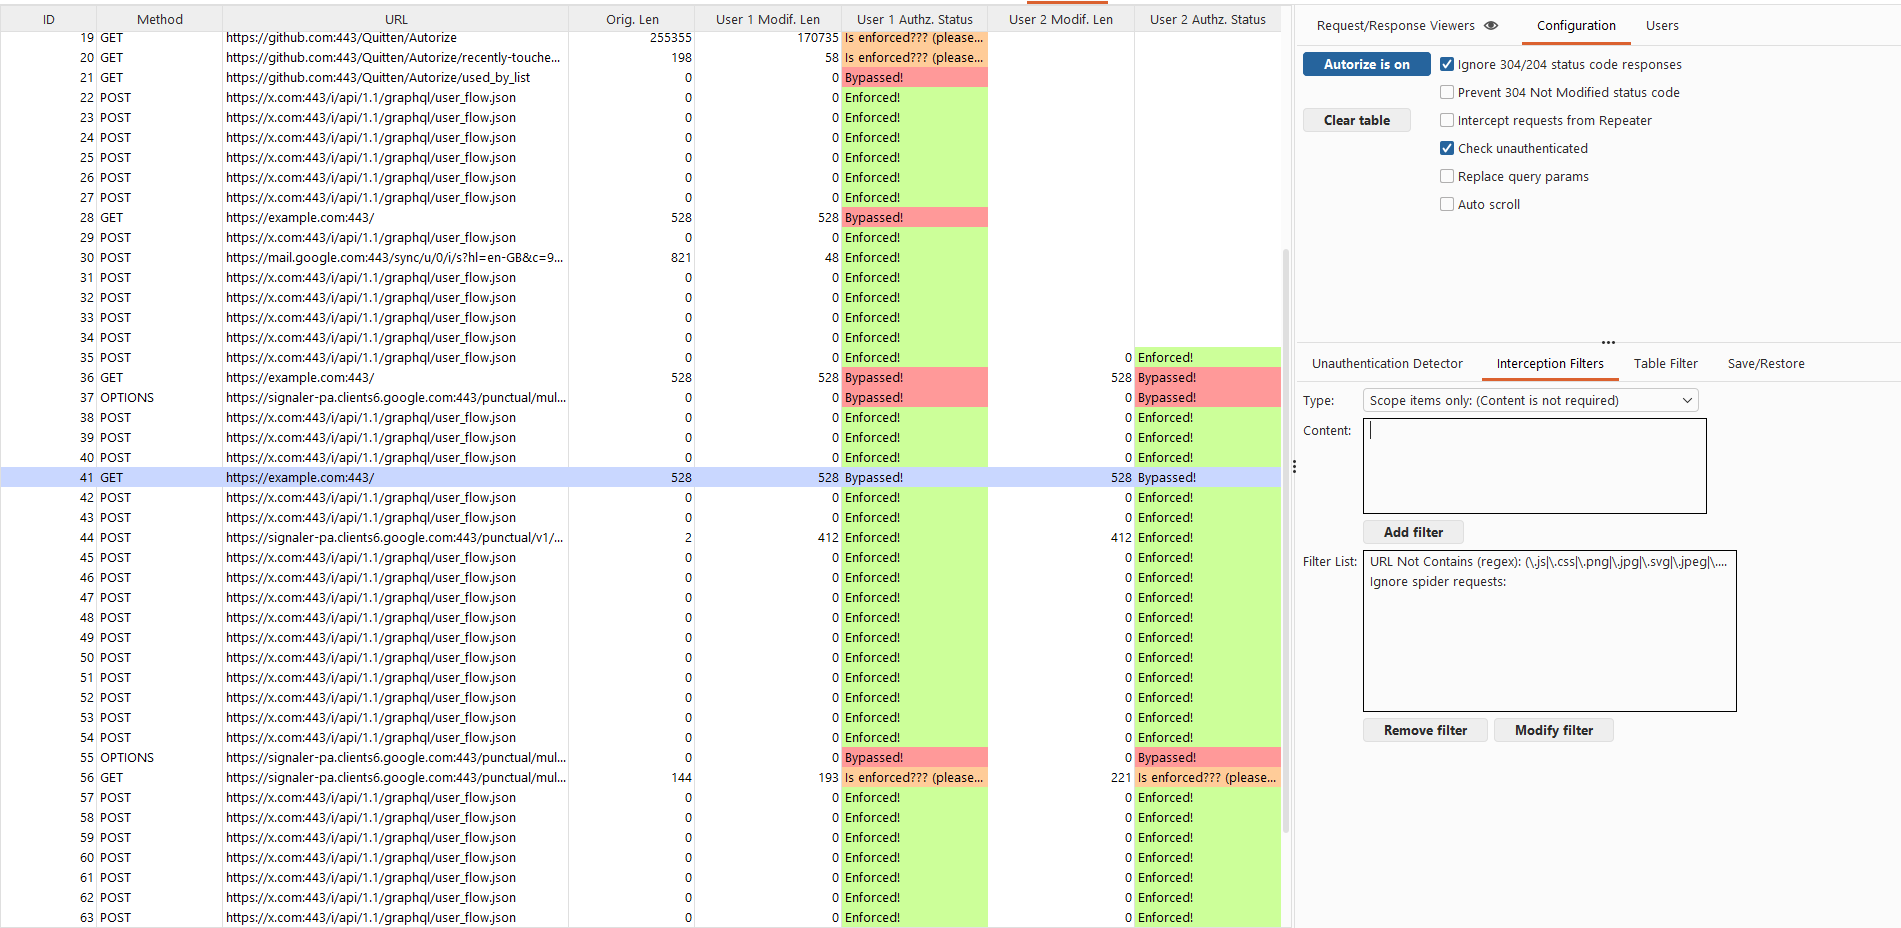 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.