CVE-2019-17638-Jetty

Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…

Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…

Docker lab for reproducing and studying CVE-2023-44487 (HTTP/2 Rapid Reset) for thesis research, providing a controlled environment for vulnerability…

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

Cyber Panel - The hosting control panel for OpenLiteSpeed

Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…

Proof-of-concept exploit for CVE-2025-47445, a path traversal vulnerability in the WordPress Eventin plugin. Includes setup instructions for a local…

Lab with PoC

PoC steps for this vulnerability

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…

This repository is for the Testing ASP.NET ViewState with YSoNet (YSoSerial.NET) workshop.

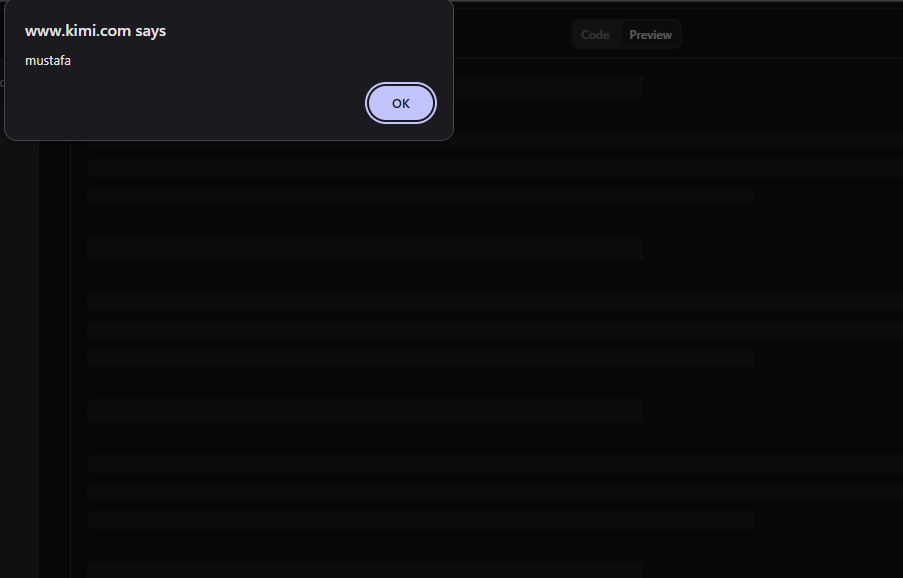
Detailed disclosure of a stored XSS vulnerability in Kimi AI v1.0's Preview tab, including attack scenario, PoC, and remediation guidance for…

Self-contained Docker lab demonstrating CVE-2023-24329, a Python urllib parser differential that bypasses URL scheme and host filters, with…

Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…

Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…

Apache HTTPd (2.4.49) – Local File Disclosure (LFI)

Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…

Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…