
CVE-2015-7214
 llamakko/cve-2015-7214
Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
exploitationpenetration-testingvulnerability-analysis+2
13
llamakko/cve-2015-7214Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 aleksejspopovs/cve-2020-16012
PoC for CVE-2020-16012, a timing side channel in drawImage in Firefox & Chrome
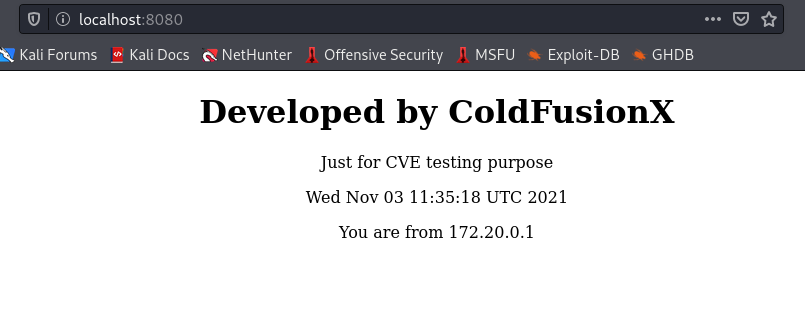 coldfusionx/cve-2021-34429
POC for CVE-2021-34429 - Eclipse Jetty 11.0.5 Sensitive File Disclosure
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 abraxas/gitlab-webhook-0net-ssrf
Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 josephfarah-ciso/cve-2026-9999-exploit
Proof-of-concept and GLSL fuzzer for CVE-2026-9999 in Chrome's ANGLE/Metal WebGL backend, with build fingerprinting, curated shaders, and crash…
 lulztigre/cve-2026-67363-67364
PoC and detection templates for pre-auth RCE and payment tampering in Balbooa Forms (Joomla), including Python exploit and Nuclei detection template.
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
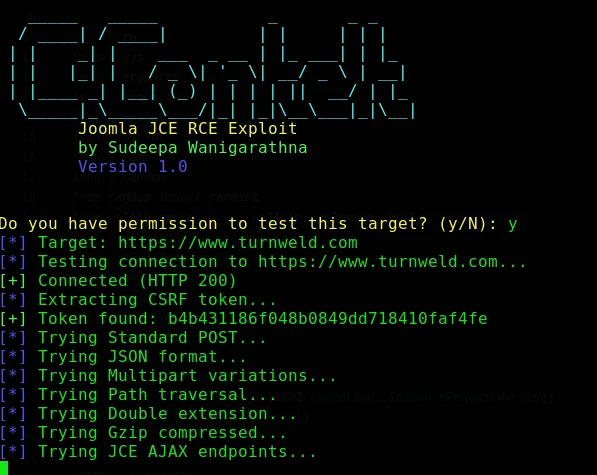 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 zprototype/cve-2023-29808
Reflected cross-site scripting (XSS) proof-of-concept exploit for CVE-2023-29808 targeting the /index.php?map=overview&findme= endpoint in cmaps…
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
 dewankpant/cve-2017-16568
Proof-of-concept exploit for a persistent XSS vulnerability in Logitech Media Server 7.9.0, demonstrating HTML code injection via the Radio URL field.