

CVE-2023-6444-POC
 wayne-ker/cve-2023-6444-poc
Proof of concept on Unauthenticated Administrator Email Disclosure CVE-2023-6444
exploitationinformation-gatheringpenetration-testing+2
wayne-ker/cve-2023-6444-pocProof of concept on Unauthenticated Administrator Email Disclosure CVE-2023-6444
 geraldoalcantara/cve-2023-49973
Customer Support System 1.0 - Cross-Site Scripting (XSS) Vulnerability in "email" field/parameter on "customer_list" Page
 ahmedmansour93/event-id-263-rule-name-soc287---arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-
🔍 Just wrapped up an incident report on a Phishing Alert (Event ID 257, SOC282). Enhancing my expertise in email threat detection and response! 🚨…
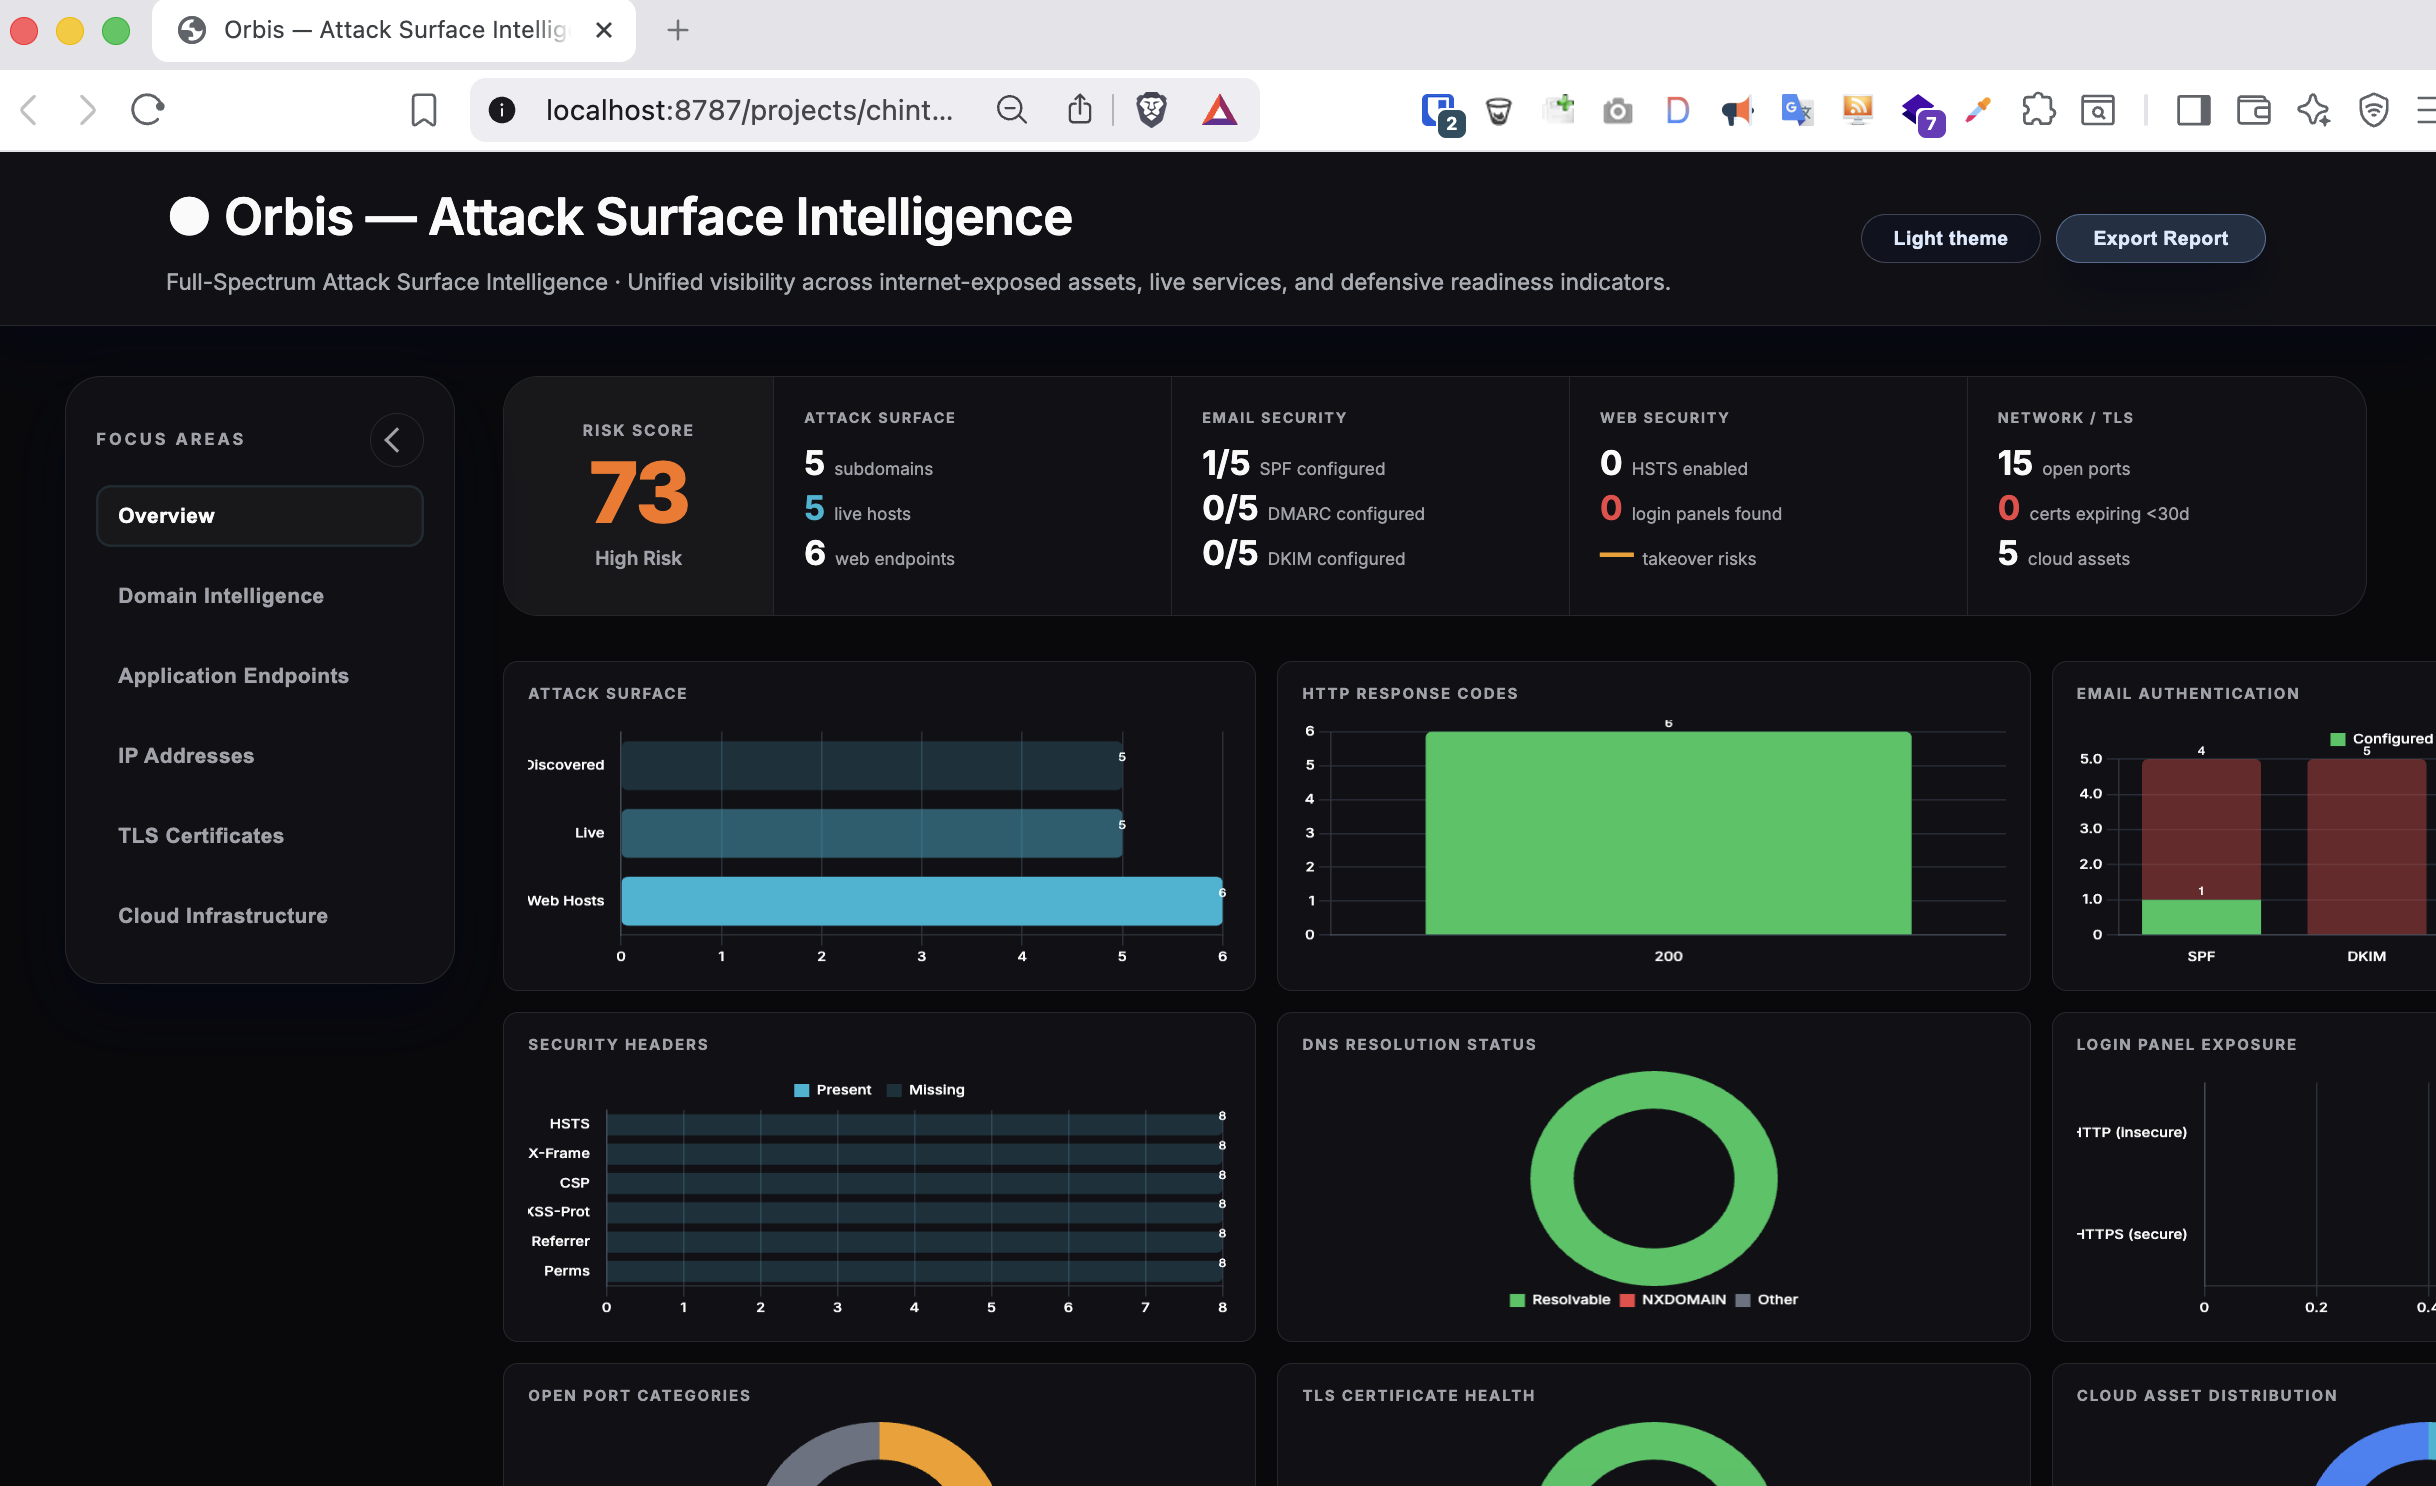 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 dgtlmoon/changedetection.io
Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…
 dariusztytko/token-reverser
Words list generator to crack security tokens
 elandio-com/sharemylogin
Zero-Knowledge Credential Sharing
 duy-31/cve-2023-51764
Postfix SMTP Smuggling - Expect Script POC
 ahrixia/cve-2023-30256
QloApp 1.5.2: Vulnerable to XSS on two Parameter (email_create and back)
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php
 sacx-7/cve-2025-50866
Cross Site Scripting (XSS)
 randomrobbiebf/cve-2023-41652
RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection
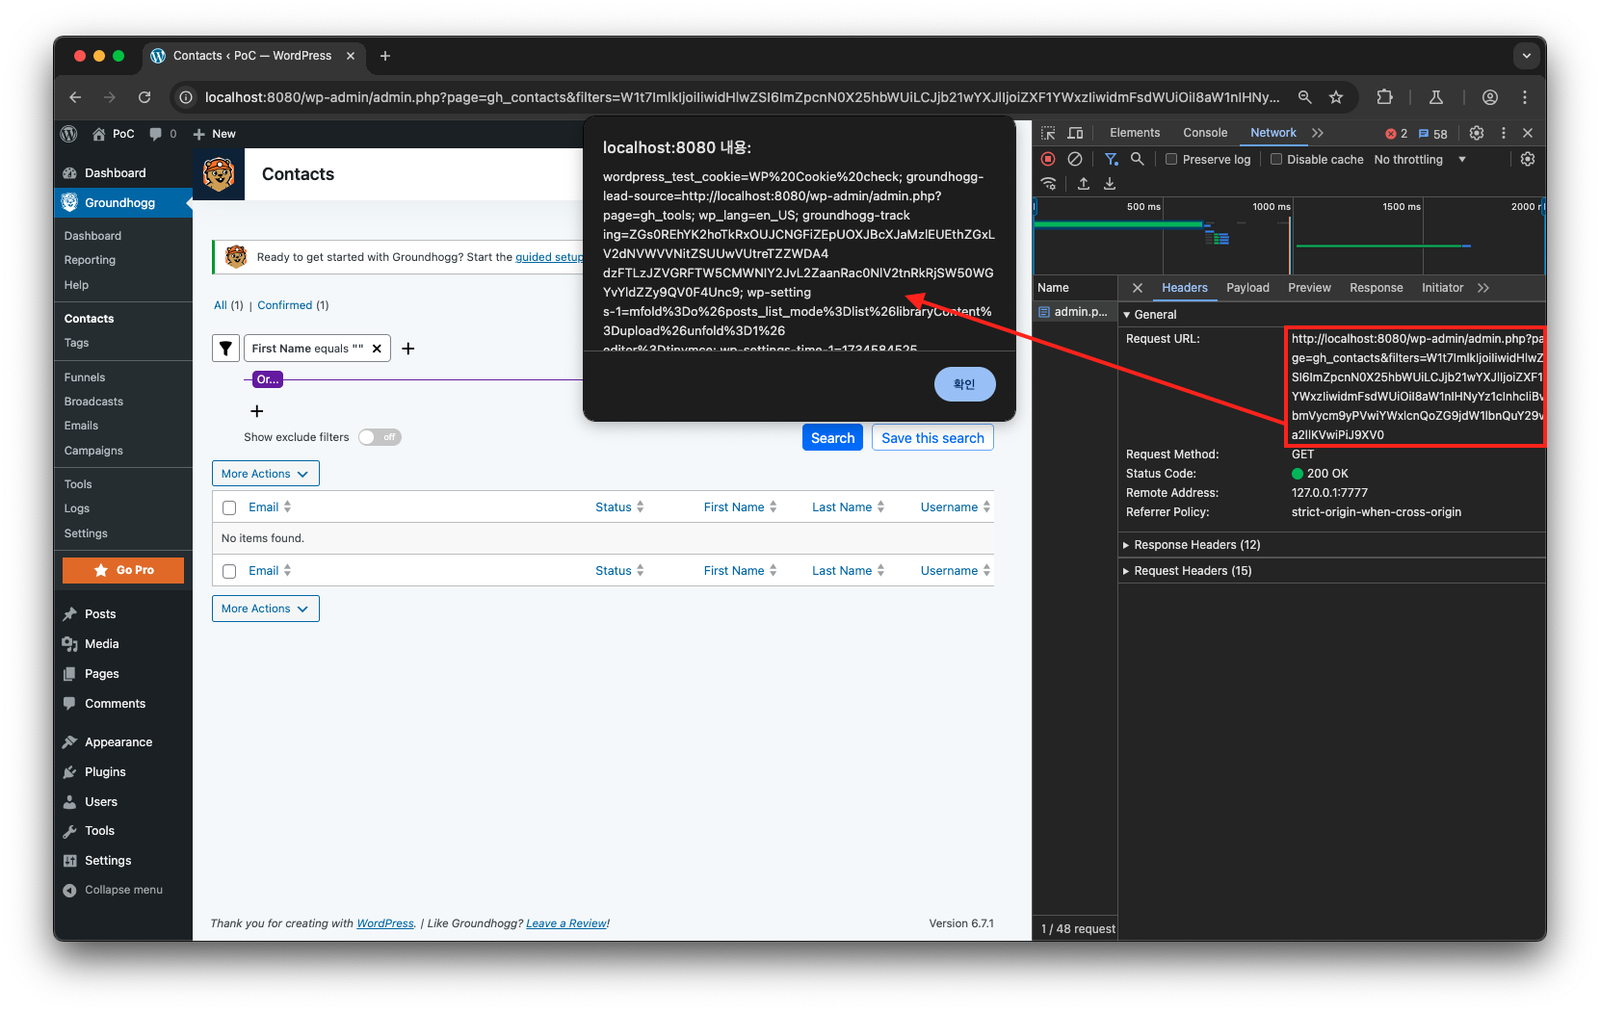 dottak/cve-2024-56289
Proof-of-concept exploit for a reflected XSS vulnerability in the Groundhogg WordPress plugin, demonstrating unauthenticated script injection via…
 bevennyamande/cve-2024-10557
A CSRF POC for Updating the Profile of a Hospital leading to Account Takeover
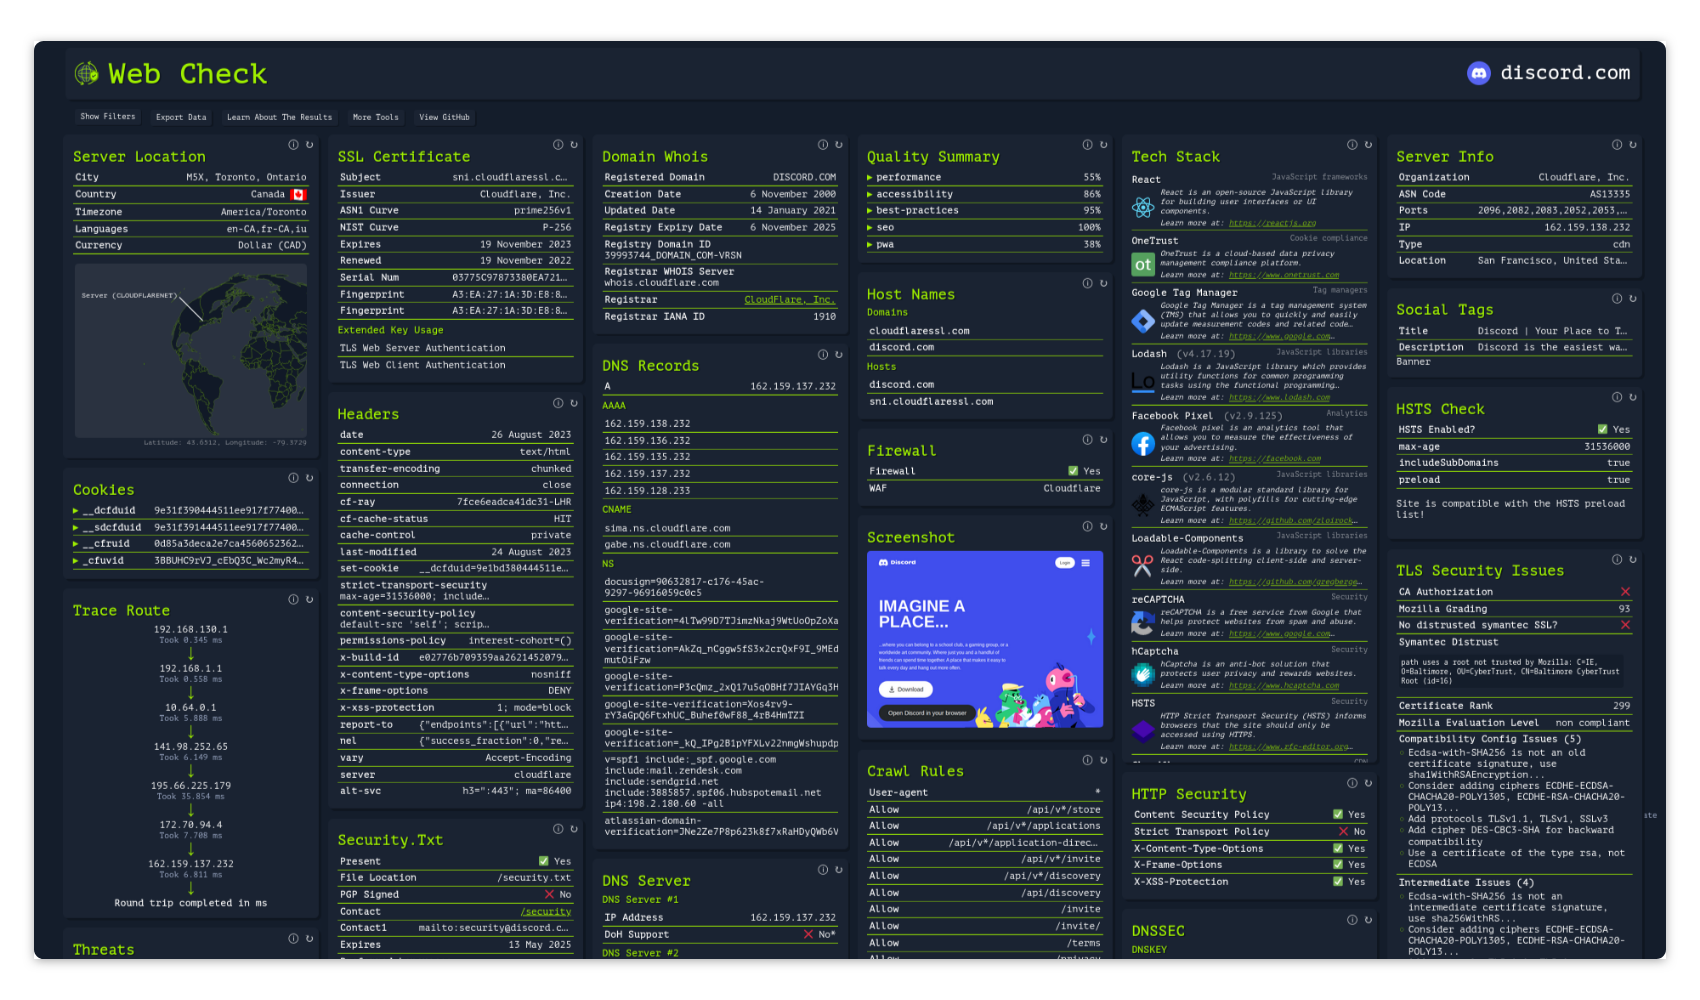 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website