
react
 janhalendk/react
A OSINT project that explores how to dump data from React
educationinformation-gatheringosint+2
janhalendk/reactA OSINT project that explores how to dump data from React
 ascr0b/pcwt
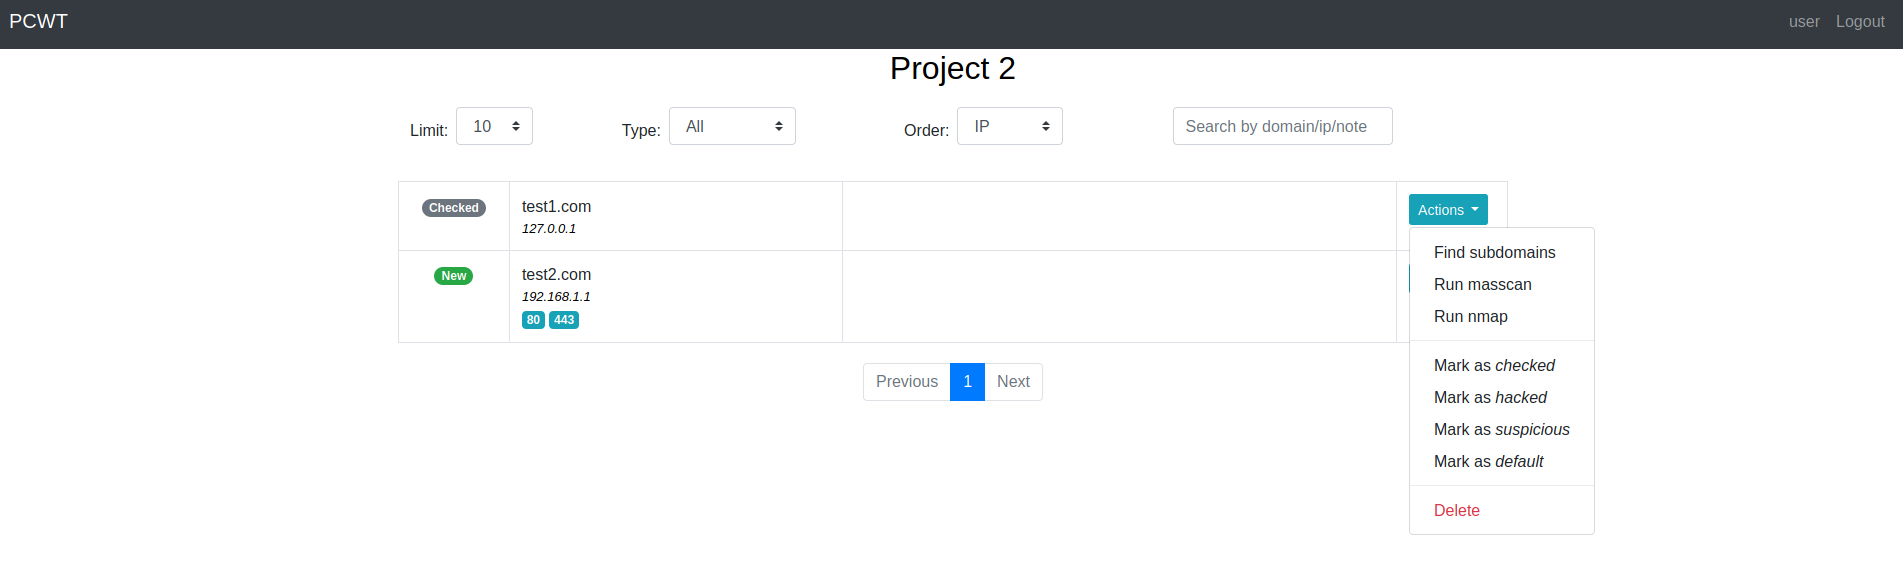
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 osmankandemir/static-code-analysis-helper
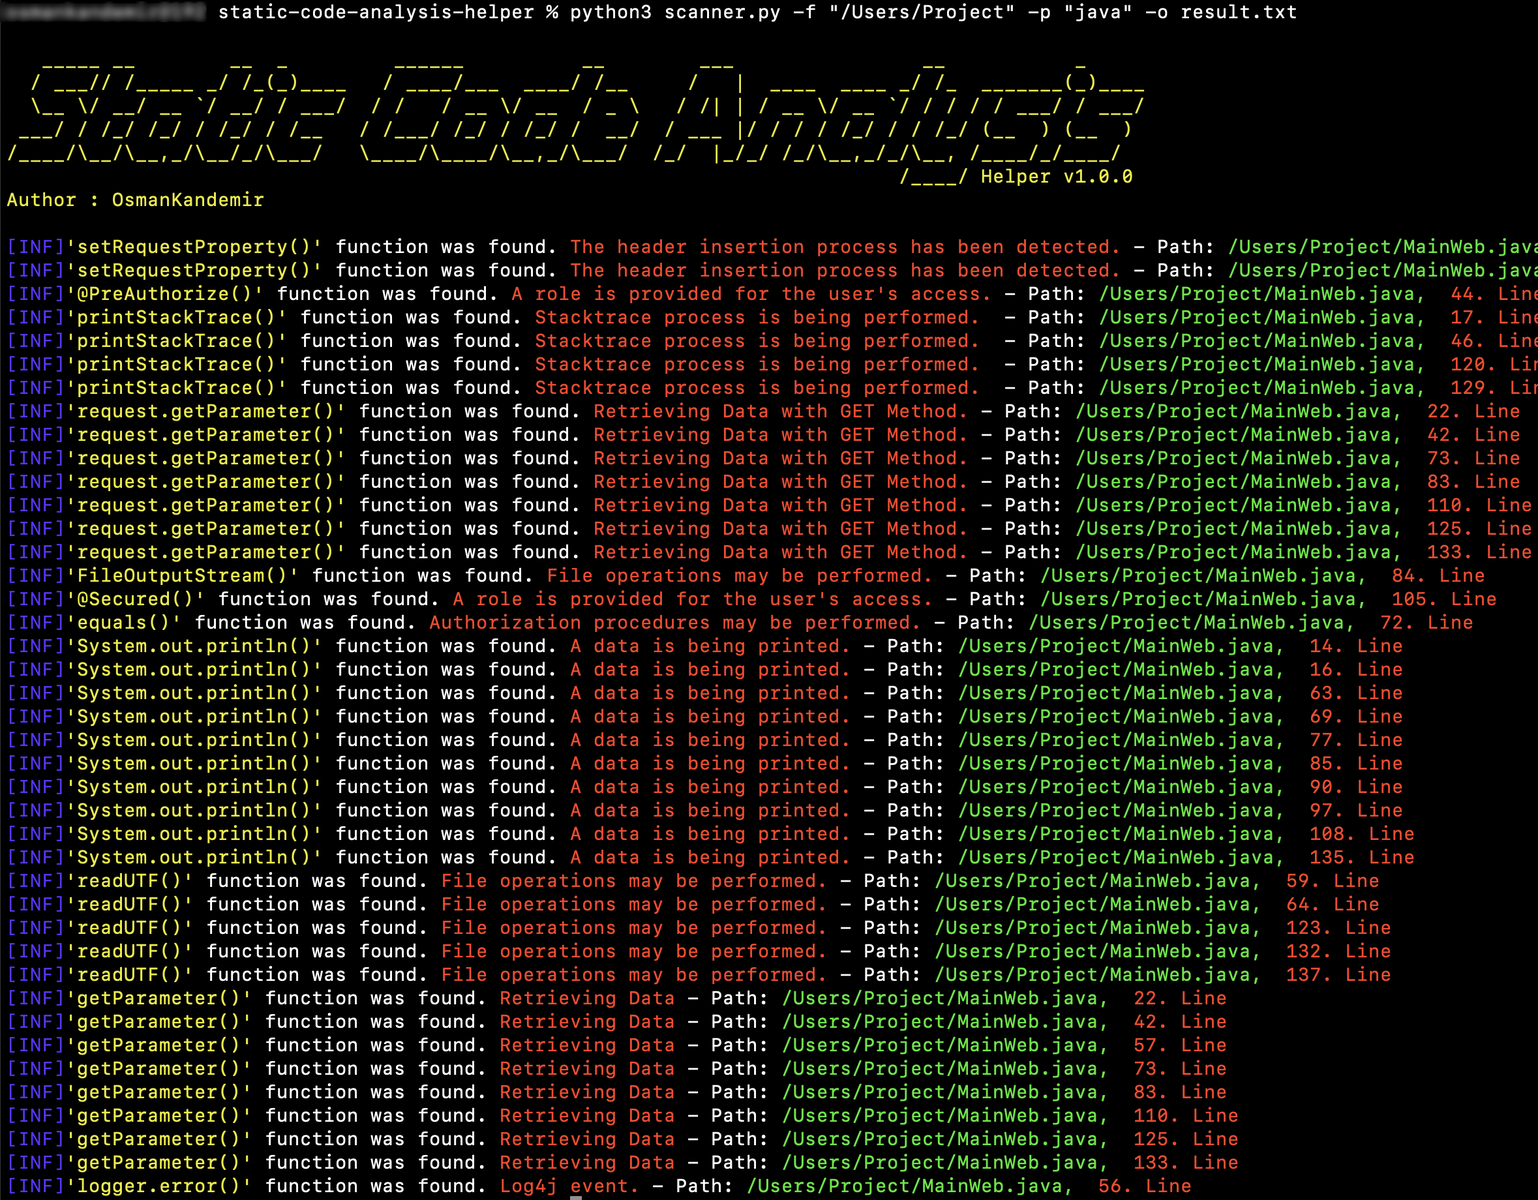
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 owasp/owasp-learning-gateway
OWASP Learning Gateway Project
 ynsmroztas/gitlabsniper
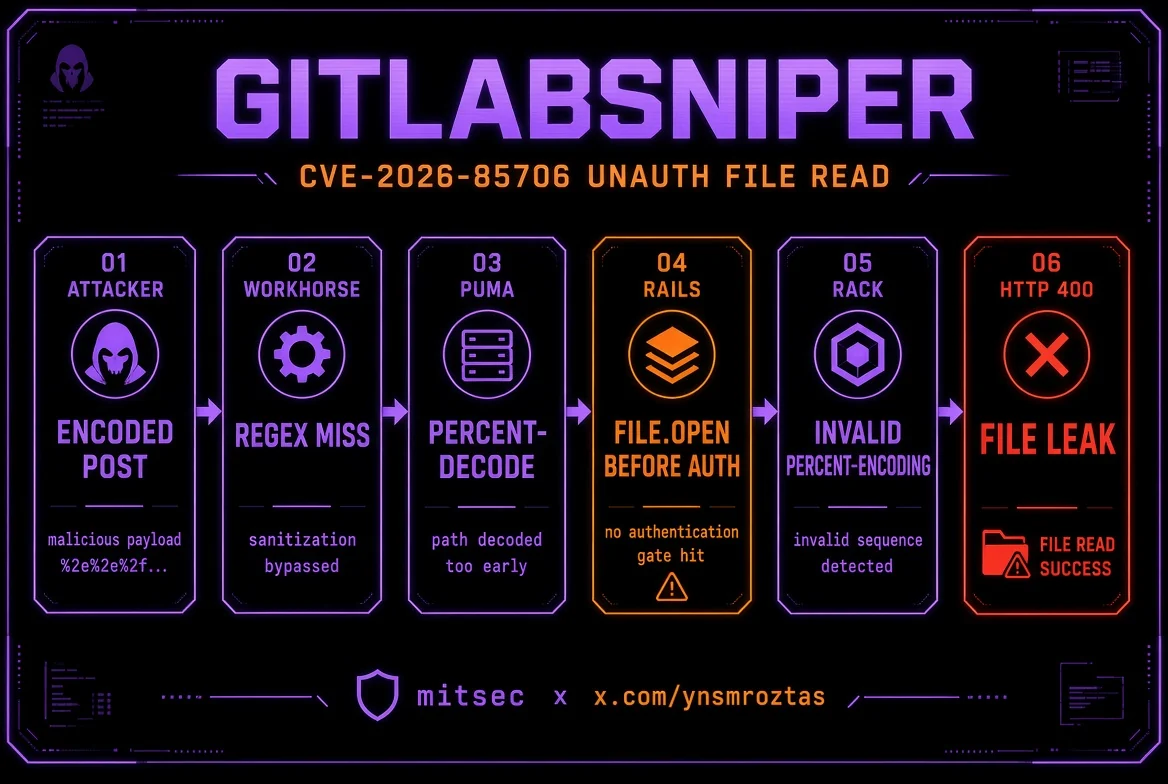
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 owasp/browser-security-project
Community-driven project providing guidance and resources to improve browser security, including best practices and educational materials for…
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 jpiechowka/at-doom-fortigate
Fortigate CVE-2018-13379 - Tool to search for vulnerable Fortigate hosts in Rapid7 Project Sonar data anonymously through The Tor network.
 clarkio/pdfjs-vuln-demo
This project is intended to serve as a proof of concept to demonstrate exploiting the vulnerability in the PDF.js (pdfjs-dist) library reported in…
 farinap5/a-xex
This project is part of a school work focusing on network security.
 lindhunt/cve-2026-26211
Public disclosure and proof-of-concept for CVE-2026-26211, a stored XSS vulnerability in Ekushey Project Manager CRM v5.0, including technical…
 imbas007/poc-cve-2026-58048
Security research project
 balochkainat160-cyber/cs50-cybersecurity
CS50's Introduction to Cybersecurity final project on React2Shell (CVE-2025-55182)
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 shahdawadfallah-sys/cybersecurity-capstone-project
Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…
 smarttfoxx/cve-2025-45778
A stored cross-site scripting (XSS) vulnerability in The Language Sloth Web Application v1.0 allows attackers to execute arbitrary javascript or HTML…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…