
CVE-2023-44487
 bcdannyboy/cve-2023-44487
Non-invasive HTTP/2 vulnerability scanner for CVE-2023-44487 that detects exploitable stream reset conditions by testing protocol downgrade and…
exploitationvulnerability-scannersweb-security
bcdannyboy/cve-2023-44487Non-invasive HTTP/2 vulnerability scanner for CVE-2023-44487 that detects exploitable stream reset conditions by testing protocol downgrade and…
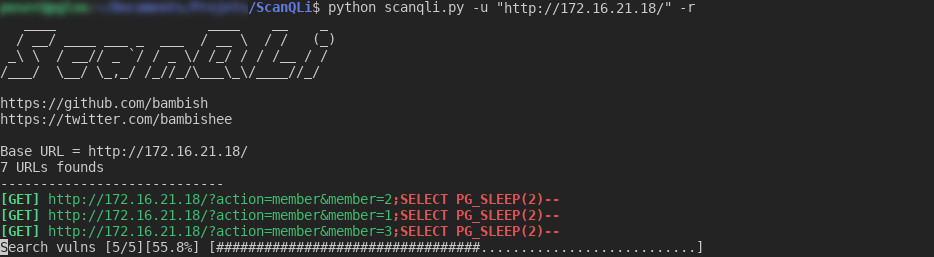 bambish/scanqli
SQLi scanner to detect SQL vulns
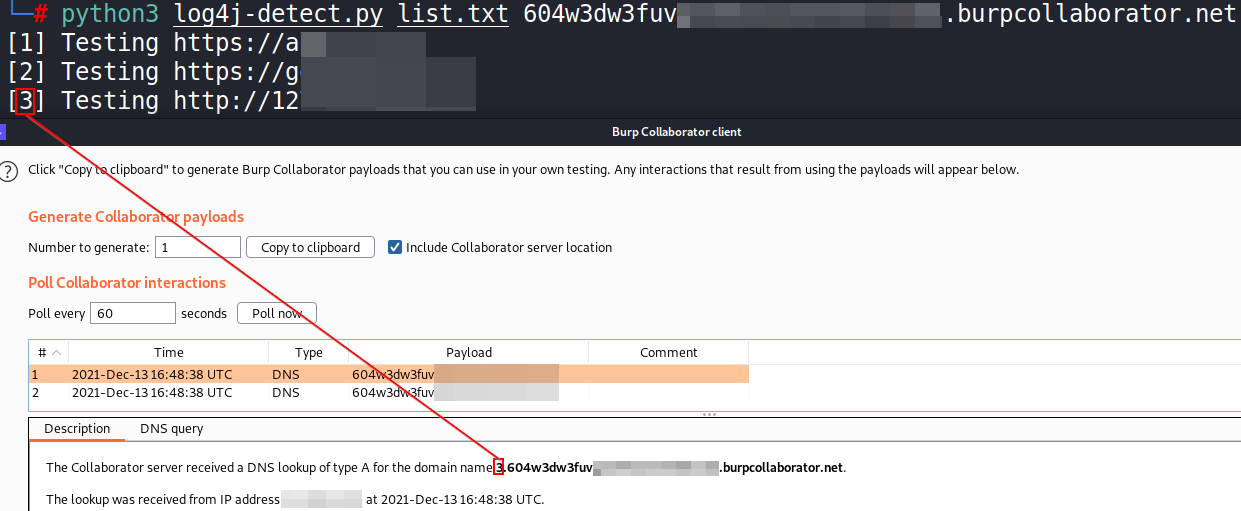 takito1812/log4j-detect
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
 1n3/httpoxyscan
HTTPoxy Exploit Scanner by 1N3 @CrowdShield
 gdssecurity/jetleak-testing-script
Script to test if a server is vulnerable to the JetLeak vulnerability
 hannob/optionsbleed
Proof-of-concept scanner for the Optionsbleed vulnerability (CVE-2017-9798) that tests Apache HTTP servers for memory leak via HTTP OPTIONS method.
 spiderlabs/airachnid-burp-extension
A Burp Extension to test applications for vulnerability to the Web Cache Deception attack
 ferreiraklet/jeeves
Time-based blind SQL injection detection tool for recon and bug bounty. Accepts single URLs or lists, supports custom headers, proxy, and POST data…
 silentsignal/burp-text4shell
Text4Shell scanner for Burp Suite
 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 samhaxr/xxrf-shots
XXRF Shots - Useful for testing SSRF vulnerability
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
 tismayil/laraveln00b
LaravelN00b .env Scanner
 souravbaghz/scanginx
Scanner For Nginx - Remote Integer Overflow Vulnerability
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
 fatal0/tomcat-cve-2020-1938-check
Go-based scanner for Apache Tomcat AJP file read/inclusion vulnerability (CVE-2020-1938). Detects and exploits Ghostcat to read arbitrary files or…
 iqzer0/vulnknox
A Go-based wrapper for the KNOXSS API to automate XSS vulnerability testing.
 fdjy1234/cve-2022-41404-dos-protection
Windows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection