
CVE-2025-70545
 jeyabalaji711/cve-2025-70545
Stored XSS proof-of-concept for PPC (Belden) ONT 2K05X router firmware v1.1.9_206L, with reproduction steps and mitigation guidance for the…
educationexploitationpenetration-testing+3
jeyabalaji711/cve-2025-70545Stored XSS proof-of-concept for PPC (Belden) ONT 2K05X router firmware v1.1.9_206L, with reproduction steps and mitigation guidance for the…
 nu11secur1ty/xssight
Educational resource on Cross-site Scripting (XSS) attack techniques, covering non-persistent, persistent, and DOM-based vectors with practical…
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
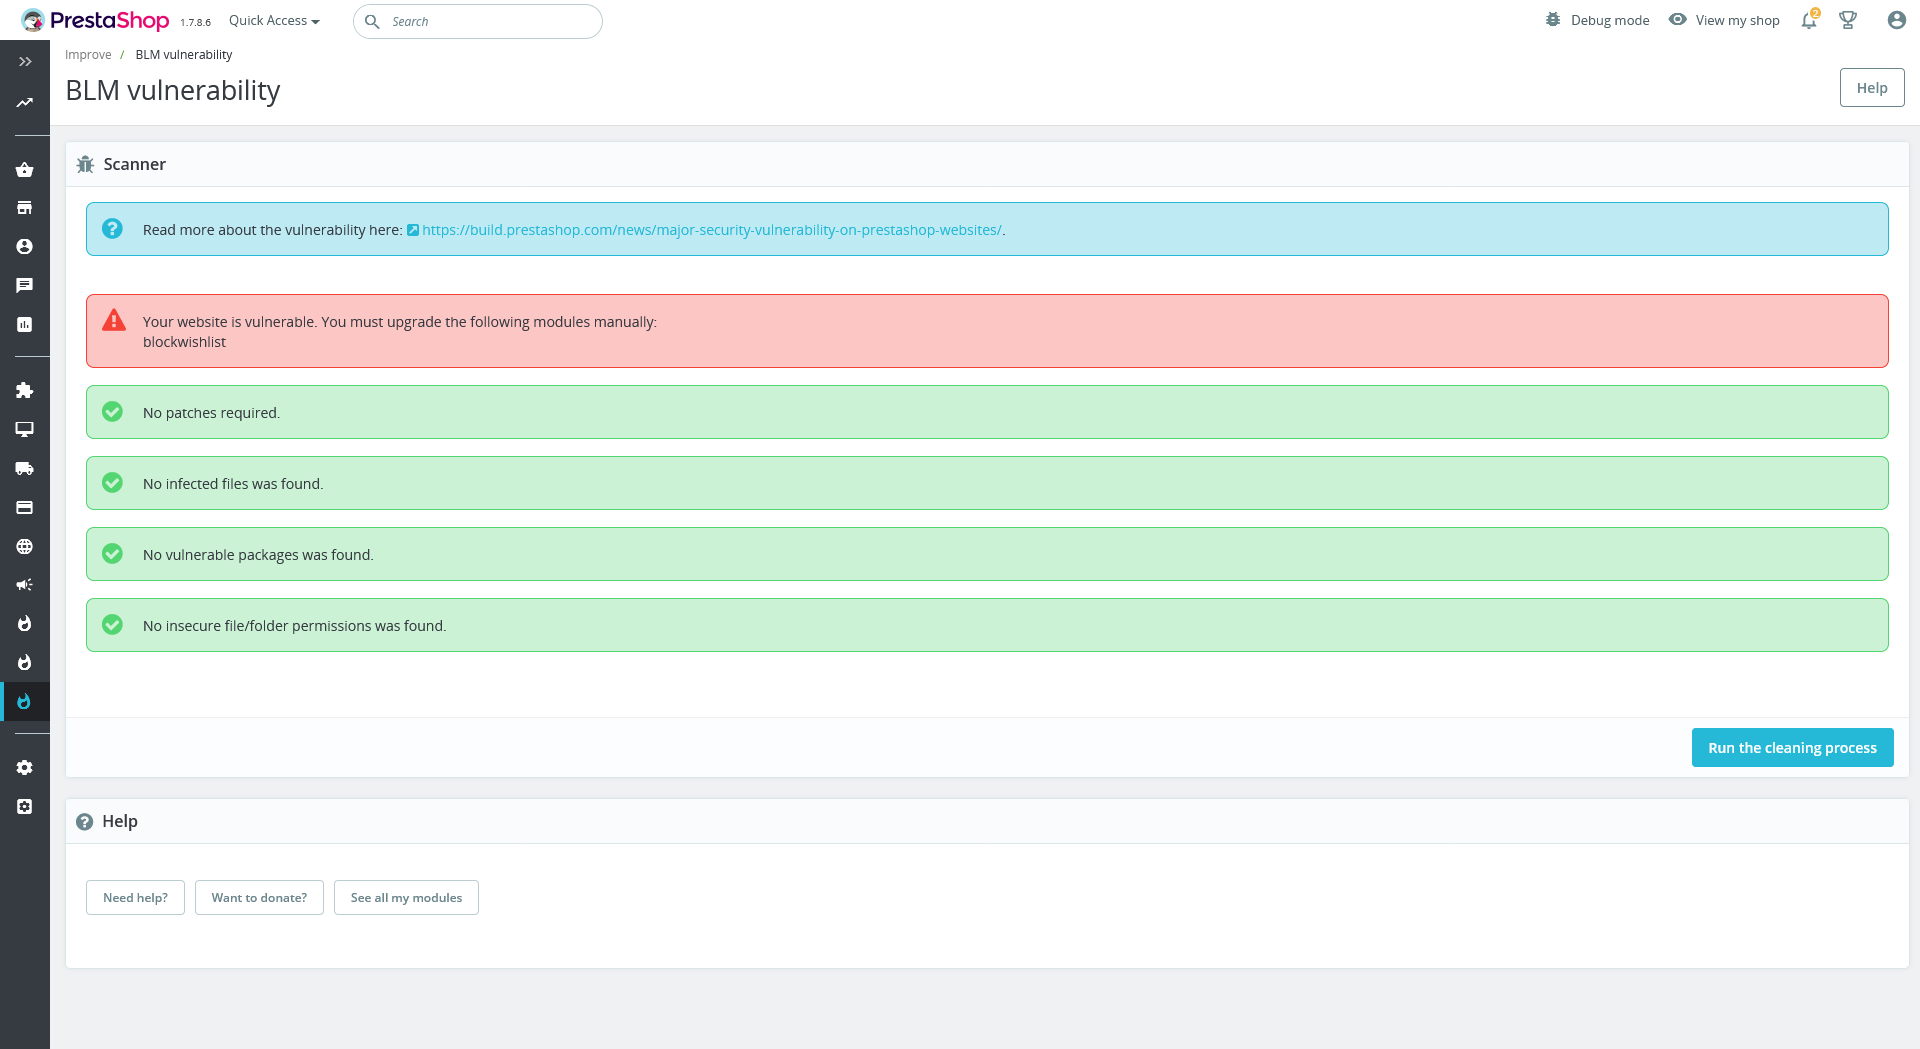 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
 kailing0220/cve-2019-5418
Ruby on Rails是一个 Web 应用程序框架,是一个相对较新的 Web 应用程序框架,构建在 Ruby 语言之上。这个漏洞主要是由于Ruby on Rails使用了指定参数的render…
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
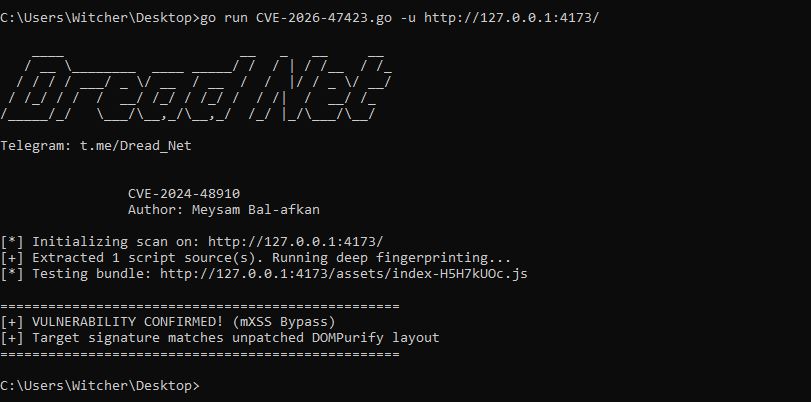 galaxy-sc/cve-2026-47423-dompurify-xss-detector
Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles,…
 cucumberanorsncompany/sealsecurityassignment
Researching on the vulnrability CVE-2023-26136
 bilalclicksafe/cve-2025-60595
SPH Engineering UgCS 5.13.0 is vulnerable to Arbitary code execution. This is the public refrence to be used on CVE site
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 shoucheng3/x-stream__xstream_cve-2020-26217_1-4-14-java77
Java library for XML serialization and deserialization, with a focus on the CVE-2020-26217 deserialization vulnerability exploit.

 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.