CVE-2024-50379-PoC
Batch detection script for Apache Tomcat CVE-2024-50379 race condition remote code execution vulnerability. Supports single and mass scanning via…

Batch detection script for Apache Tomcat CVE-2024-50379 race condition remote code execution vulnerability. Supports single and mass scanning via…

cisco-CVE-2023-20198-tester

Scripts to clone CA certificates for use in HTTPS client attacks.

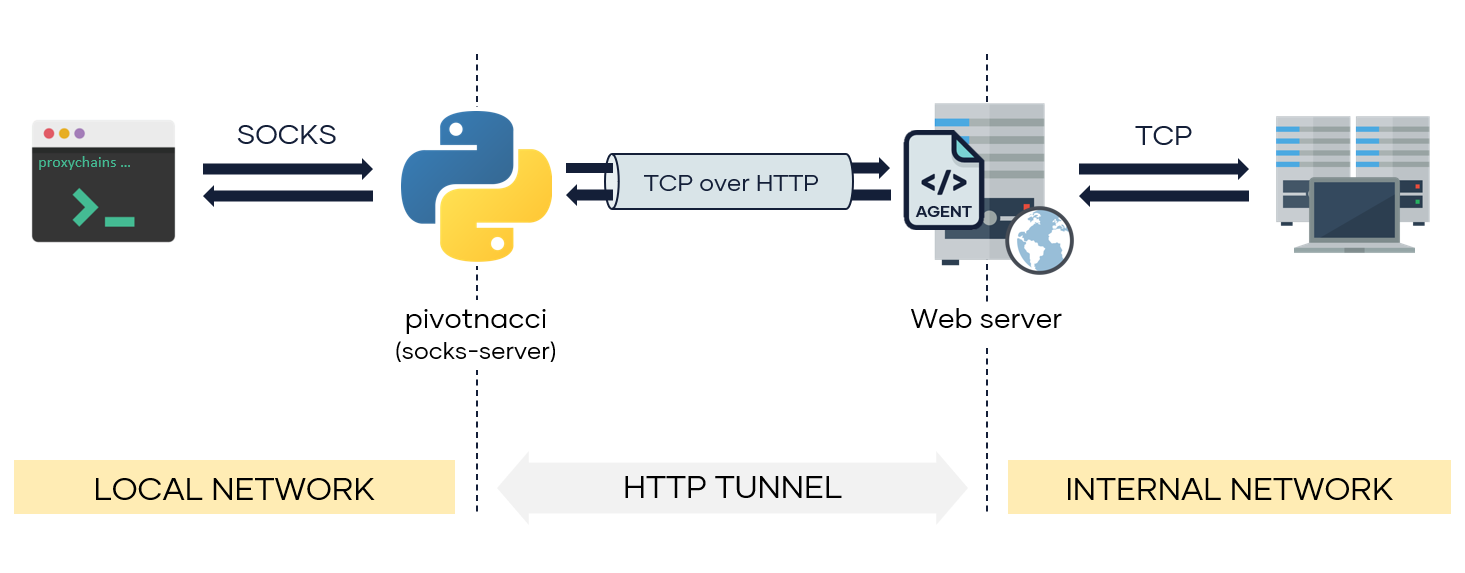
A tool to make socks connections through HTTP agents

A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.

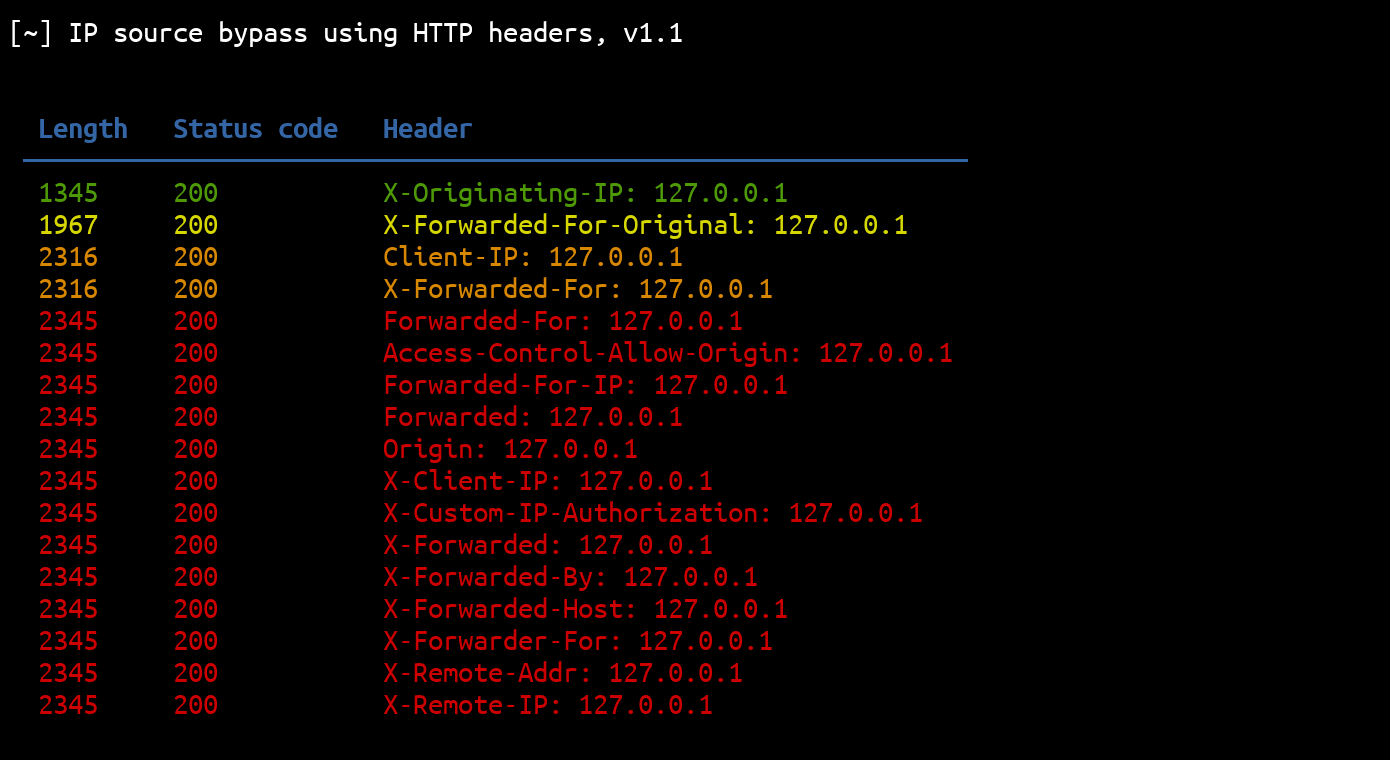
This Python script can be used to bypass IP source restrictions using HTTP headers.

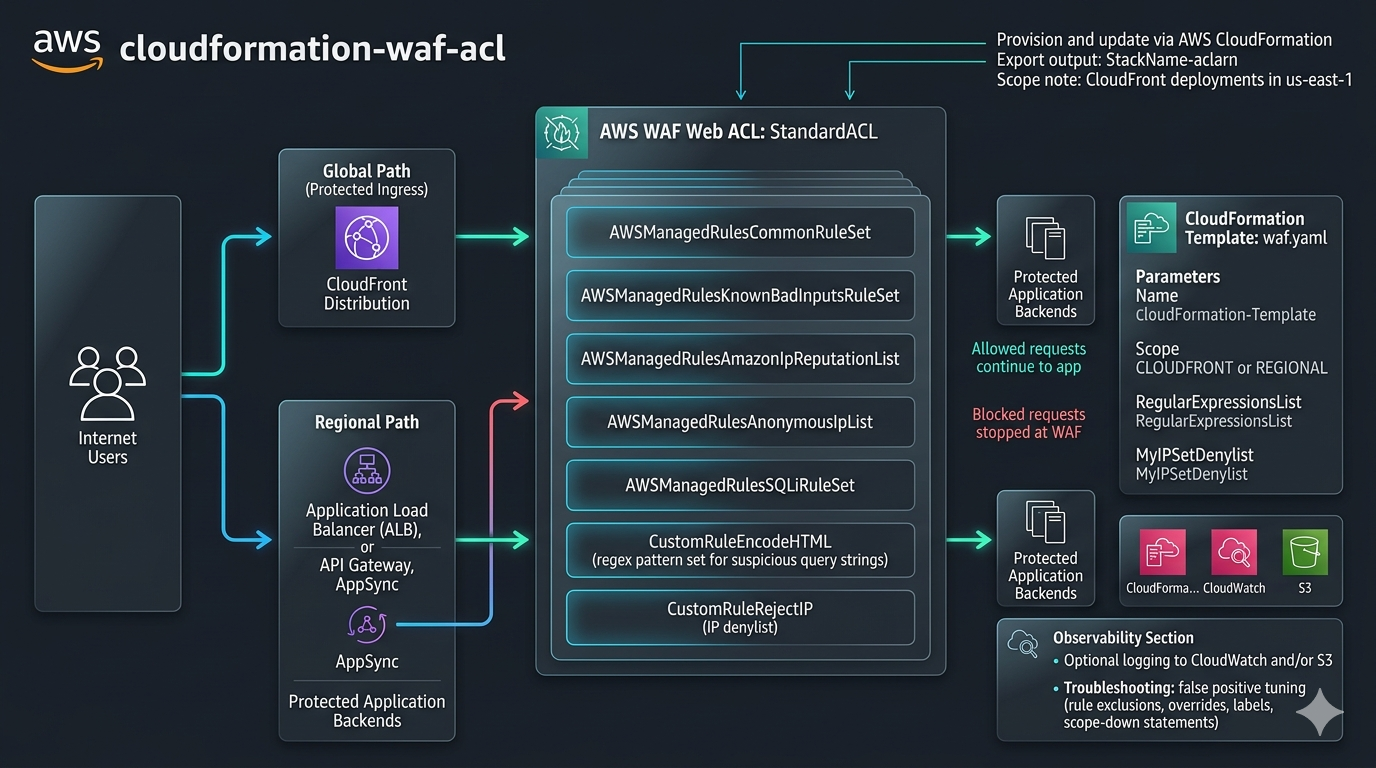
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…

AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation

Open-source security research tool for identifying origin IP exposure of websites protected by Cloudflare and similar reverse proxy services.

Shodanwave is a tool for exploring and obtaining information from Netwave IP Camera.

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

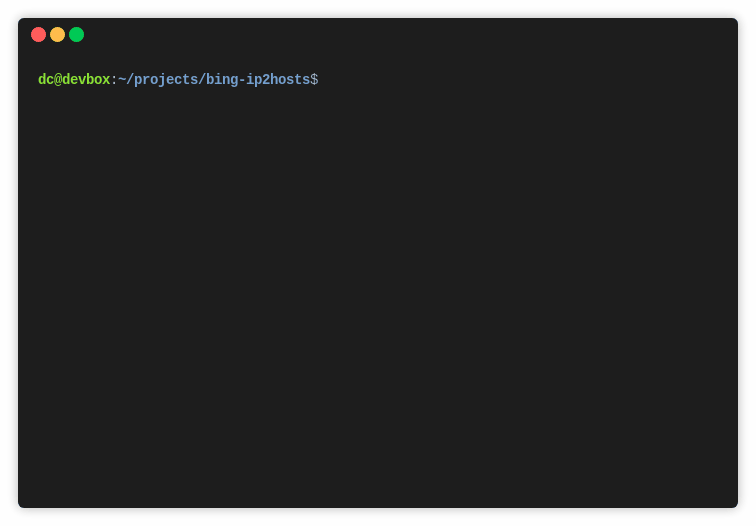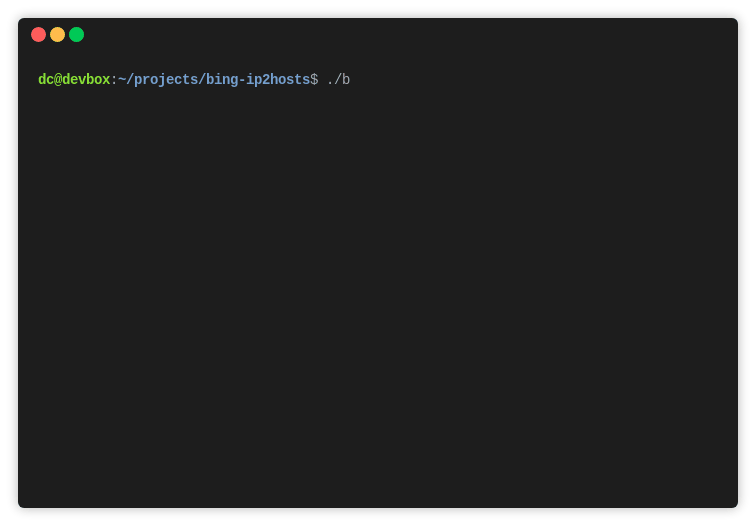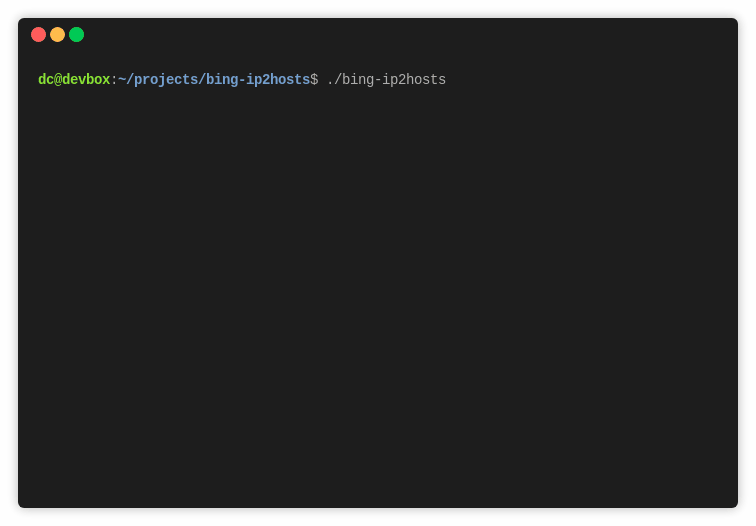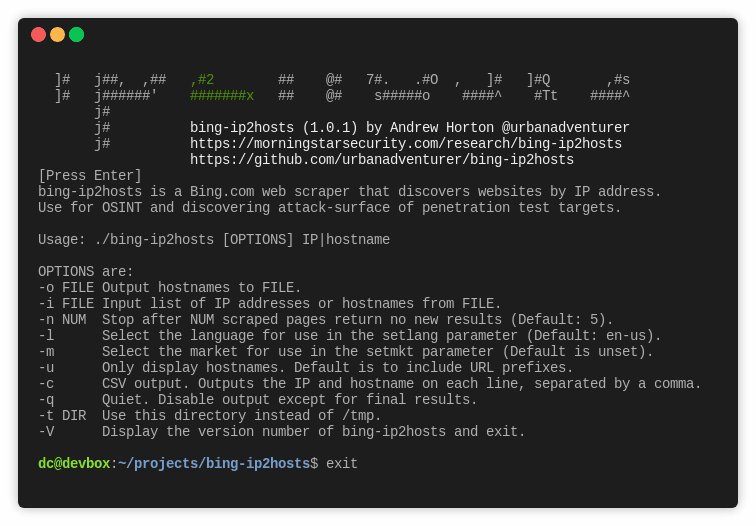
bingip2hosts is a Bing.com web scraper that discovers websites by IP address

Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…

XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.

Async Python CLI tool for bulk URL status checking with color-coded HTTP response categorization, IP tracking, and redirect following for web service…

Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…

This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…

Test for CVE-2000-0649, and return an IP address if vulnerable