vulnerability-in-Remix-React-Router-CVE-2025-31137-

CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.

CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.

Tests your WAF with +160 payloads

A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…

Quick WAF "paranoid" Doctor Evaluation | WAFPARAN01D3 Tool

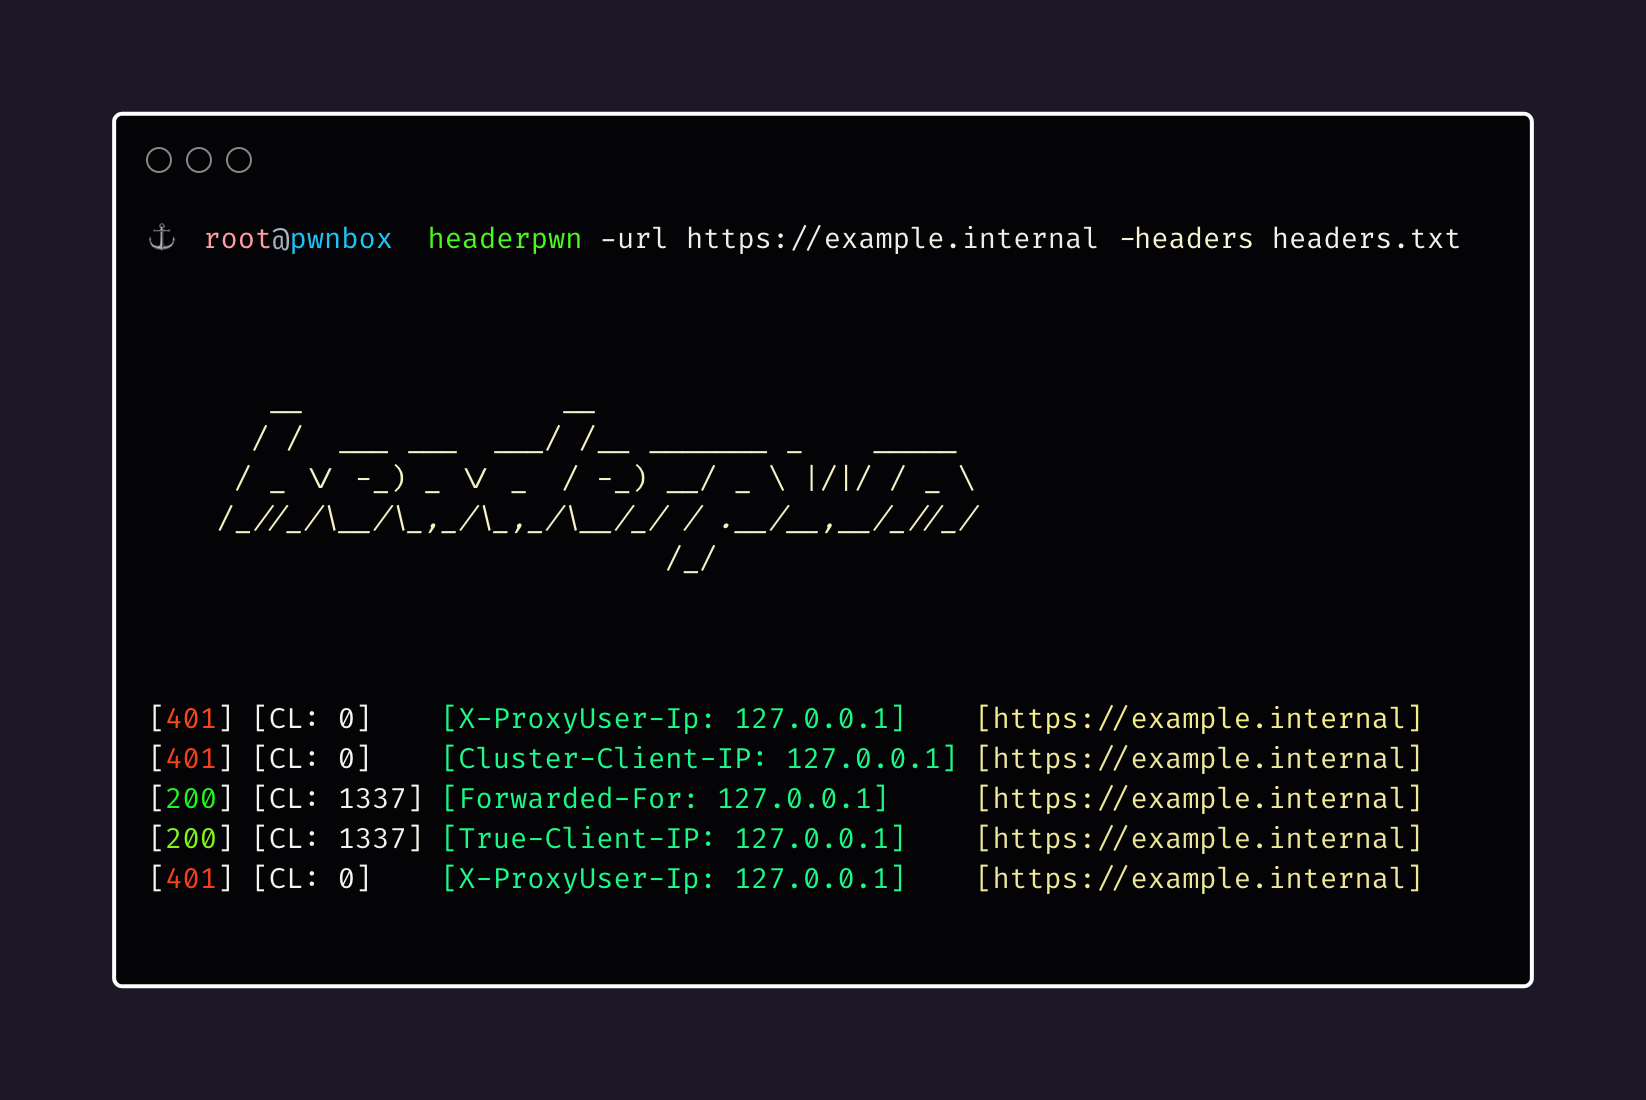
A fuzzer for finding anomalies and analyzing how servers respond to different HTTP headers

Summary of Cyber Security interview questions I have been through, hope this helps

Analyzes CVE-2024-38998, a prototype pollution vulnerability in requirejs 2.3.6, demonstrating how malicious config inputs can lead to DoS, RCE, or…

This is a showcase how the Log4J vulnerability (CVE-2021-44228) could be explored. This code is safe to run, but understand what it does and how it…

[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS

PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.

A2SV = Auto Scanning to SSL Vulnerability HeartBleed, CCS Injection, SSLv3 POODLE, FREAK... etc Support Vulnerability [CVE-2007-1858] Anonymous…

Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…

Analyzes CVE-2021-42948, a session token exposure vulnerability in HotelDruid, demonstrating how GET parameters leak session IDs and enable session…

Burp Plugin to Bypass WAFs through the insertion of Junk Data

PoC for CVE-2025-29927: Next.js Middleware Bypass Vulnerability. Demonstrates how x-middleware-subrequest can bypass authentication checks. Includes…

CVE‑2025‑55182 Detection

I Found a Zero-Day Vulnerability in langchain — Here’s How It Went

Security advisory detailing a critical CVE in Copilot AI where RAG-based citation links are forged to a third-party domain, enabling source…