
ChangeTower
 dc4ts/changetower
Lightweight web page change monitor written in Go. Detects updates on target URLs and sends notifications via Telegram or other services, ideal for…
crawlerinformation-gatheringweb-security
dc4ts/changetowerLightweight web page change monitor written in Go. Detects updates on target URLs and sends notifications via Telegram or other services, ideal for…
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
 manjen1218/cve-2022-0739-exploitation
Exploit for CVE-2022-0739 targeting unauthenticated SQL injection in BookingPress WordPress plugin versions before 1.0.11 via the…
 352926/shellshock_crawler
Using google to scan sites for "ShellShock" (CVE-2014-6271)
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
 sujaygr8/cve-2020-3187
Proof-of-concept exploit for CVE-2020-3187 targeting Cisco ASA/FTD session password disclosure via crafted HTTP cookie header.
 tamaloa/avo-cve-2024-22411
Proof-of-concept exploit for CVE-2024-22411 targeting the Avo admin panel. Demonstrates vulnerability exploitation in Ruby-based web applications.
 mak-/parameth
This tool can be used to brute discover GET and POST parameters
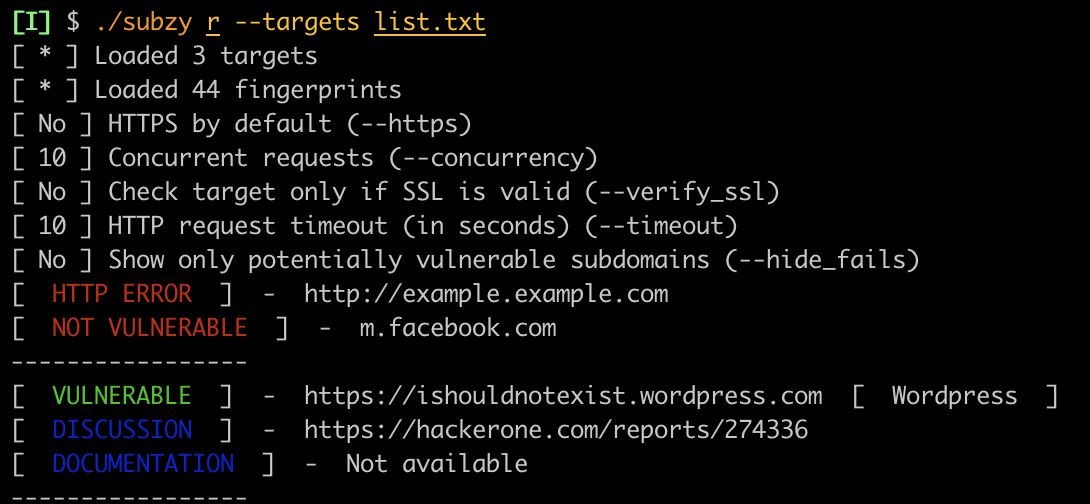 pentestpad/subzy
Subdomain takeover vulnerability checker
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
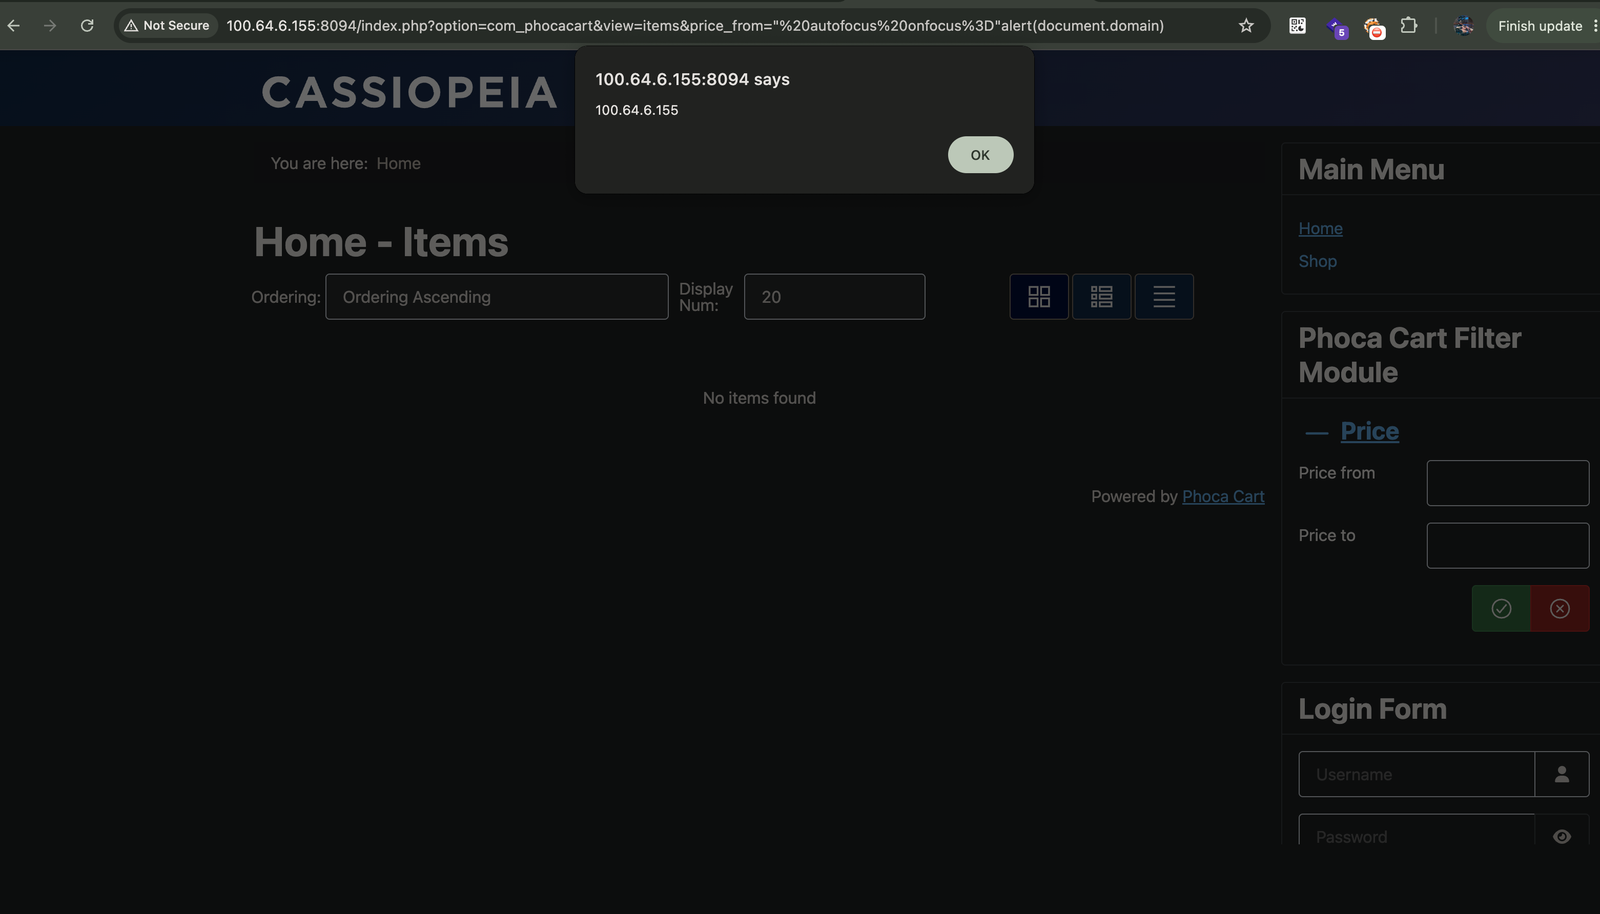 toanln-cov/cve-2026-76565
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 jul10l1r4/getrails
Get trails lib: Get all urls indexed of target
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 orange0mint/cve-2025-10035_goanywhere
CVE-2025-10035_GoAnywhere Get RCE
 dhammon/hoteldruid-cve-2021-42948
Analyzes CVE-2021-42948, a session token exposure vulnerability in HotelDruid, demonstrating how GET parameters leak session IDs and enable session…
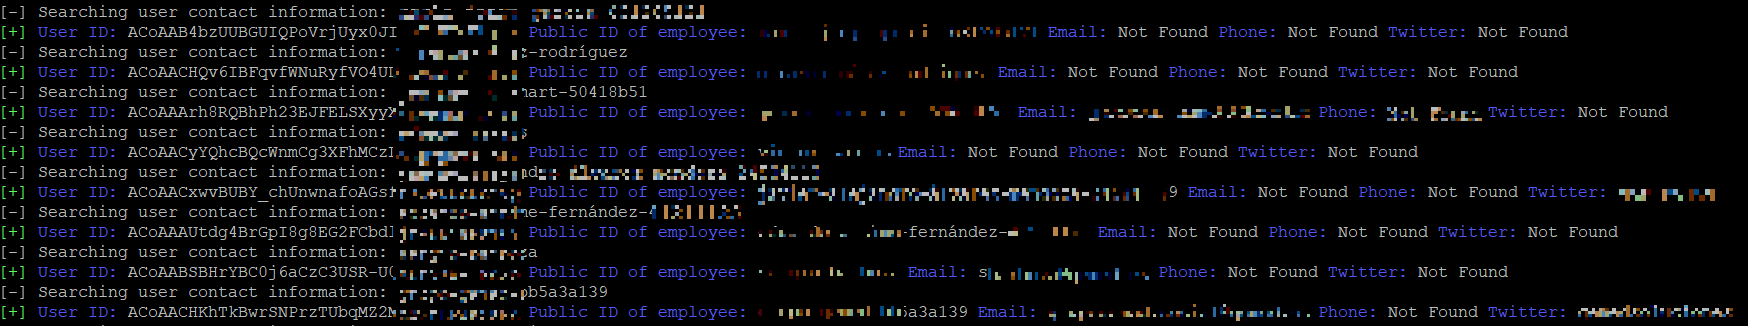 mrtuxx/socialpwned
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to…
 stamparm/dsss
Damn Small SQLi Scanner