apache__jspwiki_CVE-2022-46907_2-11-3

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…

Curated collection of XSS payload vectors for web application security testing, covering various contexts and bypass techniques.

Web Application Security Scanner Framework

Vulnerable Python Application To Learn Secure Development

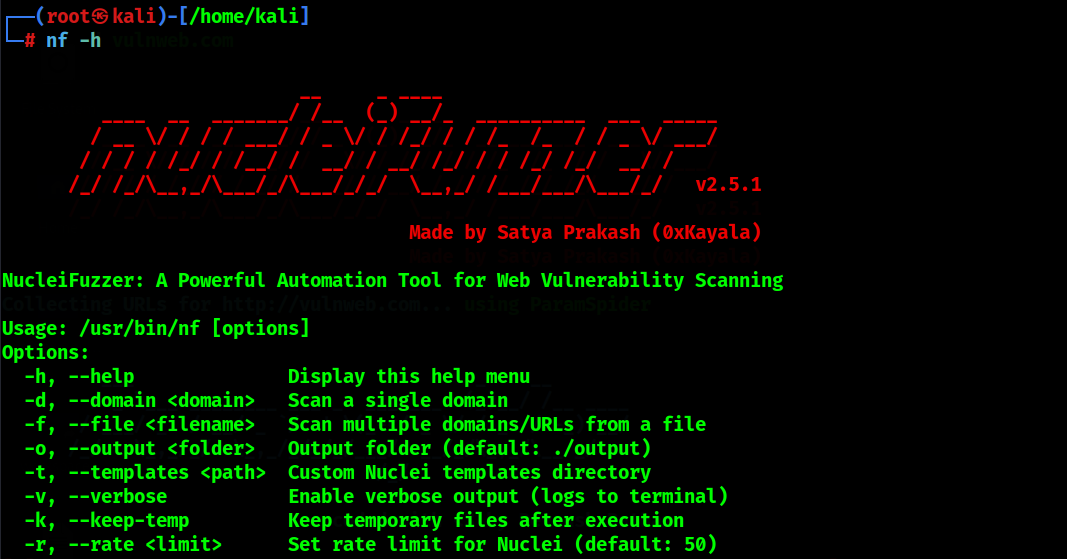
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…


Fast http dead file finder.

WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…

Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…

Capture-the-flag challenge for Ekoparty 2020 featuring a Flask web application with security vulnerabilities to exploit. Designed for hands-on…

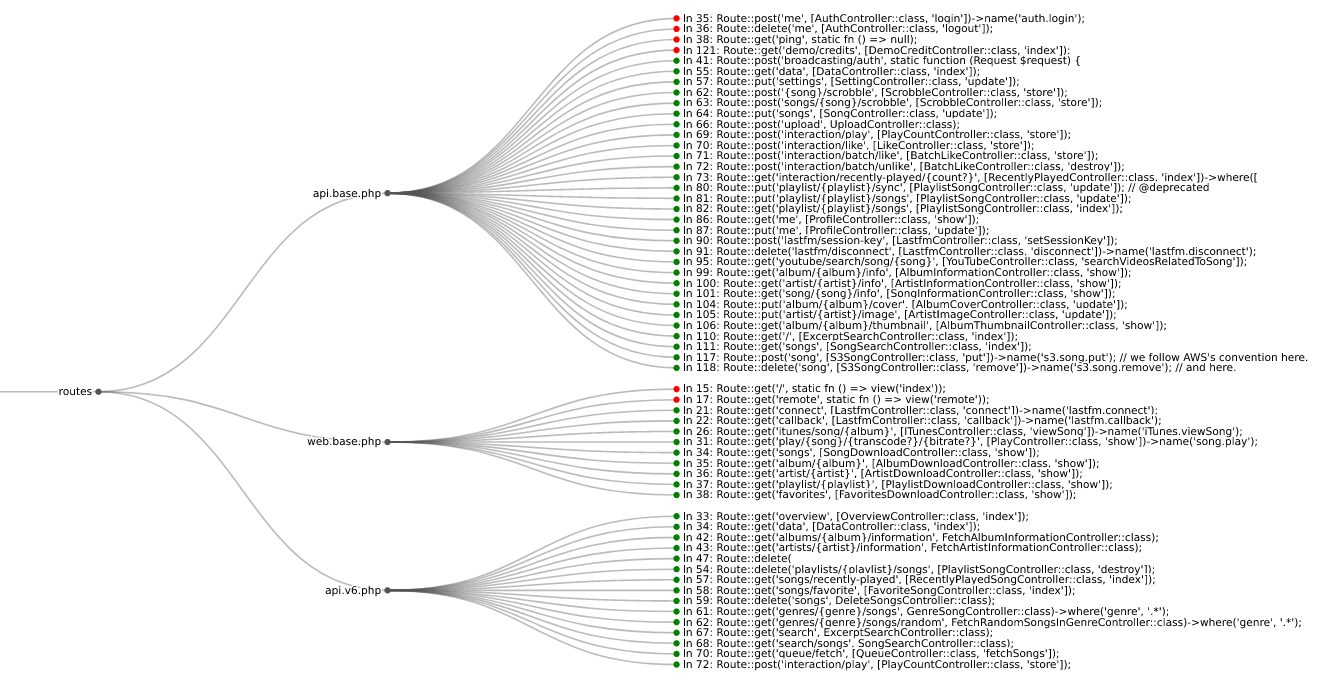
Find authentication (authn) and authorization (authz) security bugs in web application routes.

Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…

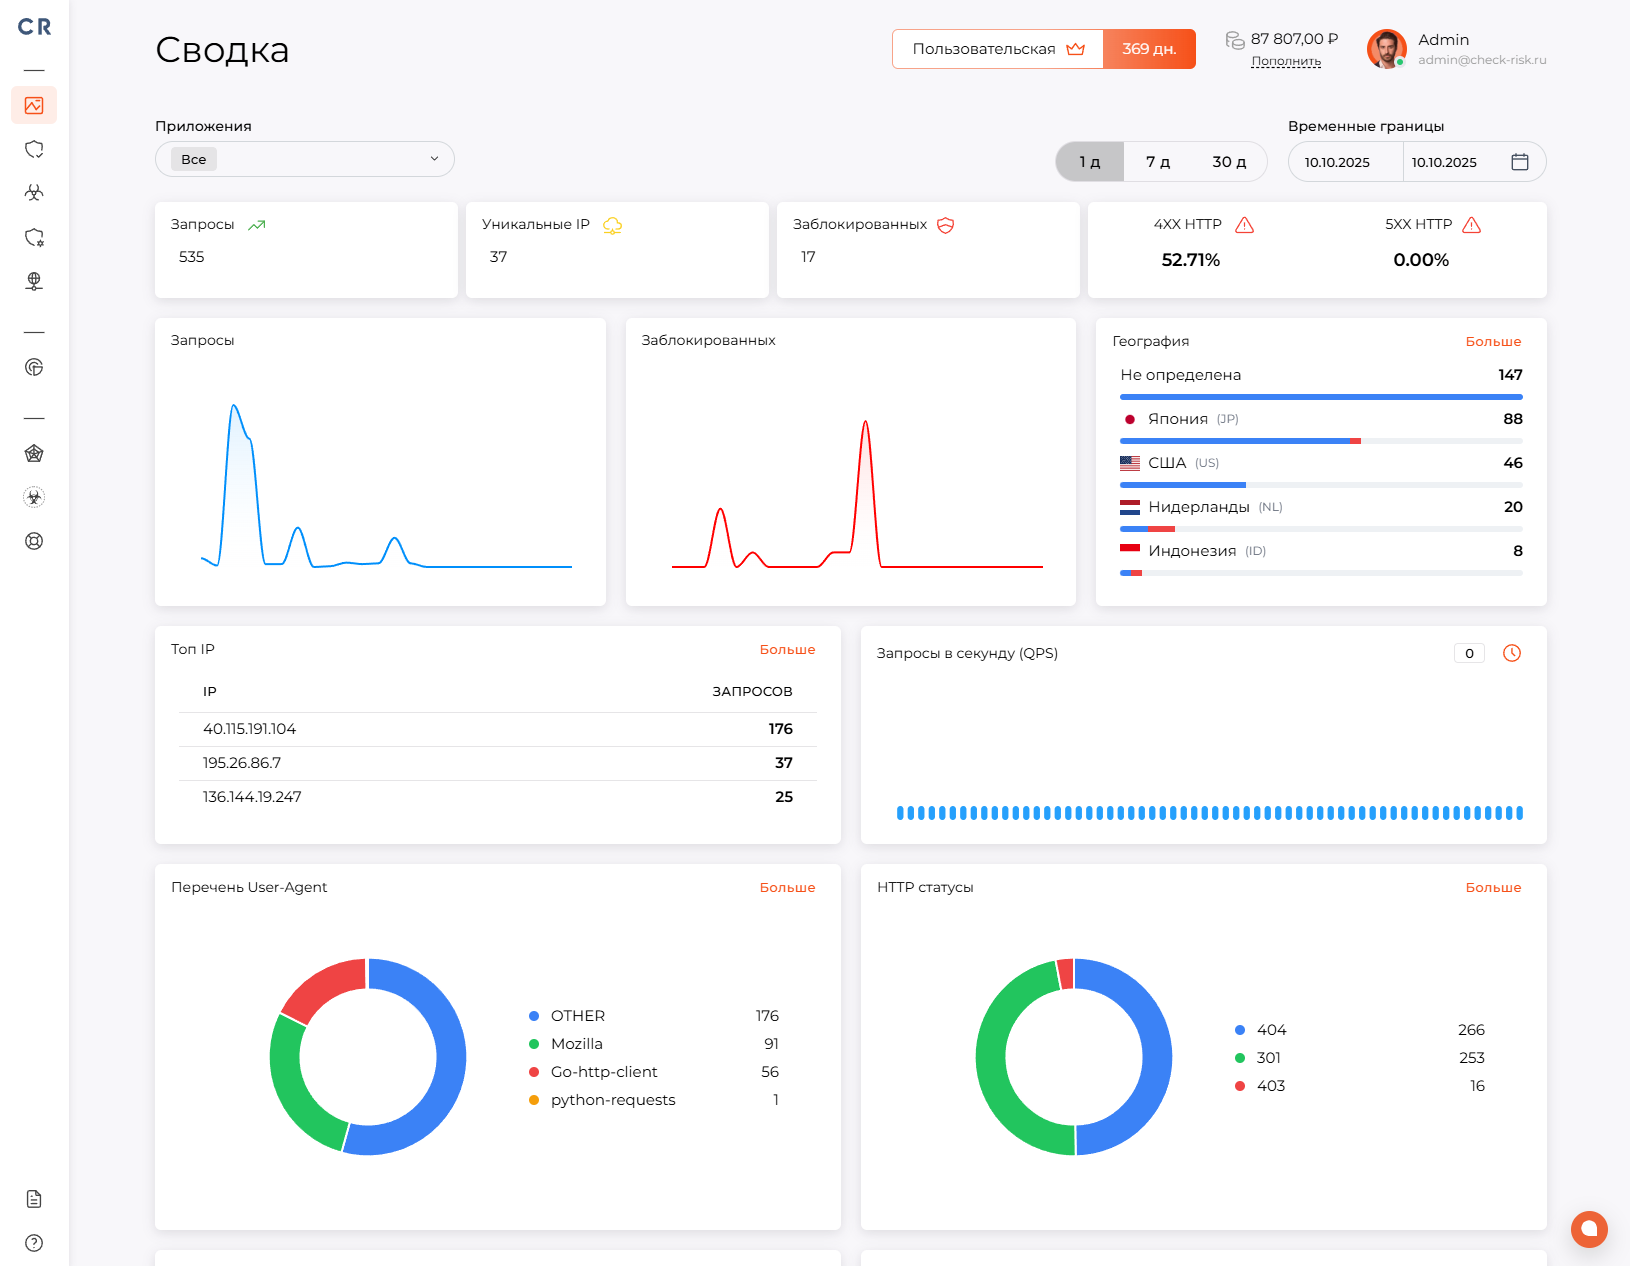
Cloud-based Web Application Firewall (WAF) providing L3/L7 protection against SQLi, XSS, DDoS, and bot attacks. Features AI assistant, anti-bot…

Web and mobile application security training platform

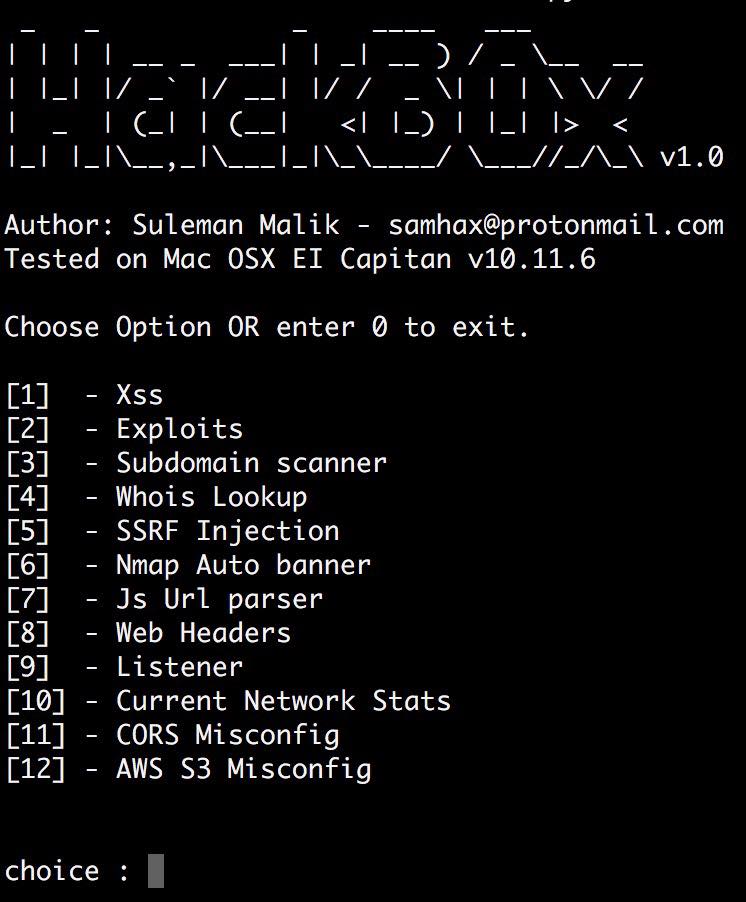
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…

Deliberately vulnerable Node.js web application containing 19+ security bugs (XSS, SSRF, Prototype Pollution, RCE) for hands-on penetration testing…