
CVE-2026-30081
 rakeshelamaran98/cve-2026-30081
Documentation of CVE-2026-30081, a high-severity cleartext transmission vulnerability in Quantum Networks QN-I-470 router firmware 6.1.1.B1, allowing…
exploitationinformation-gatheringnetwork-security+2
rakeshelamaran98/cve-2026-30081Documentation of CVE-2026-30081, a high-severity cleartext transmission vulnerability in Quantum Networks QN-I-470 router firmware 6.1.1.B1, allowing…
 vyvivekyadav04/rsc-infra-scanner
This is a fast, asynchronous Python tool that fingerprints domains for likely Next.js App Router / React Server Components (RSC) infrastructure. (I…
 wrathfuldiety/cve-2025-56311
CSRF vulnerability in FD602GW-DX-R410 router allows remote attackers to reboot the device via a crafted POST request to /boaform/admin/formReboot…
 leonardobg/cve-2023-36146
Proof-of-concept for authenticated stored cross-site scripting (XSS) vulnerability in Multilaser RE 170 router firmware 2.2.6733, with reproduction…
 fallenskill1/cve-2024-33111
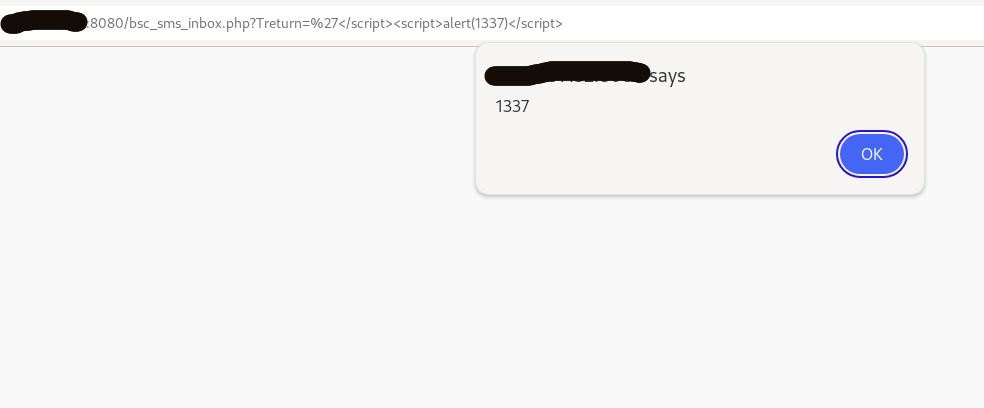
D-Link DIR-845L router is vulnerable to Cross Site Scripting (XSS) via /htdocs/webinc/js/bsc_sms_inbox.php.
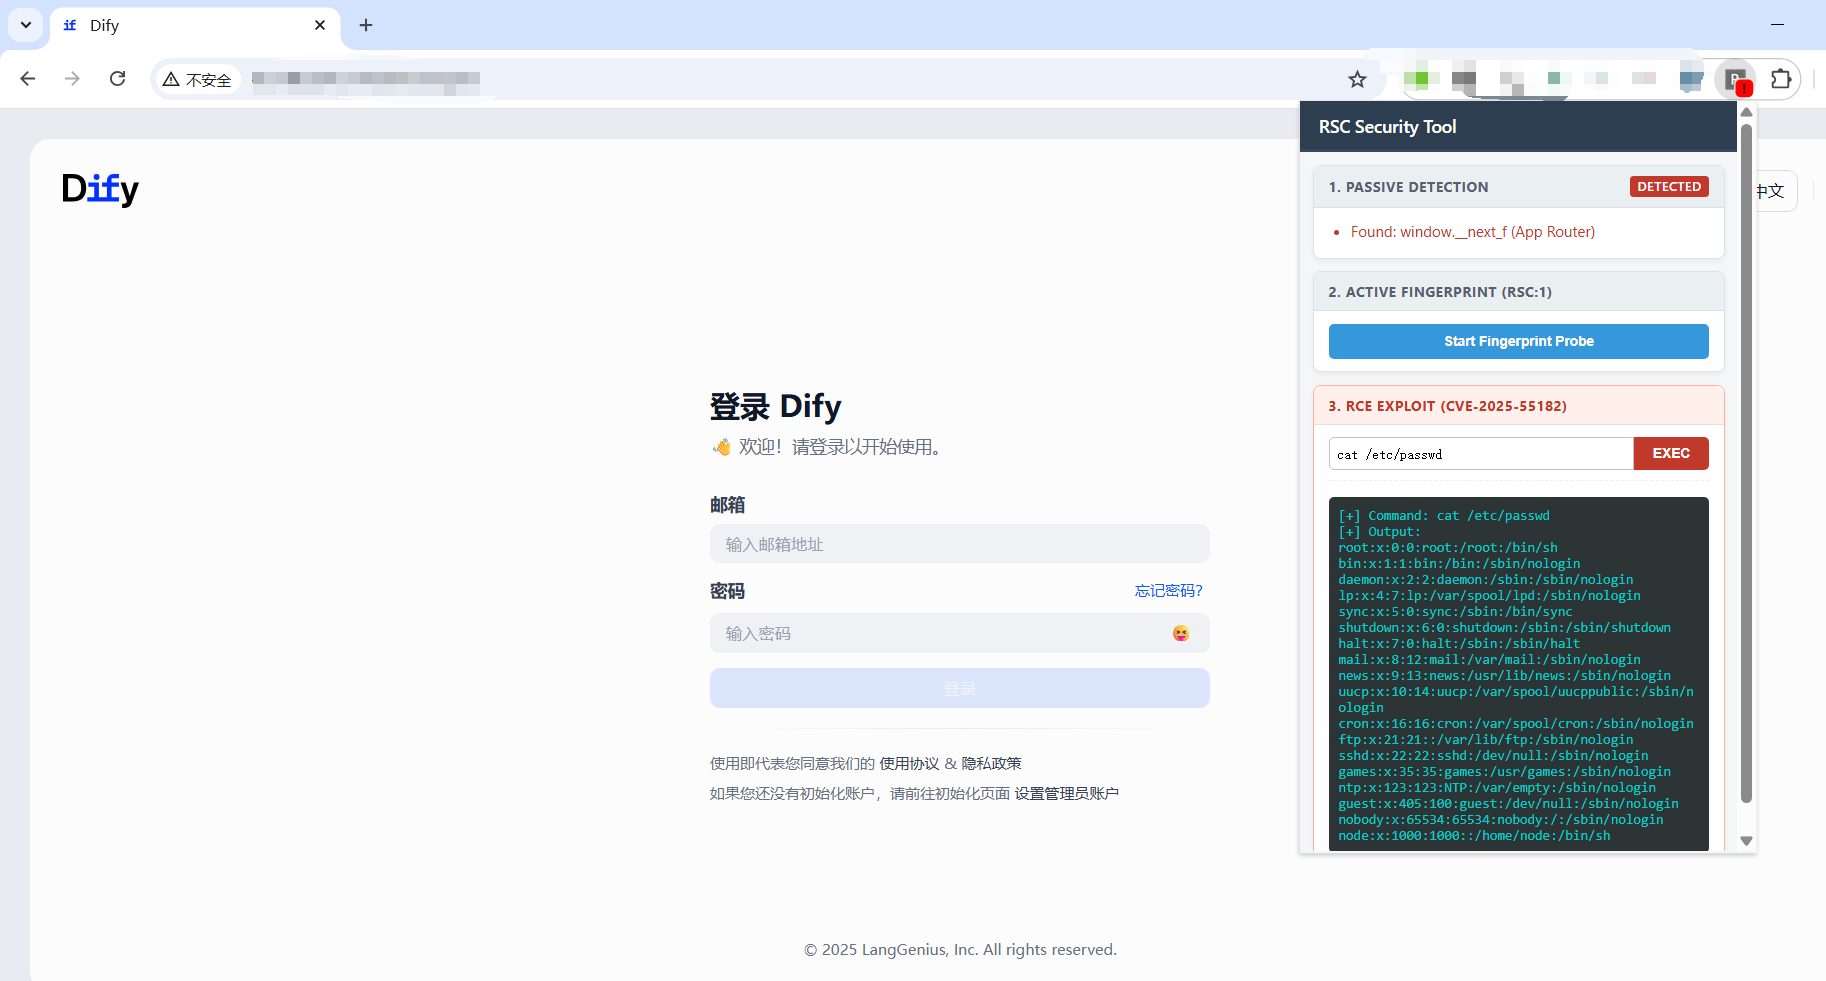 mrknow001/rsc_detector
Supports RSC fingerprinting and exploitation of the React component vulnerability CVE-2025-55182.
 drbloop2000/cve-2026-19745
Learn how I found my first two CVEs by pure accident.
 anuththara2007-w/cve-2025-55182-exploit-extension
A Chrome extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications
 baroi-ai/nepstech-xpon-router-cve-2024-40119
Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
 a17-ba/cve-2025-26202-details
CVE-2025-26202
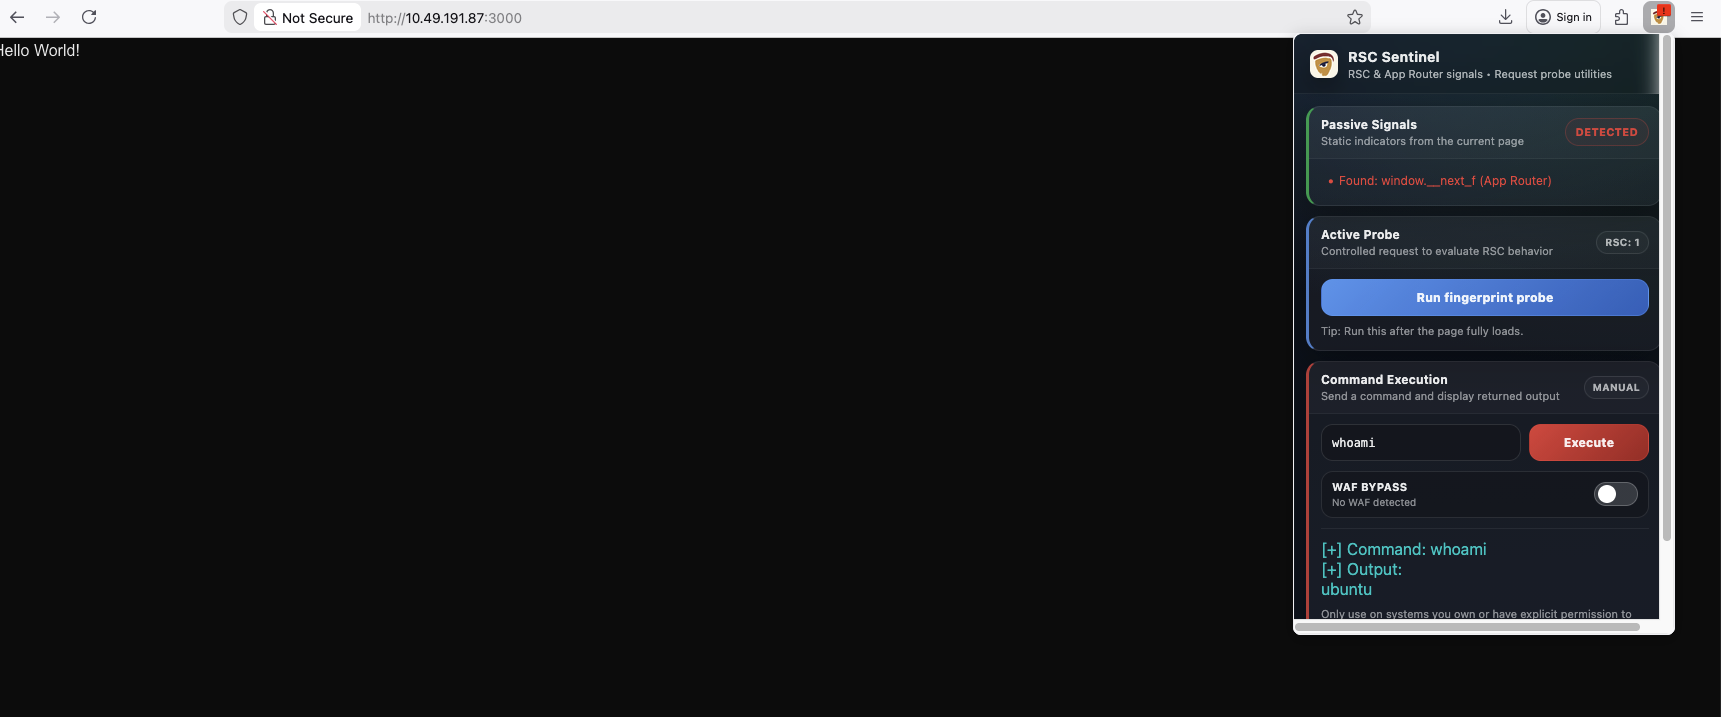 muhammaduwais/react2shell
A Firefox extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications.
 l0lsec/cve-2025-55182-lab
Intentionally vulnerable Next.js RSC Docker lab for CVE-2025-55182 (React2Shell) local testing
 g-rubert/cve-2021-46108
Proof-of-concept for stored cross-site scripting (XSS) vulnerability in D-Link DSL-2730E routers via the username parameter on the maintenance…