
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
React2Shell β€” A Firefox extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications. | Kitploit
Tools/GitHubGitHub/muhammaduwais/react2shell
Vulnerability ScannersInformation GatheringWeb SecurityPenetration TestingLearning & Education
GitHubmuhammaduwais/react2shell

React2Shell

A Firefox extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications.

View Repository
2359 months agoNot yet reviewed
Share

RSC Sentinel

A Firefox extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications.

πŸ‘οΈ Overview

RSC Sentinel is a Firefox browser extension for security researchers and educators who want to observe React Server Components (RSC) and Next.js App Router indicators while browsing. It focuses on passive detection by default, highlighting potential signals without altering site behavior. For authorized assessments, it also offers optional manual tools for active probing and controlled command execution initiated by the user.

🧩 Features

  • Passive Detection: Automatically watches for high-level RSC and App Router indicators during normal browsing.
  • Active Probing: Allows a user-initiated fingerprint request to gather additional signals in a controlled manner.
  • Manual Command Execution: Provides a manual, user-driven execution workflow intended strictly for authorized testing.

🧠 How Detection Works (High-Level)

RSC Sentinel evaluates a combination of runtime indicators, HTTP response headers, and response content patterns that are commonly associated with RSC and App Router behavior. Results are presented as signals and should be interpreted as indicators rather than definitive proof of vulnerability.

🦊 Installation (Firefox)

Install the extension from source using Firefox’s temporary add-on workflow:

  1. Open Firefox and navigate to about:debugging.
  2. Select This Firefox in the left sidebar.
  3. Click Load Temporary Add-on.
  4. Choose the manifest.json file from the project directory.

The extension will load immediately for the current browser session.
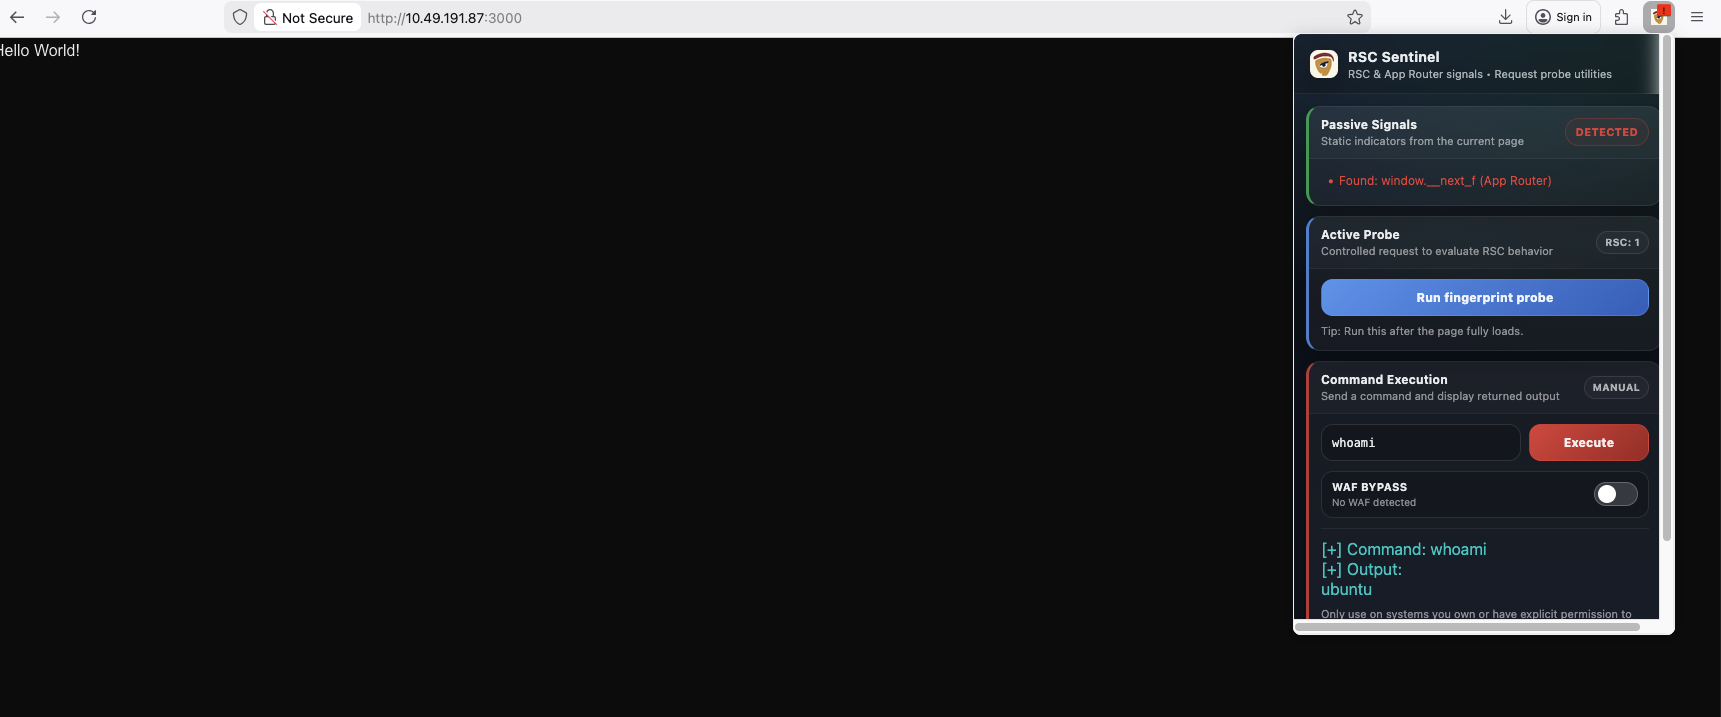
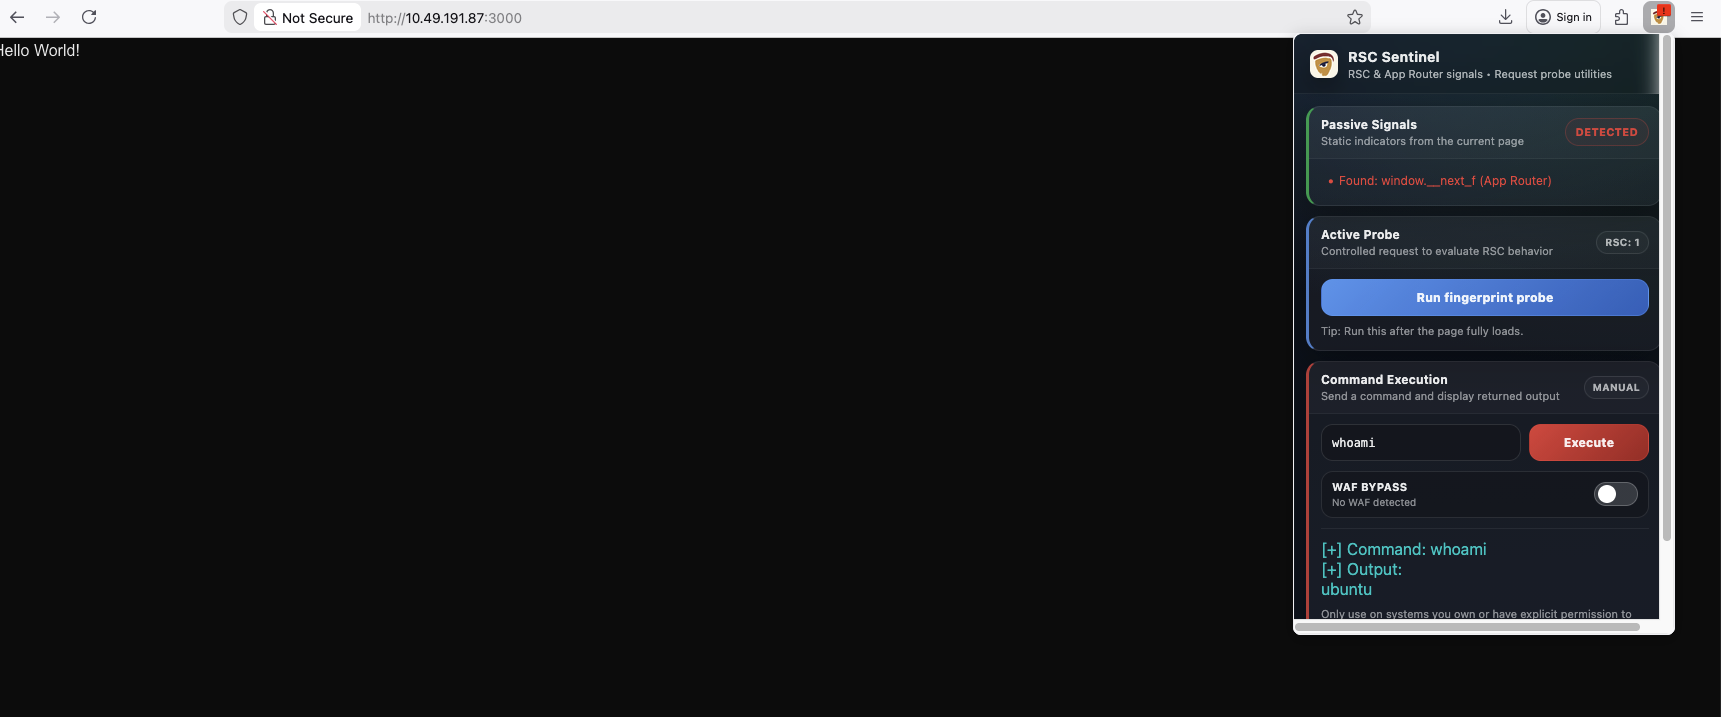
▢️ Usage

  • Browse normally; the extension performs passive detection in the background.
  • Open the extension popup from the Firefox toolbar to view detected signals.
  • Use Run fingerprint probe to initiate a manual probe when authorized.
  • Review results in the popup UI, where passive and active signals are displayed clearly.

Extension in action

πŸ—‚οΈ Project Structure

Example layout for the extension source:

.
β”œβ”€β”€ manifest.json
β”œβ”€β”€ background.js
β”œβ”€β”€ content.js
β”œβ”€β”€ popup.html
β”œβ”€β”€ popup.js
β”œβ”€β”€ images/
β”‚   └── img2.png
β”‚   └── img1.png
└── rules.json

⚠️ Responsible Use / Warning

This extension must only be used on systems you own or where you have explicit permission to test. Misuse of security tooling may be illegal or unethical. Use RSC Sentinel responsibly and in accordance with all applicable laws and policies.

πŸ“œ License & Disclaimer

This project is open-source and provided for educational and authorized security research purposes. The author is not responsible for misuse. Always conduct testing legally, ethically, and with explicit permission.


Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    968
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    347
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    319
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    297

Explore all tools

Browse our collection of tools

View all tools β†’




