Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
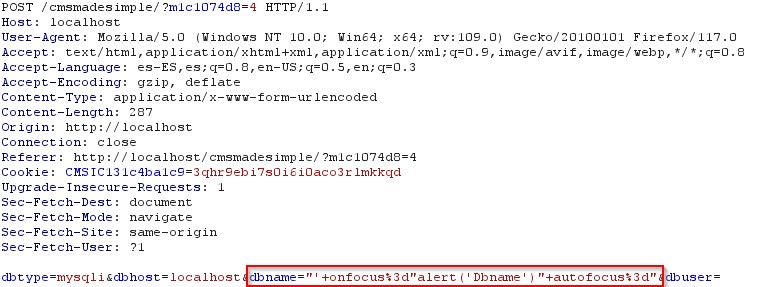
CVE-2023-43339-CMSmadesimple-Reflected-XSS---Installation preview

CVE-2023-43339-CMSmadesimple-Reflected-XSS---Installation

GitHubsromanhu/cve-2023-43339-cmsmadesimple-reflected-xss---installation

CMSmadesimple 2.2.18 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…

exploitationpenetration-testingvulnerability-analysis+2
3 years ago
celerystalk preview
Archived

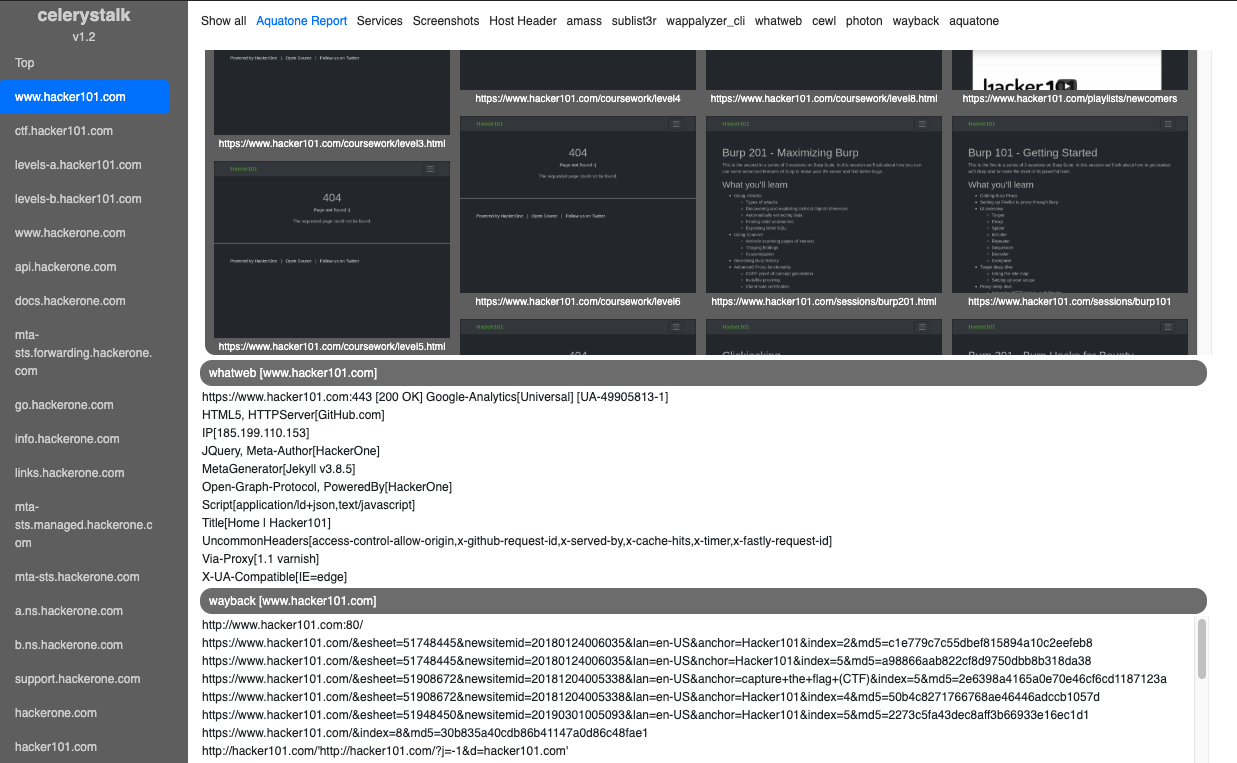
celerystalk

GitHubsethsec/celerystalk

An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.

crawlerdns-subdomain-enumerationinformation-gathering+8
4005 years ago
rengine preview

rengine

GitHubyogeshojha/rengine

reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…

crawlerdns-subdomain-enumerationinformation-gathering+9
8.8k10 months ago
CVE-2006-20001 preview

CVE-2006-20001

GitHubr1az4r/cve-2006-20001

A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…

curated-resourceseducationexploitation+2
3 years ago
CVE-2022-0236 preview
Archived

CVE-2022-0236

GitHubqurbat/cve-2022-0236

Proof of concept for unauthenticated sensitive data disclosure affecting the wp-import-export WordPress plugin (CVE-2022-0236)

exploitationinformation-gatheringpenetration-testing+2
34 years ago
nowafpls preview

nowafpls

GitHubassetnote/nowafpls

Burp Plugin to Bypass WAFs through the insertion of Junk Data

ids-ips-evasionpenetration-testingred-teaming+3
1.5k1 year ago
CVE-2026-33310 preview

CVE-2026-33310

GitHubredyank/cve-2026-33310

Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…

command-and-controlexploitationpayload-generation+2
5 months ago
CVE-2022-28281 preview
Archived

CVE-2022-28281

GitHub0vercl0k/cve-2022-28281

PoC for CVE-2022-28281 a Mozilla Firefox Out of bounds write.

binary-exploitationexploitationvulnerability-analysis+1
734 years ago
svg-cheatsheet preview

svg-cheatsheet

GitHuballanlw/svg-cheatsheet

A cheatsheet for exploiting server-side SVG processors.

curated-resourceseducationinformation-gathering+4
8056 years ago
anubis-fetch preview

anubis-fetch

GitHubfzakaria/anubis-fetch

Like curl, but it gets past Anubis and Cloudflare bot-walls.

anti-botfingerprint-spoofingscripting-automation+3
359 days ago
CVE-2025-14174-analysis preview

CVE-2025-14174-analysis

GitHubtypeconfused/cve-2025-14174-analysis

Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)

binary-analysisexploitationhardware-security+4
38 months ago
lazyrecon preview

lazyrecon

GitHubnahamsec/lazyrecon

This script is intended to automate your reconnaissance process in an organized fashion

dns-analysisinformation-gatheringpenetration-testing+3
2.0k6 years ago
CVE-2018-10583 preview

CVE-2018-10583

GitHubmrtaheramine/cve-2018-10583

An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…

exploitationinformation-gatheringmalware-analysis+2
98 years ago
CVE-2023-43341-Evolution-Reflected-XSS---Installation-Connection- preview

CVE-2023-43341-Evolution-Reflected-XSS---Installation-Connection-

GitHubsromanhu/cve-2023-43341-evolution-reflected-xss---installation-connection-

Evolution CMS 3.2.3 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…

exploitationinformation-gatheringpenetration-testing+3
2 years ago
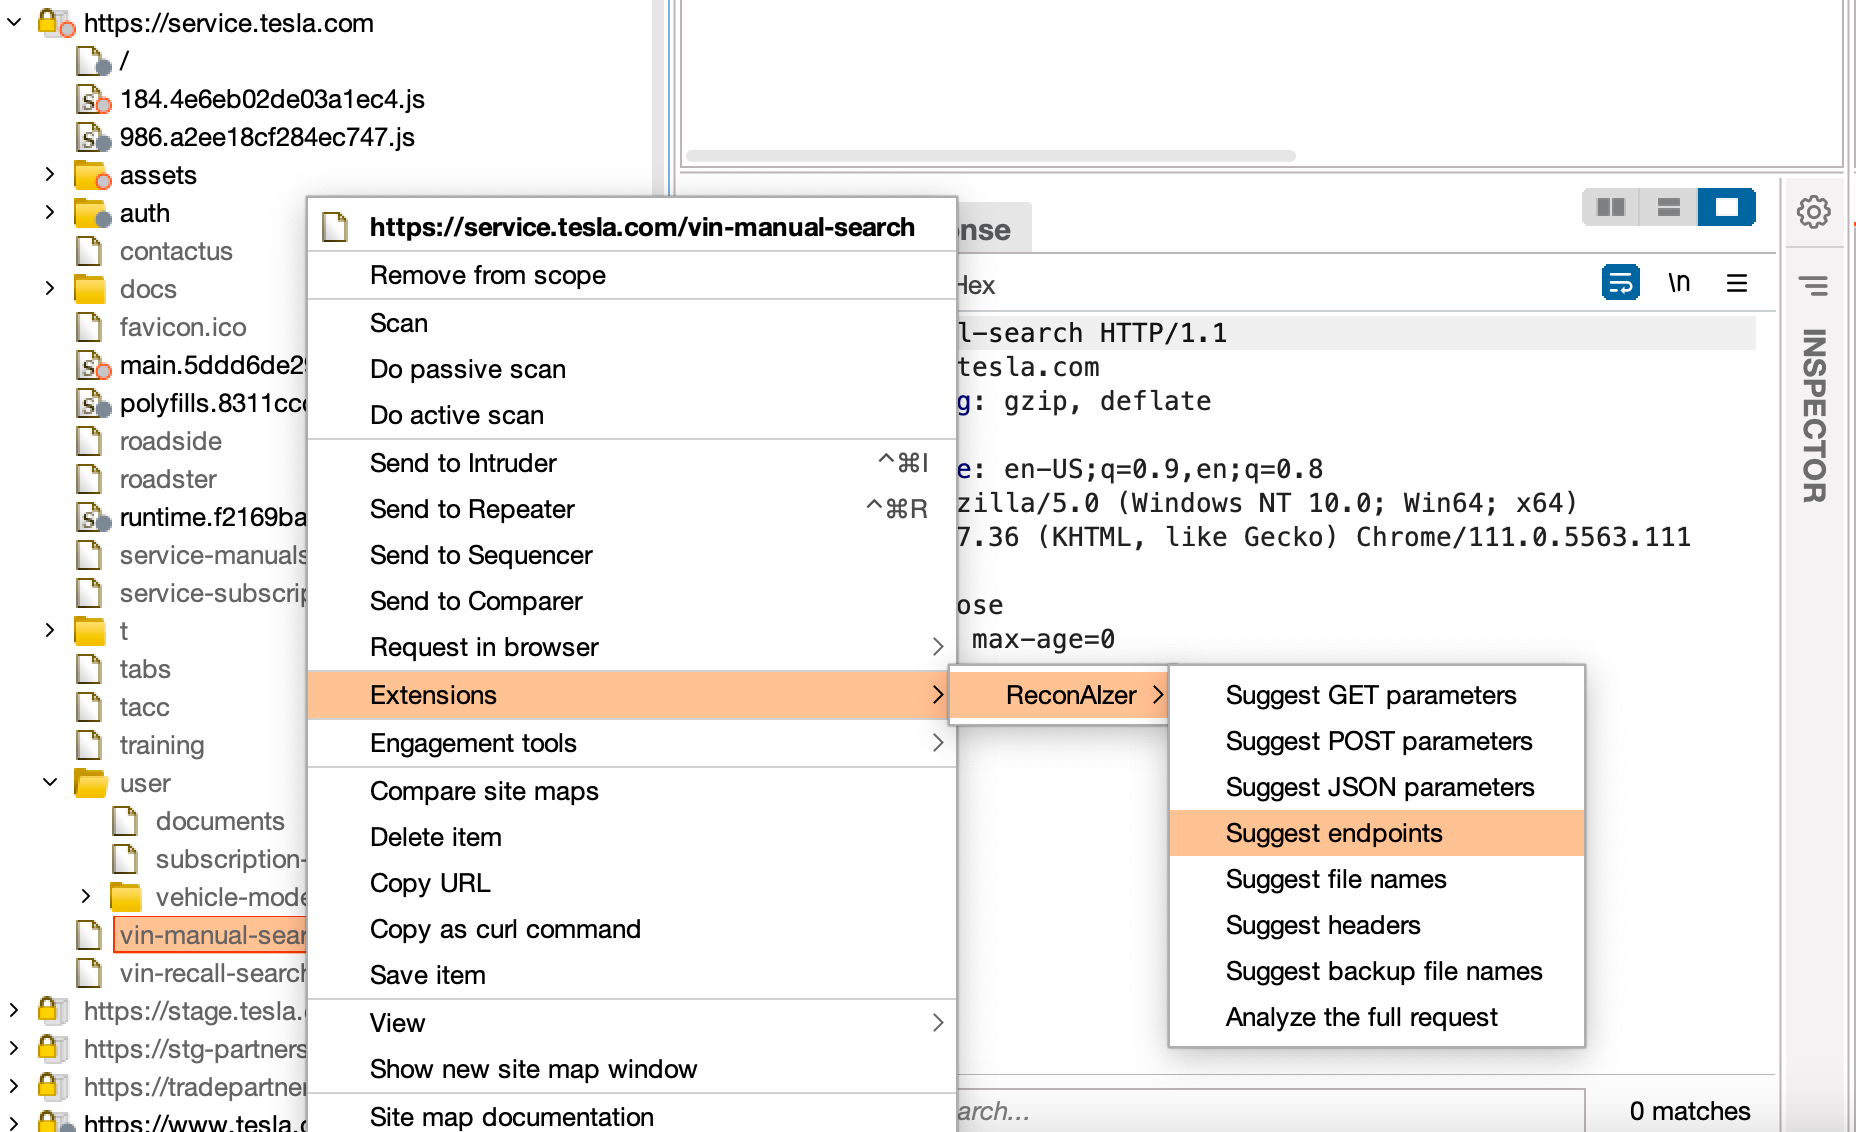
ReconAIzer preview

ReconAIzer

GitHubhisxo/reconaizer

A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!

ai-securityinformation-gatheringreconnaissance+1
9113 years ago
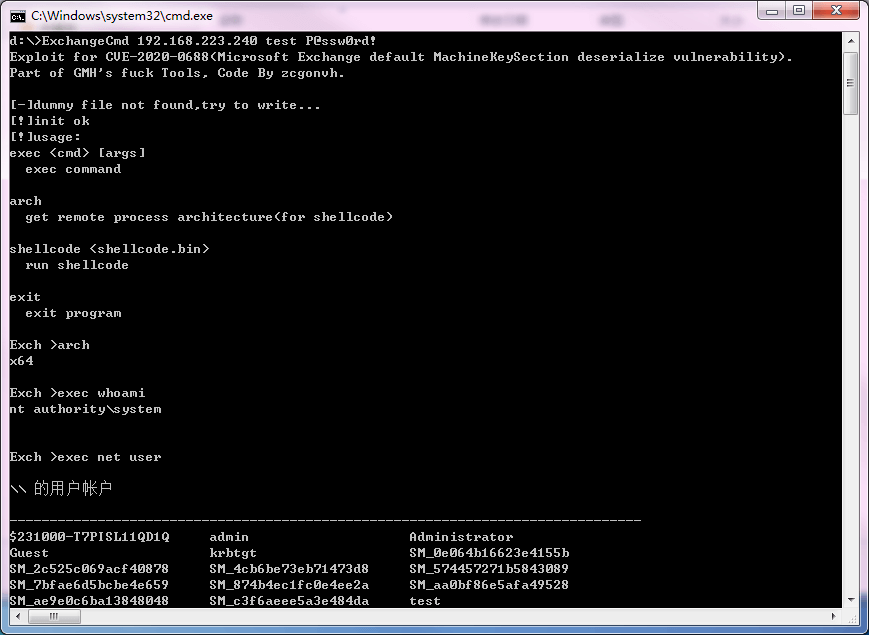
CVE-2020-0688 preview

CVE-2020-0688

GitHubzcgonvh/cve-2020-0688

Exploit and detect tools for CVE-2020-0688

exploitationinformation-gatheringpenetration-testing+2
3546 years ago
inter-recon preview

inter-recon

GitHubinternon/inter-recon

Script to perform automatic initial web and vulnerability recon

dns-analysisfuzzinginformation-gathering+7
84 years ago
CVE-2026-25938-FUXA-Unauthenticated-RCE preview

CVE-2026-25938-FUXA-Unauthenticated-RCE

GitHubjudgedbykira/cve-2026-25938-fuxa-unauthenticated-rce

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

exploitationiot-securitypayload-development+6
11 month ago
Previous123Next