Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
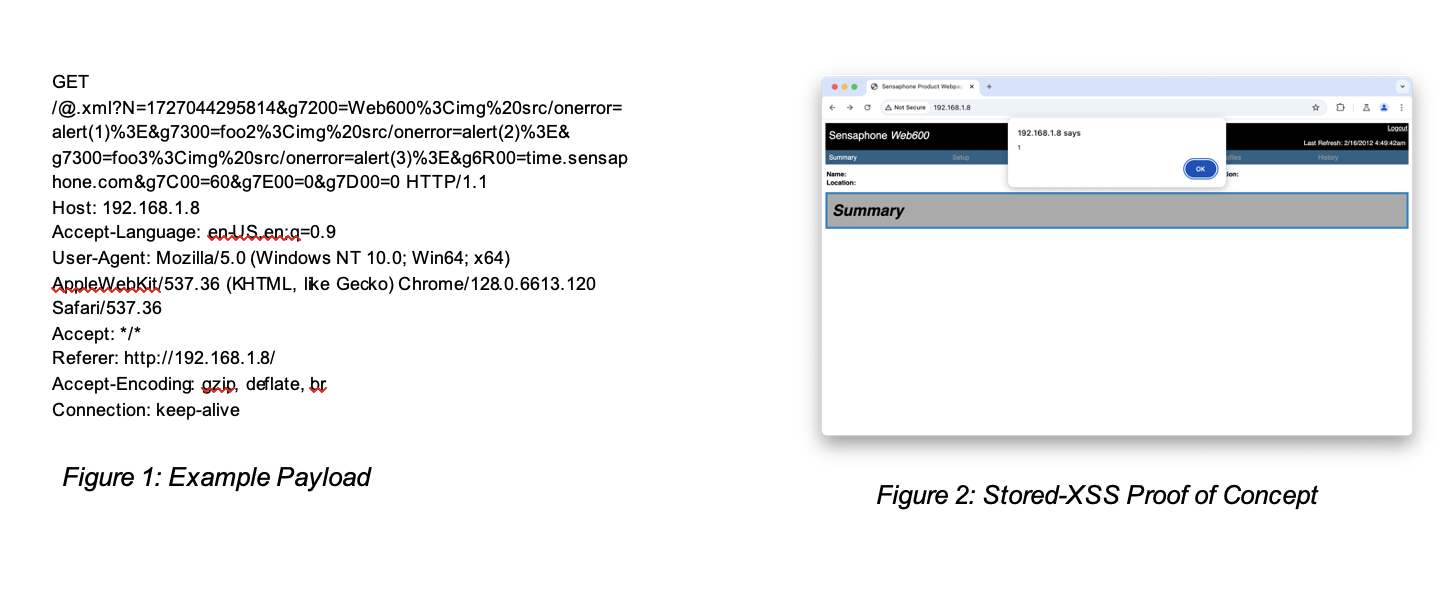
CVE-2024-55040-Sensaphone-XSS preview

CVE-2024-55040-Sensaphone-XSS

GitHubtcbutler320/cve-2024-55040-sensaphone-xss

Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)
exploitationiot-securitypenetration-testing+3
1
1 year ago
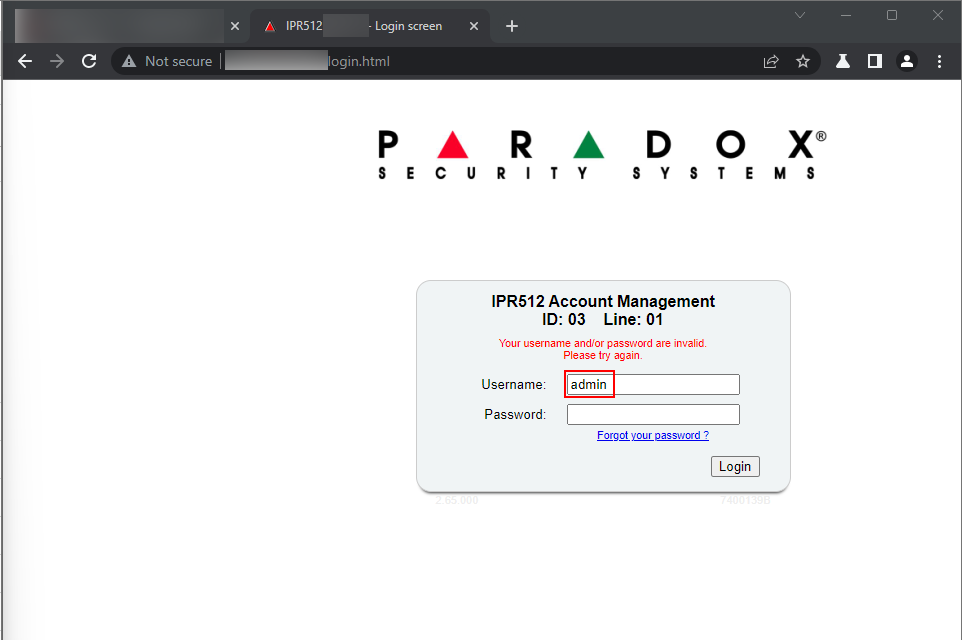
Injection-vulnerability-in-Paradox-Security-Systems-IPR512-CVE-2023-24709-PoC preview

Injection-vulnerability-in-Paradox-Security-Systems-IPR512-CVE-2023-24709-PoC

GitHubdarknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc

In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…

exploitationiot-securitypenetration-testing+3
3 years ago
boa-detector preview

boa-detector

GitHubcorelight/boa-detector

A vulnerable Boa web server detector.
iot-securitynetwork-securitysupply-chain-security+3
3 years ago
Digisol-DG-GR1321-s-Improper-Access-Control-CVE-2024-4231 preview

Digisol-DG-GR1321-s-Improper-Access-Control-CVE-2024-4231

GitHubredfox-security/digisol-dg-gr1321-s-improper-access-control-cve-2024-4231

Exploit for CVE-2024-4231, an improper access control vulnerability in Digisol DG-GR1321 routers, allowing unauthorized access to sensitive…

exploitationiot-securitymisconfiguration+3
2 years ago
CVE-2020-14965 preview

CVE-2020-14965

GitHubg-rubert/cve-2020-14965

TP-LINK Multiple HTML Injection Vulnerabilities

embedded-systems-securityhardware-securityiot-security+3
6 years ago
CVE-2021-46108 preview

CVE-2021-46108

GitHubg-rubert/cve-2021-46108

Proof-of-concept for stored cross-site scripting (XSS) vulnerability in D-Link DSL-2730E routers via the username parameter on the maintenance…

exploitationiot-securitypenetration-testing+3
4 years ago
Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232 preview

Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232

GitHubredfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232

Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
hardware-securityiot-securitymisconfiguration+3
2 years ago
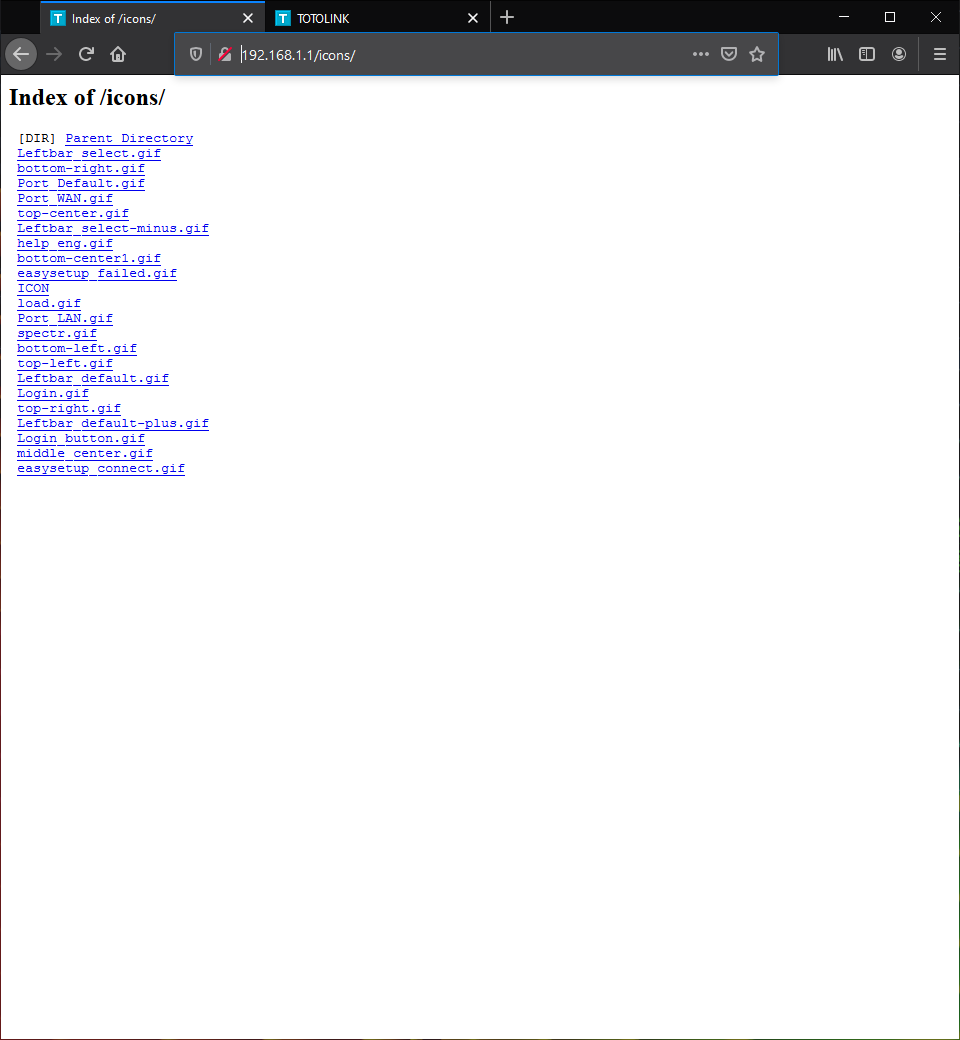
CVE-2020-27368 preview
Archived

CVE-2020-27368

GitHubswzhouu/cve-2020-27368

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
embedded-systems-securityinformation-gatheringiot-security+3
13 years ago
CVE-2025-67159 preview

CVE-2025-67159

GitHubremenis/cve-2025-67159

Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.

authenticationexploitationhardware-iot-security+3
10 months ago
CVE-2021-40859 preview

CVE-2021-40859

GitHubpussycat0x/cve-2021-40859

Auerswald VoIP System Secret Backdoors -PoC
exploitationhardware-securityiot-security+3
44 years ago
CVE-2025-45620 preview

CVE-2025-45620

GitHubweedl/cve-2025-45620

Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
authenticationhardware-securityiot-security+3
1 year ago
dref preview

dref

GitHubreverseclabs/dref

DNS Rebinding Exploitation Framework

dns-analysisexploitationiot-security+3
4945 years ago
SecureTea-Project preview

SecureTea-Project

GitHubowasp/securetea-project

The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)

defensive-toolsintrusion-detectioniot-security+4
3023 years ago
cve-2020-9375 preview

cve-2020-9375

GitHubthewhiteh4t/cve-2020-9375

TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
exploitationhardware-iot-securityiot-security+2
206 years ago
CVE-2026-0073-Research preview

CVE-2026-0073-Research

GitHubnovaek/cve-2026-0073-research

CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.

binary-analysisexploitationreverse-engineering+2
55 months ago
CVE-2023-31594 preview

CVE-2023-31594

GitHubyozarseef95/cve-2023-31594

IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
exploitationhardware-securityiot-security+3
20 days ago
CVE-2026-28767 preview

CVE-2026-28767

GitHubmichaeladamgroberman/cve-2026-28767

CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
api-securitycloud-securityiot-security+3
5 months ago
CVE-2025-48461 preview

CVE-2025-48461

GitHubjoelczk/cve-2025-48461

Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…

authenticationexploitationiot-security+3
1 year ago
Previous123Next