
waf-checker
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
api-security-testingids-ips-evasioninformation-gathering+6
35
sech0us3/waf-checkerAutomated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
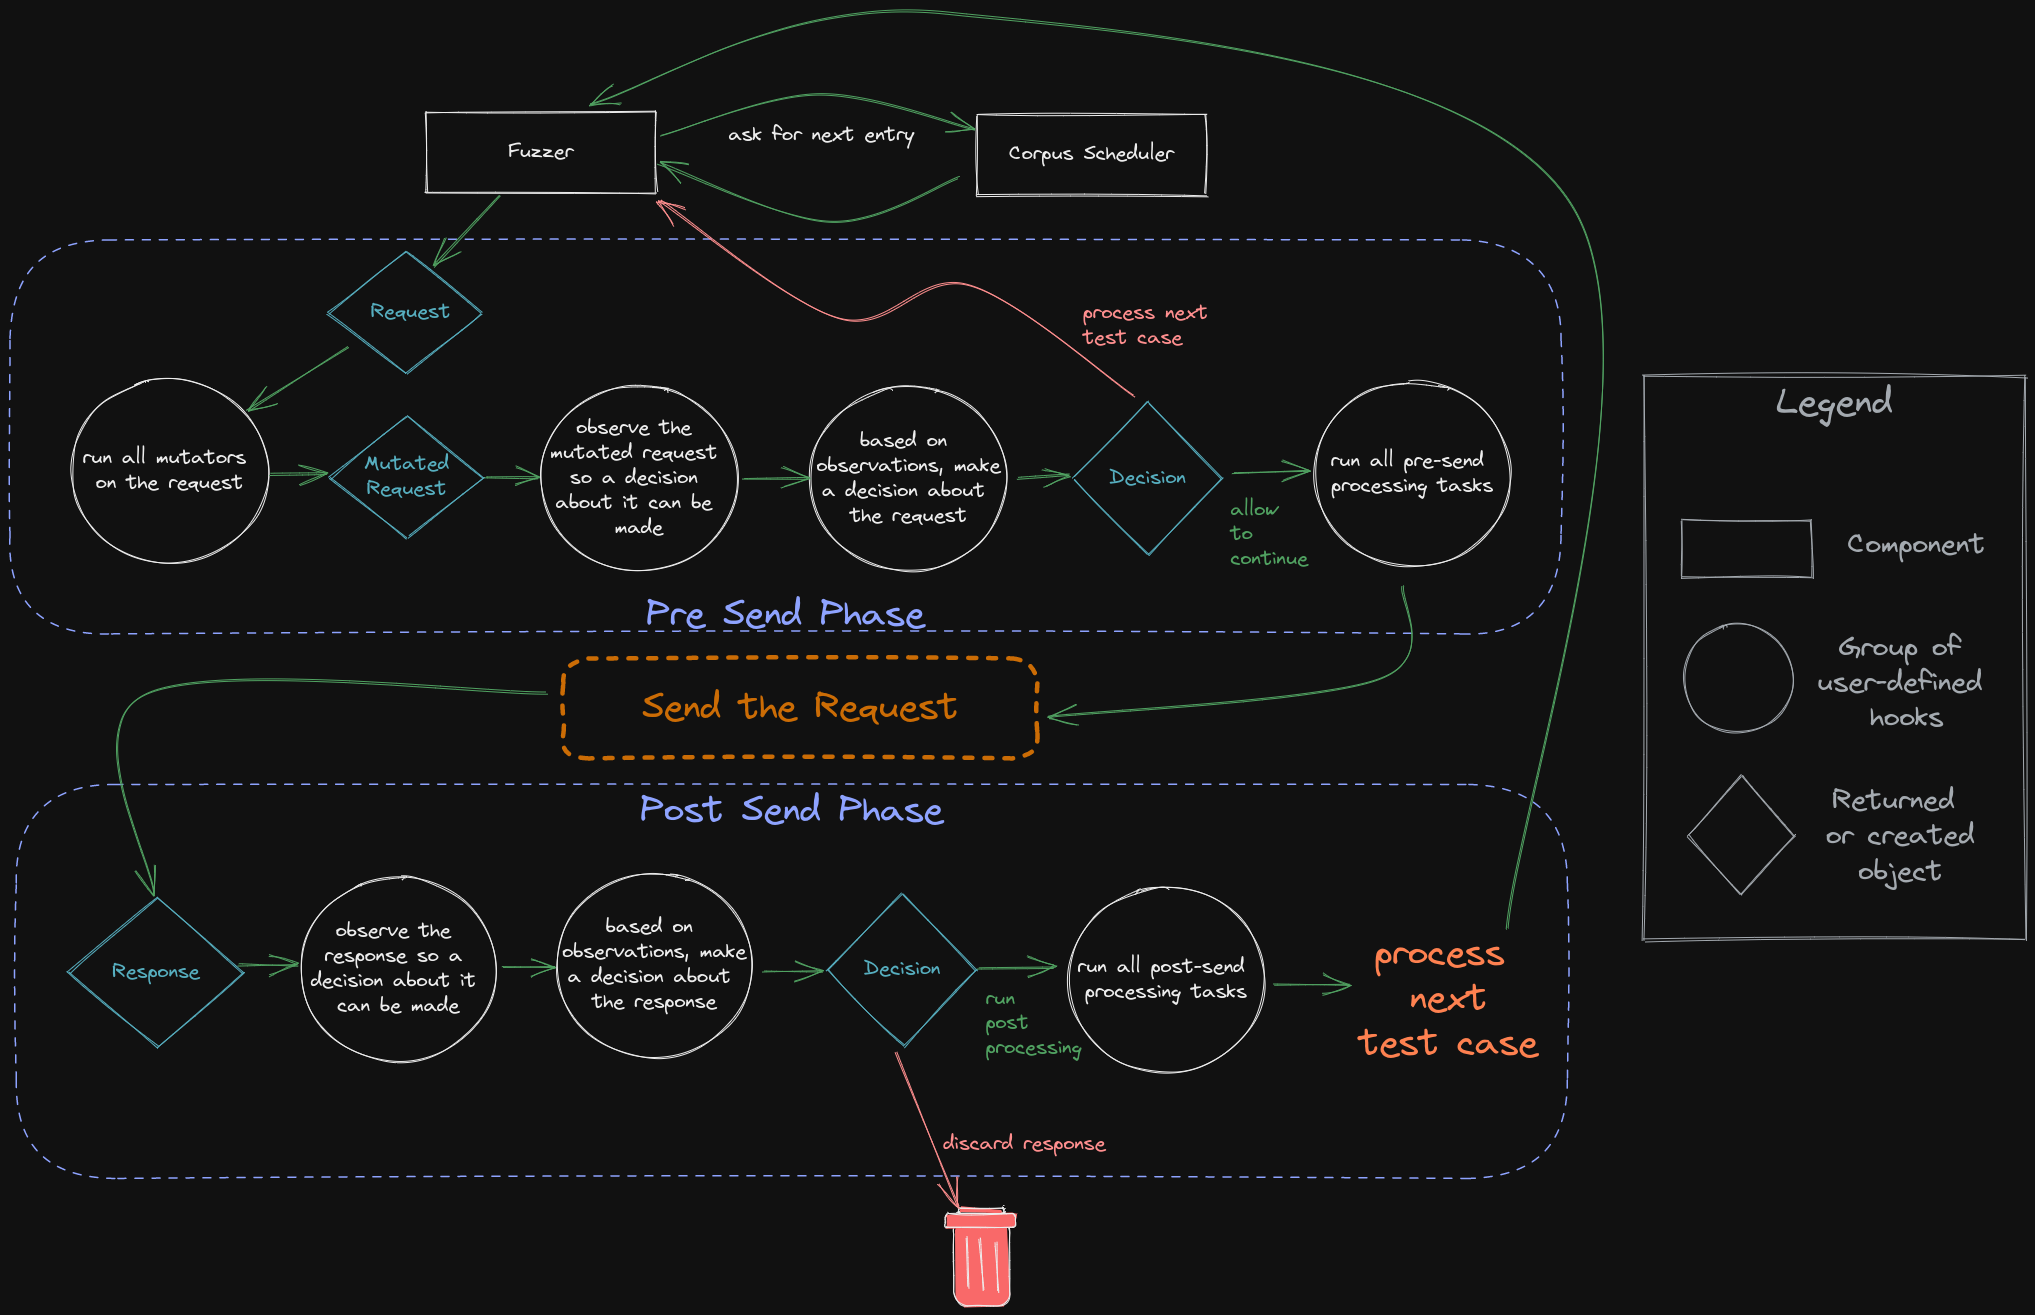 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 justmorpheus/burp-automation
Performing automated scan using Burp Suite Pro & Vmware Burp Rest API
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
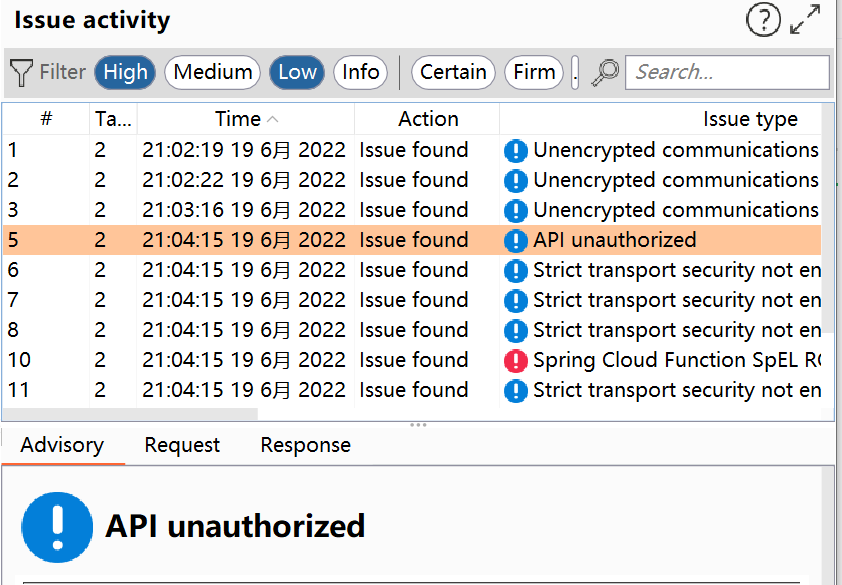 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
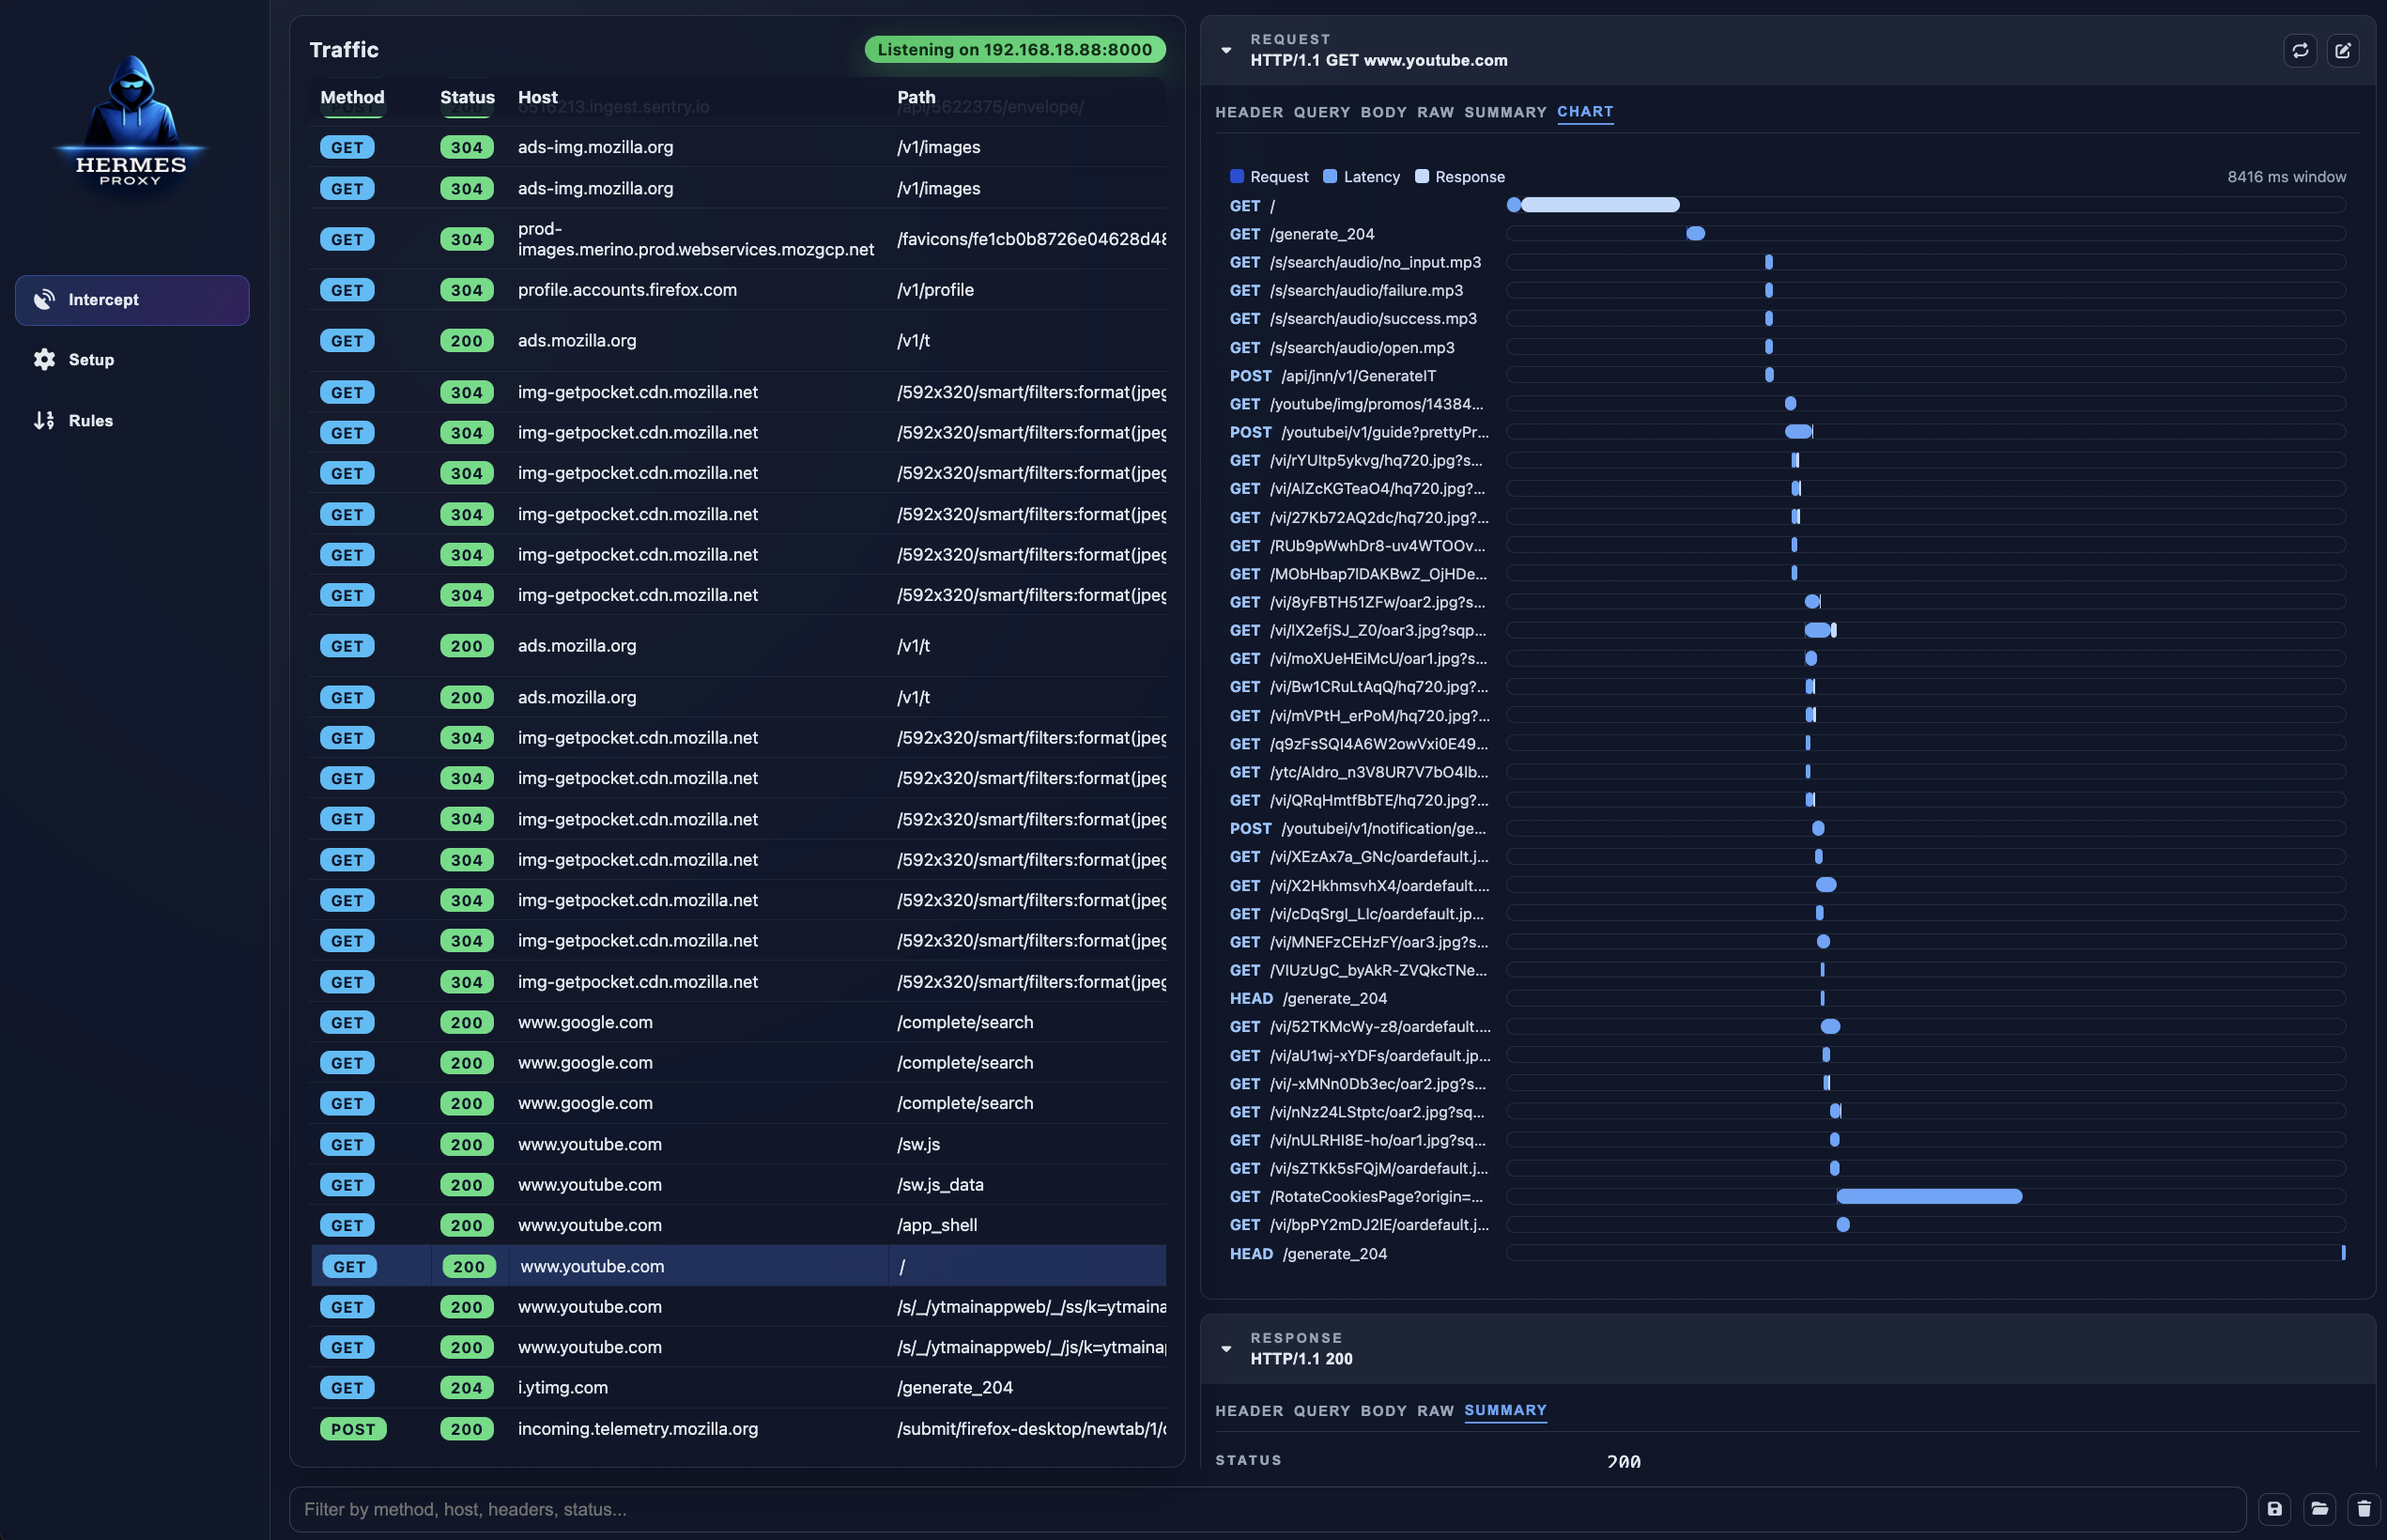 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
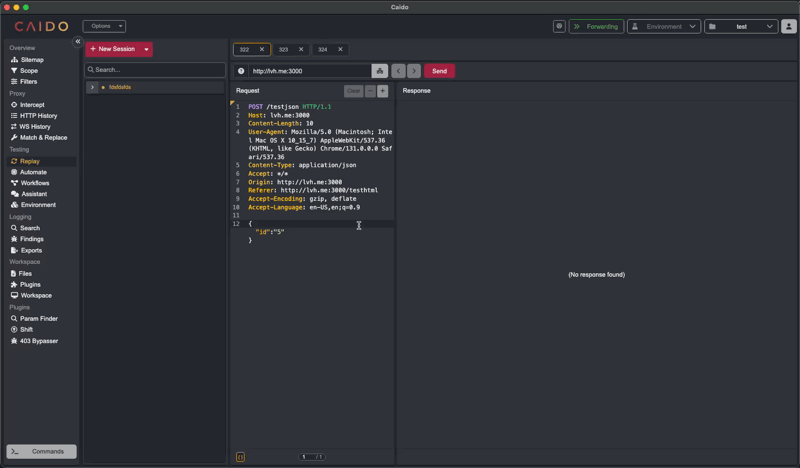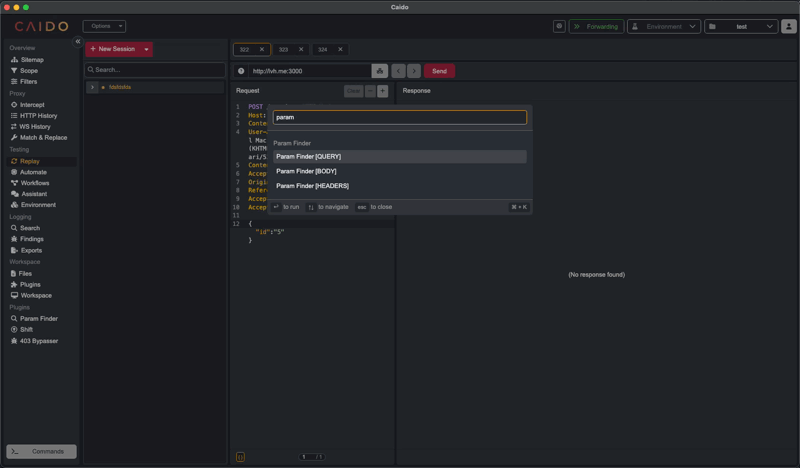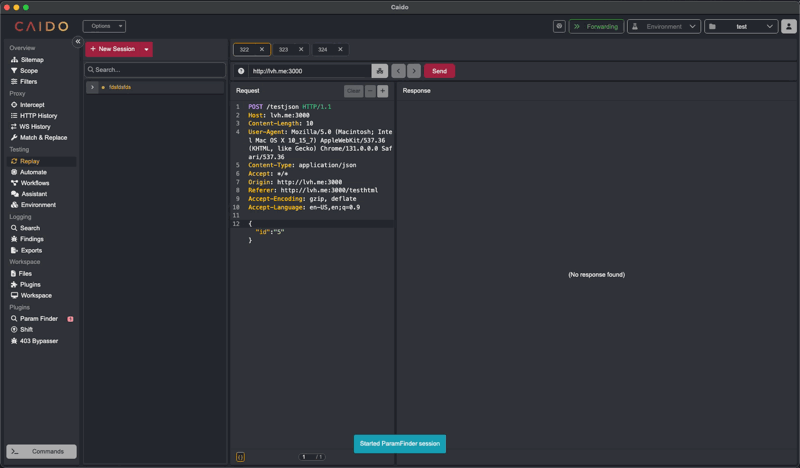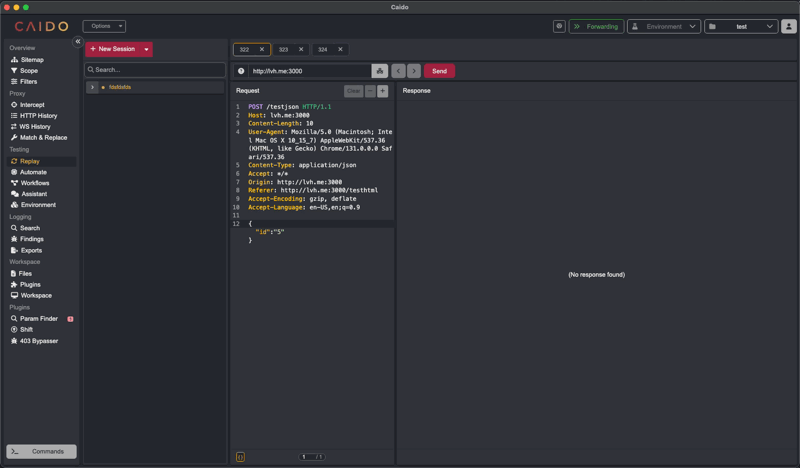 caido-community/paramfinder
Discover hidden parameters in Caido
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…