

CVE-2026-87902
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
2
bhideki/cve-2026-87902Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 cybertechajju/cve-2026-23869-exploit
Automated exploit tool for CVE-2026-23869, a remote DoS in React Server Components. Includes PoC, Nuclei template, and scanning scripts for detection…
 newlinesec/cve-2024-50603
Nuclei template-based proof-of-concept for CVE-2024-50603, enabling automated detection and exploitation of the vulnerability in target environments.
 louiselalanne/cve-2023-49314
Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…
 dinosn/cve-2026-3844
Proof-of-concept exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to remote code execution in Breeze Cache <= 2.4.4.…
 d154573r-4v3r73d/cve-2024-47875
Repository dedicated to CVE-2024-47875, providing proof-of-concept material and analysis for this specific vulnerability.
 firebasky/cve-2026-39363
Exploit for CVE-2026-39363, a Vite Dev Server WebSocket arbitrary file read vulnerability, with Python and Node.js scripts for automated exploitation…
 honeyb33z/cve-2020-11023-scanner
Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
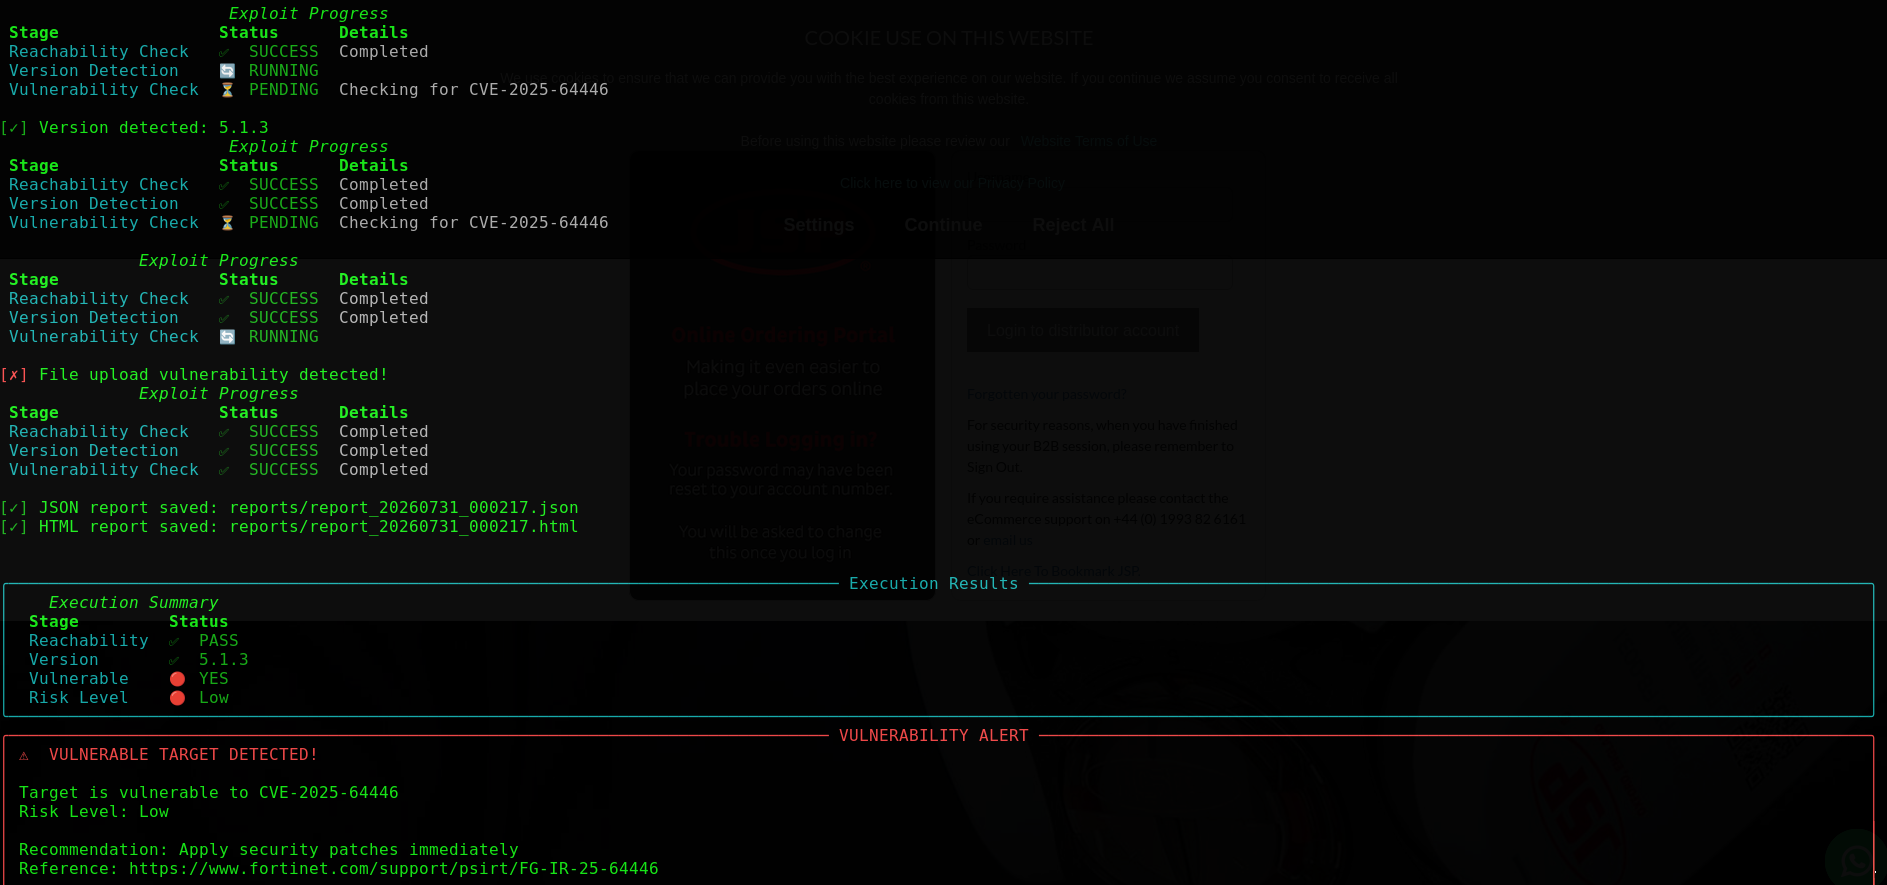 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
 zycoder0day/cve-2026-8732
Automated 8-phase exploit for CVE-2026-8732, an unauthenticated privilege escalation in WP Maps Pro ≤ 6.1.0. Uses multiprocessing and asyncio to scan…
 0x00phantom-hat/cve-2026-11991-exploit
Automated exploit for CVE-2026-11991, an authorization bypass in FlowForms WordPress plugin allowing Contributor+ users to publish any draft form via…
 dodgenefoli/cve-2025-64512
Automated proof-of-concept exploit for CVE-2025-64512 that accepts Target and Upload_dir parameters to test vulnerable file-upload functionality in…
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
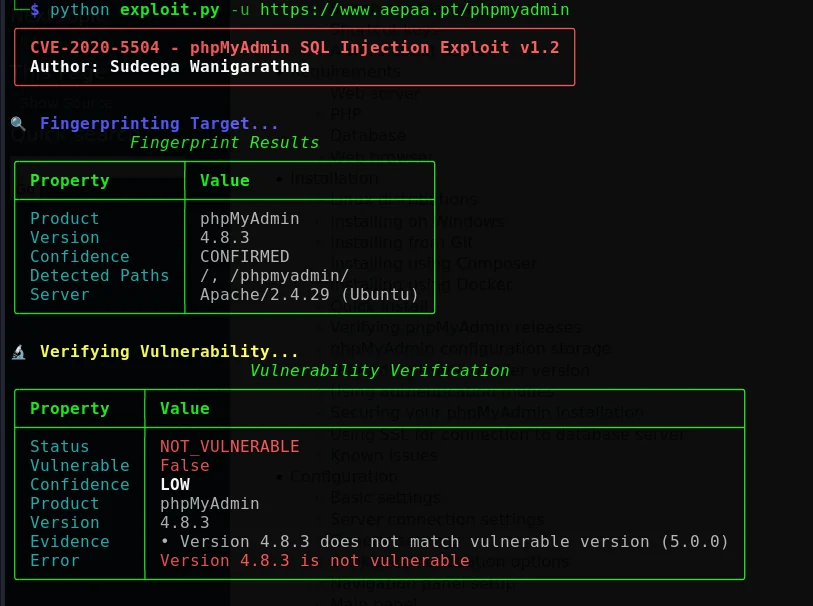 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
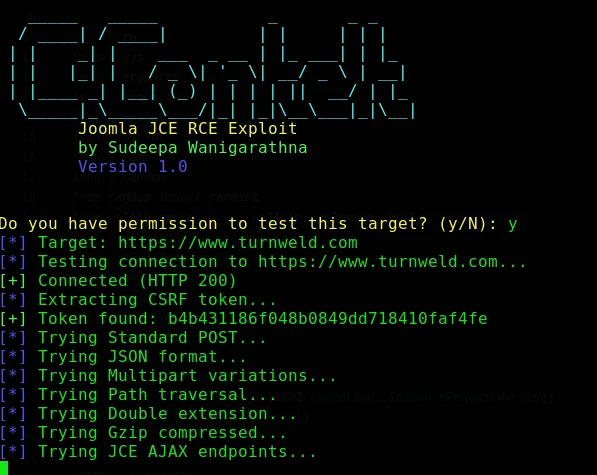 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 wezoomagency/grafxploit
Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…