
snare
 mushorg/snare
Super Next generation Advanced Reactive honEypot
information-gatheringthreat-intelligenceweb-security
mushorg/snareSuper Next generation Advanced Reactive honEypot
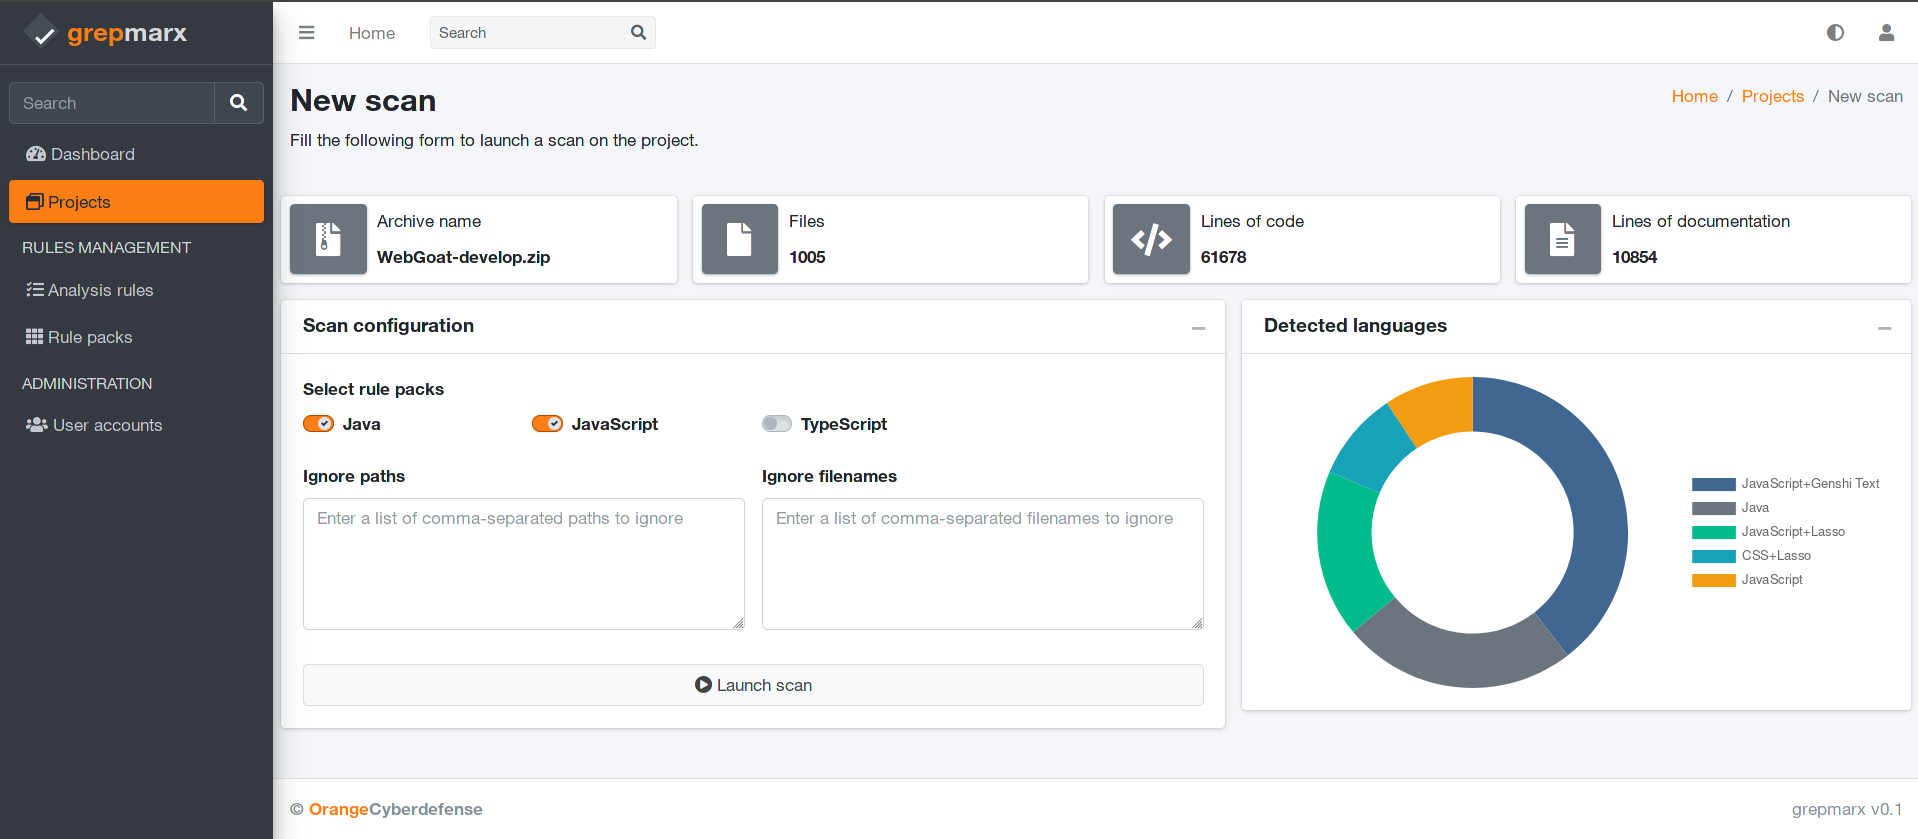 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.

 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
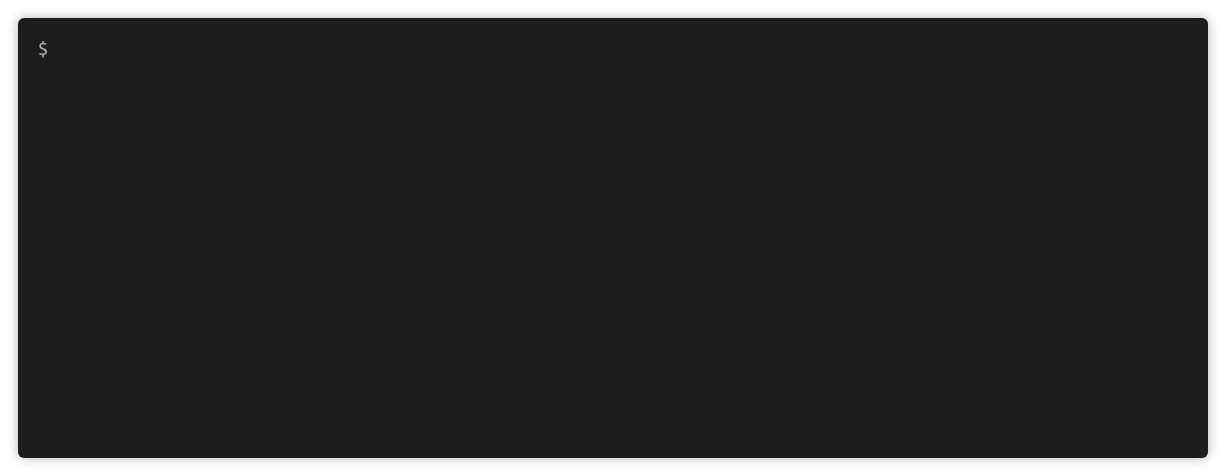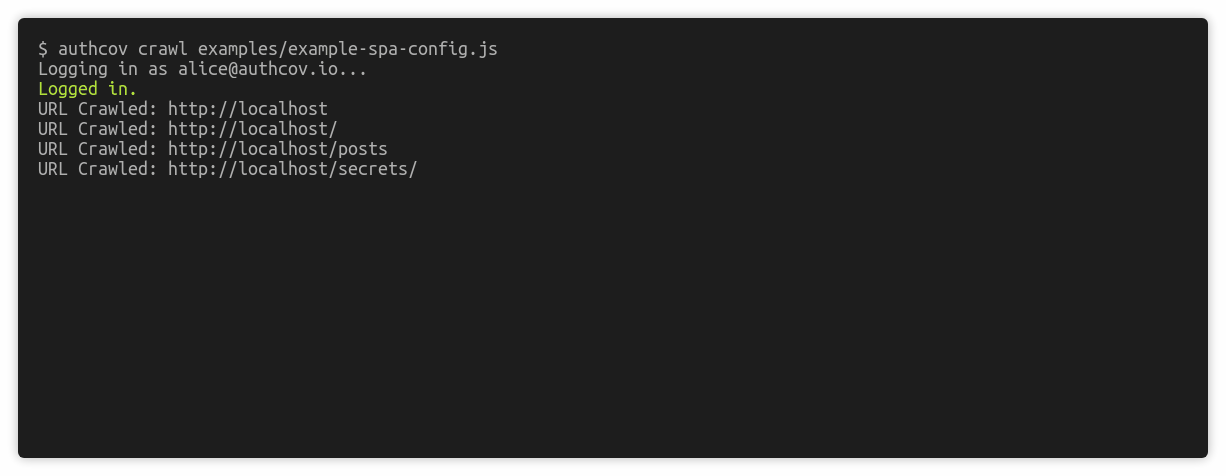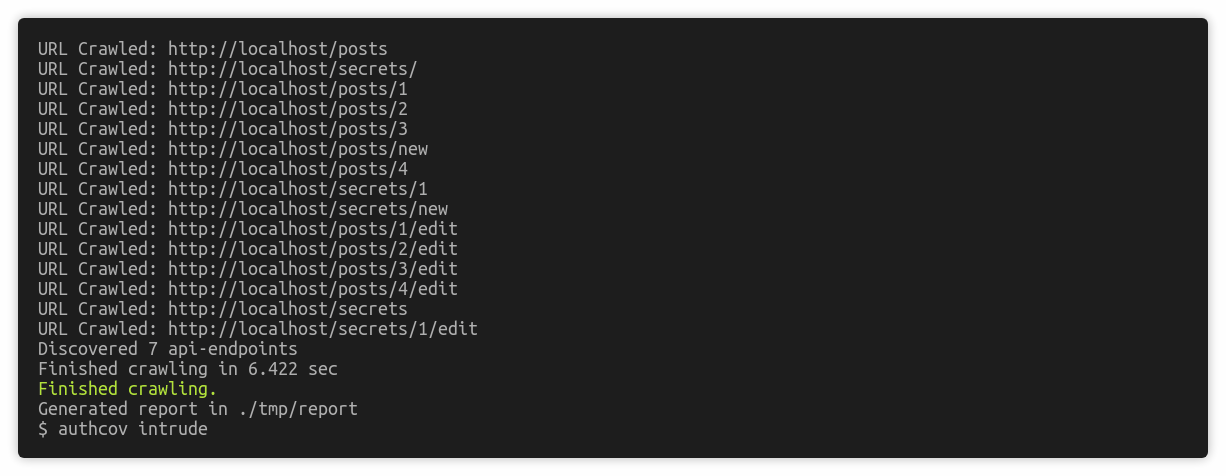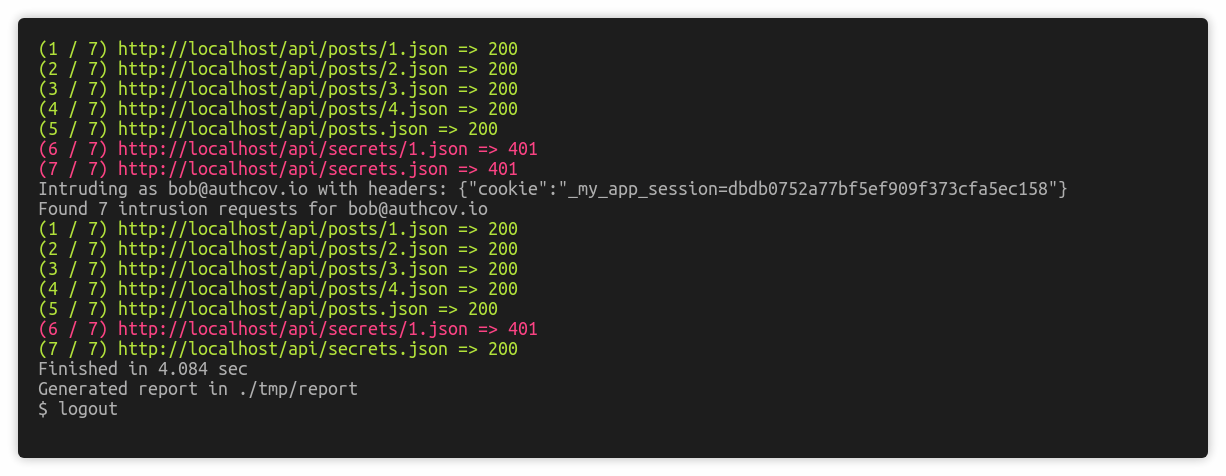 authcov/authcov
Web app authorisation coverage scanning
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
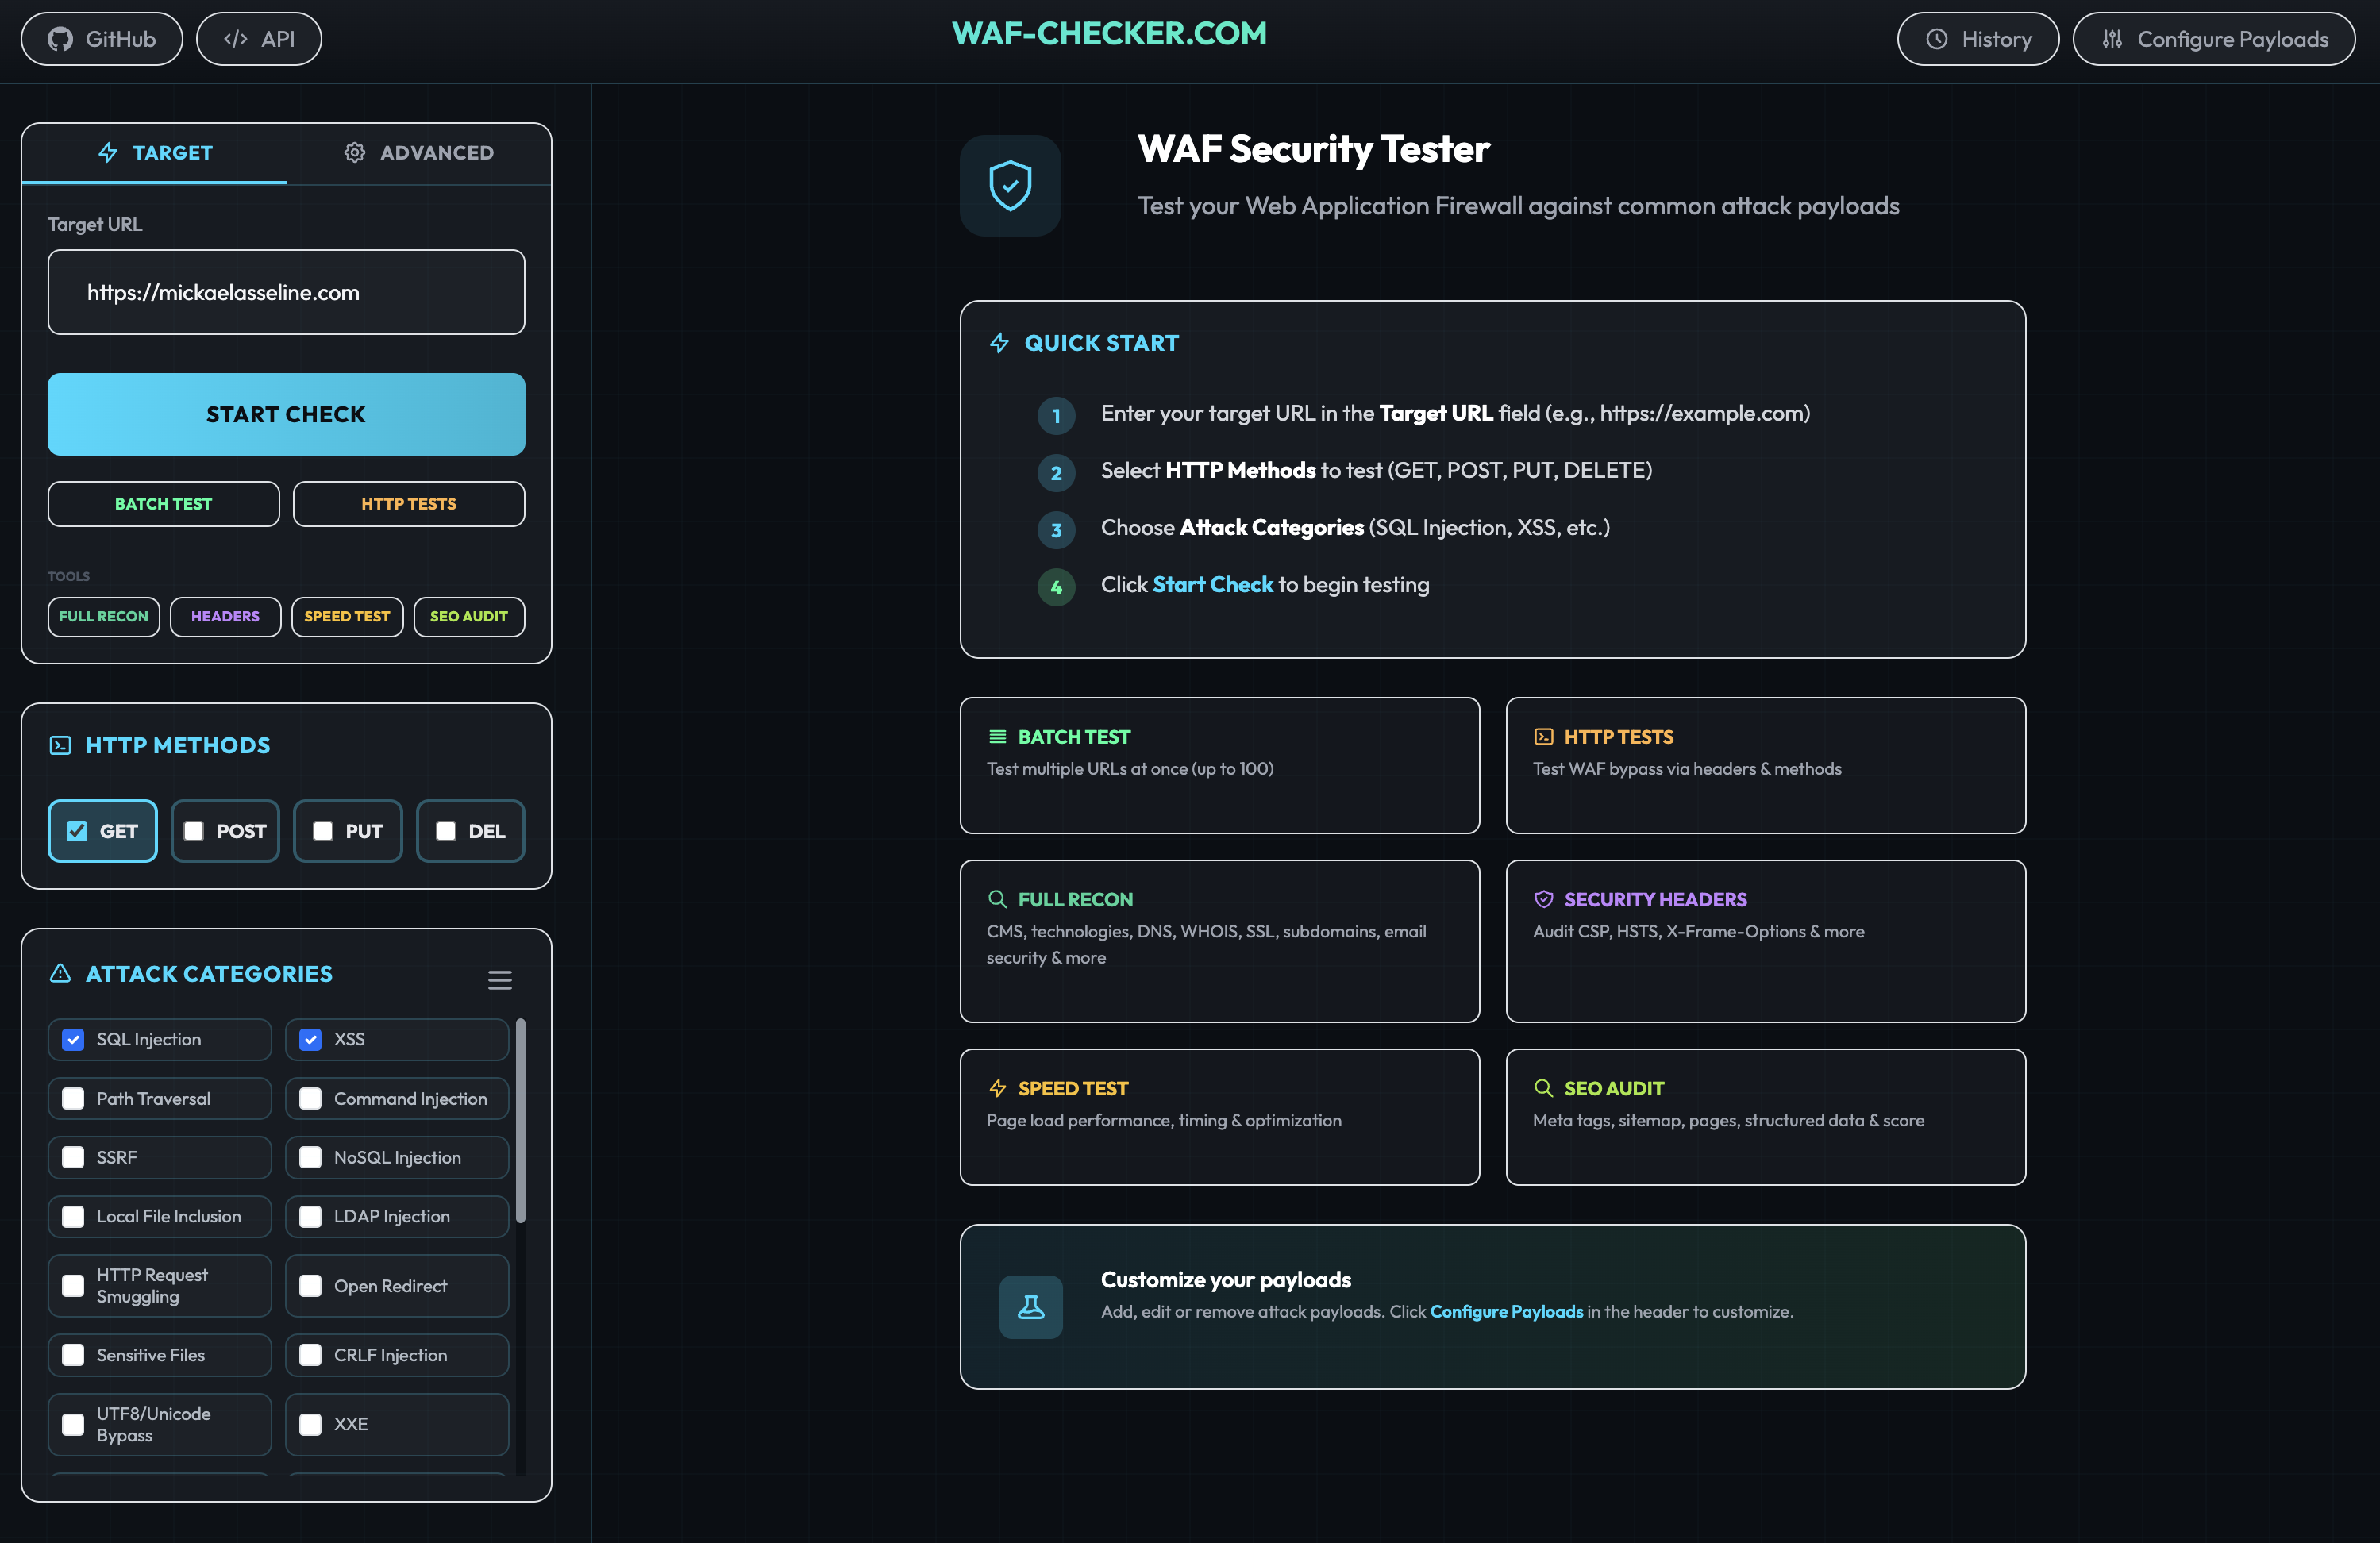 papamica/waf-checker
Tests your WAF with +160 payloads
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 mariagarber/xss-scanner
XSS scanner that detects Cross-Site Scripting vulnerabilities in website by injecting malicious scripts

 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 shalevo13/se7enslip
A scanner and testter of the CVE-2025-11001 of 7-zip
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning
 pracharapol/cve-2025-45960
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in tawk.to Live Chat 1.6.1, demonstrating JavaScript injection via unsanitized…
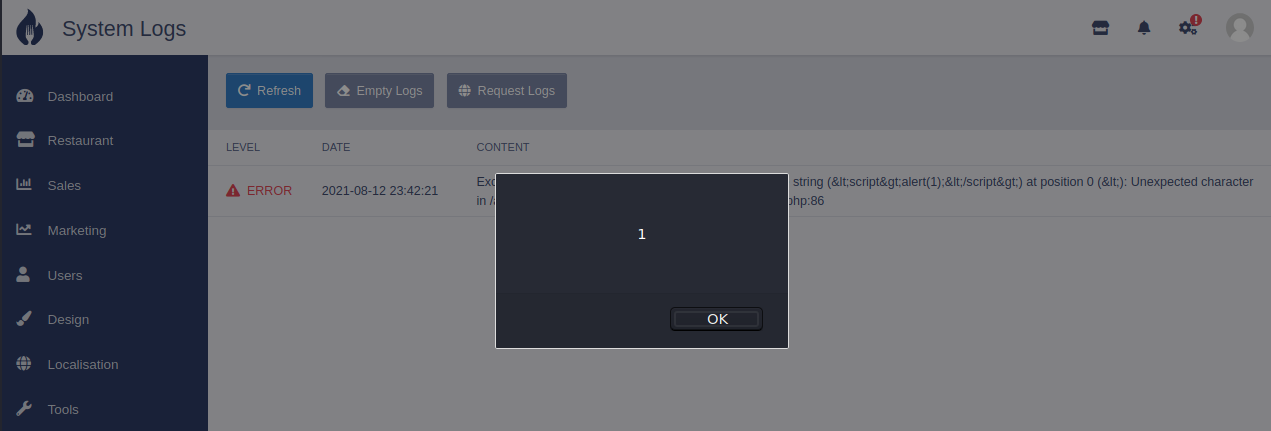 huskyhacks/cve-2021-38699-stored-xss
Stored XSS in TastyIgniter v3.0.7 Restaurtant CMS
 theexploiters/cve-2024-40111-exploit
Exploit For: CVE-2024-40111: Stored Cross-Site Scripting (XSS) in Automad 2.0.0-alpha.4