

AhsayCBS-Auth-Bypass-RCE
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
authenticationexploitationpayload-development+5
4
horizon3ai/ahsaycbs-auth-bypass-rceA proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 shadowforge-cyber/cve-2026-104286-poc
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 petriqore/cve-2026-26026_poc
PoC script for CVE-2026-26026 GLPI versions 11.0.0 through 11.0.5
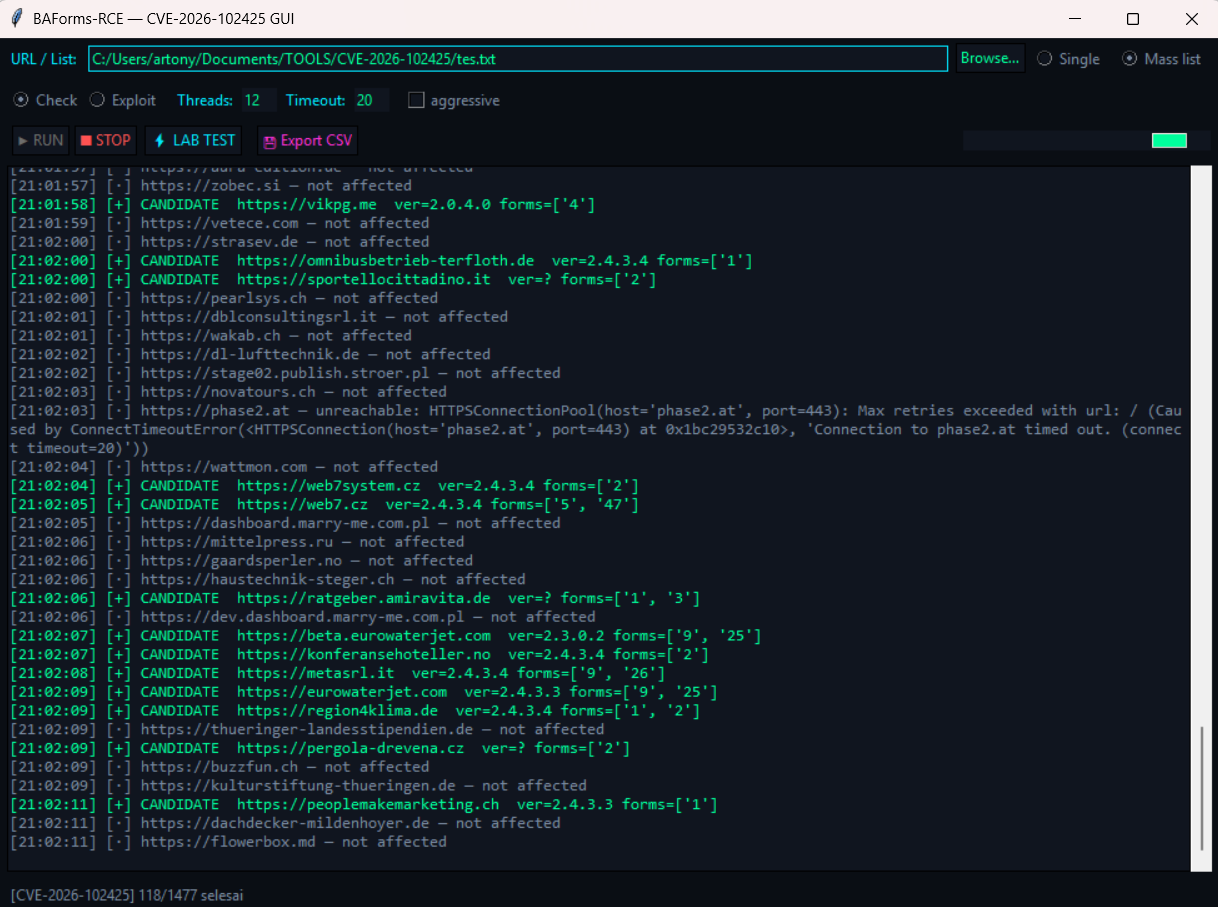 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 murrez/cve-2026-102427
Python 3 PoC for CVE-2026-102427, an unauthenticated upload RCE in OrdaSoft Joomla CCK (com_os_cck) via task=getContent and site/uploader.php using a…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 murrez/cve-2026-18143
Python PoC that checks and exploits CVE-2026-18143, an unauthenticated arbitrary file upload in Addify Request a Quote for WooCommerce ≤ 2.9.2 via…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 madfxr/xss2shell-poc
XSS2Shell: WordPress Preauth XSS to RCE Chain (CVE-2026-64638)