
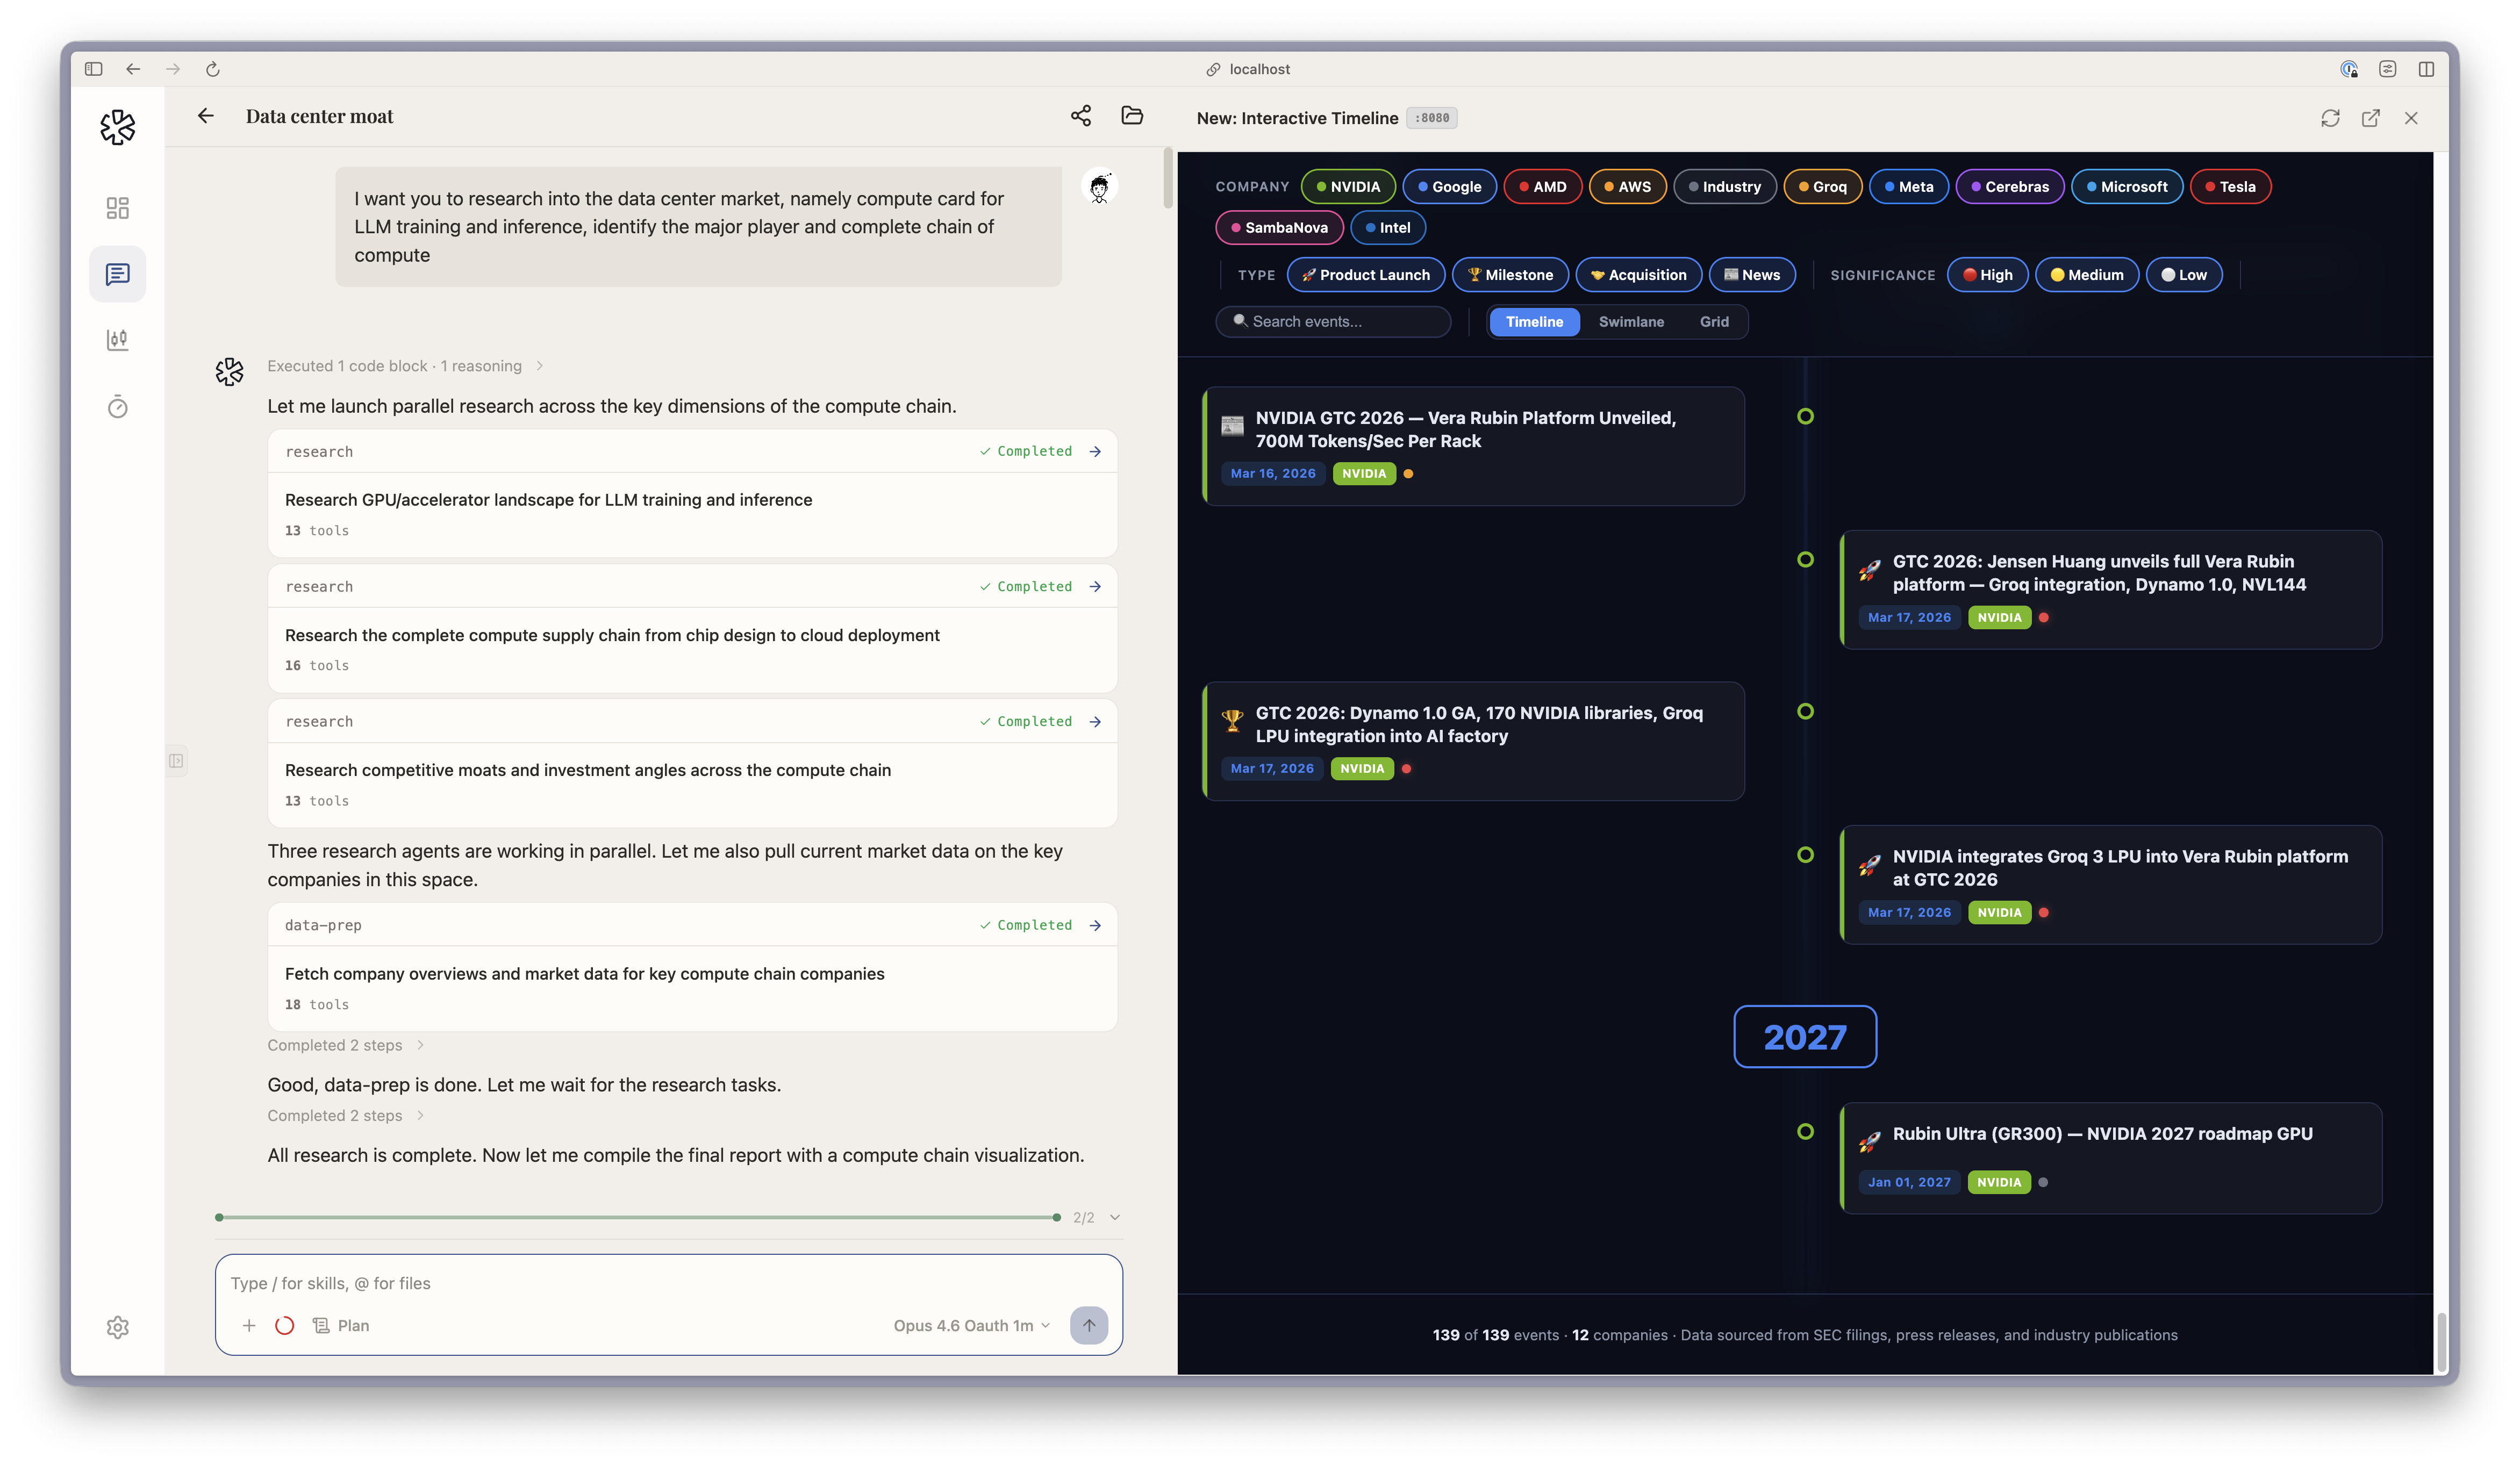
LangAlpha
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
crawlerdata-exfiltrationinformation-gathering+6
1.8k
ginlix-ai/langalphaAutomated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 symfony/symfony
The Symfony PHP framework
 globaleaks/globaleaks-whistleblowing-software
GlobaLeaks is a free and open-source whistleblowing software enabling anyone to easily set up and maintain a secure reporting platform.
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 zarcolio/sitedorks
Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
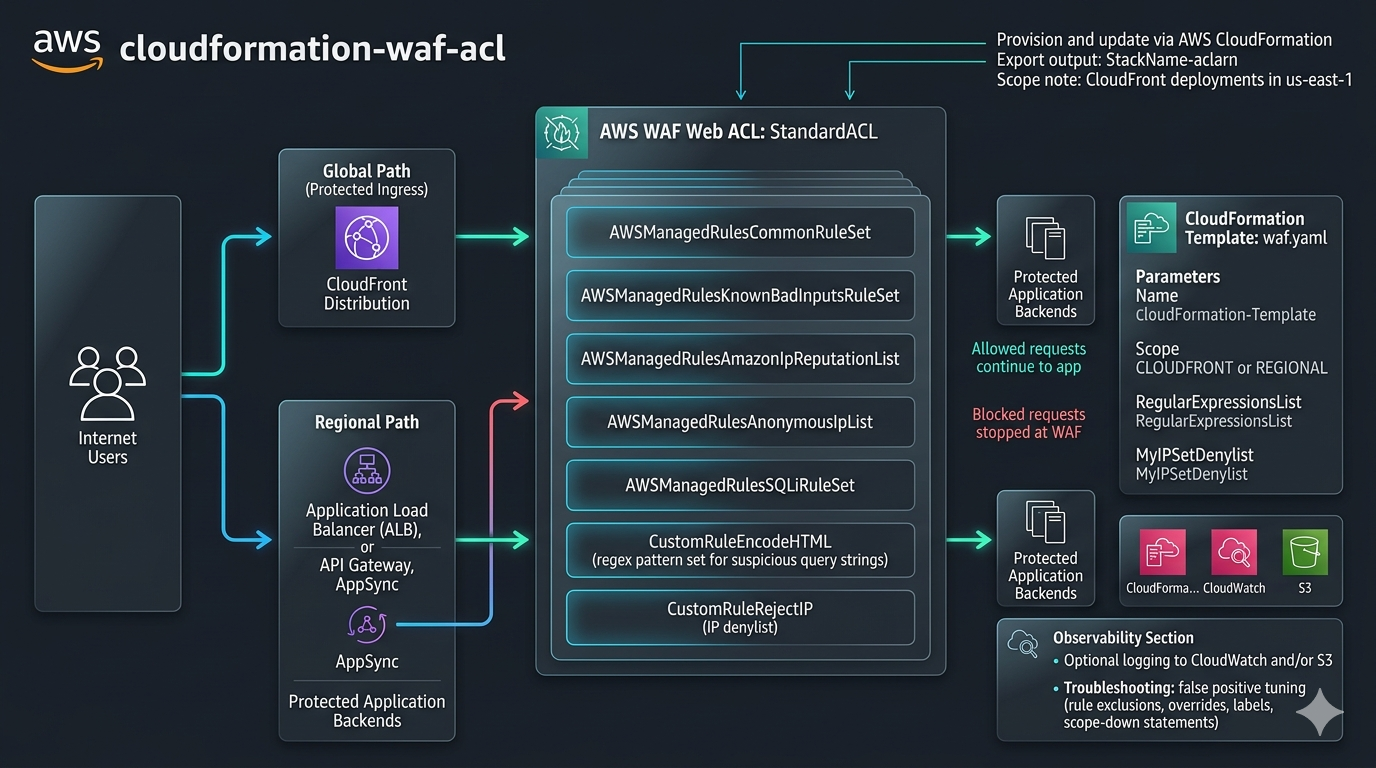 fer1035_aws/cloudformation/cloudformation-waf-acl
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…
 imsre9/cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a heap buffer overflow in NGINX rewrite/set directives, enabling DoS and potential RCE via crafted…
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…
 yuhuamiao/cve-2026-36358
Proof-of-concept demonstrating a stored XSS vulnerability in Juzaweb CMS v5.0.0 via the banner ads HTML field, leading to arbitrary script execution…
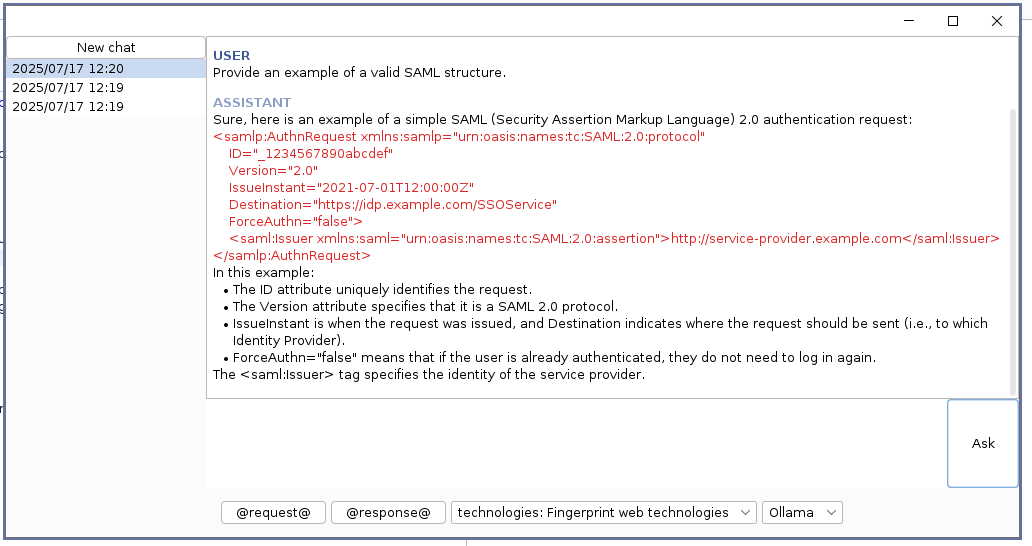 synacktiv/hopla
HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday