
CVE-2026-87796
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
educationexploitationlabs-practice+6
abraxas/cve-2026-87796Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 mbeweoo/flash-exploit-defense-system
Comprehensive multi-layer defense system against Adobe Flash CVE exploits (CVE-2012-0754, CVE-2015-xxxx, CVE-2016-xxxx, CVE-2018-xxxx) with browser,…
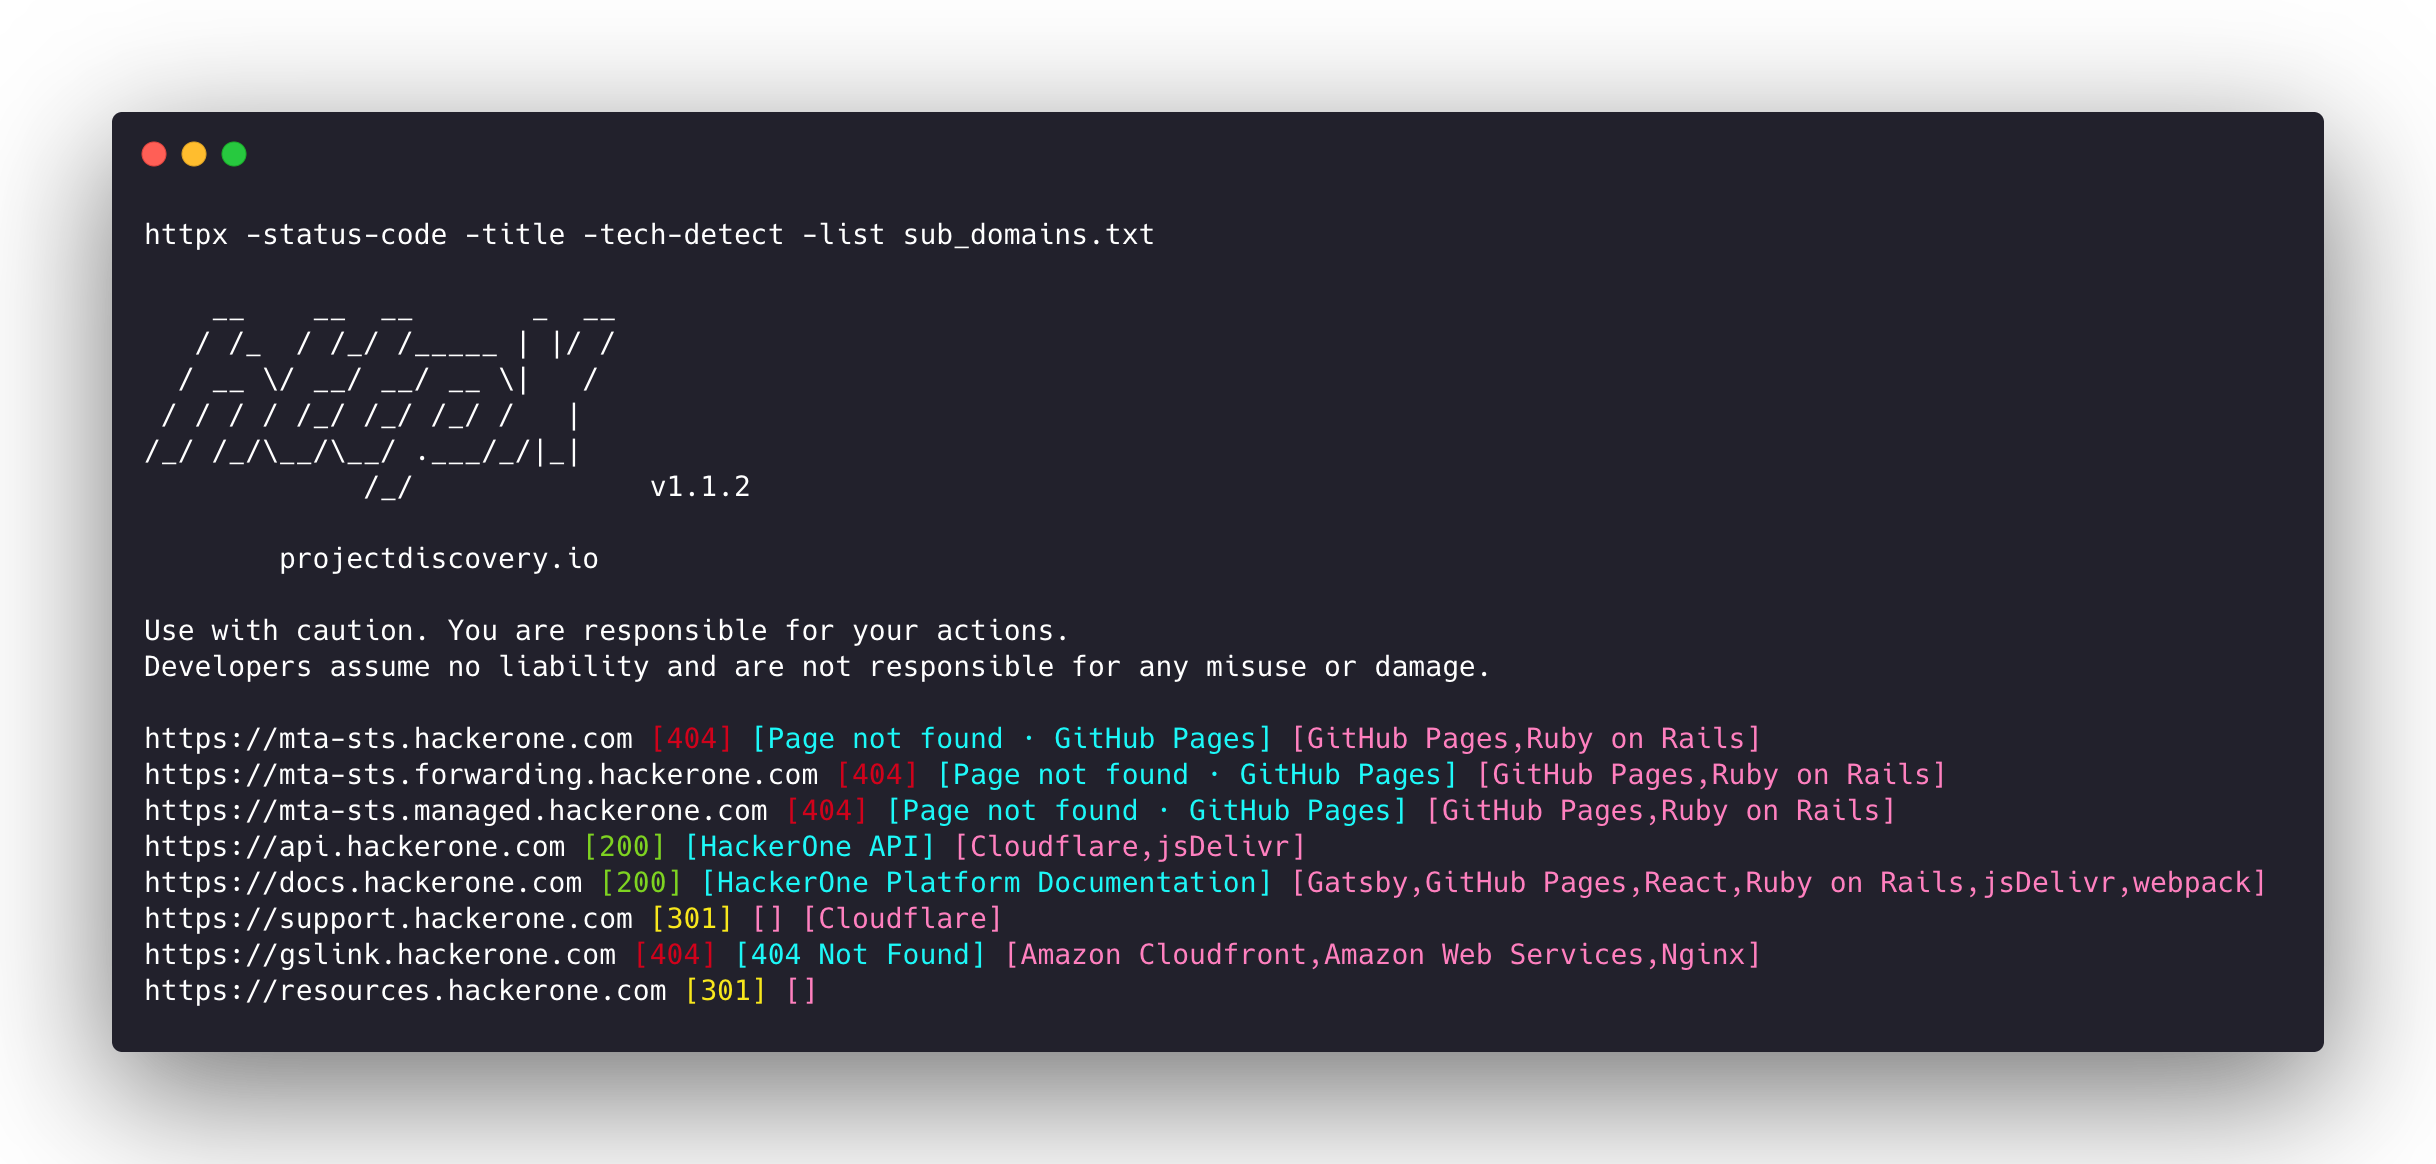 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 runanywhereai/on-device-browser-agent
On-device AI browser automation using WebLLM. No cloud, no API keys, fully private.
 spidersuite/spidersuite
Advanced cross-platform web crawler for security professionals, enabling automated reconnaissance, information gathering, and OSINT data collection…
 k3ystr0k3r/cpanelscanner
cPanel Scanner is a fast, multi-threaded tool written in Go for detecting cPanel services across IP ranges, CIDR blocks, or target lists. Perfect for…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 k3ystr0k3r/intrack
A flexible internet crawler used for scanning technologies, instances and vulnerabilities worldwide across the internet.
 blue0x1/xpath
xpath is a fast, multi-technique XPath injection scanner written in Nim. It focuses on practical detection, response comparison, visible extraction,…
 joelindra/cve-2017-9841
Tool designed to scan a list of websites for a known vulnerability in the PHPUnit framework, specifically the CVE-2017-9841 vulnerability.
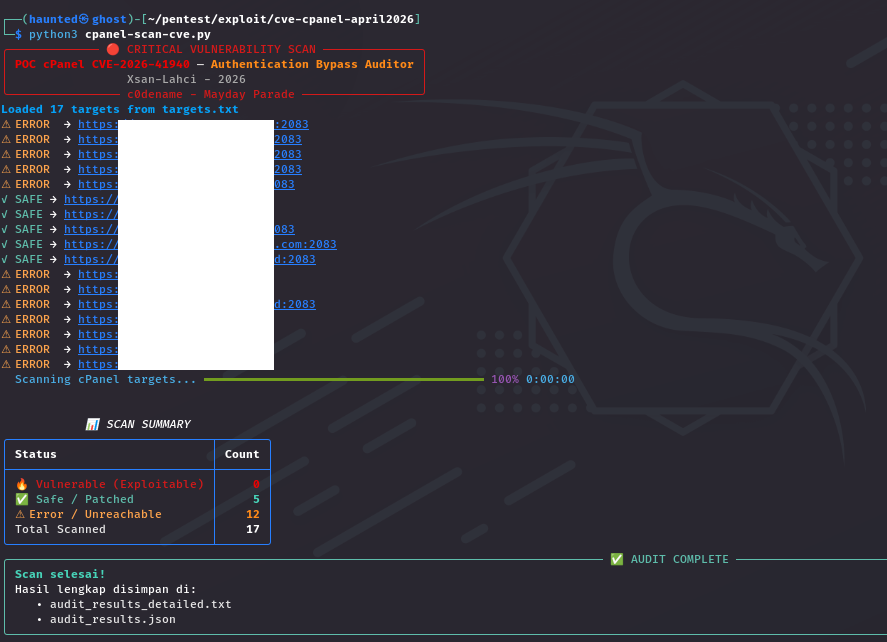 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 ef3tr/cve-2026-4106
WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.