
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
web-check preview

web-check

GitHublissy93/web-check

🕵️‍♂️ All-in-one OSINT tool for analysing any website
dns-analysisemail-harvestinginformation-gathering+10
35.1k3 days ago
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
1174 days ago
CVE-2026-104110 preview

CVE-2026-104110

GitHubpervinzahidli/cve-2026-104110

Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
api-securityauthenticationexploitation+5
7 days ago
CVE-2026-87902-A-working-PoC-for-WordPress-s-critical-path-traversal preview

CVE-2026-87902-A-working-PoC-for-WordPress-s-critical-path-traversal

GitHubrabakuku/cve-2026-87902-a-working-poc-for-wordpress-s-critical-path-traversal

Reference notes and mitigation configs for CVE-2026-87902, a WordPress Core unauthenticated path traversal and LFI flaw chainable to RCE, with Nginx,…
defensive-toolseducationpapers-research+3
16 days ago
CVE-2026-91097-CVE-2026-91106 preview

CVE-2026-91097-CVE-2026-91106

GitHubnxploited/cve-2026-91097-cve-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
defensive-toolsexploitationinformation-gathering+7
117 days ago
spip-exploits preview

spip-exploits

GitHubambionics/spip-exploits

Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
exploitationexploit-frameworkspapers-research+4
222 days ago
CVE-2026-59550 preview

CVE-2026-59550

GitHubflx-0x00/cve-2026-59550

Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
educationexploitationlabs-practice+5
23 days ago
CVE-2026-21858-n8n-FullChain preview

CVE-2026-21858-n8n-FullChain

GitHubzerodayevil/cve-2026-21858-n8n-fullchain

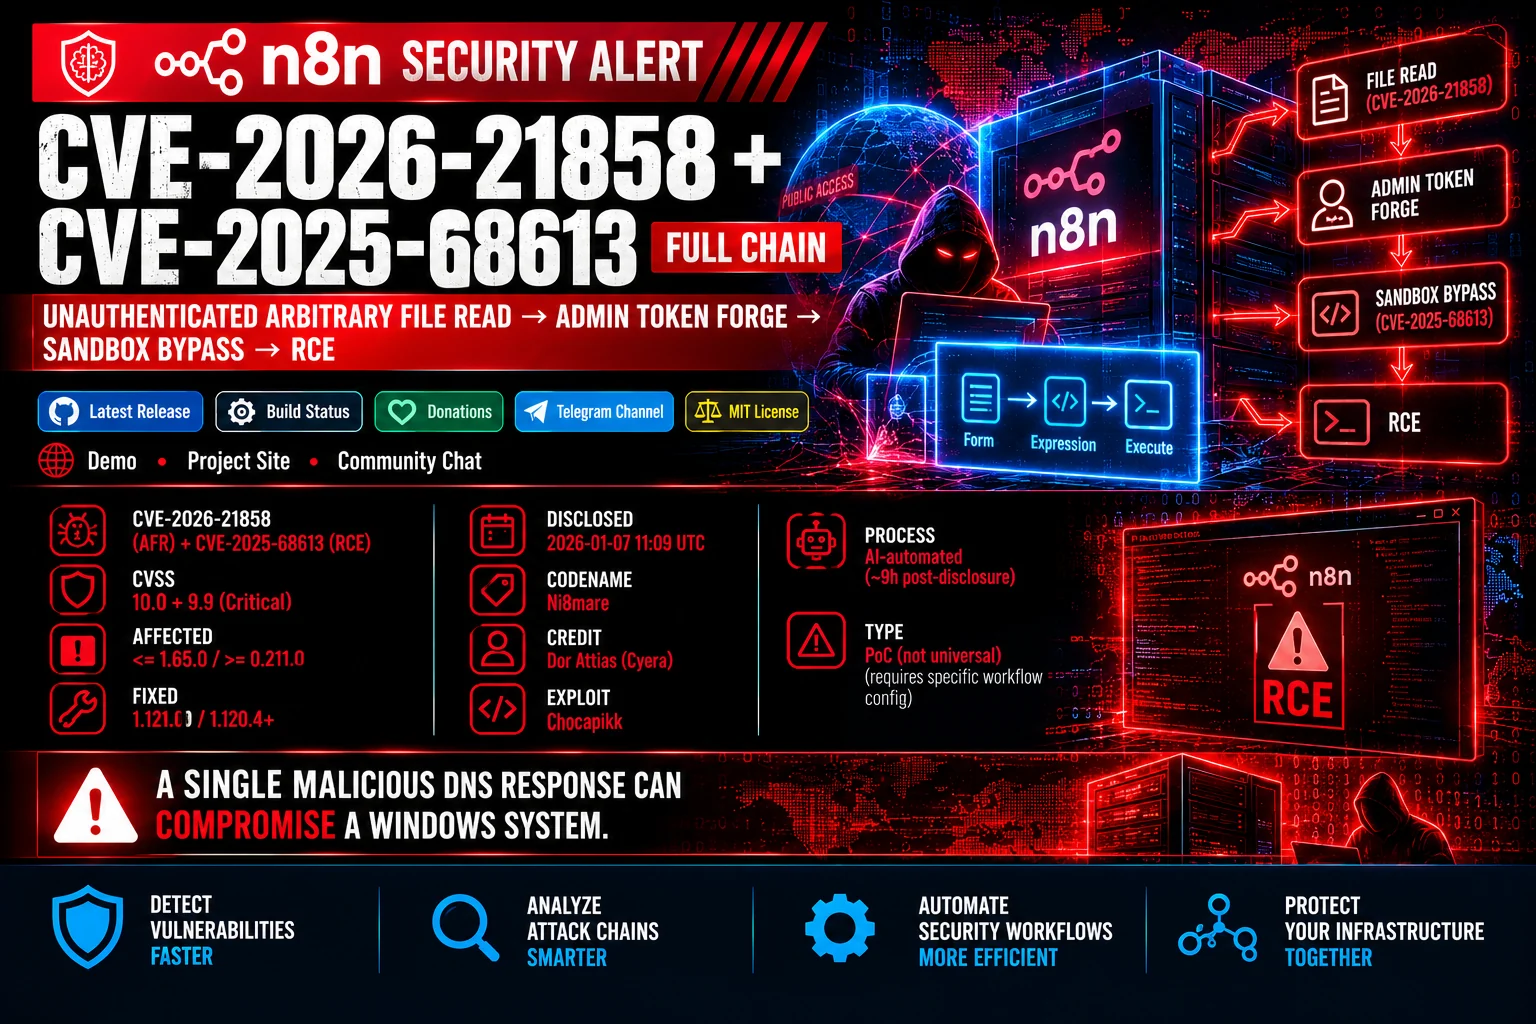
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
ai-securityexploitationpayload-development+7
8827 days ago
GitHacker preview

GitHacker

GitHubwangyihang/githacker

🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
information-gatheringpenetration-testingreconnaissance+2
1.7k1 month ago
log4shell-exploitation-lab preview

log4shell-exploitation-lab

GitHubwafeeq-fareed/log4shell-exploitation-lab

CVE-2021-44228 Log4Shell reproduced end to end: exploitation through remediation
educationexploitationlabs-practice+3
1 month ago
Bug-Bounty-Arsenal-v.3 preview

Bug-Bounty-Arsenal-v.3

GitHubfoxvr-sudo/bug-bounty-arsenal-v.3

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
api-security-testingcrawlerdevsecops+8
131 month ago
pentx-vapt-skill preview

pentx-vapt-skill

GitHubyashas-13/pentx-vapt-skill

Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
exploitationinformation-gatheringpenetration-testing+6
21 month ago
CVE-2026-2796-and-CVE-2026-2768-escape-the-wasm-box preview

CVE-2026-2796-and-CVE-2026-2768-escape-the-wasm-box

GitHubsneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box

Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
binary-exploitationexploitationvulnerability-analysis+1
11 month ago
cve-2026-63030-lab preview

cve-2026-63030-lab

GitHubmhassani97/cve-2026-63030-lab

wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
educationexploitationlabs-practice+3
1 month ago
POC-CVE-2026-63030-CVE-2026-60137- preview

POC-CVE-2026-63030-CVE-2026-60137-

GitHubtrandonga3/poc-cve-2026-63030-cve-2026-60137-

Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
api-securityeducationexploitation+6
1 month ago
CVE-2026-73847-emlog-PoC preview

CVE-2026-73847-emlog-PoC

GitHubsqueeze440/cve-2026-73847-emlog-poc

PoC for CVE-2026-73847 - emlog AI Assistant CSRF to SQL execution to admin takeover (CVSS 6.8)
exploitationpenetration-testingvulnerability-analysis+2
1 month ago
nikto preview

nikto

GitHubsullo/nikto

Nikto web server scanner

crawlerdynamic-code-analysisinformation-gathering+6
10.8k1 month ago
frogy2.0 preview

frogy2.0

GitHubiamthefrogy/frogy2.0

Orbis is an full spectrum automated external attack surface intelligent toolkit.

cloud-securitydns-analysisemail-security+9
4131 month ago
Previous12345Next