

CVE-2026-65660-Poc
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
1
shadowforge-cyber/cve-2026-65660-pocMalicious Register Directive Code Injection Exploit
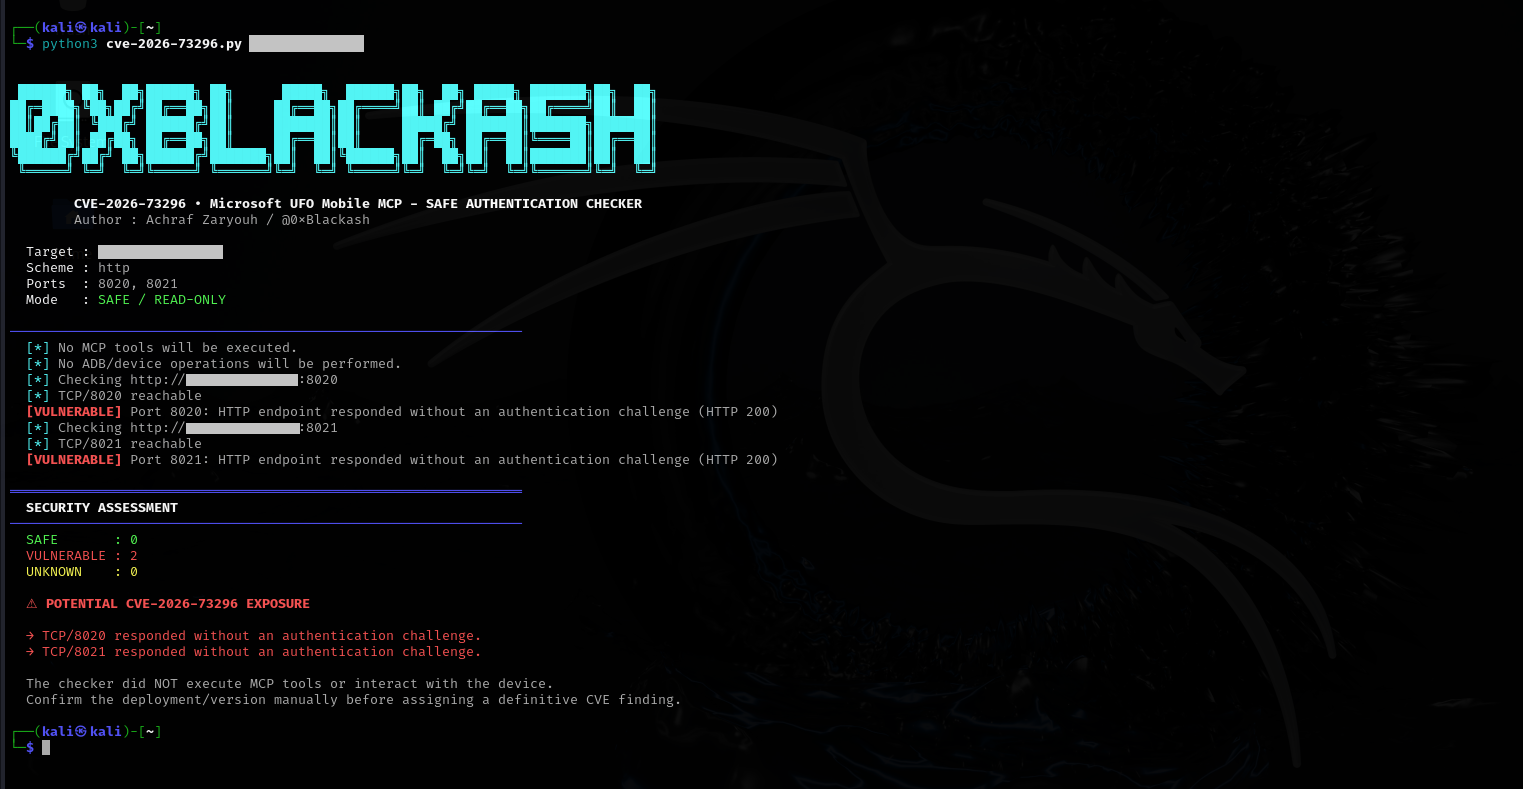 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
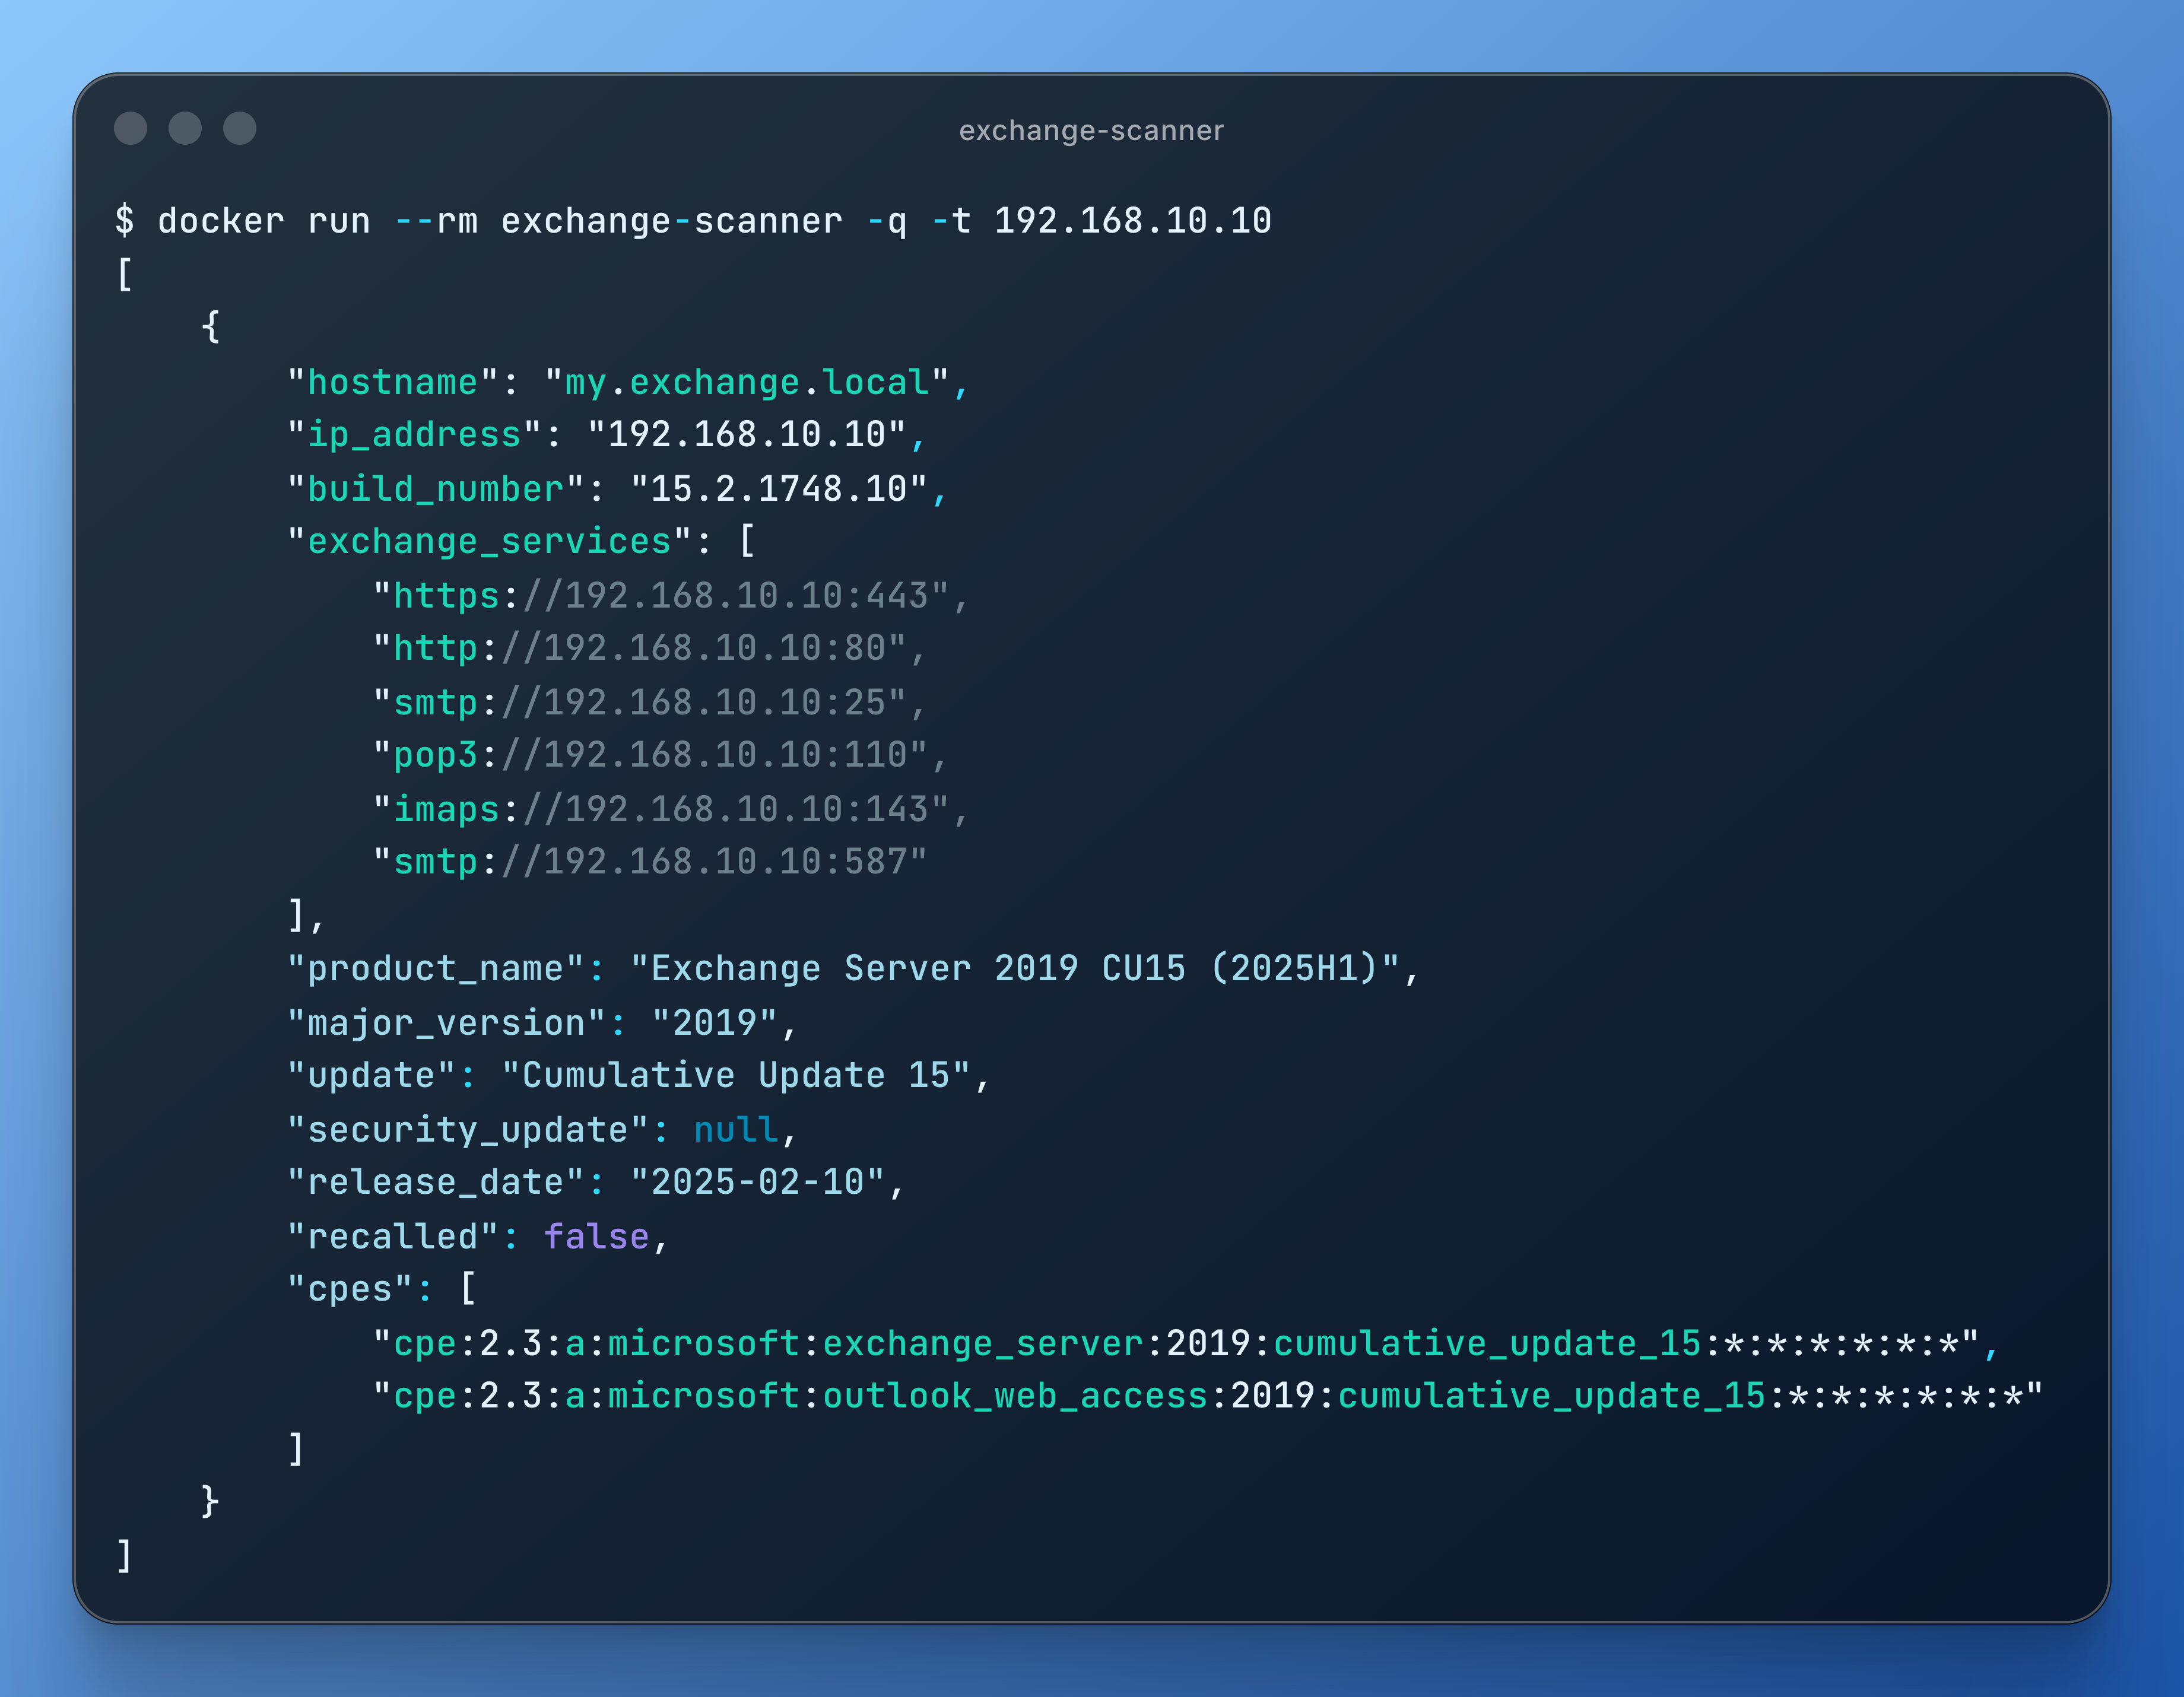 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…
 rxerium/ai-bot-ip-ranges
Official IP ranges for AI bot crawlers (OpenAI, Anthropic, Google, Microsoft, Perplexity). Weekly auto-updates.
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 p0dalirius/rdwatool
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
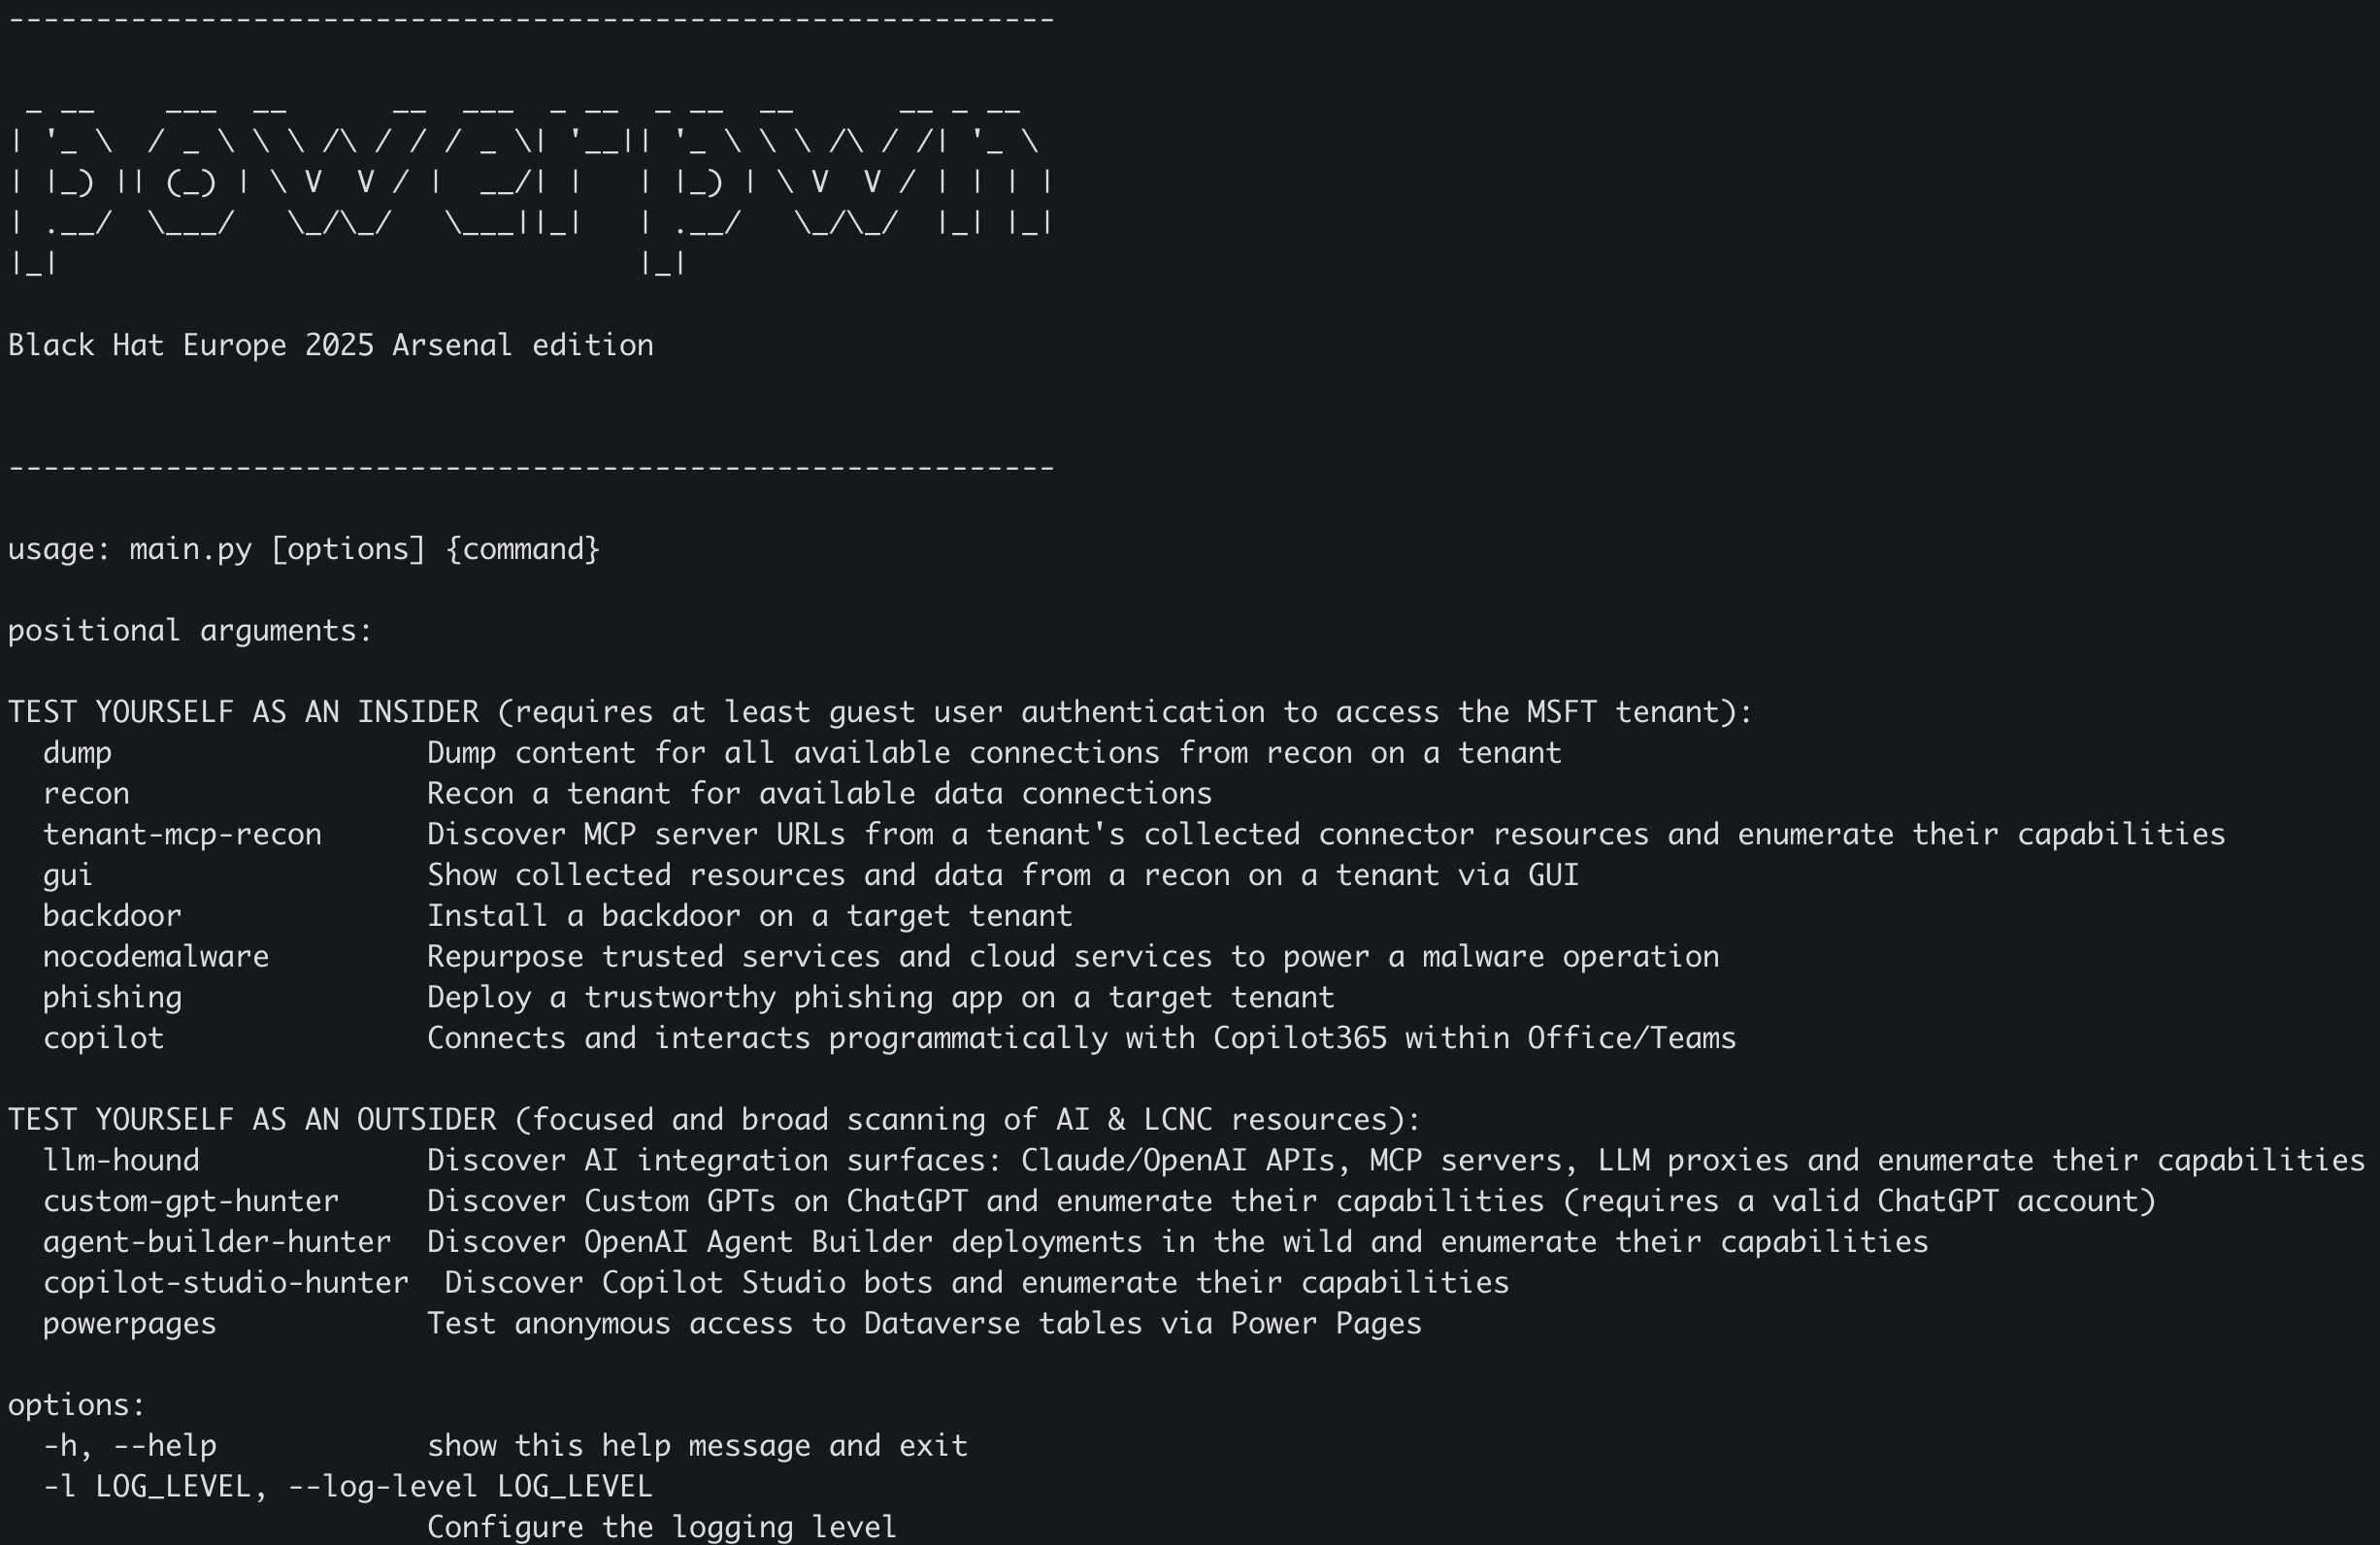 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 cameloo1/sharepoint-toolshell-micro-postmortem
Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
 cappricio-securities/cve-2000-0114
Microsoft FrontPage Extensions Check (shtml.dll)
 cappricio-securities/cve-2015-1635
Microsoft Windows 'HTTP.sys' - Remote Code Execution
 w01fh4cker/cve-2024-30043-xxe
Exploiting XXE Vulnerabilities on Microsoft SharePoint Server and Cloud via Confused URL Parsing
 kljunowsky/cve-2022-41040-poc
CVE-2022-41040 - Server Side Request Forgery (SSRF) in Microsoft Exchange Server
 ipsbruno/cve-2021-34473-nmap-scanner
A massive scanner for CVE-2021-34473 Microsoft Exchange Windows Vulnerability