
CVE-2026-104286-POC
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…

Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…

LA-Studio Element Kit for Elementor <= 1.5.6.3 - Unauthenticated Privilege Escalation via Backdoor to Administrative User Creation via lakit_bkrole…

Escaner de identificacion de vulnerabilidades para CVE-2025-4322

PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…

Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.

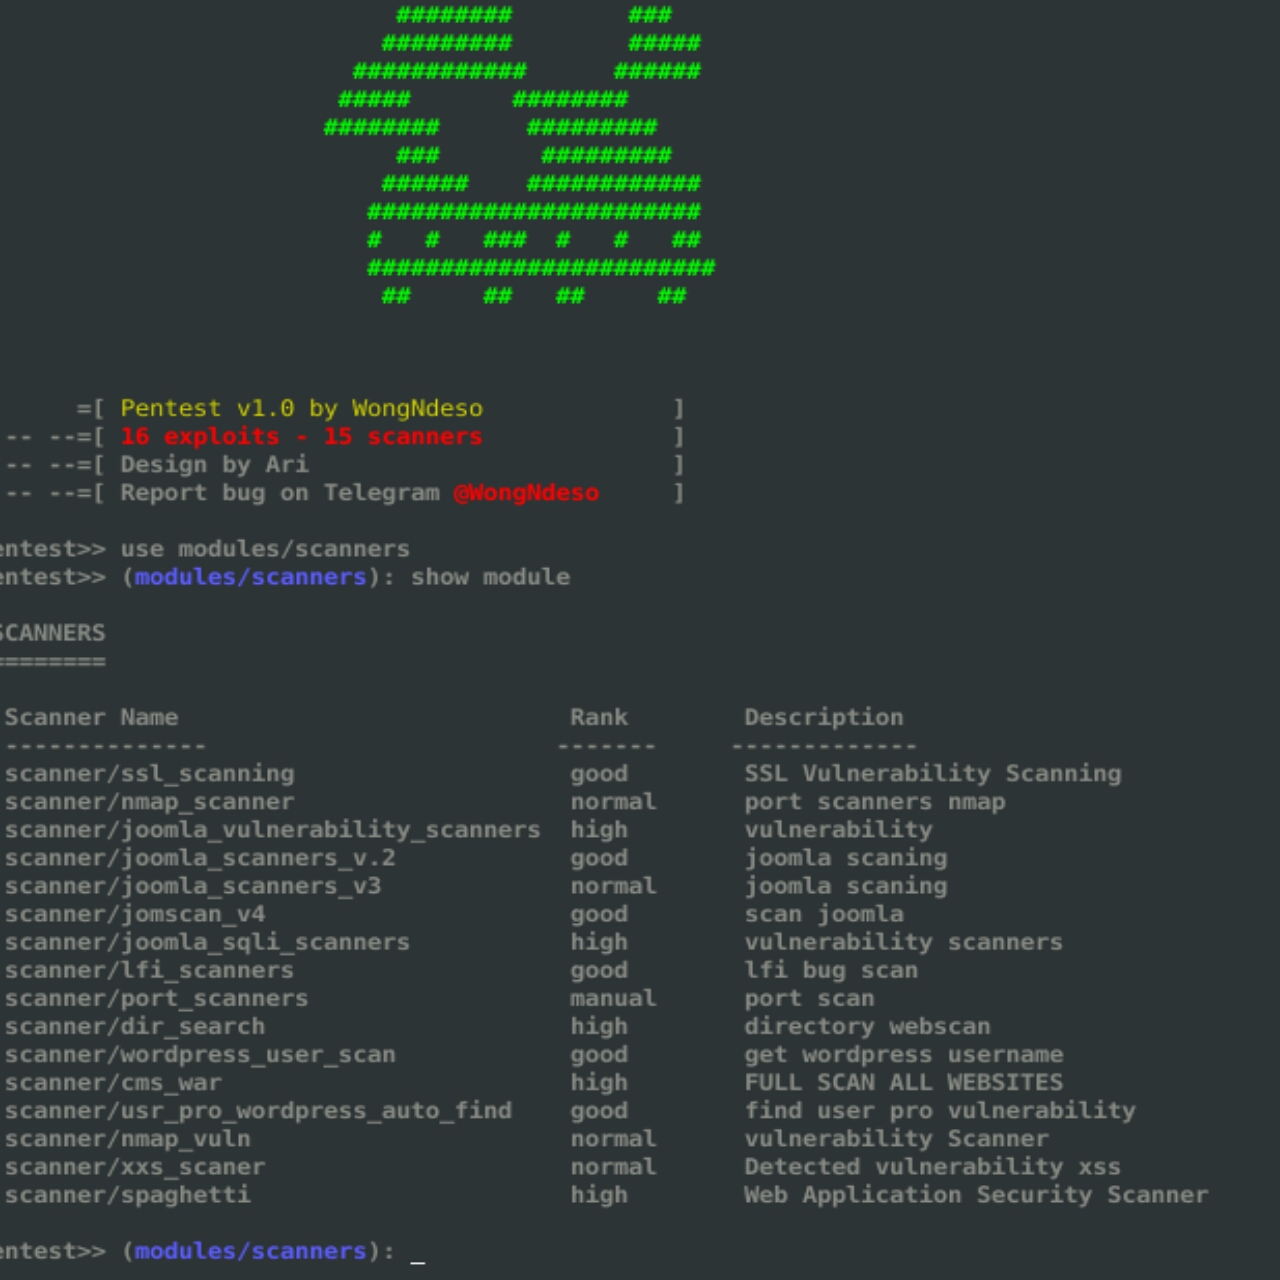
Pentest Tools Framework is a database of exploits, Scanners and tools for penetration testing. Pentest is a powerful framework includes a lot of…

This is POC for CVE-2024-2667 (InstaWP Connect – 1-click WP Staging & Migration <= 0.1.0.22 - Unauthenticated Arbitrary File Upload)

Proof-of-concept for a reflected XSS vulnerability in CheckMK Management Web Console (versions 1.5.0 to 1.6.0), enabling session theft or backdoor…


A native backdoor module for Microsoft IIS (Internet Information Services)

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…


Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…

Web application backdoor builder

Web Backdoor Cookie Script-Kit