
redknife
 yukibtc/redknife
A Swiss Army knife for offensive security.
command-and-controlinformation-gatheringpenetration-testing+4
yukibtc/redknifeA Swiss Army knife for offensive security.

 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 yym8538/cve-2026-49975
Proof-of-concept HTTP/2 Bomb exploit for CVE-2026-49975, a cookie-header memory exhaustion DoS in Apache HTTP Server 2.4.17-2.4.67, with Docker lab…
 dotnetguard/cve-2025-55182-exploit
CVE-2025-55182 — Next.js Flight Deserialization RCE exploit with interactive shell, single-command execution and multi-payload reverse shell chain.…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 rasta-mouse/pwnlift
Easy peasy file uploads
 ycseo-git/cve-2020-11800
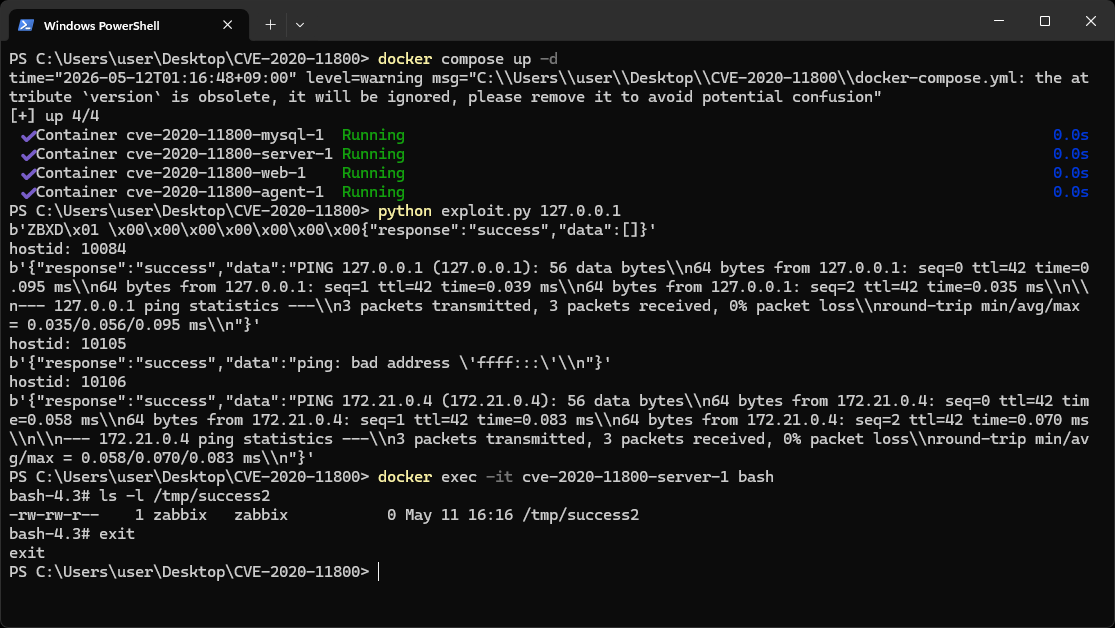
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 panchocosil/verify-ghsa-c4j6-fc7j-m34r
OOB verifier for GHSA-c4j6-fc7j-m34r / CVE-2026-44578 (Next.js WebSocket-upgrade SSRF)
 skoveit/cve-2026-34227
Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
 mathitam/thingsboard-ssrf-cve-2025-34282
PoC exploit for CVE-2025-34282 - ThingsBoard SSRF via SVG Image Upload
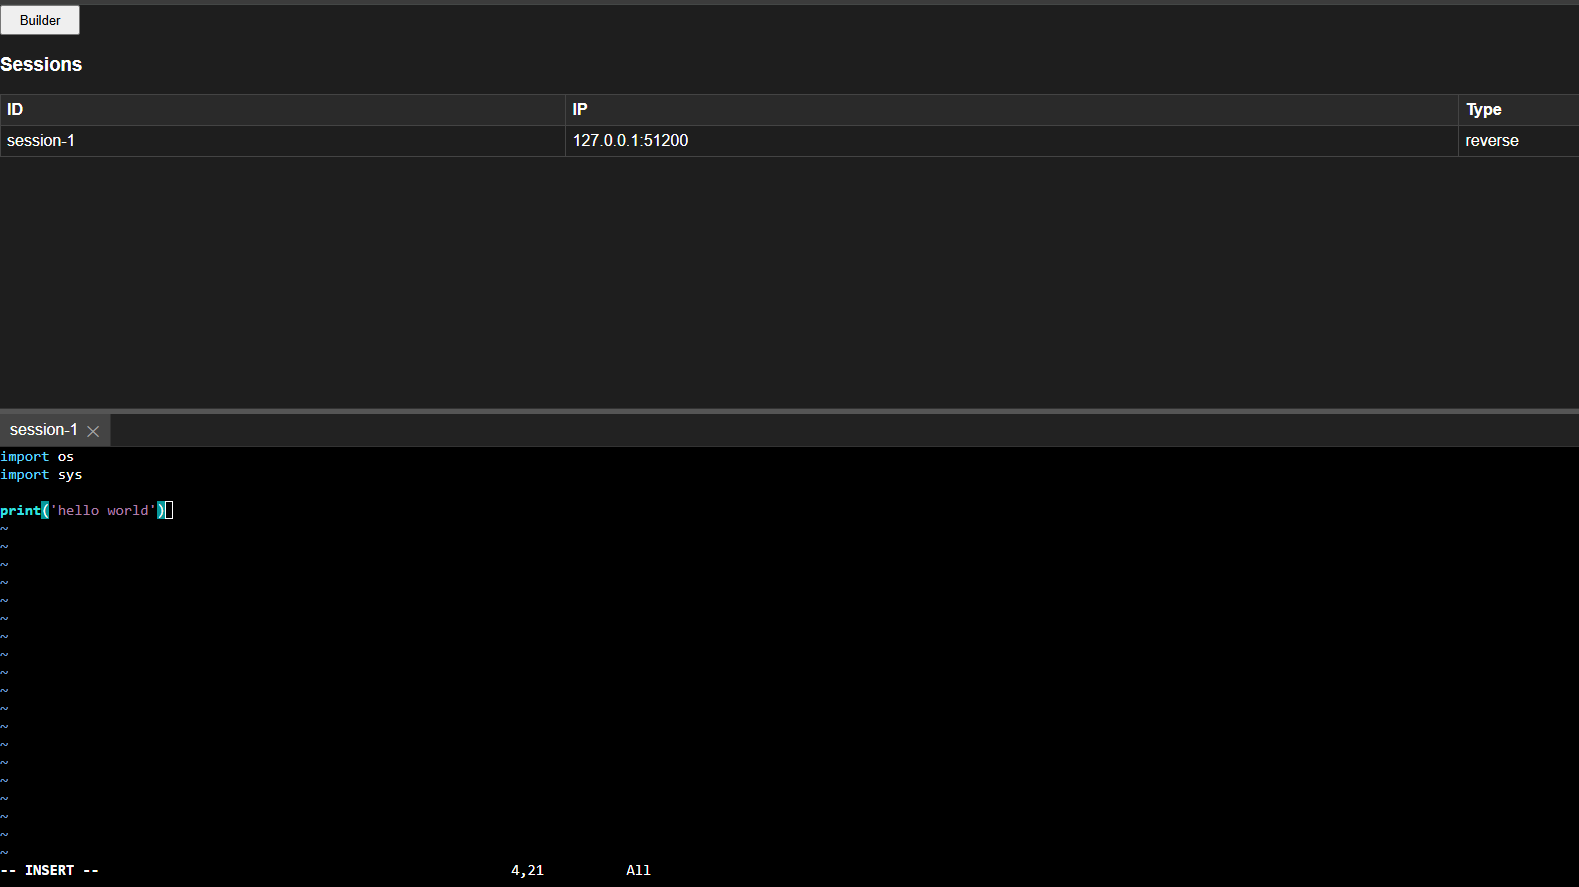 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
 zemarkhos/cve-2025-55182-exploit-poc-scanner
Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection