

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
zentinel preview

zentinel

GitHubzentinelproxy/zentinel

A security-first reverse proxy built to guard the free web.
ai-securityapi-securityauthentication-authorization+6
12022h 15m ago
CVE-2026-77771 preview

CVE-2026-77771

GitHubpervinzahidli/cve-2026-77771

Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
authenticationdefensive-toolseducation+2
1 month ago
internal-security-detect preview

internal-security-detect

GitHubrxerium/internal-security-detect

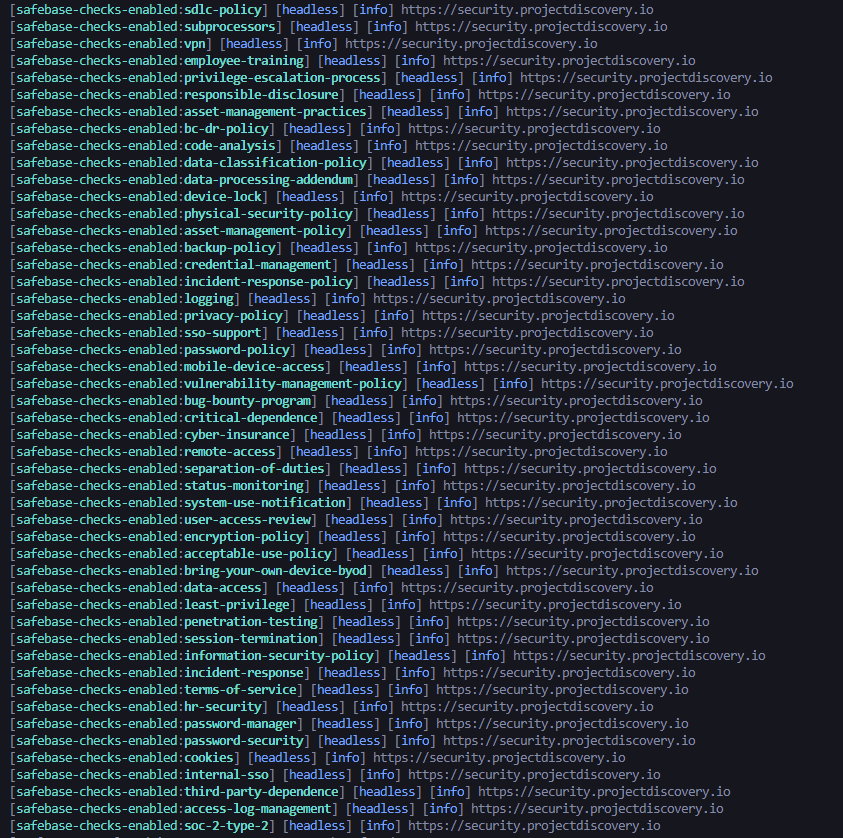
The detection of internal security controls at a company
configuration-auditingdefensive-toolsinformation-gathering+5
29 months ago
Nagios-Log-Server-2.1.7-Persistent-Cross-Site-Scripting preview

Nagios-Log-Server-2.1.7-Persistent-Cross-Site-Scripting

GitHubemreovunc/nagios-log-server-2.1.7-persistent-cross-site-scripting

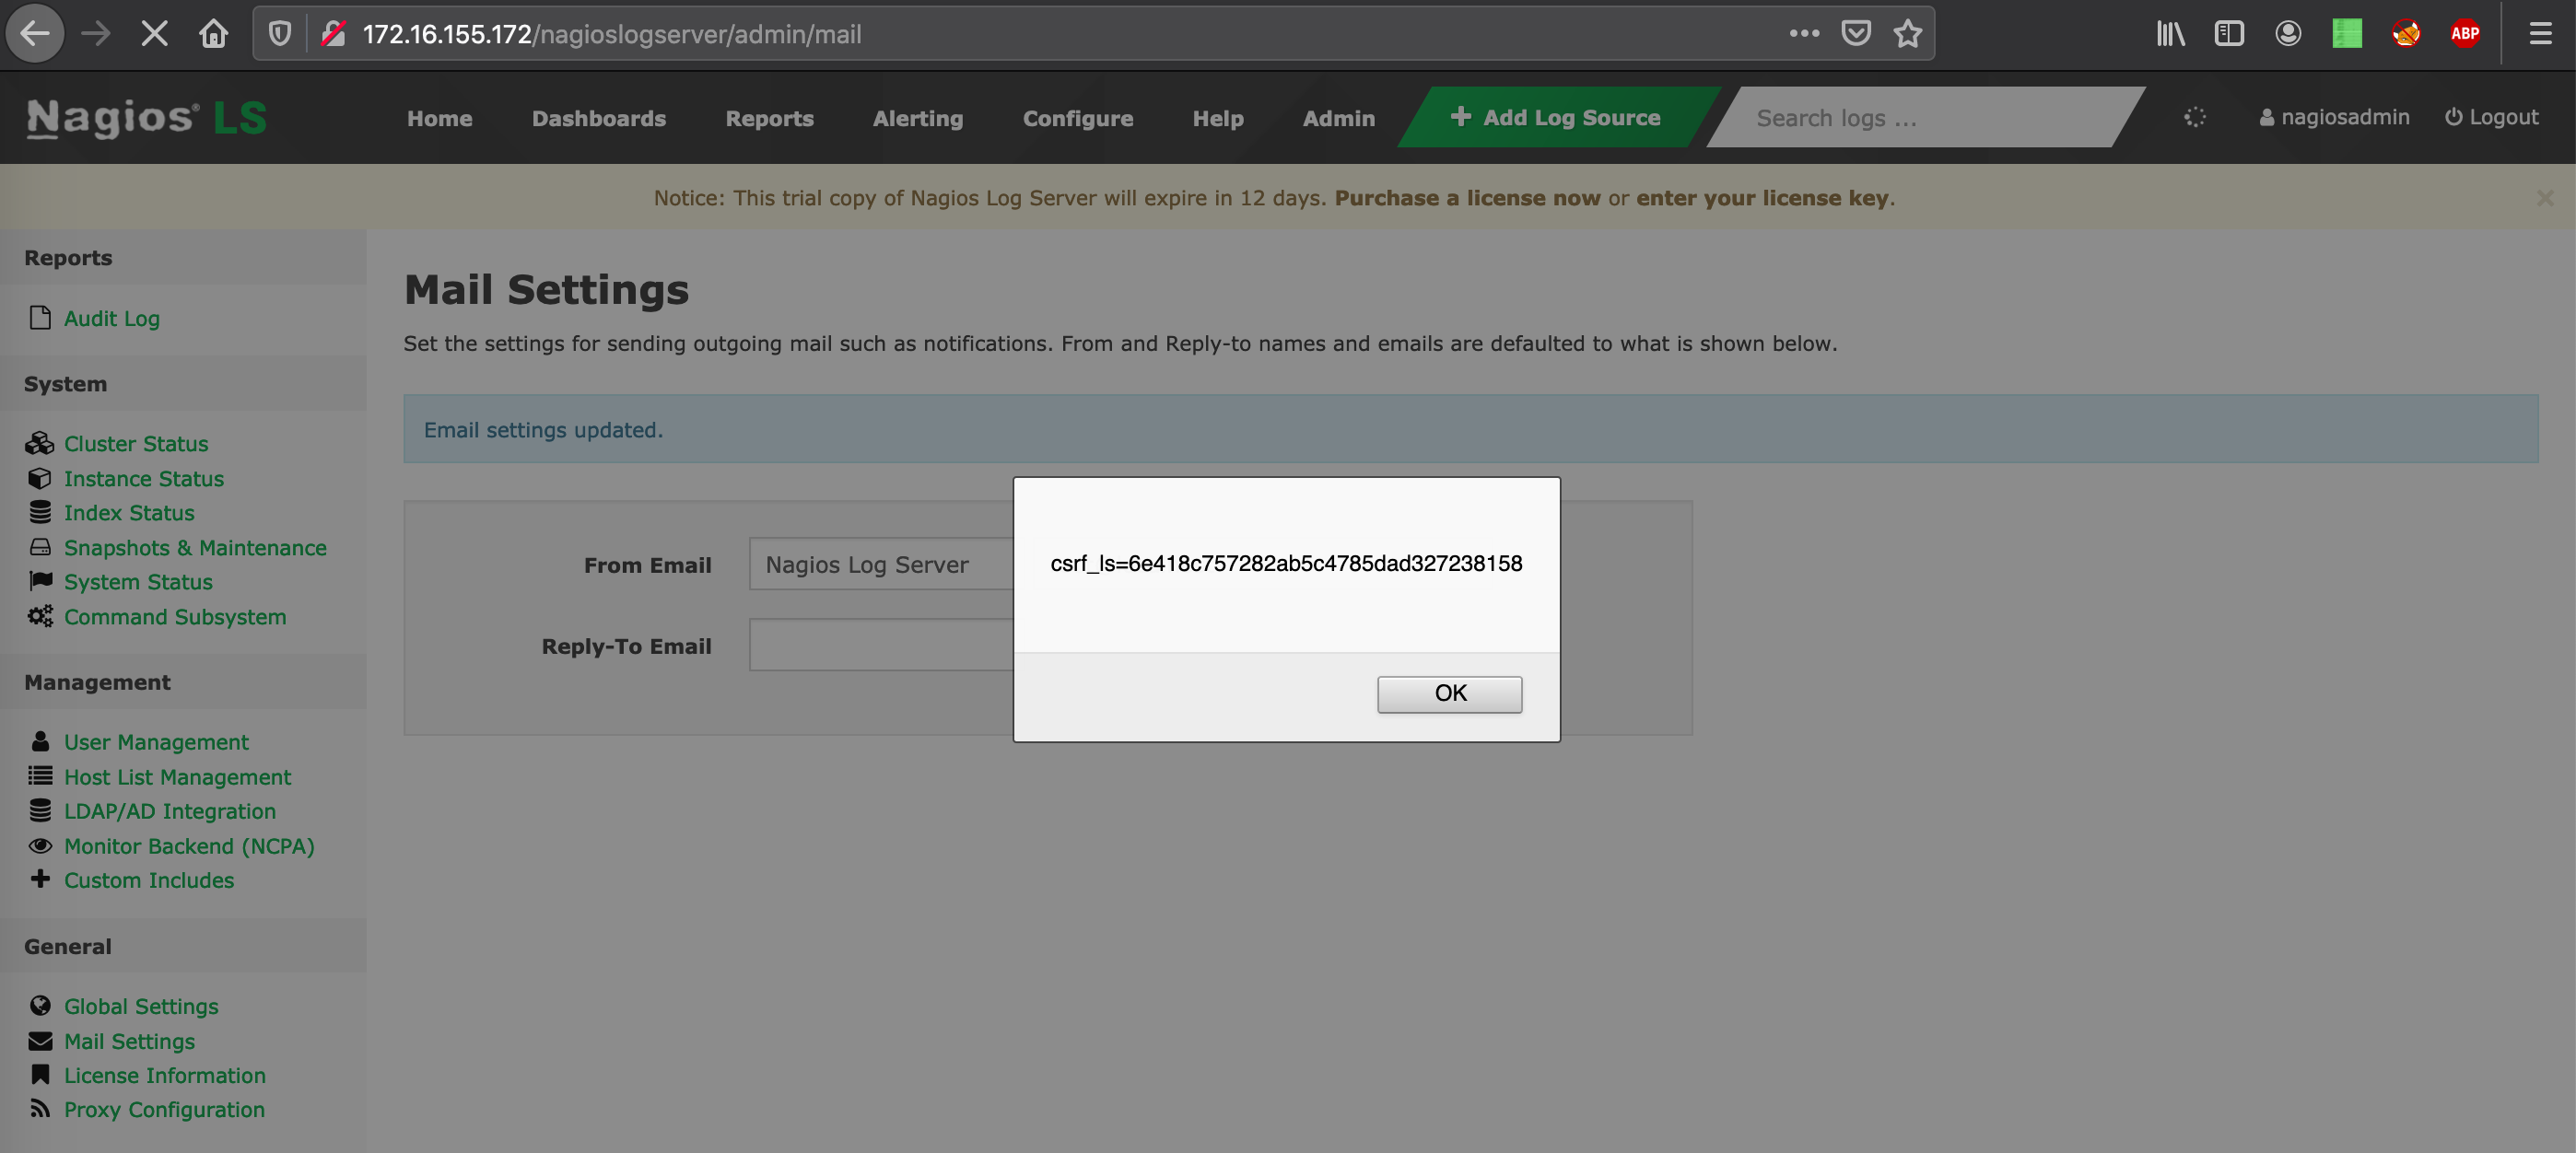
A stored cross-site scripting (XSS) in Nagios Log Server 2.1.7 can result in an attacker performing malicious actions to users who open a maliciously…
exploitationpenetration-testingvulnerability-analysis+2
35 years ago
vulnerability-in-Remix-React-Router-CVE-2025-31137- preview

vulnerability-in-Remix-React-Router-CVE-2025-31137-

GitHubpouriam23/vulnerability-in-remix-react-router-cve-2025-31137-

CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.
ctfeducationexploitation+3
11 year ago
CVE-2014-0160-Chrome-Plugin preview

CVE-2014-0160-Chrome-Plugin

GitHubmre-fog/cve-2014-0160-chrome-plugin

Deprecated Chrome plugin that checks websites for the Heartbleed vulnerability (CVE-2014-0160) via an API, with linked exploit code for educational…
curated-resourceseducationexploitation+2
3 years ago
CVE-2023-5561-PoC preview

CVE-2023-5561-PoC

GitHubpog007/cve-2023-5561-poc

WordPress does not properly restrict which user fields are searchable via the REST API, allowing unauthenticated attackers to discern the email…
exploitationinformation-gatheringreconnaissance+2
42 years ago
CVE-2021-23017-POC preview

CVE-2021-23017-POC

GitHubz3usx01/cve-2021-23017-poc

The issue only affects nginx if the "resolver" directive is used in the configuration file. Further, the attack is only possible if an attacker is…
dns-analysisexploitationmemory-forensics+2
11 year ago
React2Shell preview

React2Shell

GitHubmuhammaduwais/react2shell

A Firefox extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications.
educationinformation-gatheringpenetration-testing+2
28 months ago
CVE-2025-63420 preview

CVE-2025-63420

GitHubhossainshadat/cve-2025-63420

Proof-of-concept for CVE-2025-63420: stored HTML injection in CrushFTP Admin Panel Reports. Includes reproduction steps, CVSS scoring, and payload…
educationexploitationpenetration-testing+3
11 months ago
CVE-2024-4439 preview

CVE-2024-4439

GitHubd0rb/cve-2024-4439

Exploit code for CVE-2024-4439, an unauthenticated stored XSS vulnerability in WordPress Core up to 6.5.1, enabling arbitrary PHP command execution…
exploitationpenetration-testingvulnerability-analysis+2
122 years ago
CVE-2024-4323 preview

CVE-2024-4323

GitHubd0rb/cve-2024-4323

Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.
binary-exploitationcode-analysisexploitation+3
12 years ago
CVE-2023-49103 preview

CVE-2023-49103

GitHubd0rb/cve-2023-49103

Proof-of-concept exploit for CVE-2023-49103, an unauthenticated information disclosure vulnerability in ownCloud Graph API, leaking environment…
exploitationinformation-gatheringpenetration-testing+2
2 years ago
legion preview

legion

GitHubdeadends/legion

Legion is a Zero-Knowledge Authentication Fabric built for privacy
authenticationcryptographyhardware-security+3
1010 months ago
PoC-CVE-2025-29927 preview

PoC-CVE-2025-29927

GitHubb4sh0xf/poc-cve-2025-29927

→ poc for CVE-2025-29927
authentication-authorizationexploitationpenetration-testing+3
1 year ago
CVE-2014-0160-Chrome-Plugin preview

CVE-2014-0160-Chrome-Plugin

GitHubxyl2k/cve-2014-0160-chrome-plugin

Heartbleed
curated-resourceseducationexploitation+2
110 years ago
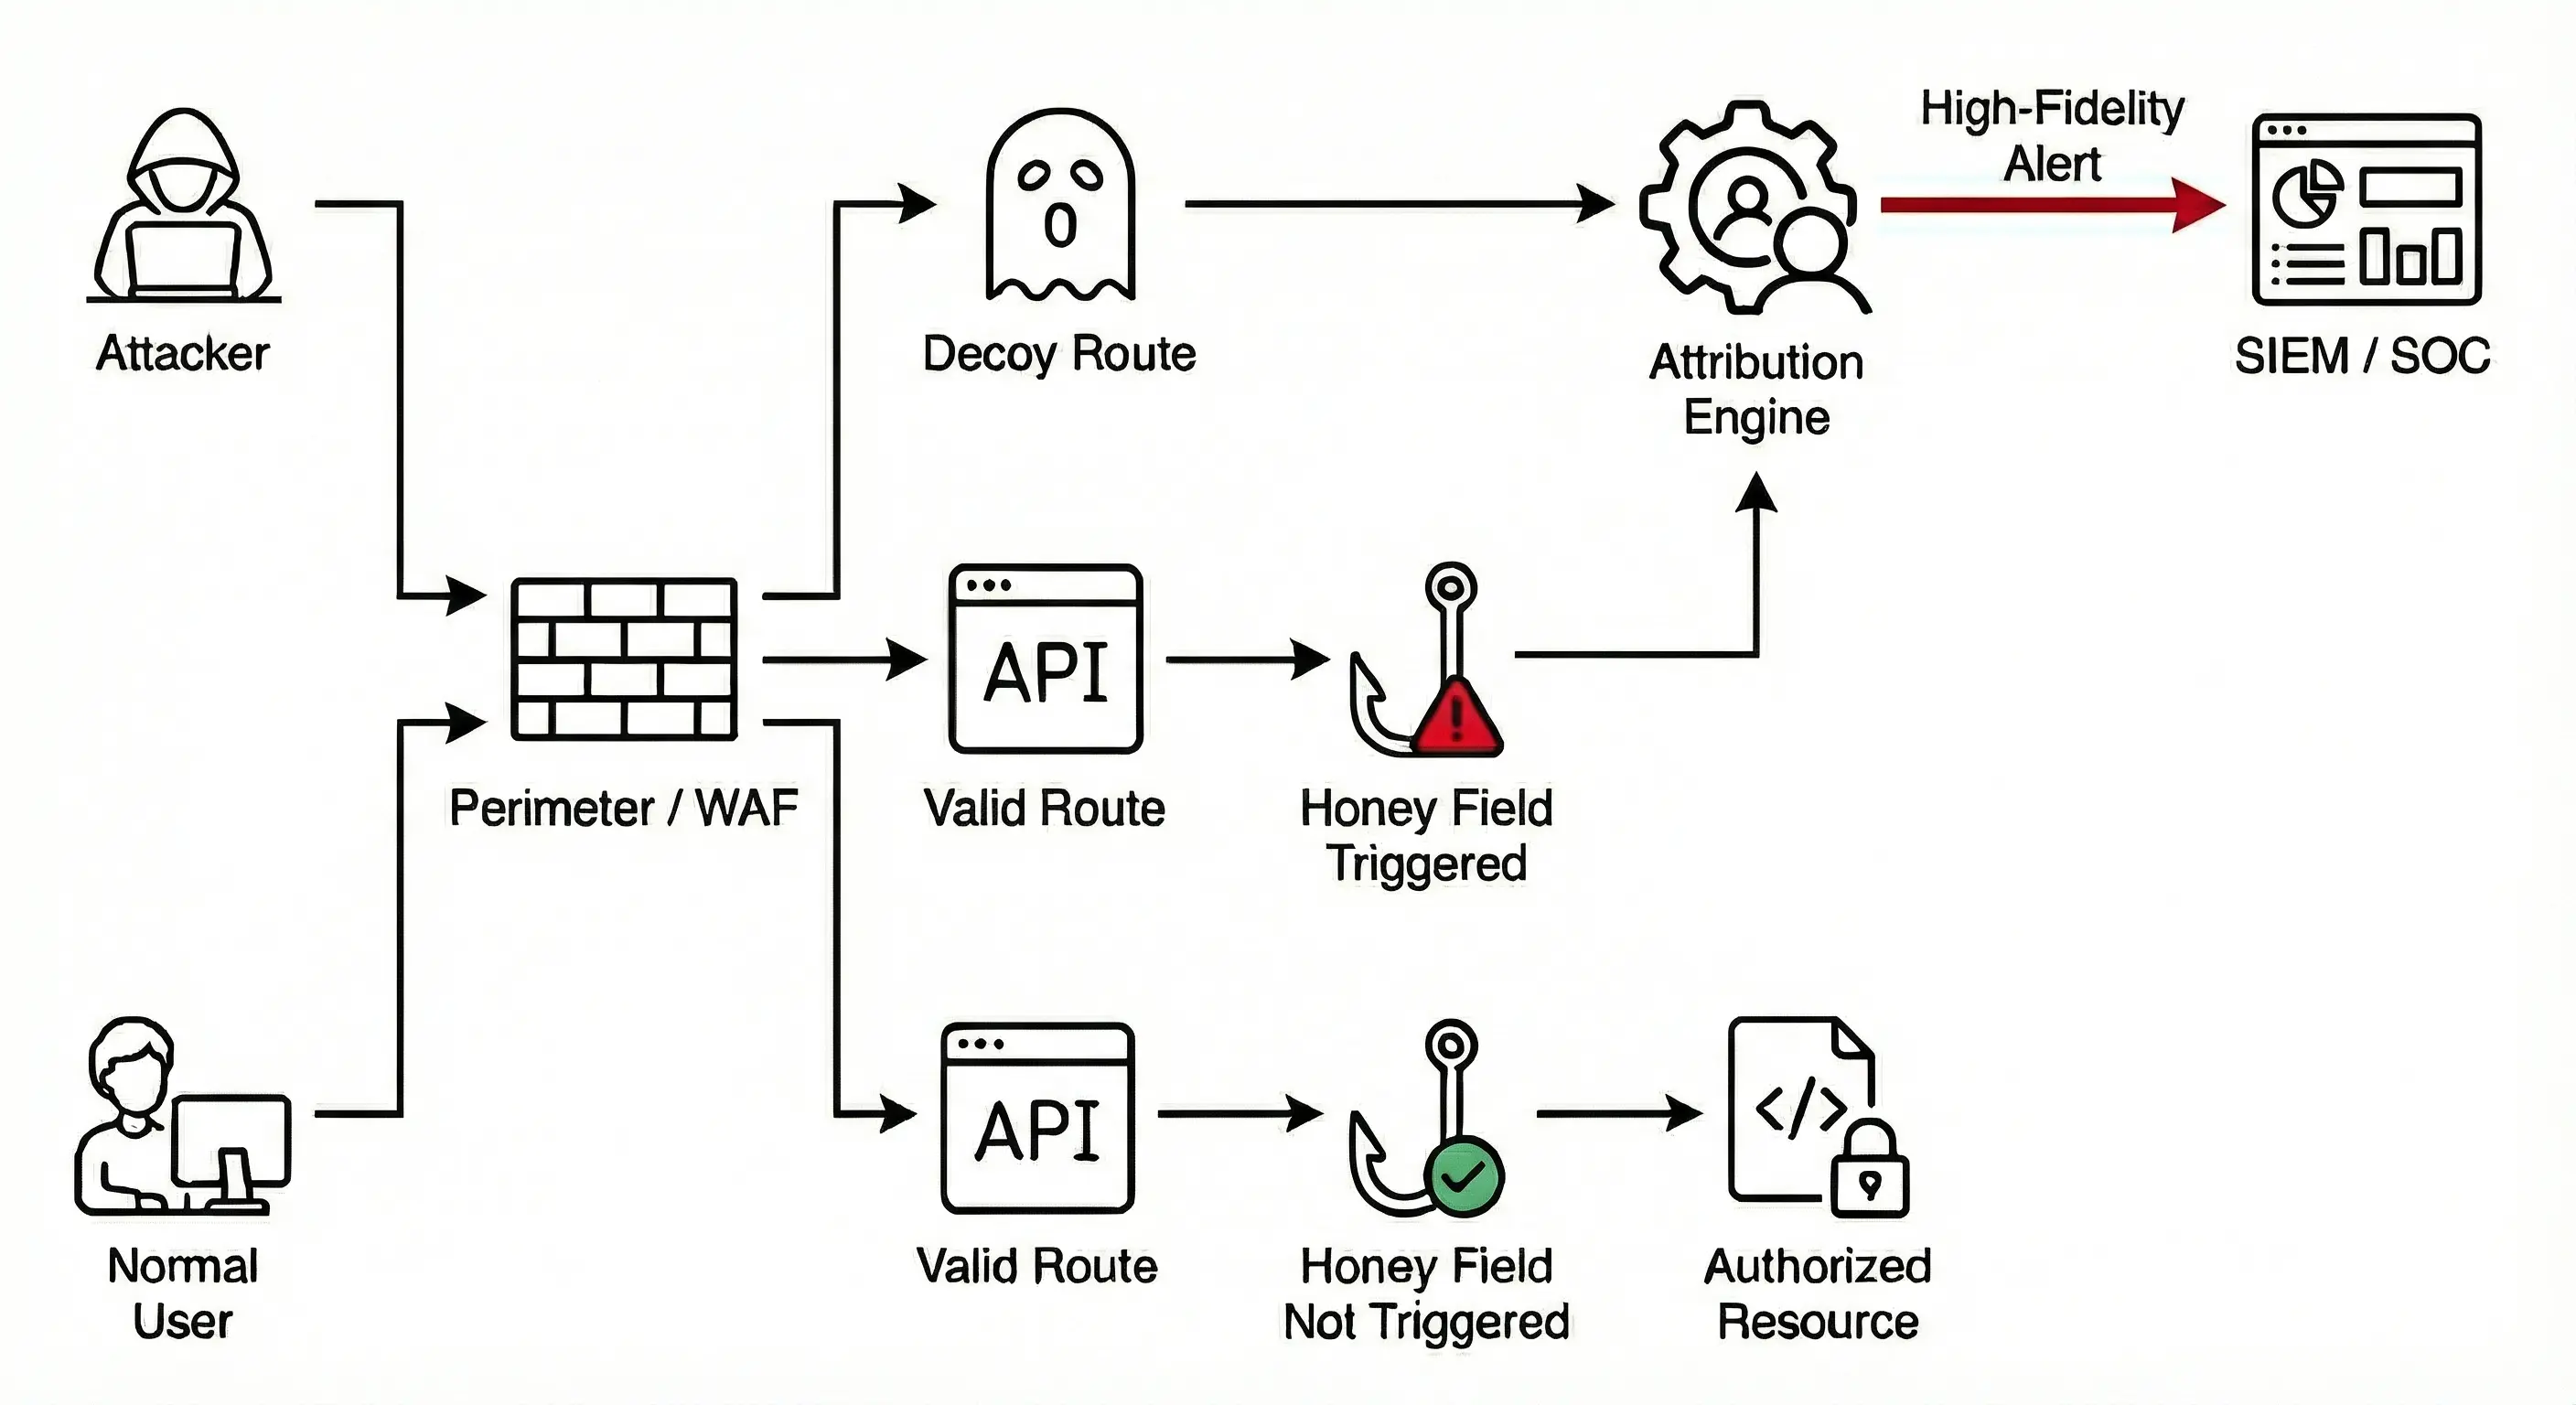
trappsec preview

trappsec

GitHubtrappsec-dev/trappsec

Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
api-securitydefensive-toolsidentity-access-management+5
134 days ago
wahh_extras preview

wahh_extras

GitHubsix2dez/wahh_extras

The Web Application Hacker's Handbook - Extra Content

curated-resourceseducationlearning-paths-courses+2
5713 years ago
Previous12Next