
pfsense-cp-filename-xss
 abraxas/pfsense-cp-filename-xss
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - XSS - CP filename stored XSS
exploitationpenetration-testingvulnerability-analysis+2
abraxas/pfsense-cp-filename-xsspfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - XSS - CP filename stored XSS
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 abraxas/element-ics-javascript
Element Web v1.12.29 - High - Remote - XSS - Univention ICS navigation.json link becomes a javascript: menu href
 bombobombone/cve-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…
 bombobombone/cve-2026-103437
Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
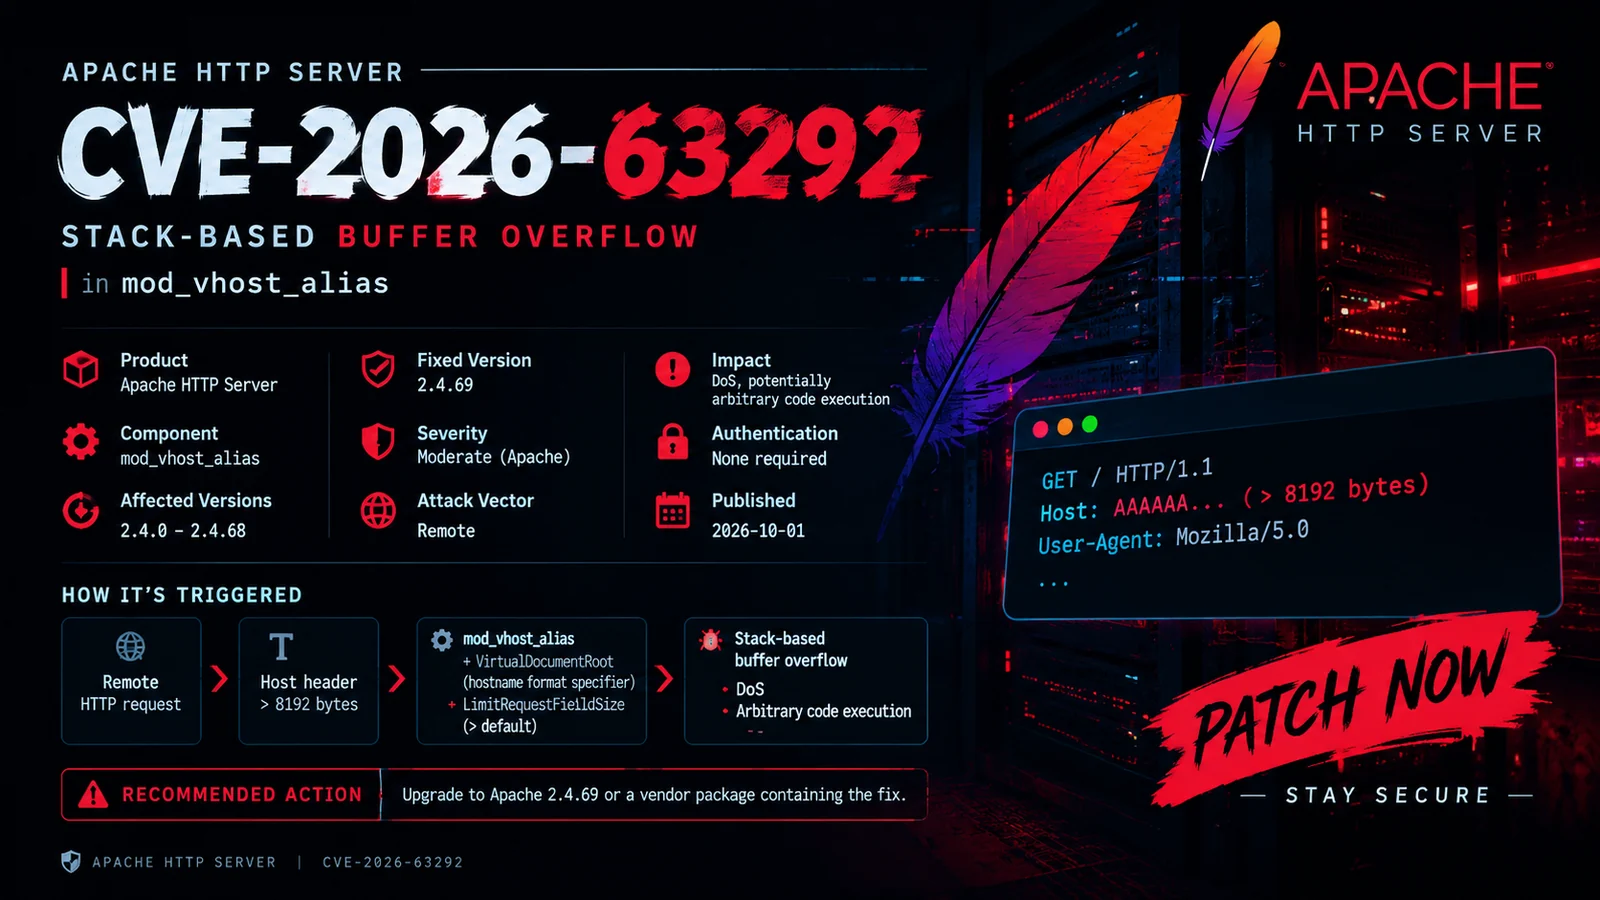 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
 ncf0126/nagios-xi-s-cve-2023-40931-exploit
Python exploit targeting the Nagios XI SQL injection vulnerability CVE-2023-40931, enabling injection-based access against affected instances.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 darkcast/cve-2020-10257
Shell exploit script for CVE-2020-10257, an unauthenticated RCE in the WordPress TRX Addons plugin that creates admin users via the wp-json API…
 babydessy/cve-2024-2876
Proof-of-concept for CVE-2024-2876, an unauthenticated SQL injection in the Email Subscribers WordPress plugin, with dork queries and a working…
 zined/cve-2023-4762
Proof-of-concept exploit for CVE-2023-4762, a Chromium V8 type confusion vulnerability enabling remote code execution via crafted JavaScript.
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 jayesh-dev21/poc_cve-2024-28157
PoC for (CVE-2024-28157) Stored XSS in Jenkins GitBucket Plugin <= 0.8
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…