By-Poloss..-..CVE-2026-19125

Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…

Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…

Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Browser resource exhaustion payload that crashes target systems via memory, GPU, audio, and rendering overload. Designed for authorized security…

Proof-of-concept and scanner for CVE-2026-27179, demonstrating vulnerability behavior in controlled environments for academic research and defensive…

Academic proof-of-concept demonstrating CVE-2026-21445 [LangFlow] for authorized security research.

Proof-of-Concept (PoC) for an authentication bypass vulnerability affecting applications using pac4j-jwt with JWE (JSON Web Encryption).

Audit and incident response tool for CVE-2026-41940 vulnerability

Passive security checker for CVE-2026-48908 affecting SP Page Builder.

A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…

A coverage-guided REST API fuzzer developed on top of LibAFL

🎯 Vulnerability scanner for SharePoint servers affected by CVE-2025-53770. Detects unsafe deserialization using ToolPane.aspx with a crafted…

Burp Suite extension to perform Kerberos authentication

Burp proxy text log converter to CSV and SQLLite

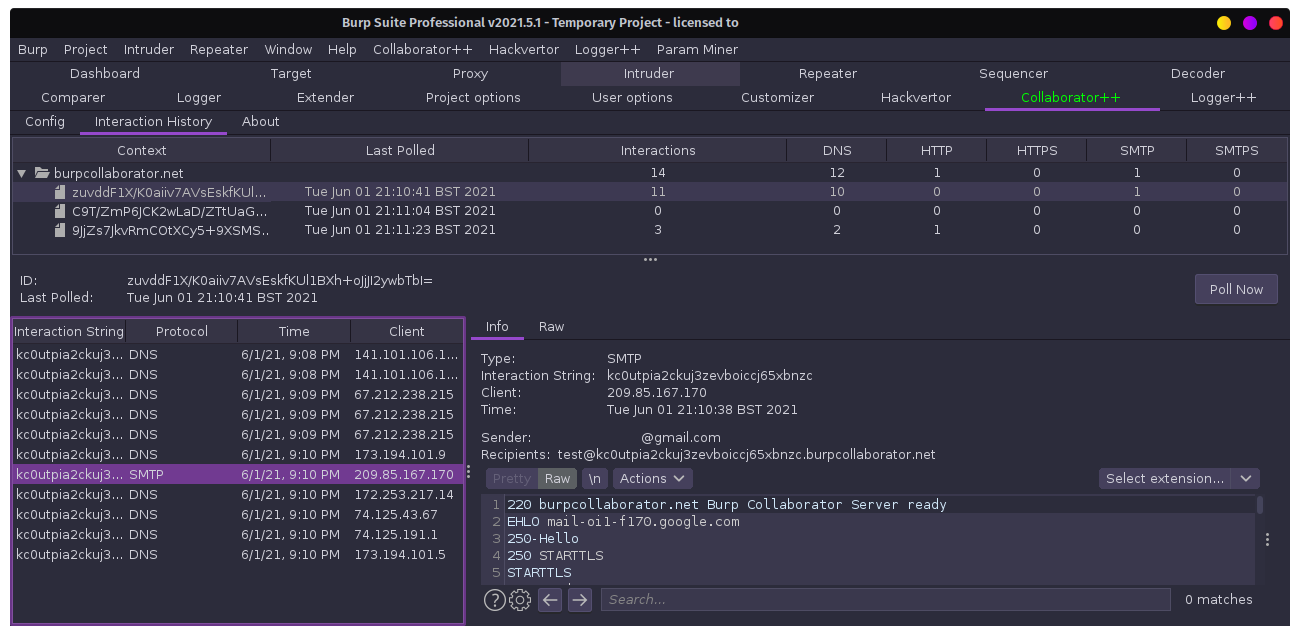
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…

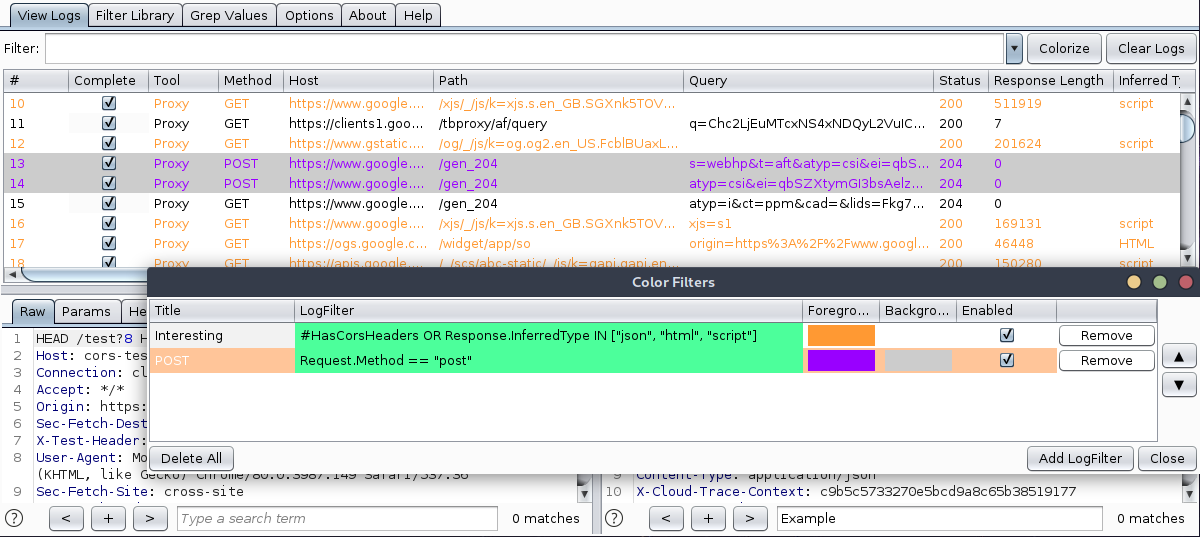
Advanced Burp Suite Logging Extension

Web Filter External Enumeration Tool (WebFEET)