IBM-Langflow-CVE-2026-48519-poc

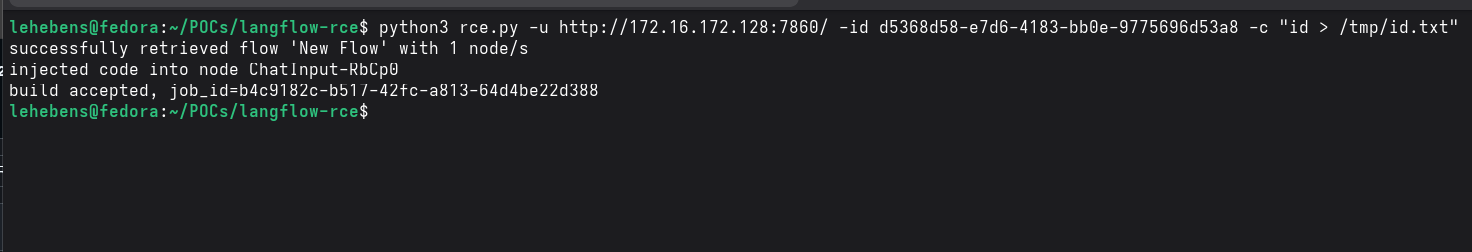
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

Mass scanner and auto-write tool for CVE-2026-49049, detecting exposed Joomla Helix3 onAjaxHelix3 handlers and verifying unauthenticated file-upload…

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…

Python PoC scanner and exploit for CVE-2026-89274, an unauthenticated arbitrary shortcode execution flaw in WP Recipe Maker <=10.8.1 via recipe…

Python 3 PoC scanner and exploit for CVE-2026-92229, an unauthenticated arbitrary shortcode execution flaw in Forminator WordPress plugin versions…

Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…

Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…

Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.

Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.

Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0

CVE-2026-63030 & CVE-2026-60137 RCE chain proof-of-concept

Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…

Exploits CVE-2026-41940, a cPanel/WHM authentication bypass, to gain root WHM access and run post-exploitation commands, account listing, and…

Client-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…

Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem

PoC for Zip Slip in MarkUs Assignment Configuration Uploads

Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…