
awesome-bugbounty-tools
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
curated-resourcesexploitationfuzzing+5
6.3k
vavkamil/awesome-bugbounty-toolsCurated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
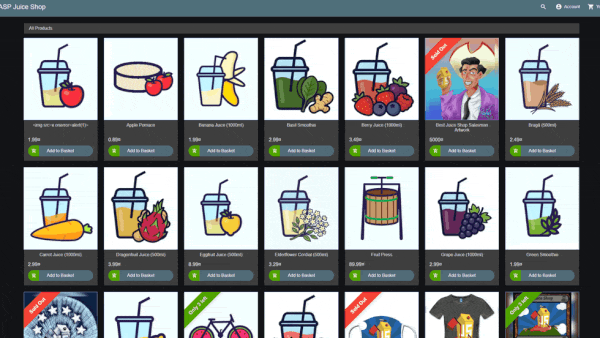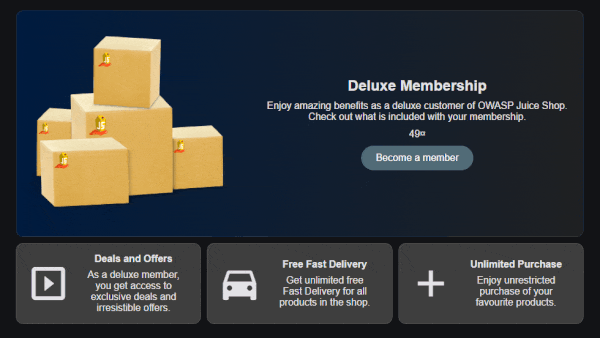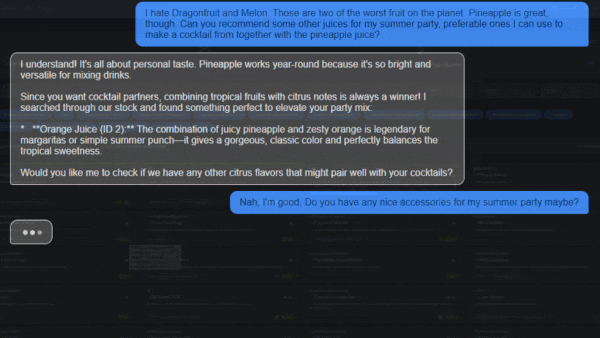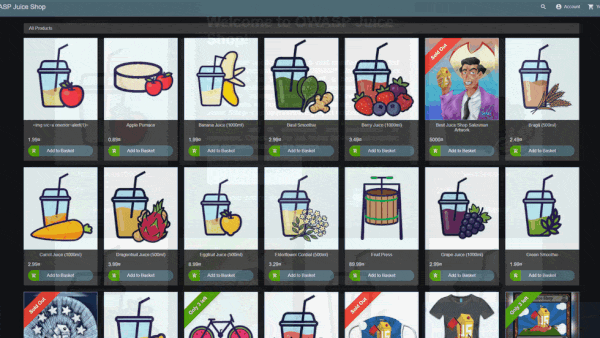 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 iamthefrogy/frogy2.0
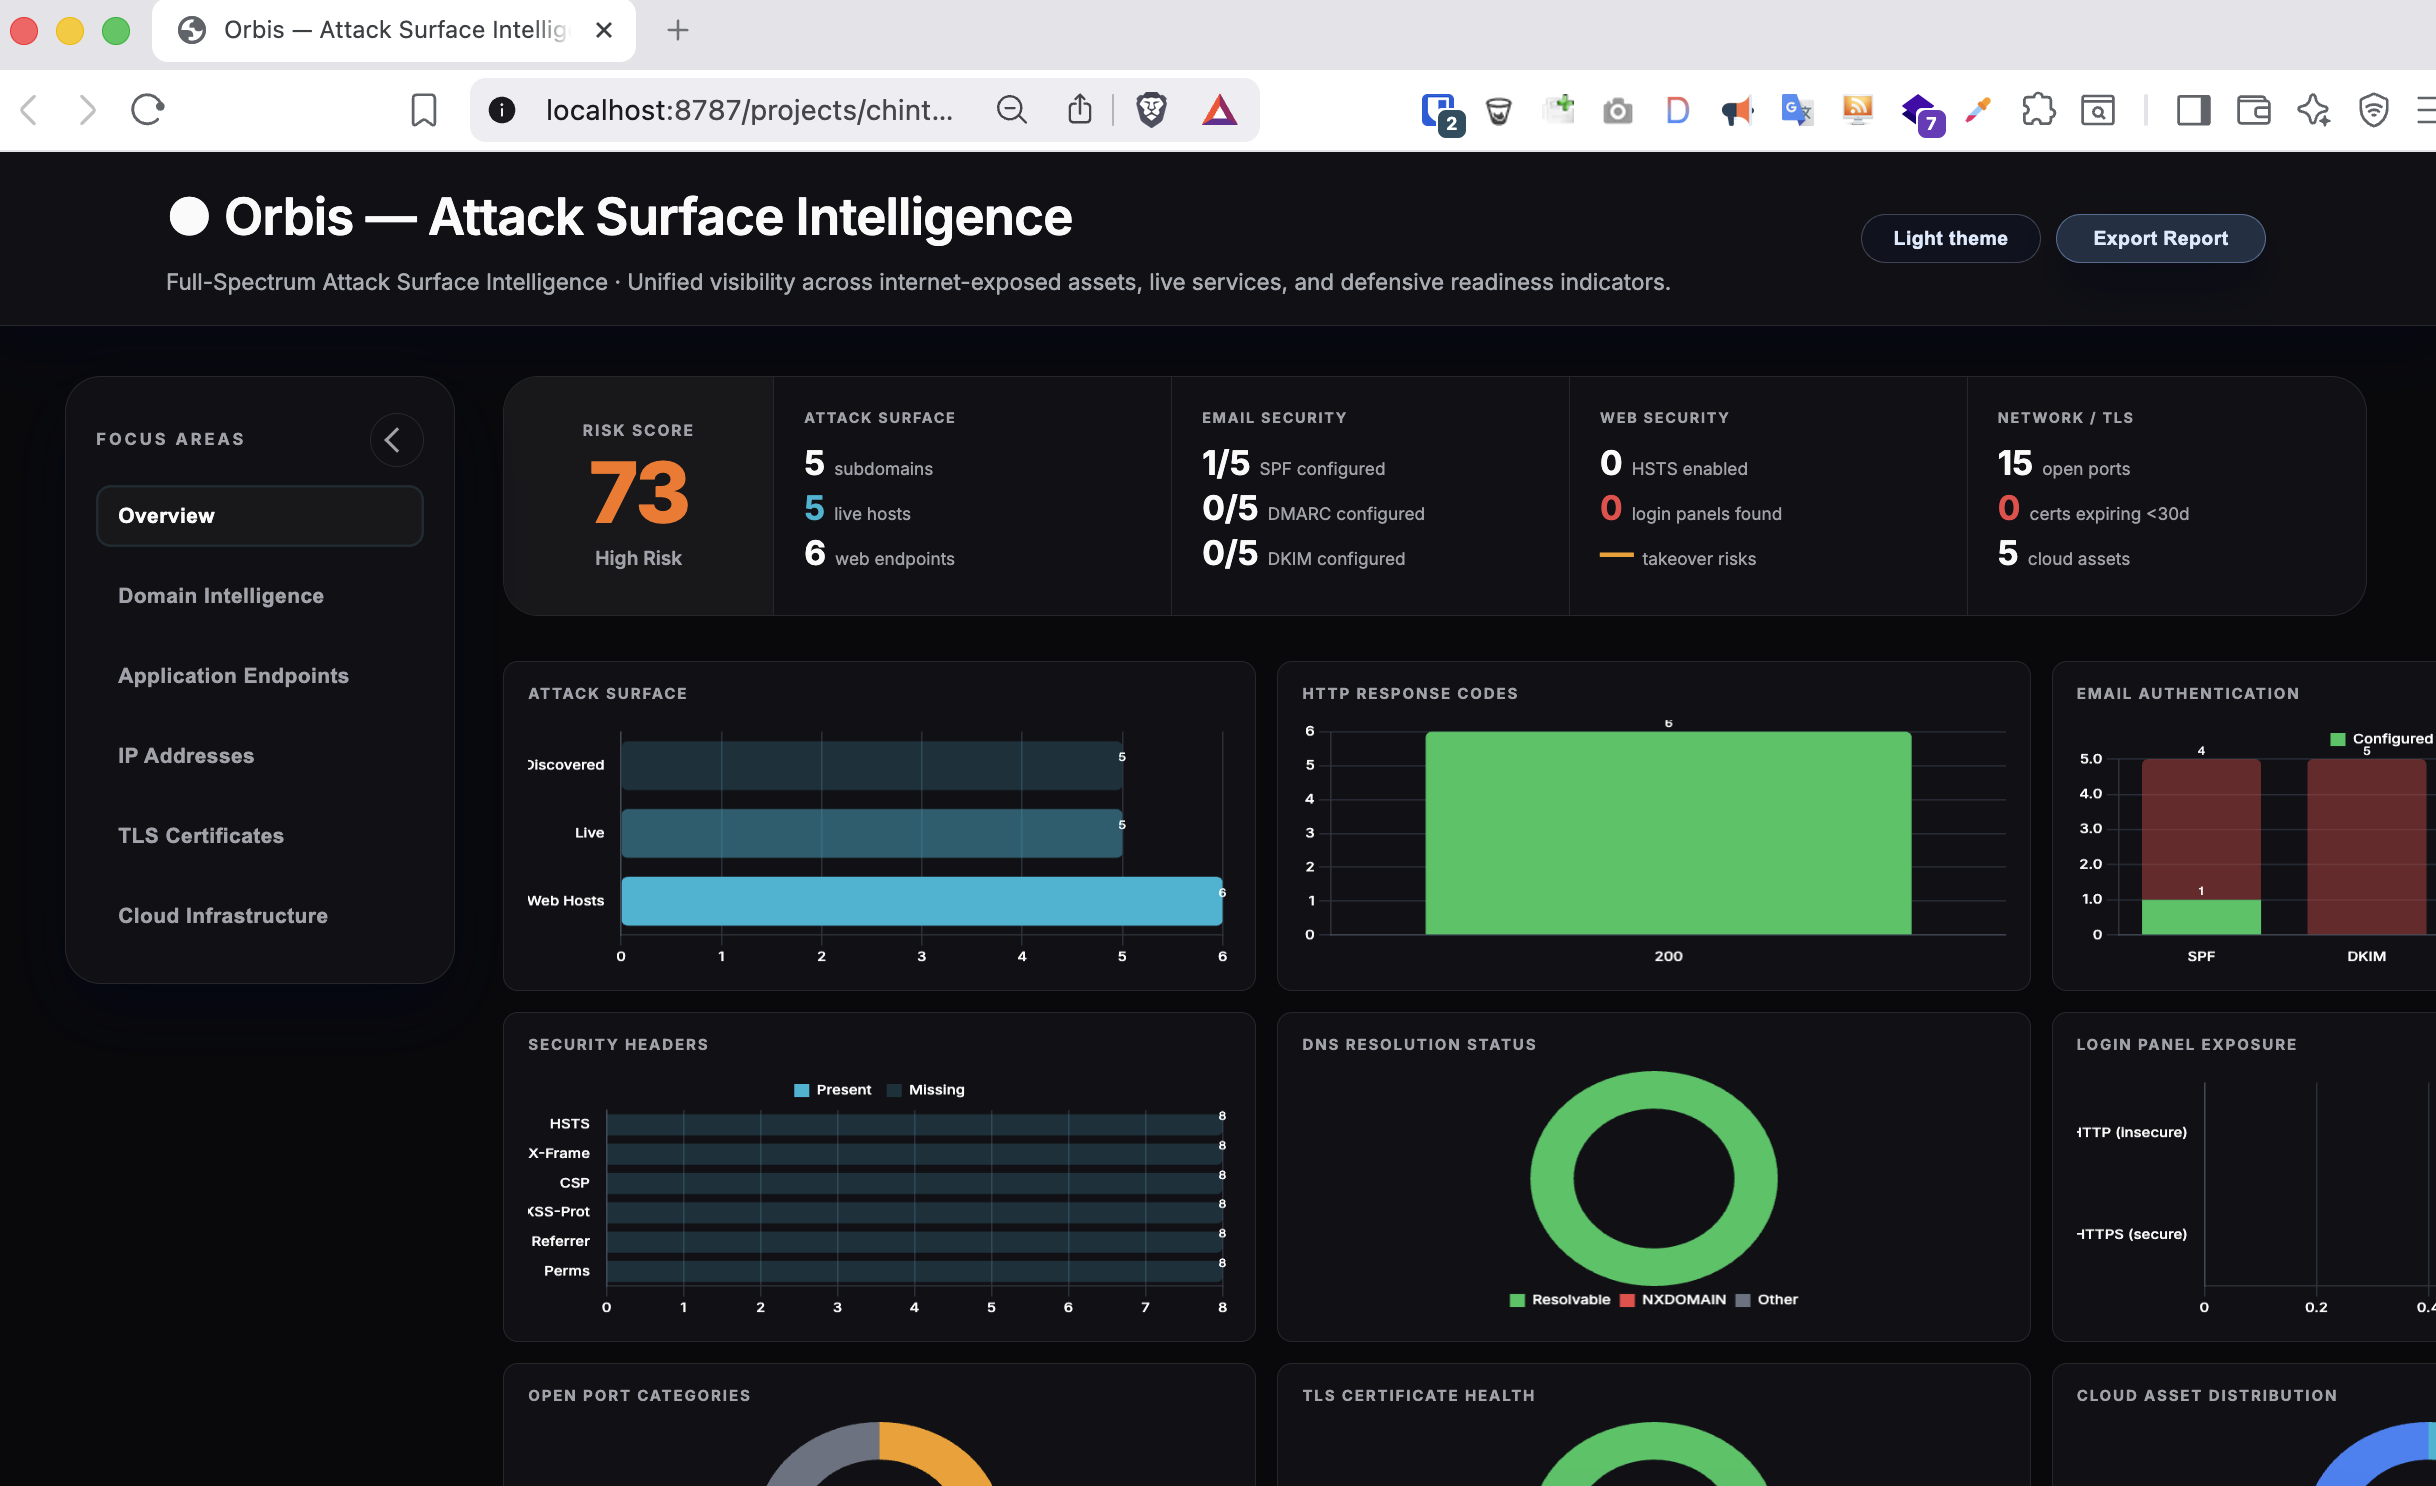
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 nullfuzz-pentest/shodan-dorks
Shodan Dorks
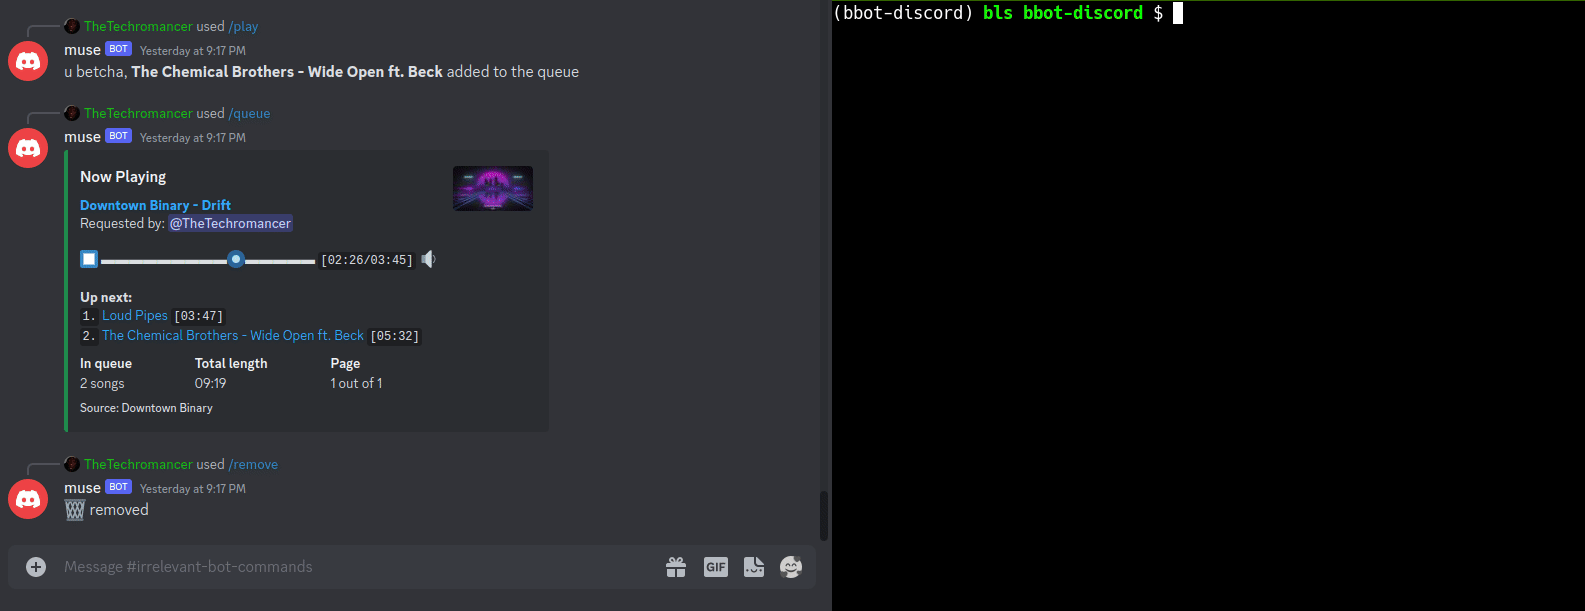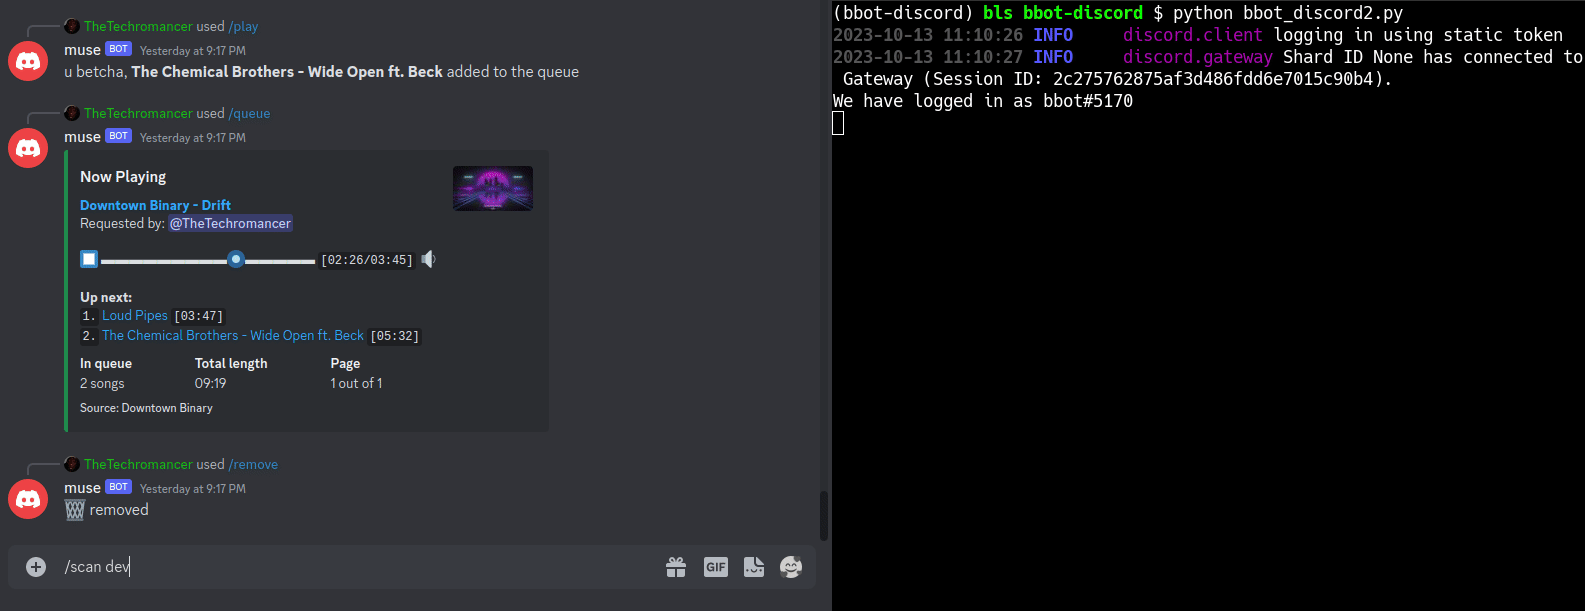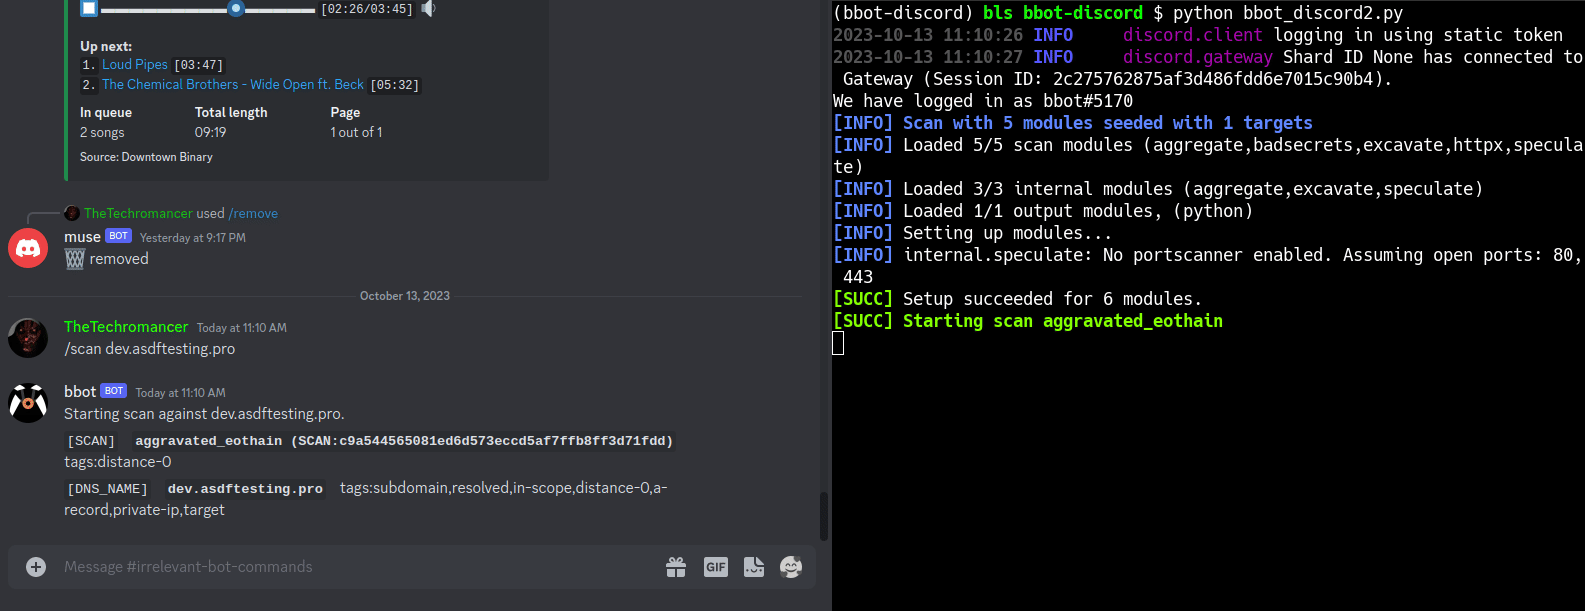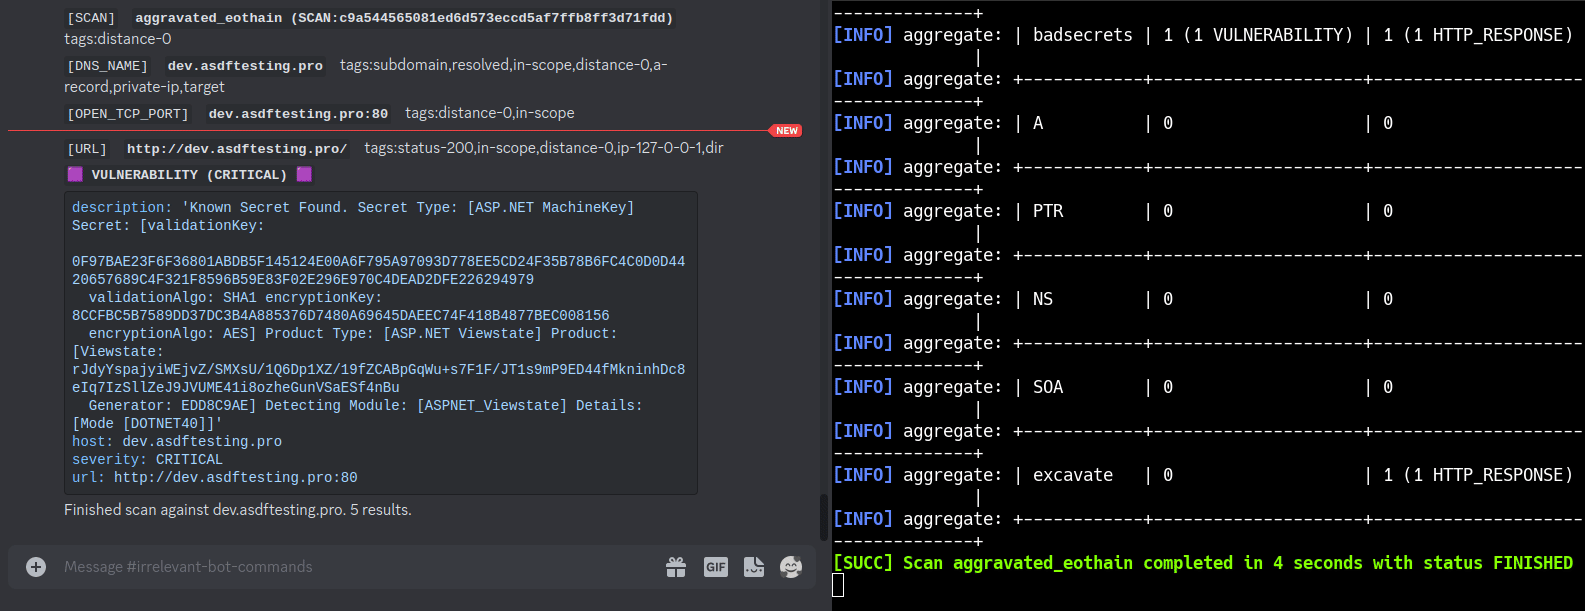 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 baroi-ai/nepstech-xpon-router-cve-2024-40119
Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
 m1k1o/neko
A self hosted virtual browser that runs in docker and uses WebRTC.
 szym0n13k/cve-2025-55971-blind-unauthenticated-ssrf-in-tcl-smart-tv-upnp-dlna-avtransport
TCL 65C655 Smart TV, running firmware version V8-R75PT01-LF1V269.001116 (Android TV, Kernel 5.4.242+), is vulnerable to a blind, unauthenticated…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 mpgn/poodle-poc
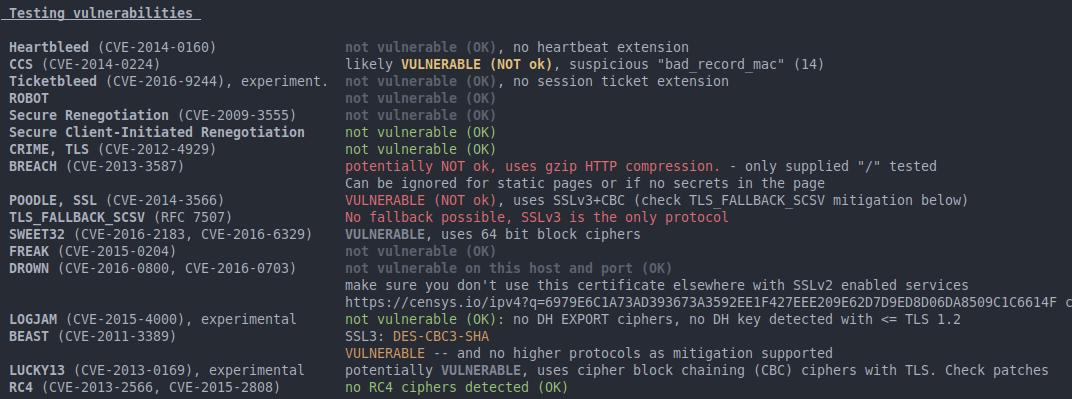
:poodle: Poodle (Padding Oracle On Downgraded Legacy Encryption) attack CVE-2014-3566 :poodle:
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 mattia-maria-scivoletto/internet-security-project
Academic report and LaTeX sources analyzing Maltego vulnerability CVE-2020-24656, an XXE injection enabling data exfiltration, written for an…